I’m excited to announce that I’ll be attending the upcoming Live! 360 Event, November 15-20, 2026, at Royal Pacific Resort at Universal Orlando, Florida. I’ll be in attendance all week and will be delivering a few talks at the event this year.
Sessions
I’ll be presenting two sessions at this year’s event. They are:
TMH06 – Moving to Zero Trust: Entra Private Access for Always On VPN Administrators. This is a popular session demonstrating how to migrate from Always On VPN (or any other VPN solution) to Entra Private Access with Zero Trust enforcement. I’ll describe how to get “from here to there,” moving from fully open VPN access to strict zero trust access without disruption.
Join Me!
If you are planning to attend the event, please join my sessions! I will be at the conference center all week, so don’t hesitate to reach out and contact me while you are there. I’m looking forward to seeing everyone soon!
The Microsoft Entra Private Network Connector is a lightweight on-premises software agent that enables Microsoft Entra Private Access to forward Global Secure Access (GSA) client traffic to internal resources. In environments with multiple connectors, traffic is normally distributed across available connectors in a connector group. While this improves resiliency and load distribution, it can create challenges for applications that rely on a consistent connector source IP address.
Stateless Connectors
By default, requests are distributed randomly among the available connectors in a connector group. Traffic forwarded to the internal resource uses the connector server’s IP address as its source. Consequently, separate connections from the same user and device can reach the application through different connectors. Importantly, session state is not shared among connectors in a connector group. As such, applications that associate session state with the source IP address may reject or interrupt these connections.
Why Session Persistence Matters
In some scenarios, an internal application might allow access only from specific connector IP addresses or associate an authenticated session with the source IP address. Random connector selection can cause subsequent connections to arrive from a different address, potentially interrupting the session. Session persistence reduces this risk by consistently using the same connector for the user and device.
Session Persistence
Microsoft recently introduced session persistence for Entra Private Access applications. When enabled, requests from the same user and device are consistently routed to the same connector for the duration of the session. This helps maintain a consistent connector egress IP address for applications that depend on source IP addresses for authentication, authorization, or session management.
Traffic Routing
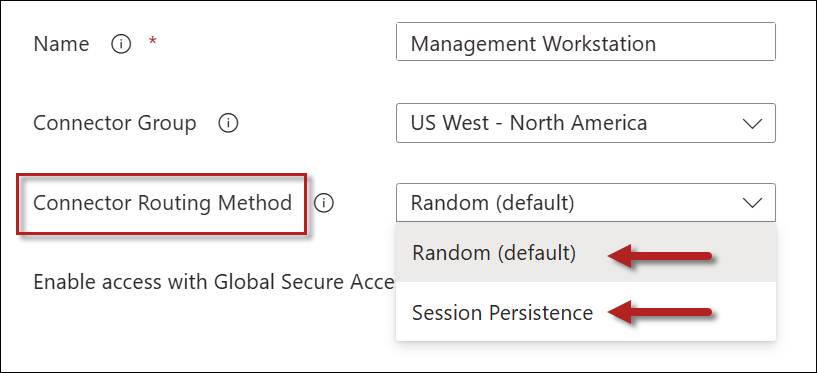
The connector traffic routing method is configured on a per-application basis. Traffic routing methods can be defined on Quick Access or Enterprise applications, and the setting can be configured on the Network access properties tab. Administrators have two options: Random or Session Persistence.
Random
This is the default behavior for the Private Network connector. All new connections are distributed randomly among connectors in the connector group.
Session Persistence
Selecting the Session Persistence option consistently routes requests from the same user and device to the connector on which the session was established.
Connector Routing Method Comparison
The following table summarizes these configuration options.
Routing Method
Benefits
Considerations
Random
Better distribution across connectors in a connector group
Source IP address may change between connections
Session Persistence
Consistent connector egress IP address
May not distribute sessions as evenly as the Random method
Failover
If the preferred connector becomes unavailable, subsequent traffic may be routed through another available connector. Applications that depend on the connector’s source IP address might require the user to establish a new session.
GSA Applications Only
Session persistence applies only to Global Secure Access applications. It is not supported for applications published using Microsoft Entra Application Proxy.
Summary
By default, Microsoft Entra Private Access distributes requests randomly among available connectors. Although this provides load distribution, it can create problems for applications that depend on a consistent connector source IP address. Session persistence addresses this issue by consistently routing traffic from the same user and device through the same connector for the duration of the session. This feature applies only to Global Secure Access applications and is not supported for Microsoft Entra Application Proxy applications.
On August 26, 2026, Microsoft released version 2.32.294 of the Entra Global Secure Access (GSA) client. This release addresses challenges caused by overlapping local and private network address spaces, improves tunnel creation performance, and prepares the client to receive future upgrades through Windows Update.
The Prefer Local Network option allows users to access resources on their current local network when its address space overlaps with a private application’s subnet. Common scenarios include accessing a local printer or casting to a nearby device.
Support for Prefer Local Network is included in this client release. However, the administrative setting required to expose the option to users is not yet available in the traffic forwarding profile. Once Microsoft makes this setting available, administrators can enable the feature and allow users to turn it on when needed.
Windows Update
Beginning in November 2026, the GSA client will automatically receive upgrades through Windows Update. Endpoints must be running GSA client 2.31.125 or later (2.32.294 or later for Windows on Arm).
Administrators can opt out of automatic updates when installing or upgrading the GSA client using the following command.
GSA client v2.32.294 accelerates the creation of new tunnels, improving connection performance. The installer also includes .NET Runtime 10.0.9. Additional changes include telemetry and accessibility enhancements, the removal of LastMile for Office 365 telemetry, and miscellaneous bug fixes.
Summary
Global Secure Access client v2.32.294 introduces useful improvements for users working on networks with overlapping address spaces and lays the groundwork for automatic client upgrades through Windows Update. The release also improves tunnel creation performance and includes several updates to telemetry, accessibility, runtime, and reliability. Administrators should evaluate Windows Update behavior and determine whether automatic upgrades are appropriate for their deployment and change management requirements.