

Entra Private Network Connector Session Persistence

The Microsoft Entra Private Network Connector is a lightweight on-premises software agent that enables Microsoft Entra Private Access to forward Global Secure Access (GSA) client traffic to internal resources. In environments with multiple connectors, traffic is normally distributed across available connectors in a connector group. While this improves resiliency and load distribution, it can create challenges for applications that rely on a consistent connector source IP address.

Stateless Connectors

By default, requests are distributed randomly among the available connectors in a connector group. Traffic forwarded to the internal resource uses the connector server’s IP address as its source. Consequently, separate connections from the same user and device can reach the application through different connectors. Importantly, session state is not shared among connectors in a connector group. As such, applications that associate session state with the source IP address may reject or interrupt these connections.

Why Session Persistence Matters

In some scenarios, an internal application might allow access only from specific connector IP addresses or associate an authenticated session with the source IP address. Random connector selection can cause subsequent connections to arrive from a different address, potentially interrupting the session. Session persistence reduces this risk by consistently using the same connector for the user and device.

Session Persistence

Microsoft recently introduced session persistence for Entra Private Access applications. When enabled, requests from the same user and device are consistently routed to the same connector for the duration of the session. This helps maintain a consistent connector egress IP address for applications that depend on source IP addresses for authentication, authorization, or session management.

Traffic Routing

The connector traffic routing method is configured on a per-application basis. Traffic routing methods can be defined on Quick Access or Enterprise applications, and the setting can be configured on the Network access properties tab. Administrators have two options: Random or Session Persistence.
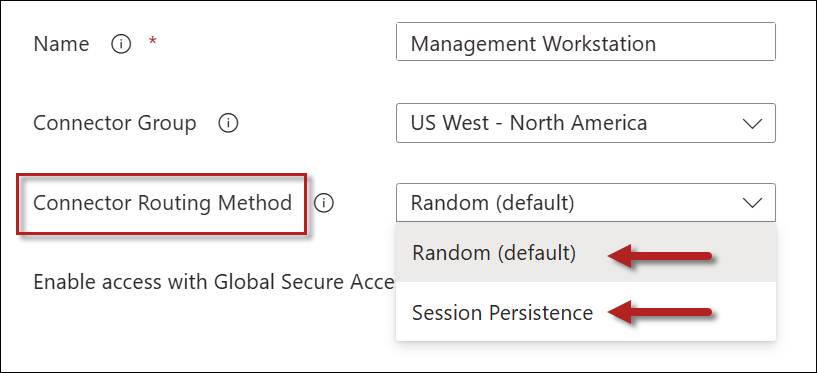
Random

This is the default behavior for the Private Network connector. All new connections are distributed randomly among connectors in the connector group.

Session Persistence

Selecting the Session Persistence option consistently routes requests from the same user and device to the connector on which the session was established.

Connector Routing Method Comparison

The following table summarizes these configuration options.

Routing MethodBenefitsConsiderations
RandomBetter distribution across connectors in a connector groupSource IP address may change between connections
Session PersistenceConsistent connector egress IP addressMay not distribute sessions as evenly as the Random method

Failover

If the preferred connector becomes unavailable, subsequent traffic may be routed through another available connector. Applications that depend on the connector’s source IP address might require the user to establish a new session.

GSA Applications Only

Session persistence applies only to Global Secure Access applications. It is not supported for applications published using Microsoft Entra Application Proxy.

Summary

By default, Microsoft Entra Private Access distributes requests randomly among available connectors. Although this provides load distribution, it can create problems for applications that depend on a consistent connector source IP address. Session persistence addresses this issue by consistently routing traffic from the same user and device through the same connector for the duration of the session. This feature applies only to Global Secure Access applications and is not supported for Microsoft Entra Application Proxy applications.

Additional Information

Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Network Connector Groups

What’s New in Entra Global Secure Access Client v2.32.294.0

On August 26, 2026, Microsoft released version 2.32.294 of the Entra Global Secure Access (GSA) client. This release addresses challenges caused by overlapping local and private network address spaces, improves tunnel creation performance, and prepares the client to receive future upgrades through Windows Update.

Changes in v2.32.294

GSA client v2.32.294 includes the following new features and capabilities.

Prefer Local Network

The Prefer Local Network option allows users to access resources on their current local network when its address space overlaps with a private application’s subnet. Common scenarios include accessing a local printer or casting to a nearby device.

Support for Prefer Local Network is included in this client release. However, the administrative setting required to expose the option to users is not yet available in the traffic forwarding profile. Once Microsoft makes this setting available, administrators can enable the feature and allow users to turn it on when needed.

Windows Update

Beginning in November 2026, the GSA client will automatically receive upgrades through Windows Update. Endpoints must be running GSA client 2.31.125 or later (2.32.294 or later for Windows on Arm).

Administrators can opt out of automatic updates when installing or upgrading the GSA client using the following command.

GlobalSecureAccessInstaller.exe /quiet /norestart EnableWindowsUpdates=0

Additional Enhancements

GSA client v2.32.294 accelerates the creation of new tunnels, improving connection performance. The installer also includes .NET Runtime 10.0.9. Additional changes include telemetry and accessibility enhancements, the removal of LastMile for Office 365 telemetry, and miscellaneous bug fixes.

Summary

Global Secure Access client v2.32.294 introduces useful improvements for users working on networks with overlapping address spaces and lays the groundwork for automatic client upgrades through Windows Update. The release also improves tunnel creation performance and includes several updates to telemetry, accessibility, runtime, and reliability. Administrators should evaluate Windows Update behavior and determine whether automatic upgrades are appropriate for their deployment and change management requirements.

Additional Information

Microsoft Entra Global Secure Access (GSA) Client v2.32.294.0

Microsoft Entra Global Secure Access (GSA)

Microsoft Entra Private Access

Microsoft Entra Internet Access

Entra Private Access and VPN Migration Strategies on Entra.News

What’s New in Entra Global Secure Access Client v2.31.125

On June 2, 2026, Microsoft released version 2.31.125 of the Entra Global Secure Access (GSA) client. This update introduces several enhancements designed to improve client resiliency, simplify troubleshooting, and provide administrators with better visibility into network connection status.

Changes in v2.31.125

GSA client v2.31.125 includes new features to streamline connectivity troubleshooting.

Network Status

The new GSA client can now distinguish between a complete network disconnection and a scenario where the device remains connected to a local network but lacks internet access. This distinction helps administrators and users more quickly identify the source of connectivity issues and reduce troubleshooting time.

Network Disconnected

No Internet Connectivity

Local Access

When Intelligent Local Access (ILA) is enabled, the client now clearly indicates when a device is connected to a trusted private network. This provides additional visibility into ILA decision-making and helps confirm that local access policies are functioning as expected.

Sign Out

The new GSA client includes an account picker when a user signs out on Entra-registered or Entra-joined devices. This enhancement simplifies account management on shared or multi-user devices by allowing users to switch identities without fully reinstalling or reconfiguring the client.

The sign out option is disabled by default. It must be enabled by setting the following registry key.

HKLM\Software\Microsoft\Global Secure Access Client\HideSignOutButton DWORD = 0

User Session Detection

Because the GSA client supports only a single interactive Windows session, this new indicator helps quickly identify unsupported multi-session scenarios that may impact client functionality or troubleshooting efforts.

Other Changes

In addition to the new features and capabilities outlined above, these changes are also included.

  • Updated embedded .NET Runtime to version 8.0.26.
  • GSA Forwarding Profile Service now automatically restarts after a failure.
  • Improved detection and tunneling of agentic network connections.
  • Various bug fixes and performance improvements.

Summary

GSA Client v2.31.125 introduces several useful enhancements focused on troubleshooting, resiliency, and user experience. Improved network status visibility, Intelligent Local Access awareness, account sign-out support, and enhanced session detection provide administrators with better diagnostic capabilities while making the client easier for end users to understand and manage. Although this release remains in preview, administrators are encouraged to begin testing this latest release soon.

Additional Information

Microsoft Entra Global Secure Access (GSA) Client v2.31.125

Microsoft Entra Private Access Intelligent Local Access

Entra Private Access Channels Are Unreachable

Administrators deploying Microsoft Entra Private Access may encounter a scenario in which the Global Secure Access (GSA) agent reports an error. However, the client continues to work without issue, and all internal resources remain reachable via the Entra Private Access connection. This issue occurs only when the Private Access forwarding profile is enabled alone. It does not happen if the Microsoft traffic forwarding profile is also enabled.

GSA Status Error

When this happens, the Private access channel status is Connected, but the Entra access channel is Disconnected. Also, you will see the following error message when clicking on the GSA client in the notification area.

Some channels are unreachable

Global Secure Access has some channels that are unreachable

Health Check

To investigate further, click the Troubleshooting tab, then click Run tool in the Advanced diagnostics tool section. In the Health check section, you will see the following error message.

Diagnostic URLs were not found in forwarding policy

Scrolling down the list also reveals the following error messages.

Magic IP received = False

Tunneling succeeded Entra Authentication = False

Root Cause

Several months ago, Microsoft made changes to the health check probes that required enabling the Microsoft traffic forwarding profile to work. Some essential health-check probes were not accessible via the Private Access channel, resulting in the error messages shown above when only the Private Access forwarding profile is enabled.

Resolution

Microsoft is rolling out changes to address this issue at the time of this writing (late October 2025). If you encounter this error, it will most likely resolve itself soon. Alternatively, administrators can enable the Microsoft traffic forwarding profile, which will also fix this issue.

Additional Information

Microsoft Entra Private Access

Microsoft Entra Global Secure Access (GSA)

Microsoft Security Service Edge (SSE) Now Generally Available

Microsoft Entra Security Service Edge (SSE) on RunAs Radio

Microsoft Security Service Edge Now Generally Available

A few weeks ago, Microsoft announced the general availability of its Security Service Edge (SSE) offering, Global Secure Access (GSA). GSA encompasses Entra Internet Access, a cloud-based Secure Web Gateway, and Entra Private Access, a Zero Trust Network Access (ZTNA) solution for accessing private data and applications on-premises.

ZTNA vs. VPN

Entra Private Access will be a compelling alternative to traditional VPN solutions such as Windows Always On VPN. Where traditional VPNs grant the endpoint an IP address on the internal network, Entra Private Access provides more granular access and does not require the device to be directly connected to the network.

GSA Client

Administrators must install the GSA client on all endpoints using Entra Internet Access or Entra Private Access. Today, the client is available for Windows and Android devices. iOS and macOS clients are forthcoming.

Private Network Connector

The Entra Private Access solution relies on the Entra Private Network Connector. The Entra Private Network Connector is a software component installed on-premises that provides remote access connectivity. Previously, it was called the Azure AD Application Proxy. Essentially, it is the same technology extended to support TCP and UDP network access in addition to HTTP.

Limitations

Entra Private Access is the way of the future for secure remote access. However, today, there are still some important limitations associated with this technology.

Private DNS

Although Microsoft announced general availability for Entra Private Access, it still lacks the private DNS feature many organizations require to provide feature parity with their existing VPN. This feature is still in private preview at the time of this writing. Hopefully, Microsoft will release this feature soon.

Device Connection

Entra Private Access does not support device-based connections. This limits its capabilities for domain-joined devices. If your organization uses hybrid Entra join today, consider sticking with Always On VPN until you move to native Entra joined endpoints.

Licensing

Global Secure Access (Entra Private Access and Entra Internet Access) are included in the Microsoft Entra Suite license. More information about Entra licensing can be found here.

Additional Information

Microsoft Global Secure Access Now Generally Available

Microsoft Entra Global Secure Access (GSA) Overview

Microsoft Entra Security Service Edge (SSE) on the RunAs Radio Podcast

Microsoft Entra Plans & Pricing

Microsoft Entra Security Service Edge (SSE) on RunAs Radio

I recently had the opportunity to join my good friend Richard Campbell on the RunAs Radio podcast. During this episode, we discussed the new Microsoft Entra Security Service Edge (SSE). This new service offering includes Entra Internet Access, a cloud-based secure web gateway, and Entra Private Access, an identity-centric zero-trust network access (ZTNA) solution. Entra Private Access is in public preview today. Entra Private Access is still in private preview at the time of this writing, however.

You can listen to RunAs Radio episode 906 here.

Enjoy!

Microsoft Entra Global Secure Access

Last week Microsoft introduced new Security Service Edge (SSE) capabilities as part of the Microsoft Entra suite of technologies. Included in these announcements, Microsoft introduced the public preview of two new secure remote access technologies – Microsoft Entra Internet Access and Microsoft Entra Private Access. The latter of these will particularly interest Microsoft Always On VPN administrators in some deployment scenarios.

Microsoft Entra Internet Access

Microsoft Entra Internet Access is a new Secure Web Gateway (SWG) cloud service solution designed to protect users from threats on the public Internet. Features include web content filtering, malware inspection, TLS inspection, and more. In addition, Entra Internet Access can protect Microsoft 365 applications. Azure Conditional Access policies can be enforced for Internet traffic. Network conditions are now included with Azure Conditional Access, which can further protect against attacks by requiring access from specific trusted or compliant networks. Today, the public preview is available for Microsoft 365 scenarios only. Internet traffic and other SaaS applications will be available later this year.

Microsoft Entra Private Access

Microsoft Entra Private Access is a Zero Trust Network Access (ZTNA) cloud service solution that leverages the Azure Application Proxy access model. With Azure App Proxy, administrators can easily publish private, on-premises web applications by installing the connector on an on-premises server. Administrators can leverage Azure AD authentication and conditional access policies to ensure device compliance or enforce multifactor authentication (MFA), if required. Microsoft Entra Private Access extends the capabilities of the Azure Application Proxy to support TCP and UDP-based applications.

Private Access vs. Always On VPN

Microsoft Entra Private Access will be a compelling alternative to Always On VPN in the future. Specifically, organizations using native Azure AD join devices could benefit tremendously from this technology. Microsoft Entra Private Access is much simpler to implement than Always On VPN and requires no on-premises infrastructure other than the Azure Application Proxy connector. Using Microsoft Entra Private Access also means that no inbound access from the Internet is required, making the solution inherently more secure and reducing the public attack surface. For organizations using hybrid Azure AD join, Always On VPN continues to be the best Microsoft solution for these scenarios.

References

Microsoft Entra Expands into Security Service Edge (SSE)

Microsoft Entra – Secure Access for a Connected World

Microsoft Entra Internet Access Preview

Microsoft Entra Private Access Preview

What is Zero Trust?

What is Zero Trust Network Access?

What is Security Service Edge (SSE)?

What is Secure Access Service Edge (SASE)?

What’s the Difference Between SSE and SASE?

Contact Us

I’ve had the privilege of participating in the private preview for Microsoft Entra Internet Access and Private Access. If you’d like to learn more about these technologies and how they can help your organization, fill out the form below, and I’ll provide more information.
