Configuring Proper Time Synchronization in an Active Directory Domain

Wall clock representing time synchronization

Accurate time is critical in an Active Directory environment. Kerberos authentication depends on it, and by default it tolerates no more than five minutes of clock skew between a client and a domain controller. Certificate validity periods, CRL publication, OCSP responses, and log correlation all depend on it too, which becomes even more important as organizations move to short-lived certificates. During a recent engagement to assess and remediate a customer’s Active Directory Certificate Services (AD CS) deployment, I noticed intermittent Kerberos authentication anomalies that didn’t line up with anything in the PKI itself. The root cause turned out to be time synchronization, which nobody had configured correctly across the domain. This post explains what I found and how I fixed it. I’ve reproduced the customer’s configuration in my lab, so the examples and output come from lab.richardhicks.net, but the process is the same one I used in the customer’s environment.

What I Found

When I reviewed time configuration across the customer’s domain, I found several problems, including the following.

  • Inconsistent domain controller configuration. Some domain controllers had never been configured and were still running the defaults. Others had been pointed manually at different external time sources, presumably by different administrators at different times. This resulted in more than one time root in the domain, which is exactly what the Windows time hierarchy is designed to prevent.
  • The PDC emulator was not authoritative. The domain controller holding the PDC emulator role had no external time source configured, so it wasn’t anchoring the domain to UTC.
  • Hyper-V was quietly providing the time. Most of the domain controllers were virtual machines running on Hyper-V. The Hyper-V time synchronization integration service (VMICTimeProvider) was enabled on all of them, and W32Time on the domain controllers was taking time from the host instead of the domain hierarchy.
  • The Hyper-V hosts had no time configuration at all. Most of the domain was running on Hyper-V hosts that were workgroup members. Workgroup machines don’t participate in the domain time hierarchy, and nobody had configured them. They were running on their own clocks, polling time.windows.com infrequently, if they could reach it at all.

The result was a loop with no anchor. The domain controllers took their time from the hosts, the hosts drifted on their own, and nothing in the environment was reliably tied to UTC. Different domain controllers on different hosts could disagree by a meaningful amount, which explained the inconsistent Kerberos behavior. In my lab, the PDC emulator showed the problem clearly.

PS C:\> w32tm.exe /query /status
Leap Indicator: 0(no warning)
Stratum: 1 (primary reference - syncd by radio clock)
...
ReferenceId: 0x564D5450 (source name: "VMTP")
...
Source: VM IC Time Synchronization Provider

Don’t be fooled by Stratum 1. The VM IC provider always reports Stratum 1, but the real source is the Hyper-V host’s clock. A quick comparison against a public time server showed the PDC emulator was about 840 milliseconds off UTC.

PS C:\> w32tm.exe /stripchart /computer:time.cloudflare.com /samples:3 /dataonly
Tracking time.cloudflare.com [162.159.200.1:123].
Collecting 3 samples.
17:36:52, +00.8405031s
17:36:54, +00.8443389s
17:36:56, +00.8415804s

That’s not enough to break Kerberos on its own, but it was drifting, and in the customer’s environment, with multiple hosts and multiple time roots, the differences were much larger.

How Time Sync Should Work

Before making changes, it’s worth reviewing how Windows time synchronization is designed to work in an Active Directory domain. The hierarchy is simple and consists of the following.

  • The forest root PDC emulator is the authoritative time source. It is the only domain controller that should synchronize with an external source, and it advertises itself as a reliable time server (AnnounceFlags 5).
  • All other domain controllers follow the domain hierarchy. They use the NT5DS type and synchronize with the PDC emulator (directly or through their domain’s PDC emulator in a multi-domain forest). They advertise as time servers, but not as reliable ones (AnnounceFlags 10, the default).
  • Domain members synchronize with a domain controller. This is the default behavior for every domain-joined machine, although virtual machines need one adjustment, which I cover next.

Virtual Machines

Virtualization adds a wrinkle. On Hyper-V, the time synchronization integration service registers its own W32Time provider, VMICTimeProvider, which feeds the guest time from the host. It’s enabled by default on every virtual machine, and on a domain-joined VM it competes with the domain hierarchy and usually wins. Microsoft’s guidance is to disable VMICTimeProvider on virtual domain controllers so they get their time from the PDC emulator instead. I recommend disabling it on domain member VMs as well, so every domain-joined machine follows the same hierarchy.

Workgroup Hyper-V Hosts

The Hyper-V hosts matter too. If they’re domain members, they’ll follow the domain hierarchy automatically. If they’re workgroup members, as they were here, they need to be configured explicitly. Even with VMICTimeProvider disabled, the host’s clock still sets each VM’s time at startup and after a restore from a saved state, and the host needs accurate time for its own logs and certificates.

Target Configuration

The end state looks like this. The PDC emulator and the Hyper-V hosts both sync with the same public source, and every domain-joined machine, physical or virtual, follows the domain hierarchy.

SystemTime sourceConfigured by
PDC emulatortime.cloudflare.comDC Time Sync GPO
Other domain controllersPDC emulatorDC Time Settings GPO
Domain members (physical and virtual)Domain controllersDomain Member Time Settings GPO
Hyper-V hosts (workgroup)time.cloudflare.comLocal configuration

Resetting Domain Controllers to the Default Configuration

With domain controllers configured inconsistently, the cleanest approach is to return every one of them to the default configuration and then manage time centrally with Group Policy. Resetting first is important. Local settings remain in the registry underneath any policy, and if a domain controller ever stops receiving the policy (for example, after the PDC emulator role moves), it falls back to whatever was configured locally. Leftover manual peer settings would quietly create a second time root.

Restoring the Defaults

The following commands reset W32Time on every domain controller in the domain. They re-enable the Hyper-V time provider (the default), restore domain hierarchy synchronization, reset the peer list to the stock time.windows.com,0x9 value, and set AnnounceFlags back to 10 with /reliable:no.

$DomainControllers = (Get-ADDomainController -Filter *).HostName
Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
# Re-enable the Hyper-V time provider (default)
$VmicKey = 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
If (Test-Path -Path $VmicKey) {
Set-ItemProperty -Path $VmicKey -Name Enabled -Value 1
}
# Restore domain hierarchy sync, default peer list, and default AnnounceFlags (10)
w32tm.exe /config /manualpeerlist:"time.windows.com,0x9" /syncfromflags:domhier /reliable:no /update
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover
}

I recommend this targeted approach over w32tm.exe /unregister and w32tm.exe /register. Re-registering the service rebuilds the entire W32Time configuration, but it can also remove the VMICTimeProvider subkey. That key is created by the Hyper-V integration components, not by W32Time, and it’s the key we’ll target with Group Policy in the next step.

Verifying the Reset

Next, confirm each domain controller is running the defaults and that no existing Group Policy is configuring W32Time.

Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
Write-Output "=== $env:COMPUTERNAME ==="
w32tm.exe /query /configuration | Select-String 'Type:|NtpServer:|AnnounceFlags:' | ForEach-Object { $_.Line.Trim() }
w32tm.exe /query /source
Write-Output "Time policy present: $(Test-Path -Path 'HKLM:\SOFTWARE\Policies\Microsoft\W32Time')"
}

Each domain controller should report Type: NT5DS (Local) and AnnounceFlags: 10 (Local), and the time policy check should return False. If it returns True, another GPO is already configuring W32Time. Find it and remove those settings before continuing. Don’t be surprised if the source still shows VM IC Time Synchronization Provider on some domain controllers at this point. That’s the default behavior we’re about to fix.

Configuring Time Sync with Group Policy

With every domain controller back to a known state, the next step is to configure time centrally with three GPOs. Two are linked to the Domain Controllers OU, and the third is linked to the domain root for domain members. The design includes the following.

GPOApplies toSettings
DC Time SettingsAll domain controllersType NT5DS, AnnounceFlags 10, NTP client and server enabled, VMICTimeProvider disabled
DC Time SyncPDC emulator only (WMI filter)Type NTP, NtpServer time.cloudflare.com,0x8 time.nist.gov,0xa, AnnounceFlags 5
Domain Member Time SettingsAll domain members (linked to the domain root)VMICTimeProvider disabled

DC Time Sync is linked with a higher precedence (link order 1), so on the PDC emulator its values override the baseline from DC Time Settings. Every other domain controller receives only the baseline. A nice benefit of this design is that it follows the PDC emulator role automatically. If the role moves to another domain controller, the WMI filter matches the new role holder, and the old one falls back to the baseline with no administrator intervention. However, if the PDC emulator role moves to another DC, don’t forget to update the outbound access rules on the edge firewall to allow the new server to access the public time resource.

Choosing a Time Source

I used time.cloudflare.com as the primary time source for this customer, with time.nist.gov as a fallback. You can use any reliable public time service, such as time.windows.com or a regional pool.ntp.org address. Separate multiple servers with spaces in the NtpServer value.

Adding a Fallback Time Source

A single upstream time source works, but it makes the entire domain dependent on one provider. Microsoft recommends configuring three or more time servers when using multiple peers, or, with only two, marking one with the UseAsFallbackOnly flag (0x2). I chose the latter, setting NtpServer to time.cloudflare.com,0x8 time.nist.gov,0xa. The 0xa flag combines client mode (0x8) and fallback only (0x2), so W32Time uses NIST only when Cloudflare is unavailable. Keep the following in mind when choosing a fallback.

  • It removes a single point of failure. Cloudflare’s time service is highly reliable, but the service itself isn’t the only thing that can fail. A DNS resolution failure, a BGP route leak or hijack affecting the provider’s prefixes, an upstream ISP routing problem, or a firewall change can all make a single provider unreachable from your network. NIST runs on a completely separate network and doesn’t use anycast, so an event that affects one provider is unlikely to affect the other.
  • An outage isn’t catastrophic. Even if the PDC emulator can’t reach any upstream source, it keeps running on its own clock and continues serving time to the rest of the domain. Every domain controller and domain member still follows the PDC emulator, so the domain stays in sync with itself while slowly drifting from UTC. That’s what matters most for Kerberos, which compares the client’s clock with the domain controller’s clock, not with UTC. A typical system clock drifts by a few seconds per day at most, so an outage lasting hours or even days has no practical impact. When the time source becomes reachable again, W32Time corrects the accumulated offset automatically.
  • Both sources must handle leap seconds the same way. Cloudflare and NIST both insert leap seconds as a one-second step, so they’re a safe pair. Google, AWS, and Meta smear leap seconds instead, so don’t pair one of them with Cloudflare or NIST. The next section explains why.
  • A fallback doesn’t improve accuracy. A second source improves availability, not accuracy. With UseAsFallbackOnly, W32Time only consults NIST when Cloudflare is unreachable, so there’s nothing to cross-check against. Even with two active peers, there’s no majority to decide which one is right if they disagree. That’s fine for a typical Active Directory domain, which doesn’t require high-accuracy time.

Leap Second Considerations

Avoid mixing time services that handle leap seconds differently. A leap second is an occasional one-second adjustment to UTC that keeps it aligned with the Earth’s rotation. Most time services, including Cloudflare and NIST, apply it the standard way, by inserting the extra second all at once. Google (and AWS) instead “smear” it by slightly slowing their clocks over a 24-hour window, so during that period their time differs from other services by up to half a second. If a domain controller has both kinds of servers in its peer list, they disagree during a leap event, and the results are unpredictable. Pick one approach and use it consistently. You can read more about each approach in Google’s leap smear documentation and Cloudflare’s NTP documentation.

Allowing Outbound NTP

The PDC emulator must be able to reach both time services on UDP port 123. In the customer’s environment, as in my lab, outbound NTP was blocked at the edge firewall. I added a rule allowing outbound UDP 123 from the PDC emulator to the IPv4 and IPv6 addresses of both time services. Cloudflare publishes its addresses in its documentation, and NIST publishes the list of servers that time.nist.gov rotates across. Be sure to include both address families if your domain controllers have IPv6 connectivity, because W32Time will often prefer IPv6 when the name resolves to both. Also, remember to update the rule if the PDC emulator role moves to a different server. You can validate reachability to both services from the PDC emulator before configuring anything.

w32tm.exe /stripchart /computer:time.cloudflare.com /samples:3 /dataonly
w32tm.exe /stripchart /computer:time.nist.gov /samples:3 /dataonly

If both return offsets, you’re good to go. An error of 0x800705B4 indicates a timeout, which usually means UDP 123 is blocked or the IPv6 path isn’t working.

Creating the GPOs

The following script creates the WMI filter and all three GPOs. It links the two domain controller GPOs to the Domain Controllers OU and the member GPO to the domain root. It requires the GroupPolicy and ActiveDirectory modules (Install-WindowsFeature -Name GPMC, RSAT-AD-PowerShell on Windows Server) and Domain Admin rights. Run it in Windows PowerShell 5.1. You can also download the script from GitHub.

#Requires -Modules GroupPolicy, ActiveDirectory
$ErrorActionPreference = 'Stop'
# Variables
$Domain = Get-ADDomain
$DomainFqdn = $Domain.DNSRoot
$DomainDn = $Domain.DistinguishedName
$DcOu = $Domain.DomainControllersContainer
$Pdc = $Domain.PDCEmulator
$PolicyKey = 'HKLM\SOFTWARE\Policies\Microsoft\W32Time'
$NtpServer = 'time.cloudflare.com,0x8 time.nist.gov,0xa'
# Create the WMI filter (or reuse it if it already exists)
$WmiFilterName = 'PDC Emulator'
$WmiQuery = 'SELECT * FROM Win32_ComputerSystem WHERE DomainRole = 5'
$SomPath = "CN=SOM,CN=WMIPolicy,CN=System,$DomainDn"
$WmiFilter = Get-ADObject -Server $Pdc -SearchBase $SomPath -LDAPFilter "(&(objectClass=msWMI-Som)(msWMI-Name=$WmiFilterName))" -Properties 'msWMI-ID'
If ($null -eq $WmiFilter) {
$WmiId = "{$([Guid]::NewGuid().ToString().ToUpper())}"
$Now = (Get-Date).ToUniversalTime().ToString('yyyyMMddHHmmss.ffffff-000')
$FilterParams = @{
Server = $Pdc
Name = $WmiId
Type = 'msWMI-Som'
Path = $SomPath
OtherAttributes = @{
'msWMI-Name' = $WmiFilterName
'msWMI-Parm1' = 'Domain controller holding the PDC emulator role'
'msWMI-Parm2' = "1;3;10;$($WmiQuery.Length);WQL;root\CIMv2;$WmiQuery;"
'msWMI-Author' = "$env:USERNAME@$DomainFqdn"
'msWMI-ID' = $WmiId
'msWMI-CreationDate' = $Now
'msWMI-ChangeDate' = $Now
}
}
New-ADObject @FilterParams
}
Else {
$WmiId = $WmiFilter.'msWMI-ID'
}
# DC Time Settings (all domain controllers)
$AllDcGpo = New-GPO -Name 'DC Time Settings' -Comment 'Baseline W32Time settings for all domain controllers' -Server $Pdc
$Gpo = @{ Name = $AllDcGpo.DisplayName; Server = $Pdc }
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'Type' -Type String -Value 'NT5DS' | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Config" -ValueName 'AnnounceFlags' -Type DWord -Value 10 | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\TimeProviders\NtpClient" -ValueName 'Enabled' -Type DWord -Value 1 | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\TimeProviders\NtpServer" -ValueName 'Enabled' -Type DWord -Value 1 | Out-Null
# Disable the Hyper-V time provider (Group Policy Preference, writes to the service key)
$PrefParams = @{
Name = $AllDcGpo.DisplayName
Server = $Pdc
Context = 'Computer'
Action = 'Update'
Key = 'HKLM\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
ValueName = 'Enabled'
Type = 'DWord'
Value = 0
}
Set-GPPrefRegistryValue @PrefParams | Out-Null
# DC Time Sync (PDC emulator only)
$PdcGpo = New-GPO -Name 'DC Time Sync' -Comment 'External NTP source for the PDC emulator' -Server $Pdc
$Gpo = @{ Name = $PdcGpo.DisplayName; Server = $Pdc }
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'Type' -Type String -Value 'NTP' | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'NtpServer' -Type String -Value $NtpServer | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Config" -ValueName 'AnnounceFlags' -Type DWord -Value 5 | Out-Null
# Assign the WMI filter to DC Time Sync
$PdcGpoDn = "CN={$($PdcGpo.Id.ToString().ToUpper())},CN=Policies,CN=System,$DomainDn"
Set-ADObject -Server $Pdc -Identity $PdcGpoDn -Replace @{ gPCWQLFilter = "[$DomainFqdn;$WmiId;0]" }
# Domain Member Time Settings (all domain members)
$MemberGpo = New-GPO -Name 'Domain Member Time Settings' -Comment 'Disable the Hyper-V time provider so domain members follow the domain hierarchy' -Server $Pdc
$PrefParams = @{
Name = $MemberGpo.DisplayName
Server = $Pdc
Context = 'Computer'
Action = 'Update'
Key = 'HKLM\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
ValueName = 'Enabled'
Type = 'DWord'
Value = 0
}
Set-GPPrefRegistryValue @PrefParams | Out-Null
# Link both DC GPOs (DC Time Sync takes precedence)
New-GPLink -Name 'DC Time Sync' -Target $DcOu -LinkEnabled Yes -Order 1 -Server $Pdc | Out-Null
New-GPLink -Name 'DC Time Settings' -Target $DcOu -LinkEnabled Yes -Order 2 -Server $Pdc | Out-Null
# Link the member GPO to the domain root
New-GPLink -Name 'Domain Member Time Settings' -Target $DomainDn -LinkEnabled Yes -Server $Pdc | Out-Null
Get-GPInheritance -Target $DcOu -Server $Pdc | Select-Object -ExpandProperty GpoLinks | Format-Table DisplayName, Order, Enabled
Get-GPInheritance -Target $DomainDn -Server $Pdc | Select-Object -ExpandProperty GpoLinks | Format-Table DisplayName, Order, Enabled

There are a few things worth noting about this script.

  • Everything targets the PDC emulator. The GroupPolicy cmdlets talk to the PDC emulator by default, but the ActiveDirectory cmdlets can pick any domain controller. Without -Server, Set-ADObject may land on a domain controller where the new GPO hasn’t replicated yet, and the script fails partway through. I hit this in the field, so the script now pins every call to the PDC emulator.
  • Only the required values are written. Enabling the Global Configuration Settings Administrative Template writes every value it contains, including some outdated clock discipline defaults. Setting individual registry values avoids that, and everything not set by policy keeps its default. The trade-off is that GPMC may show these under Extra Registry Settings instead of Windows Time Service. That’s cosmetic.
  • VMICTimeProvider is disabled with a preference, not a policy. There is no Administrative Template setting for it. The Group Policy Preference writes directly to the service key, so it persists even if the GPO stops applying, which is what you want for a domain controller.
  • The member GPO needs only the preference. Domain members already default to NT5DS, so VMICTimeProvider is the only thing keeping virtual machines off the domain hierarchy. Because it’s linked to the domain root, it also applies to domain controllers. That’s harmless, since DC Time Settings sets the same value and takes precedence.
  • The WMI filter is assigned directly. The GroupPolicy module has no cmdlet for creating or assigning WMI filters, so the script writes the gPCWQLFilter attribute itself.
  • Multi-domain forests. DomainRole = 5 matches the PDC emulator of any domain. Link DC Time Sync only in the forest root domain. Child domain PDC emulators should follow the domain hierarchy.
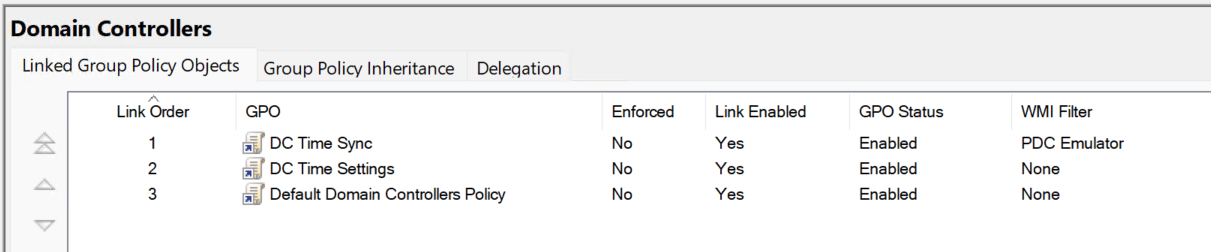
DC Time Sync and DC Time Settings GPOs linked to the Domain Controllers OU

GPOs applied to domain controllers.

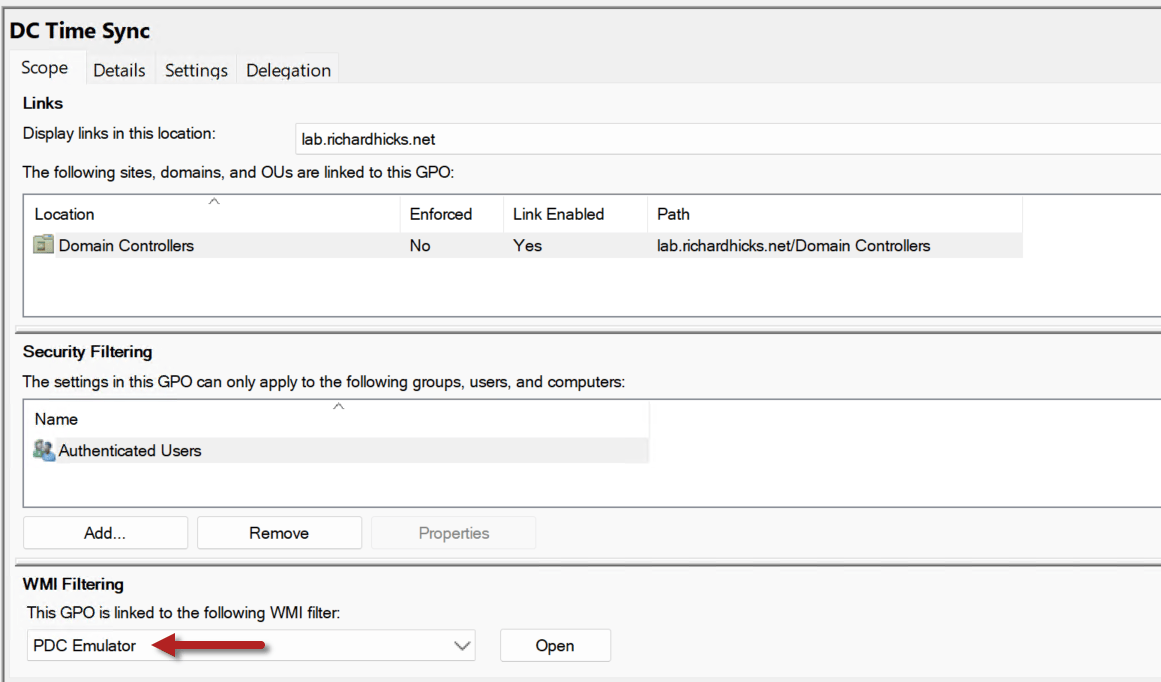
DC Time Sync GPO with the PDC Emulator WMI filter applied

DC Time Sync GPO with WMI filtering applied to PDC emulator.

Applying the Policies

Force replication so every domain controller has the new GPOs, then apply them and restart the time service.

Invoke-Command -ComputerName $Pdc -ScriptBlock { repadmin.exe /syncall /AdeP | Out-Null }
Start-Sleep -Seconds 60
Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
gpupdate.exe /target:computer /force | Out-Null
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover | Out-Null
}

Domain members pick up the new GPO at their next policy refresh. However, W32Time reads which providers are enabled only when the service starts, so a member VM keeps using VMICTimeProvider until W32Time restarts or the machine reboots. To switch a member over immediately, run the following commands on it.

gpupdate.exe /target:computer /force
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover

Configuring the Workgroup Hyper-V Hosts

With the domain controllers fixed, the last piece is the Hyper-V hosts. In the customer’s environment, most of the domain ran on hosts that were workgroup members, and none had any time configuration. The VMs no longer take their time from the host continuously, but the host’s clock still sets each VM’s time at startup and after a restore from a saved state. Workgroup machines don’t participate in the domain hierarchy, so Group Policy can’t help here. Each host must be configured locally, and there are two reasonable options.

  • Sync directly from the public time service. This is what I did for the customer. The hosts don’t depend on a VM they’re running, which avoids a chicken-and-egg problem at boot. It does require allowing outbound UDP 123 from each host.
  • Sync from the PDC emulator. This keeps a single internal source of truth and needs no additional edge firewall rules, since domain controllers answer NTP requests by default. The downside is that the host boots before the PDC emulator VM and runs on its own clock until the domain controller is available.

Either way, everything traces back to the same UTC source. Run the following commands locally on each Hyper-V host.

# Sync from Cloudflare, with NIST as a fallback
# (0x1 = use SpecialPollInterval, 0x2 = fallback only, 0x8 = client mode)
w32tm.exe /config /manualpeerlist:"time.cloudflare.com,0x9 time.nist.gov,0xb" /syncfromflags:manual /update
# Poll every 1024 seconds (workgroup machines default to once a week)
Set-ItemProperty -Path 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\NtpClient' -Name SpecialPollInterval -Value 1024
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover

Setting SpecialPollInterval is important. The workgroup default is 604,800 seconds, or one week, which is far too infrequent to keep a virtualization host accurate. The 0xb flag on time.nist.gov adds fallback only (0x2) to the same flags, so the hosts follow the same primary and fallback design as the PDC emulator. To sync from the PDC emulator instead, replace the peer list with the PDC emulator’s name or IP address, and optionally add another domain controller with the 0xb flag as a fallback. Use IP addresses if the hosts don’t use the domain’s DNS servers.

Domain Member Virtual Machines

VMICTimeProvider is enabled by default on every Hyper-V VM, not just domain controllers, so domain-joined member VMs take their time from the host instead of the domain hierarchy. With accurate hosts, that works, but it creates a second time root. Domain controllers follow the PDC emulator, while member VMs follow whichever host they run on. In my lab, a member VM was about 77 milliseconds off the PDC emulator, even though both its host and the PDC emulator synced with Cloudflare. If a host loses access to its time source, its VMs drift away from the domain controllers, which is the original problem in a new place. The Domain Member Time Settings GPO prevents this. It disables only the W32Time provider, not the Hyper-V time synchronization integration service, so VMs still get their clock set at startup and after a restore from a saved state.

Validating the Configuration

Once everything is in place, confirm each tier of the hierarchy is getting time from the right place, including the domain controllers, domain members, the Hyper-V hosts, and the domain as a whole.

Validating Domain Controllers

Run the following commands to check the time configuration and status of every domain controller.

Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
Write-Output "=== $env:COMPUTERNAME ==="
w32tm.exe /query /configuration | Select-String 'Type:|NtpServer:|AnnounceFlags:' | ForEach-Object { $_.Line.Trim() }
w32tm.exe /query /status | Select-String 'Stratum:|Root Dispersion:|Source:' | ForEach-Object { $_.Line.Trim() }
Write-Output "VMICTimeProvider Enabled: $(Get-ItemPropertyValue -Path 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider' -Name Enabled)"
}
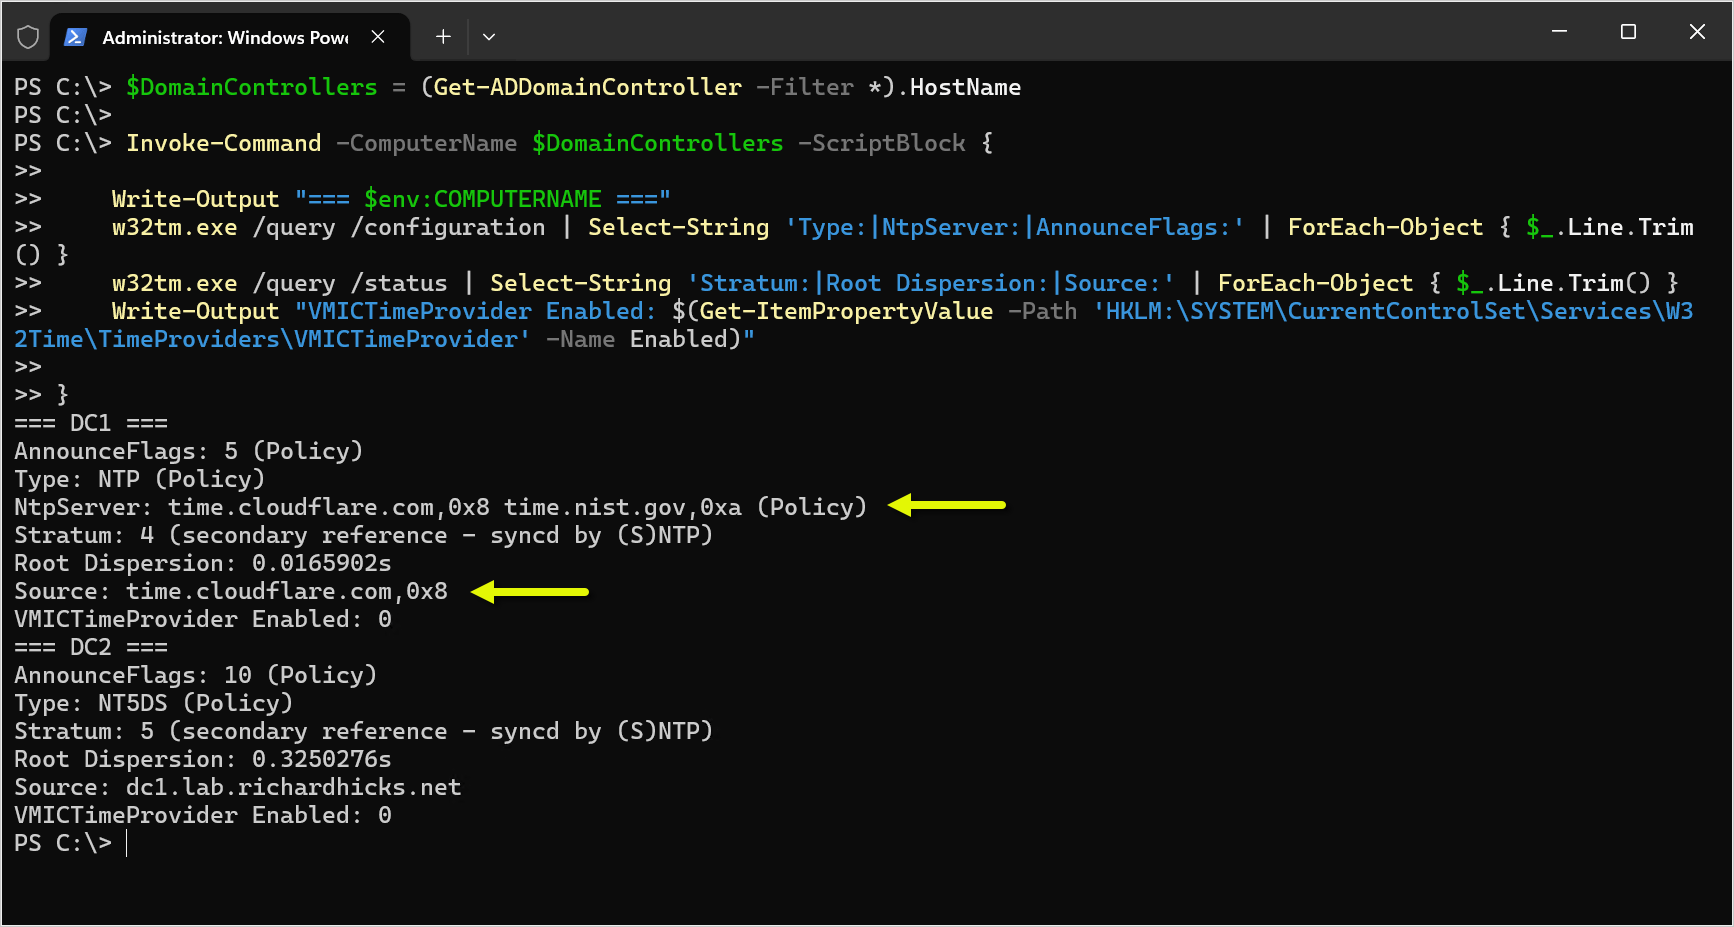
PowerShell output validating W32Time configuration on each domain controller

Validating domain controller time configuration settings.

The .Line.Trim() is there for a reason. Select-String results returned through Invoke-Command are deserialized objects that PowerShell can’t format, so without it you’ll see blank lines instead of the output. The following table shows what to look for on each type of server.

ServerTypeAnnounceFlagsSourceStratumVMICTimeProvider
PDC emulatorNTP (Policy)5 (Policy)time.cloudflare.com,0x840
Other domain controllersNT5DS (Policy)10 (Policy)PDC emulator50
Hyper-V hostsNTP (Local)n/atime.cloudflare.com,0x94n/a

The (Policy) label confirms Group Policy is in control rather than local settings. Root Dispersion will be high immediately after the service restarts and should settle under a second within about 30 minutes. NtpServer lists both time services, but the source should show time.cloudflare.com. If it shows time.nist.gov, the PDC emulator can’t reach Cloudflare and has switched to the fallback.

Validating Domain Members

On a domain member VM, run the following commands to confirm it follows the domain hierarchy and agrees with the PDC emulator.

w32tm.exe /query /source
w32tm.exe /query /status | Select-String 'Stratum:|Source:|ReferenceId:'
w32tm.exe /stripchart /computer:$Pdc /samples:5 /dataonly
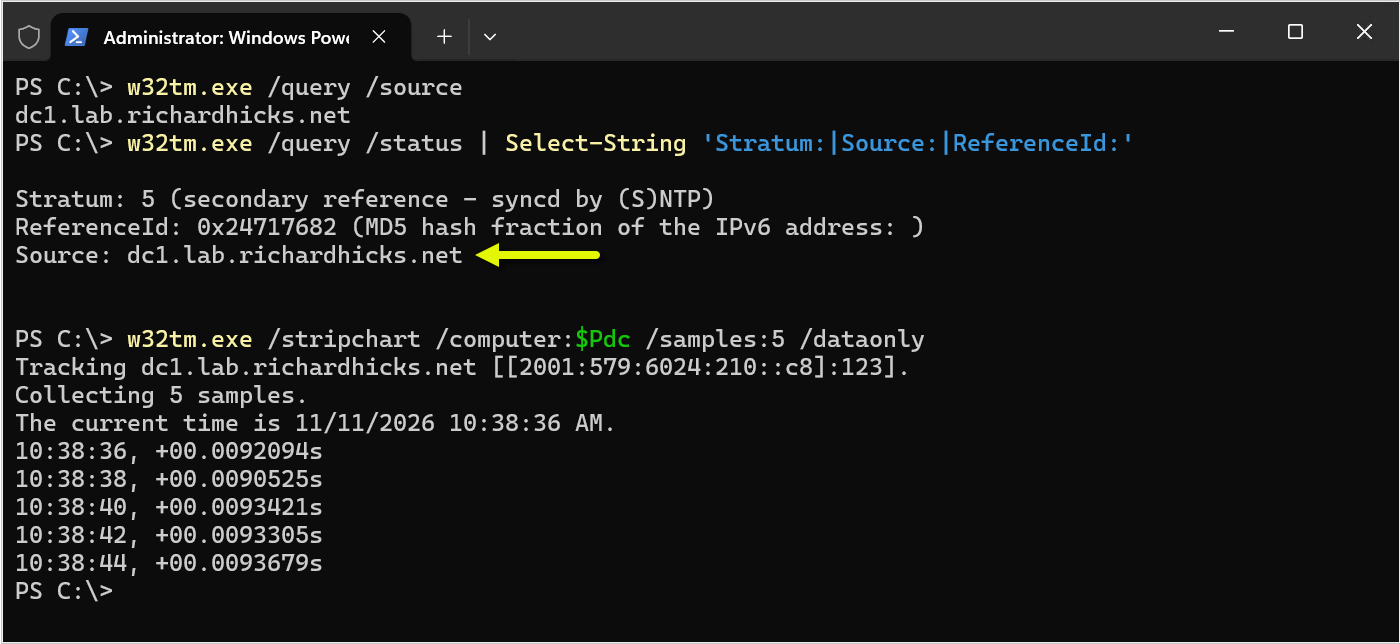
w32tm.exe output on a domain member VM synchronizing with the PDC emulator dc1

Domain member VM synchronizing with the PDC emulator.

The source should be a domain controller, not VM IC Time Synchronization Provider, and the stratum should be one or two levels below the PDC emulator. In my lab, a member VM went from about 77 milliseconds off the PDC emulator to under 10 milliseconds within minutes of switching to the domain hierarchy.

Validating Hyper-V Hosts

On the Hyper-V hosts, run the following commands locally.

w32tm.exe /query /source
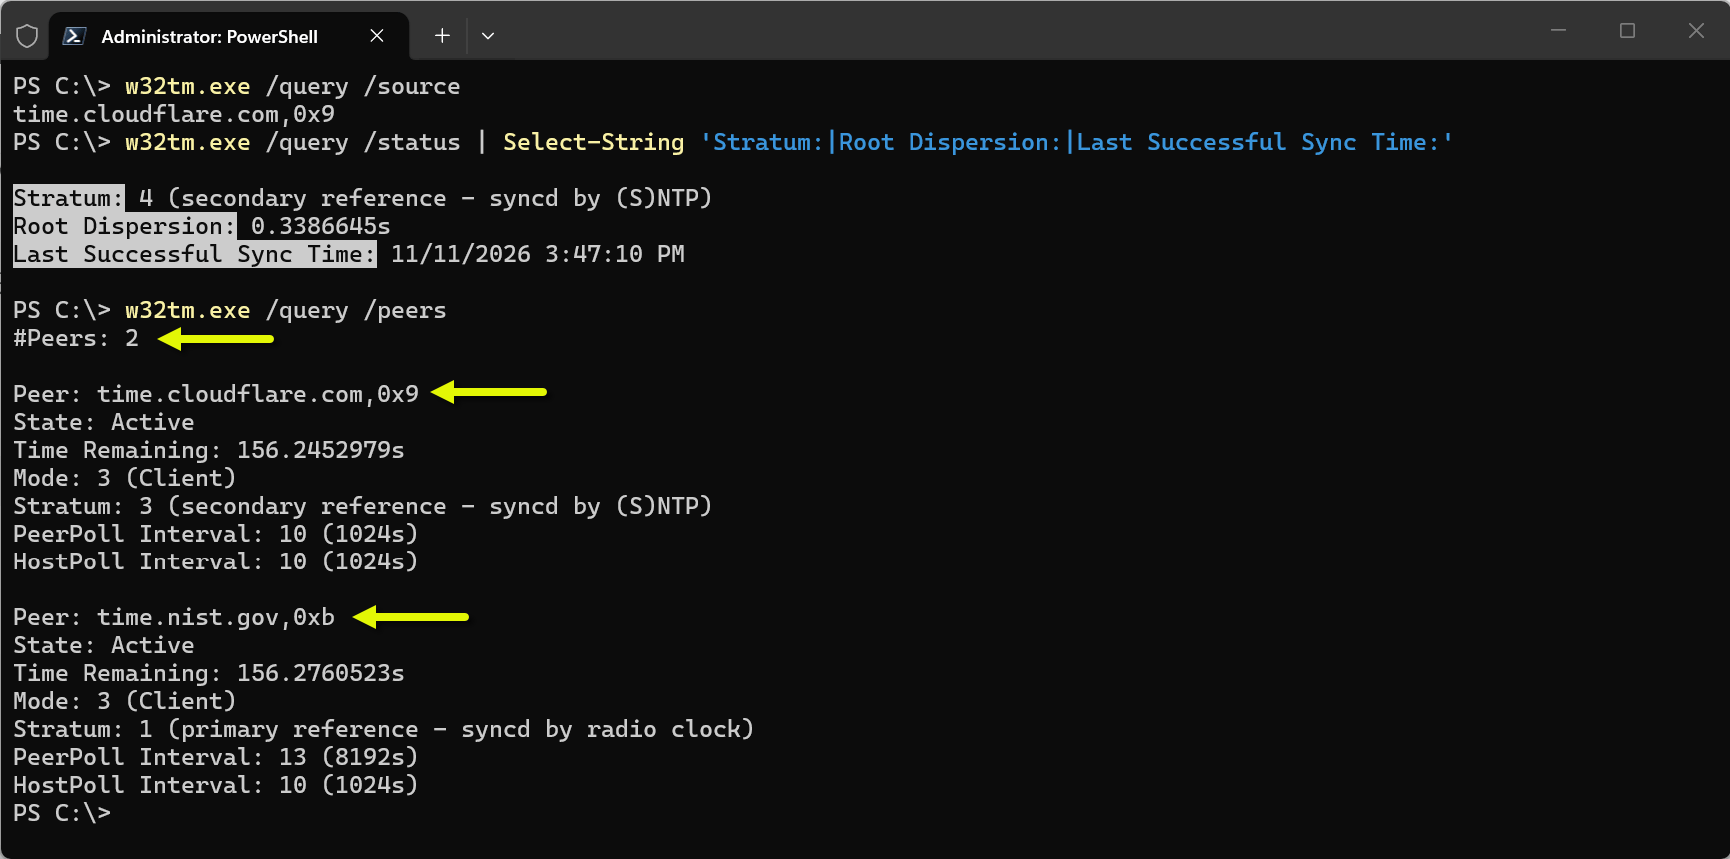
w32tm.exe /query /status | Select-String 'Stratum:|Root Dispersion:|Last Successful Sync Time:'
w32tm.exe /query /peers
w32tm.exe output on a Hyper-V host synchronizing with time.cloudflare.com, with time.nist.gov as a fallback peer

Time synchronization settings on the Hyper-V host server.

Both time services are listed as peers. The State for time.cloudflare.com should be Active. A state of Pending that persists usually means the host can’t reach that time server. However, Pending is also normal for up to one polling interval after the service restarts, which is about 17 minutes with a SpecialPollInterval of 1024 seconds, because W32Time rebuilds its peer list and resets the peer statistics. To tell the difference, run w32tm.exe /query /peers /verbose and check LastSyncError. A value of 0x00000000 (Succeeded) means the last sync worked, and the peer will return to Active at its next poll.

Validating the Domain

After things have had time to settle, check the entire domain at once. Every domain controller should show a small offset relative to the PDC emulator, with no errors.

w32tm.exe /monitor /domain:$DomainFqdn
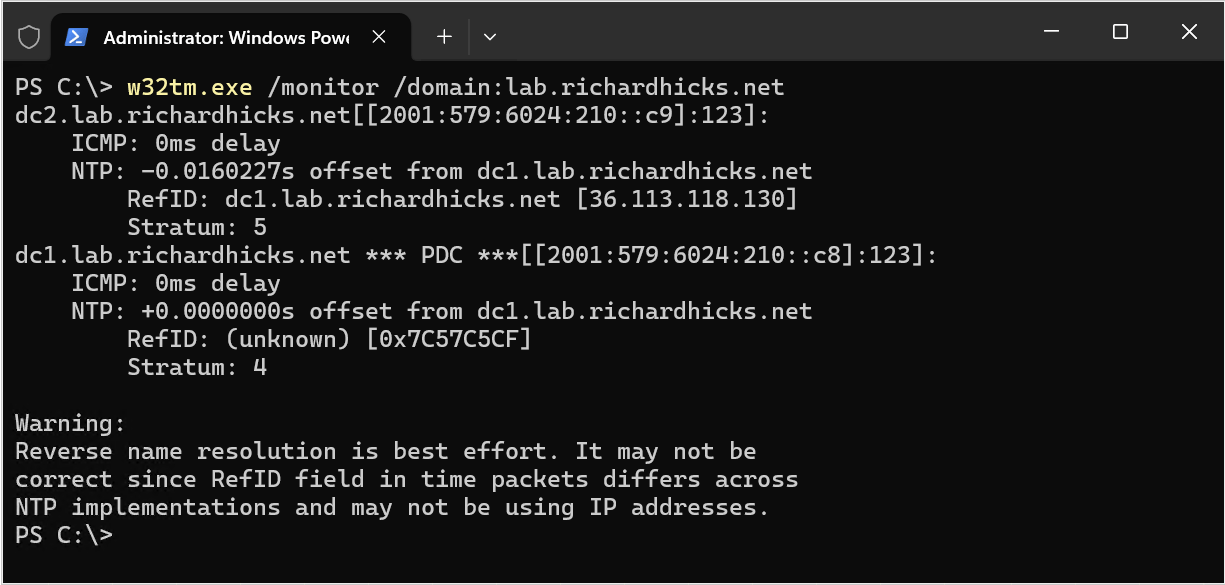
w32tm.exe /monitor output showing all domain controllers in sync with the PDC emulator

All domain controllers synchronizing with the PDC emulator.

You might notice an unusual IPv4 address listed for dc1, such as 36.113.118.130. That’s not dc1’s address, and it’s not a real IPv4 address at all. It’s the RefID, which identifies the server’s upstream time source. The NTP reference ID field is only 32 bits, so when the source is reached over IPv6, as time.cloudflare.com is here, the field contains the first 32 bits of the MD5 hash of the source’s IPv6 address, as defined in RFC 5905. It’s expected behavior and can safely be ignored. In my lab, the PDC emulator went from roughly 840 milliseconds off UTC to closely tracking UTC once it began syncing with Cloudflare. In the customer’s environment, the Kerberos anomalies stopped once all domain controllers and hosts converged on a single source.

Summary

Time synchronization is easy to overlook, especially in virtualized environments where Hyper-V quietly fills in the gaps. In this case, the symptoms showed up as Kerberos anomalies during an AD CS engagement, but the root cause was a domain with no single, authoritative time source. The fix came down to the following steps.

  1. Reset every domain controller to the default W32Time configuration.
  2. Configure the PDC emulator, and only the PDC emulator, to sync with a reliable public time service, plus a second as a fallback, using a WMI-filtered GPO.
  3. Configure all other domain controllers to follow the domain hierarchy and disable VMICTimeProvider on every domain controller with a second GPO.
  4. Disable VMICTimeProvider on domain members with a third GPO linked to the domain root, so virtual machines follow the domain hierarchy too.
  5. Allow outbound UDP 123 for the systems that sync externally.
  6. Explicitly configure any workgroup Hyper-V hosts, since they don’t participate in the domain hierarchy.

With Group Policy managing the domain controllers and domain members, the configuration is consistent, self-documenting, and follows the PDC emulator role automatically if it ever moves.

Additional Information

Windows Time Service Technical Reference

Windows Time Service Tools and Settings

Synchronizing Time on Virtualized AD DS Environments: VMICTimeProvider vs AD

Configure the Root PDC with an Authoritative Time Source and Avoid a Widespread Time Skew

Cloudflare Time Services

NTP Pool Project

NIST Internet Time Service (ITS)

Network Time Protocol Version 4 (RFC 5905)

90 DAYS LEFT: Windows Server 2016 End of Life January 2027 – Plan Your AD CS Migration Now

Heads up, fellow Windows Server administrators! There are now just THREE MONTHS remaining before Windows Server 2016 reaches end of support, so now is the time to finalize any migrations for workloads hosted on this platform. Mainstream support ended on January 11, 2022, and Windows Server 2016 has since remained in extended support. However, extended support ends on January 12, 2027. After that date, Microsoft will no longer provide security updates or technical support, increasing the risk of running production workloads due to exposure to newly discovered vulnerabilities and exploits.

Active Directory Certificate Services

Many organizations are still running critical infrastructure on Windows Server 2016. Administrators often delay upgrading Microsoft Active Directory Certificate Services (AD CS) due to its complexity. However, a well-planned AD CS migration not only reduces risk but also provides an opportunity to modernize cryptography, certificate templates, and operational practices.

Certificate Authorities

Administrators must carefully migrate Certificate Authorities (CAs) running on Windows Server 2016 to minimize downtime. In environments where ongoing CA maintenance has been limited, migrating the CA database can be especially challenging. If the CA is installed on a domain controller, now is a good time to consider separating these services to ensure reliable operation. Also, it’s a good idea to evaluate the CA’s configuration and security posture during migration to enhance security and improve service resilience.

NDES Servers

Microsoft Network Device Enrollment Services (NDES) servers, commonly deployed to facilitate certificate enrollment via Microsoft Intune, pose a unique challenge during migration. Unfortunately, configuring NDES is exceedingly complex and error-prone. NDES relies on a delicate combination of specialized IIS configuration, AD service accounts, custom certificate templates, and CA permissions, making even minor changes risky without proper planning. Not surprisingly, administrators are often hesitant to touch these systems as they are notoriously difficult to troubleshoot when problems arise.

Pro Tip: We spend an entire day covering NDES configuration in the Mastering Enterprise PKI Certificates with Microsoft Intune training course. The next session is February 3-5, 2027. Register now!

Intune Certificate Connectors

Don’t overlook Windows Server 2016 servers with the Intune Certificate Connector installed. Fortunately, this is one of the more manageable workloads to migrate. All that’s required is to install new connectors on supported servers and delete the old ones.

Summary

With extended support for Windows Server 2016 ending on January 12, 2027, organizations running production workloads—especially critical infrastructure such as Active Directory Certificate Services (AD CS), Certificate Authorities (CAs), and NDES servers—face significant security risks from unpatched vulnerabilities once the OS reaches end-of-life. Careful migration planning to newer versions such as Windows Server 2022 or 2025 is essential to minimize downtime, improve security posture, and ensure long-term resilience.

Start Planning Now

Don’t risk running unsupported workloads in 2027! Complete your migration today. If you’d like expert guidance, I have many years of experience migrating these workloads. I have developed specialized tools and techniques to ensure a smooth, secure, and successful transition. Fill out the form below to schedule a free one-hour consultation to assess your Windows Server 2016 AD CS workloads, identify migration risks, and outline next steps.

Additional Information

Windows Server 2016 Lifecycle Policy

PKI Fundamentals with Microsoft Active Directory Certificate Services (AD CS) Online Training Course

Mastering Enterprise PKI Certificates with Microsoft Intune Online Training Course

Live! 360 Event Orlando, Florida 2026

I’m excited to announce that I’ll be attending the upcoming Live! 360 Event, November 15-20, 2026, at Royal Pacific Resort at Universal Orlando, Florida. I’ll be in attendance all week and will be delivering a few talks at the event this year.

Sessions

I’ll be presenting two sessions at this year’s event. They are:

Join Me!

If you are planning to attend the event, please join my sessions! I will be at the conference center all week, so don’t hesitate to reach out and contact me while you are there. I’m looking forward to seeing everyone soon!

NDES Security Hardening: Protecting and Monitoring the SCEP Registry Configuration

The Active Directory Certificate Services (AD CS) Network Device Enrollment Service (NDES) is widely deployed to support the issuance and management of enterprise PKI certificates via Microsoft Intune and the Intune Certificate Connector. NDES relies on registry settings to identify its issuing CA, certificate templates, and other SCEP configuration parameters. An attacker with sufficient access to an NDES server could alter these settings and redirect enrollment to another template published on the issuing CA and accessible to the NDES service account. Because enrollment might continue without an obvious service failure, administrators could overlook the change. This article explains how to restrict access to the MSCEP registry key, audit modifications, and use Sysmon to collect additional investigative context.

Understanding the MSCEP Registry Configuration

NDES stores its core SCEP configuration under the HKLM\SOFTWARE\Microsoft\Cryptography\MSCEP registry key. These settings identify the issuing CA and certificate templates used for enrollment and control other aspects of NDES operation. Because they directly influence how certificate requests are processed, unauthorized changes could alter enrollment behavior without modifying the NDES application itself.

Enrollment Templates

NDES uses the following registry values to identify the certificate templates used for SCEP enrollment.

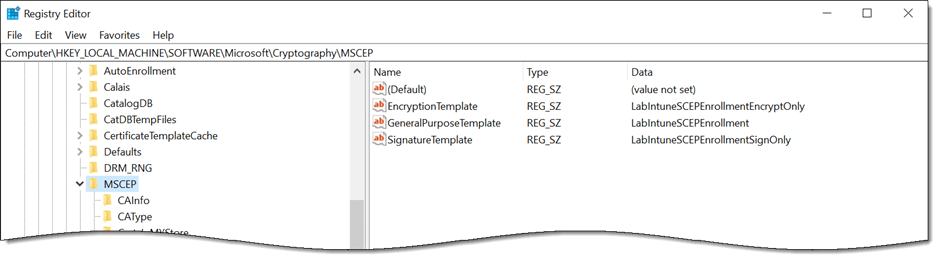
HKLM\SOFTWARE\Microsoft\Cryptography\MSCEP\EncryptionTemplate
HKLM\SOFTWARE\Microsoft\Cryptography\MSCEP\GeneralPurposeTemplate
HKLM\SOFTWARE\Microsoft\Cryptography\MSCEP\SignatureTemplate

MSCEP registry key with the EncryptionTemplate, GeneralPurposeTemplate, and SignatureTemplate values

In many deployments, all three values reference the same template. If the environment supports distinct signature, encryption, or general-purpose enrollment scenarios, each value can reference a template designed for that specific purpose.

Additional MSCEP Settings

The MSCEP key contains more than certificate template assignments. Its CAInfo and CAType subkeys identify the CA to which NDES submits requests, while other subkeys control settings such as the hash algorithm and capabilities advertised to SCEP clients.

Information Disclosure and Reconnaissance

The default permissions for the MSCEP registry key are inherited from HKLM\SOFTWARE, which grants the local Users group read access. This allows locally authenticated users, as well as users granted remote registry access, to read the template names and CA configuration. Template names can aid reconnaissance, as an attacker can query Active Directory for the corresponding template definitions and evaluate their configurations against known AD CS escalation techniques. The CAInfo subkey can also disclose the internal fully qualified domain name of the issuing CA. Restricting access to the MSCEP key reduces unnecessary exposure of this information.

Why the MSCEP Key Is an Effective Monitoring Target

After NDES is deployed to production, these values should change only during planned reconfiguration. This makes the MSCEP key a high-value, low-noise monitoring target. Legitimate modifications should be rare and documented, while any unexpected change warrants immediate investigation.

Before You Begin

The changes described in this article modify access permissions and configure auditing for registry settings that NDES requires. An incorrect service identity, incomplete allowlist, or unsupported environmental assumption can prevent certificate enrollment. Test these changes in a nonproduction environment first, confirm that you have a working backup and rollback procedure, and validate successful enrollment before applying them broadly. Adapt the examples to your environment and follow your organization’s change management and security review processes.

In addition, be sure to back up the configuration before making any changes. A full server backup or a virtual machine snapshot is helpful. However, administrators can perform additional steps to save information before altering the default settings.

Determine the NDES Service Account

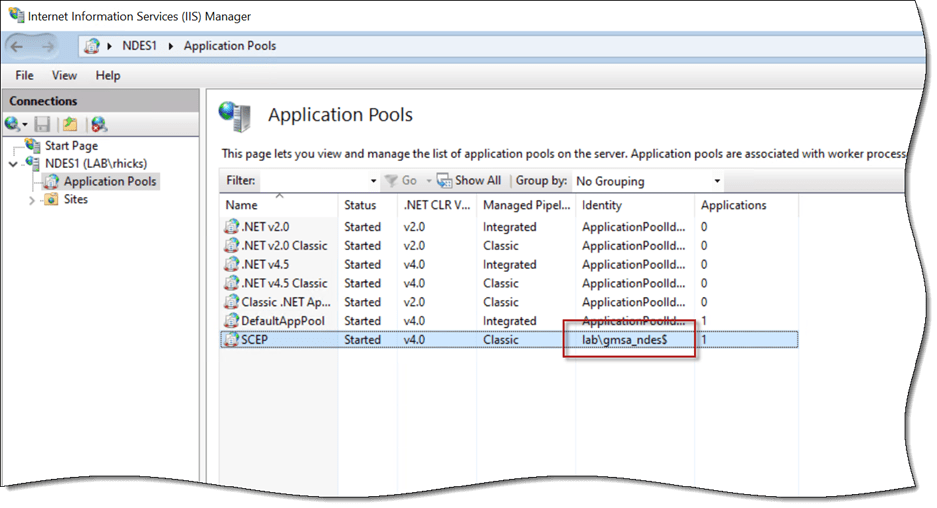
The permissions applied below grant access to the account used by the SCEP application pool. Confirm this account before proceeding by opening IIS Manager (inetmgr.exe), expanding the IIS server, and selecting Application Pools. Highlight the SCEP application pool and note the account shown in the Identity column.

IIS Manager application pools showing the SCEP application pool identity

Back Up the Current Permissions

A registry export with reg.exe captures data but not the security descriptor, so it is not a rollback for this change. Run the following PowerShell commands to capture the descriptor in SDDL format instead.

$Key = 'HKLM:\SOFTWARE\Microsoft\Cryptography\MSCEP'
(Get-Acl -Path $Key -Audit).Sddl | Out-File -FilePath .\mscep-acl-backup.txt -Encoding utf8

The rollback process is covered later in this post.

Restricting Access to the MSCEP Key

For a dedicated NDES server, restrict the MSCEP key to SYSTEM, the local Administrators group, and the identity used by the SCEP application pool. All other access entries should be removed, including the inherited Read permission for the local Users group. If another service identity requires access in your environment, such as a domain service account used by the Intune Certificate Connector, account for it in both the explicit access rules and the allowlist before applying the changes.

Administrators must retain full control. Even if the Administrators entry were removed, a local administrator could exercise the necessary privileges to take ownership of the key and rewrite its permissions. The ACL therefore reduces unnecessary access but does not provide a security boundary against a local administrator or an attacker with equivalent privileges. This is why the auditing described in the next section is an important complementary control.

Important Note: Registry values do not carry their own security descriptors, so the permissions applied here govern the MSCEP key, every value in it, and every subkey beneath it. The service identity is granted full control rather than read because NDES writes to this key during normal operation, and read-only access will break it.

Removing Inheritance

The inherited entries from HKLM\SOFTWARE are where the broad access comes from, so they must be removed first. On the NDES server, open an elevated PowerShell command window and run the following commands.

$Acl = Get-Acl -Path $Key -Audit
$Acl.SetAccessRuleProtection($True, $False)

The -Audit parameter reads the system access control list (SACL) and the discretionary access control list (DACL), so both can be updated and committed in a single write later. The second parameter of SetAccessRuleProtection is set to false, which discards the inherited entries rather than converting them to explicit copies. This approach is intentional. Inherited entries cannot be removed with the PurgeAccessRules method, so preserving them would leave the broad grants in place and defeat the entire exercise. No explicit deny entry is required anywhere in this process. After this change, the local Users group has no access to the key at all.

Granting Explicit Access

Breaking inheritance also removes the SYSTEM and Administrators grants, so our explicit entries will replace them. Well-known security identifiers (SIDs) are used instead of account names, so this works correctly on non-English Windows installations.

$ServiceIdentity = 'corp\gmsa_ndes$'   # or 'corp\svc_ndes' if using a domain service account
$Sid = (New-Object System.Security.Principal.NTAccount($ServiceIdentity)).Translate([System.Security.Principal.SecurityIdentifier])
ForEach ($Identity in @('S-1-5-18', 'S-1-5-32-544', $Sid.Value)) {
    $Trustee = New-Object System.Security.Principal.SecurityIdentifier($Identity)
    $Acl.AddAccessRule((New-Object System.Security.AccessControl.RegistryAccessRule($Trustee, 'FullControl', 'ContainerInherit', 'None', 'Allow')))
}

S-1-5-18 is the well-known SID for SYSTEM, and S-1-5-32-544 is the well-known SID for the local Administrators group. ContainerInherit ensures the rights propagate to the subkeys.

Removing Unapproved Access Entries

The remaining explicit entries are evaluated against an allowlist, and anything that does not belong to those three identities is purged.

$AllowedSids = @('S-1-5-18', 'S-1-5-32-544', $Sid.Value)
ForEach ($Entry in ($Acl.Access | Where-Object { -not $_.IsInherited } | Select-Object -ExpandProperty IdentityReference -Unique)) {
    If ($Entry -is [System.Security.Principal.SecurityIdentifier]) {
        $EntrySid = $Entry
}
Else {
        $EntrySid = $Entry.Translate([System.Security.Principal.SecurityIdentifier])   
}
   
If ($AllowedSids -notcontains $EntrySid.Value) {
        $Acl.PurgeAccessRules($EntrySid)   
}
}

Sweeping against an allowlist rather than purging a fixed list of known principals removes application capability SIDs, CREATOR OWNER, any application pool entry that no longer matches the current SCEP application pool service account, and anything left over from previous administrative changes, without enumerating them in advance. It also makes the operation repeatable, so running it a second time on an already hardened server produces the same result.

Important Note: This code uses SID comparison. Identity references can be returned as either an NTAccount or a SecurityIdentifier, depending on whether the account resolves, so comparing by name will silently miss orphaned entries.

Auditing Changes to the MSCEP Key

Restricting the ACL reduces unnecessary access, but it cannot prevent a local administrator from taking ownership or rewriting the permissions. Auditing provides a complementary detective control by recording attempts to modify the key.

Add the Registry Audit Rule

To enable auditing, add an audit rule to the MSCEP key’s SACL that records successful and failed attempts by any identity to modify its values, subkeys, or permissions. Then commit the DACL and SACL together.

$Everyone = New-Object System.Security.Principal.SecurityIdentifier('S-1-1-0')
$AuditRule = New-Object System.Security.AccessControl.RegistryAuditRule($Everyone, 'SetValue, CreateSubKey, Delete, ChangePermissions, TakeOwnership', 'ContainerInherit', 'None', 'Success, Failure')
$Acl.AddAuditRule($AuditRule)
Set-Acl -Path $Key -AclObject $Acl

The audited operations are limited to changes. Specifically, setting a value, creating or deleting a subkey, changing permissions, and taking ownership. Reads are intentionally not audited. The three identities that still have access read these values routinely, so auditing that activity would generate excessive noise. Note that failure auditing applies only to the listed modification rights, so a denied read attempt will not be logged.

In addition, TakeOwnership and ChangePermissions are included deliberately because an attempt to alter the key’s security descriptor could indicate that someone is trying to weaken or bypass the applied controls. These operations should be rare after deployment and warrant investigation when they are not associated with an approved administrative change.

Recycle the SCEP Application Pool

Once the permissions are committed, recycle the SCEP application pool to close any existing registry handles and ensure the worker process reopens the MSCEP key under the new access controls.

Restart-WebAppPool -Name SCEP

Enable the Registry Audit Subcategory

An audit rule on its own does not generate events. The Object Access category must have the Registry subcategory enabled before Windows will write anything to the Security event log. Confirm the current setting by running the following command.

auditpol.exe /get /subcategory:"{0CCE921E-69AE-11D9-BED3-505054503030}" /r

The subcategory is referenced by GUID rather than by name for locale independence. If it is not enabled, enable it through Group Policy under Advanced Audit Policy Configuration > Object Access > Audit Registry rather than setting it locally, so the setting survives and applies consistently across your NDES infrastructure.

Recommended Security Alerts

With the Registry audit subcategory and the SACL configured as described, creating, deleting, or modifying a registry value under the MSCEP key generates event ID 4657 in the Security event log, identifying the account, the value name, and both the old and new data. That last detail is what makes the event immediately actionable. You do not have to look up what the template was supposed to be, because the event tells you what it was and what it was changed to.

My recommendation is to alert on every event ID 4657 associated with EncryptionTemplate, GeneralPurposeTemplate, or SignatureTemplate values rather than attempting to tune out individual processes or accounts. These values should remain static after deployment, so their expected change volume is zero. Monitor modifications elsewhere under the MSCEP path as well but establish a baseline before treating every such event as an alert because some NDES configurations may update other values or subkeys during normal operation.

Additional Alerts

Two additional events are worth correlating when one of these fires:

  • Event ID 4670 records a change to the permissions on the object. On a hardened key, this is a strong signal, since it means someone modified the ACL you just applied.
  • An application pool recycle or an IIS restart shortly after a value change is the corroborating signal. Because NDES caches the template configuration in the worker process, a substituted template does not take effect until the SCEP application pool or server restarts. An attacker seeking immediate activation would therefore need to trigger a recycle or restart, creating another potentially observable event. Otherwise, the change could take effect later during a routine recycle or restart.

Add Process Context with Sysmon

Security event ID 4657 identifies the account, process name, process ID, registry value, and old and new data associated with a change. However, it does not provide the full command line, process lineage, hashes, or surrounding activity needed for a more complete investigation. The System Monitor (sysmon.exe) utility from the Microsoft Sysinternals suite supplements the Security event log with this information.

Sysmon is not a replacement for SACL. The Security event records the authorization decision as Windows made it, which is the authoritative record. Sysmon records the process lineage around that decision. The two sources are complementary. Sysmon can capture the process that triggers an application pool recycle or an IIS restart when that activity matches the configured process creation rules.

Sample Sysmon Configuration for NDES

I have published a sample Sysmon configuration for NDES servers on GitHub. It is available here. This targeted configuration monitors SCEP enrollment settings, IIS application pool activity, registration authority certificates and private keys, credential access, and selected AD CS, certificate store, IIS, and operating-system security events relevant to an NDES deployment. It is not intended to serve as a general enterprise baseline. You can run it as a standalone configuration on an NDES server or merge its rule groups into an existing baseline such as SwiftOnSecurity or Olaf Hartong sysmon-modular.

Install or Update Sysmon

After reviewing and testing the sample configuration, install Sysmon or apply the configuration to an existing Sysmon deployment. To install Sysmon, open an elevated command window and run the following command.

sysmon.exe -accepteula -i sysmon-ndes.xml

To update an existing installation and confirm the active configuration, run the following commands.

sysmon.exe -c sysmon-ndes.xml
sysmon.exe -c

Sysmon events are written to the following event log location.

Applications and Services Logs > Microsoft > Windows > Sysmon > Operational.

Sysmon Monitoring Coverage

The configuration is centered on detecting changes to security-sensitive registry locations. The remaining rules capture the process, file, network, and system activity needed to investigate those changes.

  • Registry events 12, 13, and 14 cover the MSCEP key and its subkeys using a contains condition so both the native and WOW6432Node paths are captured. The same rule group covers the Certificate Services configuration key, machine certificate stores and trust anchors, SCHANNEL and TLS configuration, IIS service configuration, and common persistence locations.
  • Process creation events capture the tools used to make these changes, including reg.exe, regedit.exe, certutil.exe, appcmd.exe, and iisreset.exe. Tools such as appcmd.exe and iisreset.exe, as well as PowerShell commands such as Restart-WebAppPool, can recycle the SCEP application pool or restart IIS, allowing a modified template configuration to take effect. Sysmon can capture these actions when the initiating process and command line match the configured process-creation rules. PowerShell Script Block Logging provides additional visibility into commands executed within an existing PowerShell session, which might not be captured as separate Sysmon process-creation events.
  • Process access events are restricted to handle requests against LSASS with the access masks commonly associated with credential dumping. On a host that holds registration authority private keys and runs under a gMSA identity, this is the single highest-value rule.
  • File creation and deletion events cover the private key containers under Crypto\RSA, Crypto\Keys, and Crypto\PCPKSP, the IIS configuration directory, and certificate file extensions. Web content extensions such as .aspx and .ashx are also included, because a file with one of those extensions appearing under the NDES site is a strong indicator of a web shell.
  • Network connection events are purposefully scoped to scripting hosts and file transfer utilities rather than everything. An NDES server constantly talks to the CA and enrolling clients, and logging all of it produces excessive noise and provides little insight.
  • Named pipe, WMI, and process tampering events are also included. Legitimate volume for these is close to zero on a dedicated NDES server, so they are logged in full.

Note: The registry rule group includes an exclusion for the highest-volume legitimate writers, such as services.exe, svchost.exe, and TrustedInstaller.exe, as well as CreateKey events. Without those exclusions, useful events are buried within minutes. However, broad process-based exclusions can create visibility gaps. Administrators should validate that those exclusions do not suppress meaningful changes to the monitored paths.

Correlating Sysmon and Security Log Events

When a template value is modified, the Security event log records event ID 4657 with the account, value name, and old and new data. Sysmon records event ID 13 for the same operation, including the image path and process GUID associated with the write. If Sysmon also captured the corresponding process-creation event, the process GUID can be used to correlate event ID 13 with event ID 1, which provides the full command line and parent-process information. The Security event identifies the audited account and registry change, while Sysmon supplies richer process lineage and surrounding activity.

Sysmon event recording a change to the MSCEP registry key

Sysmon Deployment Considerations

Before deploying this configuration, confirm that it is compatible with your installed Sysmon version and existing monitoring baseline. Test it on a representative NDES server first, then review the resulting event volume and adjust only those rules that conflict with known, legitimate activity.

  • Confirm the schema version supported by your installed Sysmon build by running
    sysmon.exe -s before deployment. The sample configuration uses schema version 4.90 and therefore requires Sysmon 15 or later.
  • The FileBlockExecutable rules actively block matching executable files rather than merely recording their creation. Review and test these rules carefully before deploying the configuration in production.
  • If you already run a Sysmon baseline, merge these rule groups into it rather than installing this configuration over the top of it. Installing a new configuration replaces the existing one entirely.
  • Forward both the Sysmon Operational event log and the Security event log to your Security Information and Event Management (SIEM) platform. Local event logs on a compromised server hosting an Internet-published SCEP endpoint are of limited investigative value, and an alert that nobody receives provides little protection.
  • Validate the configuration in a lab first. Sysmon rule evaluation order is not always intuitive, and an overly broad include rule on a busy server can generate a surprising amount of data.

NDES Operational Considerations

Tightening permissions on a key that a running service depends on has consequences worth understanding before you make these changes in production.

  • If the Intune Certificate Connector service runs as a custom account rather than SYSTEM, add that account to the allowlist and grant it read access. Check the logon account on the connector service before you begin. In this scenario, I recommend running the Intune Certificate Connector as SYSTEM to follow security best practices.
  • If you change the SCEP application pool identity later, NDES will fail until the key permissions are updated to include the new identity. These permissions are aligned to a specific account, so any change to that account requires a corresponding change here.
  • If you operate multiple NDES servers, apply these changes to all of them to ensure full coverage.
  • Document any planned change to the template configuration in your change management process. If you alert on these events as recommended, someone will need to close the ticket the alert generates.

Validate Permissions, Auditing, and Enrollment

Run the following PowerShell command to verify the resulting access rules.

(Get-Acl -Path $Key).Access | Format-Table IdentityReference, RegistryRights, IsInherited

PowerShell output of the MSCEP registry key permissions

Only SYSTEM, BUILTIN\Administrators, and the NDES service account identity should be listed, and none of the entries should be inherited. Next, run the following command to confirm the audit rule is present.

(Get-Acl -Path $Key -Audit).Audit

PowerShell output of the MSCEP registry key audit settings

With the Registry audit subcategory enabled, perform a controlled test in a lab by changing a template value and recycling the SCEP application pool. Verify that event ID 4657 appears in the Security event log and includes the expected old and new values.

Security event ID 4657 recording a registry value change

Event ID 4657 details with the old and new registry values

If event ID 4657 does not appear in the Security event log after you modify a registry value under the MSCEP key, confirm that the Registry audit subcategory is enabled.

auditpol.exe /get /subcategory:"{0CCE921E-69AE-11D9-BED3-505054503030}"

auditpol output showing the Registry audit subcategory setting

If you deployed the Sysmon configuration, confirm it is loaded and generating events. Sysmon events are recorded in the Applications and Services Logs > Microsoft > Windows > Sysmon > Operational event log. The log should include events related to the test, including the registry value modification. Depending on how the application pool was recycled and which process-creation rules are enabled, it might also contain the process that initiated the recycle.

Sysmon event for the SCEP application pool recycle

You will also find events containing process creation details, including the full command line, process ID, parent process ID, and related information.

Sysmon process creation event details

Sysmon process creation event showing the command line and parent process

Finally, perform a device enrollment. Certificate enrollment should remain unaffected by these changes, and confirming successful enrollment after making these changes is essential before returning the NDES server to production.

Restore the Previous Registry Permissions

If enrollment breaks and the cause is not immediately obvious, administrators can restore the security descriptor captured earlier by running the following PowerShell commands.

$Sddl = Get-Content -Path '.\mscep-acl-backup.txt' -Raw
$Acl = Get-Acl -Path $Key -Audit
$Acl.SetSecurityDescriptorSddlForm($Sddl.Trim())
Set-Acl -Path $Key -AclObject $Acl
Restart-WebAppPool -Name SCEP

In practice, the most common cause of failure is granting access to the wrong service identity. This is why confirming the application pool identity is the first step in this process. Administrators should not skip this validation step.

Summary

The MSCEP registry values determine which certificate templates NDES uses for SCEP enrollment. An attacker with administrative access to the NDES server could modify these values and redirect enrollment to an unintended template without creating an obvious service failure. Restricting access to the MSCEP key reduces unnecessary exposure, while registry auditing and Sysmon provide visibility into unauthorized changes and the processes responsible for them. Forward these events to your SIEM, configure alerts for unexpected modifications, and validate the detection workflow before relying on it in production.

Additional Information

Sample Sysmon Configuration for NDES on GitHub

Download Sysmon from Microsoft Sysinternals

Microsoft NDES Information Disclosure: Detection and Remediation

Get-NdesNtlmDisclosure PowerShell Script on GitHub

Configure Infrastructure to Support SCEP with Microsoft Intune

Publish NDES with Microsoft Entra Application Proxy

Microsoft NDES Information Disclosure: Detection and Remediation

The Active Directory Certificate Services (AD CS) Network Device Enrollment Service (NDES) is a common building block for certificate deployment with Microsoft Intune. When NDES is used with the Intune Certificate Connector, the NDES server is published to the Internet so that managed devices can enroll for certificates using the Simple Certificate Enrollment Protocol (SCEP). Anything accessible via the Internet warrants careful attention, and a default NDES installation can expose more information than administrators might expect. Specifically, the NDES administration page can disclose sensitive information and should be removed. However, removing access to the page isn’t enough. Even after the NDES administration page is removed, IIS can continue to expose Windows authentication on that path through orphaned configuration entries, enabling NTLM-based information disclosure to unauthenticated Internet clients.

NDES Administration Page

NDES exposes its web-based functionality through applications hosted in Internet Information Services (IIS). A default NDES installation creates two IIS applications under the CertSrv virtual directory. The first is mscep, which is the SCEP endpoint itself. The second is mscep_admin, which is the NDES administration page used to generate one-time challenge passwords.

NDES IIS virtual directories mscep and mscep_admin

Standalone Configuration

In a standalone NDES deployment, an administrator browses to the administration page, authenticates, and receives a one-time password that is embedded in the certificate request. NDES validates the password against its local cache before forwarding the request to the certification authority (CA).

Intune Certificate Connector

The Intune Certificate Connector does not use this mechanism. Intune generates its own challenge, and the NDES policy module installed by the connector validates the certificate request against the authorizations Intune has granted for that specific device. The connector also disables the standard NDES challenge-password mechanism. As a result, the administration page is not used for Intune certificate enrollment and serves no operational purpose in this configuration.

Preauthentication Limitations

Reverse-proxy preauthentication normally provides an additional security boundary by requiring a client to authenticate before its request is forwarded to the published application. With Microsoft Entra Application Proxy, Microsoft Entra ID preauthentication can block unauthenticated Internet clients from reaching the internal web application, reducing its exposure to scanning, password-spraying attacks, and other malicious requests.

However, SCEP clients cannot complete the Microsoft Entra ID authentication process or present the authentication token required by Application Proxy. Enabling preauthentication would therefore prevent managed endpoints from reaching NDES and enrolling for certificates. When publishing NDES through Microsoft Entra Application Proxy, the Pre Authentication setting must be configured as Passthrough. Other reverse proxies must similarly allow unauthenticated requests to reach the NDES SCEP endpoint. The Intune SCEP policy module, not the reverse proxy, validates and authorizes certificate requests before NDES submits them to the certification authority.

NDES published through a reverse proxy with the Intune Certificate Connector

Information Disclosure

Because the NDES administration page is configured to use Windows authentication, IIS can negotiate NTLM with an unauthenticated client that requests the mscep_admin path. When the client sends an NTLM Type 1 negotiation message, IIS can respond with a Type 2 challenge containing a target information block. No credentials are required to receive this challenge or the information it contains.

Depending on the server configuration and negotiated NTLM options, the Type 2 message can disclose some or all of the following information:

  • NetBIOS domain name
  • NetBIOS computer name
  • DNS domain name
  • DNS computer name (server FQDN)
  • DNS forest name
  • Operating system version and build number

This is significant because the internal Active Directory namespace often differs from the public namespace used to publish NDES. For example, the published external name might be ndes1.example.com, but the NTLM challenge might disclose an internal domain of corp.example.net and a server FQDN of ndes1.corp.example.net. None of that information is available from public DNS.

Testing

To view disclosed information, use curl.exe to send a static NTLM type 1 negotiation message and inspect the response headers. Run the following command on the NDES server.

curl.exe -skI -H 'Authorization: NTLM TlRMTVNTUAABAAAAB4IIAAAAAAAAAAAAAAAAAAAAAAA=' https://localhost/certsrv/mscep_admin

curl output showing the NTLM challenge returned by the NDES administration page

A response containing a WWW-Authenticate header with an NTLM value indicates the endpoint is offering a challenge. When the header includes a base64 payload beginning with TlRMTVNTUAAC, the server has returned a type 2 message, leading to information disclosure on the target host. A response with no WWW-Authenticate header at all is the desired result.

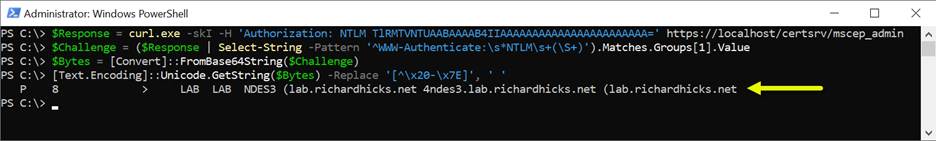
Here are the PowerShell commands to decode and view the base64 payload and the disclosed information.

$Response = curl.exe -skI -H 'Authorization: NTLM TlRMTVNTUAABAAAAB4IIAAAAAAAAAAAAAAAAAAAAAAA=' https://localhost/certsrv/mscep_admin
$Challenge = ($Response | Select-String -Pattern '^WWW-Authenticate:\s*NTLM\s+(\S+)').Matches.Groups[1].Value
$Bytes = [Convert]::FromBase64String($Challenge)
[Text.Encoding]::Unicode.GetString($Bytes) -Replace '[^\x20-\x7E]', ' '

Decoded NTLM challenge revealing server and domain information

PowerShell Script

I have created and published a PowerShell script to simplify testing NDES servers for information leakage. The script is published on GitHub here. In addition, you can install the script from the PowerShell Gallery by running the following command.

Install-Script -Name Get-NdesNtlmDisclosure

The output of the command on a vulnerable server is as follows.

Get-NdesNtlmDisclosure output on a vulnerable NDES server

A Note on External Testing

When NDES is published using Microsoft Entra Application Proxy, external test results can be inconsistent. In my repeated testing across three separate servers, the first request sometimes returned a bare NTLM challenge with no payload, and a second request, seconds later, returned the full type 2 message. Therefore, do not treat a single clean external result as confirmation. Test locally on the server itself, then repeat external tests at least twice to confirm the results.

Additional Security Concerns

Beyond the namespace disclosure, an Internet-accessible NDES administration page introduces some additional security concerns.

Password Spray Attacks

An internet-facing endpoint that accepts domain credentials is a target for password spraying attacks. Failed authentication attempts can count toward the configured account-lockout threshold, introducing a potential denial-of-service risk to user accounts.

Service Disclosure

The presence of an NTLM challenge on the well-known mscep_admin path also identifies the server as an NDES host, providing attackers with useful reconnaissance information for targeted attacks.

Remediation

If the reverse proxy configuration exposes the NDES administration page, it becomes an Internet-accessible authenticated endpoint that no part of the Intune enrollment workflow uses. Removing it is a simple and effective attack-surface reduction measure.

Remove the NDES Administration Page

Administrators can remove the NDES administration page IIS application by opening an elevated PowerShell command window and running the following command.

Remove-WebApplication -Site 'Default Web Site' -Name 'CertSrv/mscep_admin'

After running this command, browsing to the administration page returns HTTP 404. The application is gone, and SCEP enrollment continues to work normally. At this point, most administrators would consider the task complete.

The Problem

If you attempt to browse the administration page after removing it, you will still be prompted to authenticate. If you supply valid credentials, you will receive the expected 404. The authentication prompt itself is the real problem.

IIS Authentication Settings

The NDES role configuration writes IIS authentication settings for the administration page into a separate location element in applicationHost.config. Remove-WebApplication deletes the application definition under the sites element, but it does not touch the location element. IIS continues to match the path and applies the authentication settings it finds there, even though no application exists at that location.

The orphaned configuration is visible only in the raw configuration file. It does not appear in IIS Manager, and Get-WebApplication reports nothing at that path. You can run the following command to view this configuration.

Select-String -Path "$env:SystemRoot\System32\inetsrv\config\applicationHost.config" -Pattern '<location path=|windowsAuthentication enabled='

On a server where the administration page has been removed, the output still includes an entry like the following.

991: <location path=”Default Web Site/CertSrv/mscep_admin”>
997: <windowsAuthentication enabled=”true”>

IIS configuration entries enabling Windows authentication for mscep_admin

Orphaned Configuration

To fully remediate this information disclosure and prevent potential disruption caused by password-spraying attacks, administrators must also remove the orphaned configuration location. This eliminates Windows authentication on the administration path entirely.

Remove-WebConfigurationLocation -Name 'Default Web Site/CertSrv/mscep_admin'

The NDES role configuration also enables Windows authentication on the SCEP application. Because anonymous authentication is also enabled, requests to the SCEP endpoint are ordinarily processed without an authentication challenge. However, Windows authentication is not required on an NDES server supporting the Intune Certificate Connector, and leaving it enabled on an Internet-facing endpoint serves no operational purpose. I recommend disabling it explicitly.

Set-WebConfigurationProperty -PSPath 'MACHINE/WEBROOT/APPHOST' -Location 'Default Web Site/CertSrv/mscep' -Filter 'system.webServer/security/authentication/windowsAuthentication' -Name 'enabled' -Value $False

By default, Windows authentication is handled in kernel mode, so stale state information in HTTP.SYS can continue serving challenges after a configuration change. Be sure to run iisreset.exe after making these changes.

iisreset.exe /restart

Validation

Repeat the NTLM probes demonstrated earlier against the administration page. The absence of a WWW-Authenticate header confirms the challenge has been eliminated.

curl.exe -skI -H 'Authorization: NTLM TlRMTVNTUAABAAAAB4IIAAAAAAAAAAAAAAAAAAAAAAA=' https://localhost/certsrv/mscep_admin

curl output confirming mscep_admin no longer offers an NTLM challenge

Confirm that SCEP still responds anonymously. A status code of 200 with a plain-text capability list is expected.

curl.exe -skI 'https://localhost/certsrv/mscep/mscep.dll?operation=GetCACaps'

curl output showing the SCEP GetCACaps response with status code 200

Repeat the first test against the internal FQDN and the published external FQDN, then perform a device enrollment to confirm the deployment is unaffected.

PowerShell

After making these changes, Get-NdesNtlmDisclosure.ps1 will indicate that the NTLM challenge is not offered.

Get-NdesNtlmDisclosure output showing the NTLM challenge is not offered

Summary

The NDES administration page is not required when the Intune Certificate Connector is installed on an NDES server and should be removed as part of attack surface reduction. However, removing the IIS application leaves behind an orphaned configuration location that continues to apply Windows authentication settings to the path. The result can be an Internet-facing endpoint that discloses the internal domain name, server name, forest name, operating system build, and other information to an unauthenticated remote client that initiates NTLM negotiation.

Removing the admin application alone is not enough. You must also remove the configuration location, disable Windows authentication where it is not required, restart IIS, and validate the result with an NTLM probe to ensure full mitigation.

Additional Information

Get-NdesNtlmDisclosure PowerShell Script on GitHub

NDES Security Hardening: Protecting and Monitoring the SCEP Registry Configuration

Publish NDES with Microsoft Entra Application Proxy

Intune Certificate Connector Configuration Failed

Microsoft Intune Certificate Connector Failure

Certificate Connector for Intune Configuration Failure

Create and Assign SCEP Profiles in Microsoft Intune

Simple Certificate Enrollment Protocol (RFC 8894)

Mastering Certificates with Microsoft Intune September 2026

I’m excited to announce that I will be delivering another edition of the Mastering Certificates with Microsoft Intune course, hosted by ViaMonstra Online Academy. This is a three-day live online training course that takes place September 1-3, 2026. This course dives deep into issuing and managing certificates using Microsoft Intune, covering both on-premises and cloud-based solutions.

Course Overview

This interactive training equips IT professionals with the skills to provision and manage enterprise PKI certificates using Microsoft Intune. It explores Active Directory Certificate Services (AD CS), Microsoft Cloud PKI for Intune, and non-Microsoft solutions, with live demonstrations featuring real-world scenarios.

Key Learning Objectives

Those taking the online training course will learn the following.

  • Certificate Basics: Understand certificate roles and enterprise use cases.
  • Deployment Options: Master Intune certificate deployment (Intune policies, revocation, security) and Microsoft Cloud PKI (licensing, benefits, limitations, BYOCA).
  • Intune Deployment: Learn PKCS and SCEP deployment, security best practices, and troubleshooting.
  • High Availability: Explore strategies for reliable certificate management.

Course Highlights

Here are some key highlights for attendees of the training.

  • Expert-Led: Learn from a veteran IT professional, a Microsoft MVP, with deep PKI and Intune expertise.
  • Interactive Demonstrations: The course includes numerous practical exercises in real-world scenarios.
  • Resources: Access to security best practices and sample scripts for automated configuration.
  • Community: Join a private Facebook group for peer collaboration.
  • Live Q&A: Engage directly with the instructor for a clearer understanding.

Who Should Attend?

This training event is ideal for IT administrators, security professionals, and systems engineers working with Intune, AD CS, or Microsoft Cloud PKI for Intune.

Prerequisites

Those attending the online training course should be familiar with the following.

  • Basic networking knowledge (TCP/IP, DNS).
  • Familiarity with Active Directory, Windows OS, and Intune.
  • Access to an AD CS setup and an Azure subscription with Intune Suite licenses.

Why It Matters

Certificates are vital for secure authentication and communication. This course bridges theory and practice, equipping you to deploy and manage digital certificates effectively in cloud-native environments.

Details

Here is some additional information about the training event.

  • When: September 1-3, 2026 (sessions begin at 9:00 AM CDT).
  • Where: Live online via ViaMonstra Online Academy.
  • Cost: $2,395.00 (Sold separately – not included in All-Access Pass).

Why ViaMonstra?

ViaMonstra delivers top-tier IT training from Microsoft MVPs, focusing on practical, up-to-date skills and fostering a collaborative community.

Take the Next Step

Ready to master certificate management with Microsoft Intune? Register at ViaMonstra Online Academy for the August 2025 Mastering Certificates with Microsoft Intune training course today!

REMINDER: Windows Server 2016 End of Life January 2027 – Plan Your AD CS Migration Now

With just over six months remaining before Windows Server 2016 reaches end of support, now is the time to begin planning migrations for workloads hosted on this platform. Mainstream support ended on January 11, 2022, and Windows Server 2016 has since remained in extended support. However, extended support ends on January 12, 2027. After that date, Microsoft will no longer provide security updates or technical support, increasing the risk of running production workloads due to exposure to newly discovered vulnerabilities and exploits.

Active Directory Certificate Services

Many organizations are still running critical infrastructure on Windows Server 2016. Administrators often delay upgrading Microsoft Active Directory Certificate Services (AD CS) due to its complexity. However, a well-planned AD CS migration not only reduces risk but also provides an opportunity to modernize cryptography, certificate templates, and operational practices.

Certificate Authorities

Administrators must carefully migrate Certificate Authorities (CAs) running on Windows Server 2016 to minimize downtime. In environments where ongoing CA maintenance has been limited, migrating the CA database can be especially challenging. If the CA is installed on a domain controller, now is a good time to consider separating these services to ensure reliable operation. Also, it’s a good idea to evaluate the CA’s configuration and security posture during migration to enhance security and improve service resilience.

NDES Servers

Microsoft Network Device Enrollment Services (NDES) servers, commonly deployed to facilitate certificate enrollment via Microsoft Intune, pose a unique challenge during migration. Unfortunately, configuring NDES is exceedingly complex and error-prone. NDES relies on a delicate combination of specialized IIS configuration, AD service accounts, custom certificate templates, and CA permissions, making even minor changes risky without proper planning. Not surprisingly, administrators are often hesitant to touch these systems as they are notoriously difficult to troubleshoot when problems arise.

Pro Tip: We spend an entire day covering NDES configuration in the Mastering Enterprise PKI Certificates with Microsoft Intune training course. The next session is September 1-3, 2026. Register now!

Intune Certificate Connectors

Don’t overlook Windows Server 2016 servers with the Intune Certificate Connector installed. Fortunately, this is one of the more manageable workloads to migrate. All that’s required is to install new connectors on supported servers and delete the old ones.

Summary

With extended support for Windows Server 2016 ending on January 12, 2027, organizations running production workloads—especially critical infrastructure such as Active Directory Certificate Services (AD CS), Certificate Authorities (CAs), and NDES servers—face significant security risks from unpatched vulnerabilities once the OS reaches end-of-life. Careful migration planning to newer versions such as Windows Server 2022 or 2025 is essential to minimize downtime, improve security posture, and ensure long-term resilience.

Start Planning Now

Don’t leave these mission-critical infrastructure services to the last minute! Begin planning your migration today. If you’d like expert guidance, I have many years of experience migrating these workloads. I have developed specialized tools and techniques to ensure a smooth, secure, and successful transition. Fill out the form below to schedule a free one-hour consultation to assess your Windows Server 2016 AD CS workloads, identify migration risks, and outline next steps.

Additional Information

Windows Server 2016 Lifecycle Policy

PKI Fundamentals with Microsoft Active Directory Certificate Services (AD CS) Online Training Course

Mastering Enterprise PKI Certificates with Microsoft Intune Online Training Course

Troubleshooting NDES Error 0x80094800 Unsupported Cert Type on Windows Server 2025

With Windows Server 2016 fast approaching end of life (EOL – January 2027) I’ve been helping many customers get their existing Network Device Enrollment Service (NDES) server upgraded to Windows Server 2025. In the past I’ve had few problems deploying NDES on Windows Server 2016, 2019, and 2022. However, NDES deployments on Windows Server 2025 have proven more challenging. Unlike previous releases, many installations fail during initial configuration with little indication of the underlying cause. The error described below is quite common, in my experience.

Unsupported Cert Type

When configuring the NDES role on Windows Server 2025, administrators may encounter an installation failure with the following error message.

Failed to enroll RA certificates. The requested certificate template is not supported by this CA. 0x80094800 (-2146875392 CERTSRV_E_UNSUPPORTED_CERT_TYPE)

Investigation

Inspection of the issuing CA confirmed that the required NDES certificate templates had been published successfully and were visible on the target issuing CA server.

After confirming the templates were published, I validated connectivity between the NDEs server and the issuing CA to rule out communication issues.

certutil.exe -config <servername\commonname> -ping

Root Cause

Although the precise root cause remains unclear, the issue appears related to timing or object availability during NDES configuration. In many cases it behaves like a delay in template publication visibility, Active Directory replication latency, or another dependency timing issue encountered during setup.

Note: This error can also occur if the administrator is not a member of the Enterprise Administrators group, or if the security permissions on these default templates has changed.

Recovery

Fortunately, if you encounter this issue you can usually just remove the configuration using PowerShell and run it again.

Uninstall-AdccsNetworkDeviceEnrollmentService -Force

However, in my experience running the installer again results in another error, usually the 0x80070003 ‘Path Not Found’ error. If that happens, see my published guidance for recovering from this error here.

https://directaccess.richardhicks.com/2026/05/26/troubleshooting-ndes-error-0x80070003-path-not-found-on-windows-server-2025

While recovery is usually straightforward, preventing the issue entirely is preferable.

Recommendation

I recommend publishing the required templates on the target issuing CA before proceeding with the NDES configuration. Publishing these templates manually before running NDES configuration ensures they are already visible and available to the CA, potentially avoiding timing-related enrollment failures during setup. The following default templates are required for NDES configuration.

  • IPsec (Offline request)
  • CEP Encryption
  • Exchange Enrollment Agent (Offline request)

Note: Best practice is to remove these templates after configuration because they are intended only for NDES registration authority enrollment and are not typically required for ongoing issuance.

Summary

When deploying NDES on Windows Server 2025, administrators may encounter the 0x80094800 CERTSRV_E_UNSUPPORTED_CERT_TYPE error even when the required templates appear correctly configured. Although the exact cause remains uncertain, the issue appears related to timing or template availability during setup. In most cases, removing and re-running the NDES configuration resolves the problem, while pre-publishing the default NDES templates before configuration can help prevent it entirely.

Additional Information

Troubleshooting NDES Error 0x80070003 Path Not Found on Windows Server 2025

Intune PKCS and SCEP Certificate Validity Period

TRAINING: Mastering Enterprise PKI Certificates with Microsoft Intune

Troubleshooting NDES Error 0x80070003 Path Not Found on Windows Server 2025

When deploying enterprise PKI certificates with Microsoft Intune using SCEP, administrators must deploy one or more on-premises Network Device Enrollment Service (NDES) servers together with the Intune Certificate Connector. Installing and configuring NDES can be challenging because the solution includes multiple dependencies and has many moving parts. Troubleshooting installation failures can be difficult, particularly on Windows Server 2025 where I have observed installation issues more frequently than on earlier Windows Server releases.

Path Not Found

As I work with customers to migrate their existing NDES services to Windows Server 2025, I frequently encounter installation errors. Specifically, the ‘Path Not Found’ error is increasingly common. Using PowerShell or the Server Manager, administrators may encounter a failed NDES installation that returns the following error message.

CMSCEPSetup::Install: The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND)

NDES installation failing with error 0x80070003 ERROR_PATH_NOT_FOUND

Investigation

Reviewing the NDES installation log at C:\Windows\certocm.log yields an important clue.

Microsoft Active Directory Certificate Services: Failed to add the web virtual directory. The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND): The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND)

Root Cause

This error occurs after a failed installation attempt which corrupts the IIS configuration on the NDES server. This prevents the NDES installer from configuring applications in the default web site. Fortunately, the problem is easy to resolve.

Recovery Steps

To recover from this error, first uninstall the NDES service (not the role) by opening an elevated PowerShell command window and running the following command.

Uninstall-AdcsNetworkDeviceEnrollmentService -Force

Next, remove the corrupt IIS configuration file.

Remove-Item C:\Windows\System32\inetsrv\config\applicationHost.config -Force

Copy a known-good IIS configuration file from the WinSxS folder.

$WinSxSConfig = Get-ChildItem C:\Windows\WinSxS -Recurse -Filter applicationHost.config -ErrorAction SilentlyContinue | Sort-Object LastWriteTime -Descending | Select-Object -First 1
Copy-Item -Path $WinSxSConfig.FullName "C:\Windows\System32\inetsrv\config\applicationHost.config" -Force

And finally, recreate the default website.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" add site /name:"Default Web Site" /bindings:http/*:80: /physicalPath:"%SystemDrive%\inetpub\wwwroot"

Once complete, proceed with the NDES configuration.

Pro Tip

Because this issue occurs frequently enough in my experience, I recommend backing up the IIS configuration immediately after installing the NDES role and before beginning configuration. You can backup the IIS configuration by opening an elevated PowerShell command window and running the following command.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" add backup 'Backup Name'

If the NDES configuration subsequently fails, uninstall the configuration, then restore the backup using the following command.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" restore backup 'Backup Name'

Once complete, proceed with the NDES configuration once again.

Summary

NDES installation failures on Windows Server 2025 can leave IIS in an inconsistent state and trigger 0x80070003 ERROR_PATH_NOT_FOUND errors during configuration. Restoring a known-good IIS configuration and recreating the default web site resolves the issue quickly. Backing up the IIS configuration before beginning NDES configuration can significantly reduce recovery time if installation problems occur.

Additional Information

Troubleshooting NDES Error 0x80094800 Unsupported Cert Type on Windows Server 2025

Intune PKCS and SCEP Certificate Validity Period

TRAINING: Mastering Enterprise PKI Certificates with Microsoft Intune

Microsoft AD CS Adds Post-Quantum Cryptography Support with ML-DSA

Despite predictions of its decline, Microsoft Active Directory Certificate Services (AD CS) continues to evolve. Following significant enhancements introduced in late 2025, including CRL partitioning and support for 16K database pages, the May 2026 update adds another important capability: support for Post-Quantum Cryptography (PQC).

ML-DSA

Specifically, the May 2026 update adds support for ML-DSA-44, ML-DSA-65, and ML-DSA-87 in Windows Server 2025 for AD CS. This enables administrators to begin evaluating post-quantum cryptographic algorithms and assessing PQC readiness in enterprise PKI environments

Configuration

After applying the May 2026 update to an issuing Certification Authority (CA), administrators will find new PQC algorithms under the Algorithm name drop-down list, as shown here.

Certificate template Cryptography tab listing the ML-DSA-44, ML-DSA-65, and ML-DSA-87 algorithms

Note: If you don’t see these new algorithms, ensure you have selected Key Storage Provider from the Provider Category drop-down list. In addition, ensure that you select Signature on the Request Handling tab.

Test Results

Initial testing across common enterprise certificate scenarios produced mixed results. While PQC works well in some scenarios, other workloads still show limitations.

Code Signing

Code signing with an ML-DSA-44 certificate issued by AD CS works perfectly. For example, I can use Set-AuthenticodeSignature to sign a PowerShell script, as shown here.

Set-AuthenticodeSignature signing a PowerShell script with an ML-DSA-44 certificate

Viewing the file’s properties shows that the encryption algorithm used to sign the file was ML-DSA-44, as expected.

File digital signature details showing the ML-DSA-44 signature algorithm

IIS

TLS-based workloads proved more challenging. Attempts to configure an HTTPS binding in IIS failed with the following error message.

There was an error while performing this operation. A specified logon session does not exist. It may already have been terminated. (Exception from HRESULT: 0x80070520).

IIS error binding an ML-DSA certificate to an HTTPS site: a specified logon session does not exist

RRAS and SSTP

Similar limitations occurred when testing remote-access VPN scenarios using RRAS and SSTP. Specifically, configuring a PQC TLS certificate for SSTP in RRAS failed. Although I was able to assign the certificate using Set-RemoteAccess, the RemoteAccess service failed to start.

RemoteAccess service failing after assigning an ML-DSA certificate for SSTP

Remote Desktop

Unfortunately, using PQC certificates for RDP also fails. Although I could assign the PQC certificate to the RDP listener, clients fail to connect using RDP and return the following error message.

This computer can’t connect to the remote computer. Try connecting again. If the problem continues, contact the owner of the remote computer or your network administrator.

Error code: 0x904
Extended error code: 0x7

Remote Desktop connection error 0x904 with extended error 0x7 when using an ML-DSA certificate

Summary

The May 2026 update marks an important milestone for AD CS by introducing initial support for PQC algorithms, allowing organizations to begin evaluating ML-DSA certificates in enterprise environments. Early testing shows promising results for signing scenarios such as code signing; however, broader infrastructure workloads, including TLS, VPN, and Remote Desktop, remain limited today. Although PQC support is still in its early stages, these updates demonstrate Microsoft’s ongoing investment in AD CS and provide administrators with an opportunity to begin preparing their PKI environments for the post-quantum future. Additional PQC enhancements, including ML-KEM support and broader ecosystem integration, are anticipated in future Windows updates.

Additional Information

Enterprise PKI with Microsoft Active Directory Certificate Services

Microsoft May 2026 Security Updates (KB5087539)

Post-Quantum Cryptography (PQC) in the Enterprise: Timeline and Readiness