Troubleshooting Windows CLAT (WinCLAT) with the WinCLAT PowerShell Module

Windows CLAT (WinCLAT) is generally available on Windows 11 25H2, starting with build 26200.9550. WinCLAT is the Windows client-side translator for 464XLAT (RFC 6877). It translates IPv4 traffic from applications into IPv6 for delivery to a NAT64 gateway, allowing IPv4-only applications to continue working on IPv6-only and IPv6-mostly networks. Successful operation depends on both the Windows client configuration and the supporting network infrastructure. This post explains how to use the WinCLAT PowerShell module to verify these requirements, diagnose common problems, and test IPv4 connectivity through the translation path.

Why Use the WinCLAT PowerShell Module

WinCLAT is configured and inspected using the netsh.exe interface clat command context. However, its output requires careful interpretation when troubleshooting. A configuration command can complete without error even when Group Policy prevents the requested setting from taking effect. An instance can report that it is translating while IPv4 traffic fails, and disabling a global setting does not necessarily stop a manually enabled instance. The WinCLAT PowerShell module simplifies these tasks by checking the effective configuration after changes and providing health checks with explanations and recommended corrective actions. It supports troubleshooting on individual computers and across multiple remote computers.

How WinCLAT Activates

Understanding when WinCLAT activates automatically helps explain many troubleshooting scenarios. With AutoEnable enabled, Windows automatically activates WinCLAT on eligible non-cellular interfaces when the following conditions are met.

  • WinCLAT is permitted. The Permit setting is enabled. Today, it is disabled by default in Windows.
  • The interface has an IPv6 address assigned using Stateless Address Autoconfiguration (SLAAC) and an IPv6 default route.
  • The interface has no native IPv4 connectivity. On an IPv6-mostly network, DHCPv4 option 108, called IPv6-Only Preferred (RFC 8925), tells a compatible client to operate without a native IPv4 address for the period specified by the DHCPv4 server. WinCLAT provides IPv4 application connectivity over IPv6 during that time.
  • A NAT64 prefix has been discovered, either from the PREF64 option in router advertisements (RFC 8781) or by querying ipv4only.arpa for AAAA records through a DNS64 server (RFC 7050). DNS64 is required for the DNS-based discovery method but is not required when WinCLAT discovers the prefix through PREF64.

NAT64 Gateway Requirements

Successful IPv4 connectivity through WinCLAT also requires a reachable NAT64 gateway configured to translate traffic using the discovered prefix. Discovering a prefix and activating WinCLAT do not confirm that the gateway is reachable or that traffic can pass through it.

Automatic and Manual Activation

AutoEnable is enabled by default and allows Windows to activate WinCLAT automatically when an interface meets the required conditions. Manually enabled instances behave differently, as described later in this post. WinCLAT can be enabled manually on a specific interface after automatic activation is disabled. When WinCLAT is translating, Windows assigns the interface an IPv4 address from the 192.0.0.0/29 IPv4 Service Continuity Prefix (RFC 7335) and adds an IPv4 default route through WinCLAT.

Installing the Module

The WinCLAT module is available in the PowerShell Gallery and runs on Windows PowerShell 5.1 and PowerShell 7. Run the following command to install the module.

Install-Module -Name WinCLAT -Scope CurrentUser

The module is needed only on the computer running the commands. Remote computers require WinRM, and commands that read interface state or change configuration require an elevated session on the target.

Step 1: Run Test-WinCLAT

Test-WinClat is the starting point for any WinCLAT problem. Run it from an elevated session so the interface checks can run.

Test-WinClat

The summary shows the overall result (Pass, Warning, Fail, or NotApplicable), whether any interface is translating, and the checks that returned a warning or failure. Individual checks can also return Info for conditions that do not affect the overall result. To display every check and its explanation, use -Detailed with Format-List.

Test-WinClat -Detailed | Format-List -Property Check, InterfaceAlias, Result, Detail
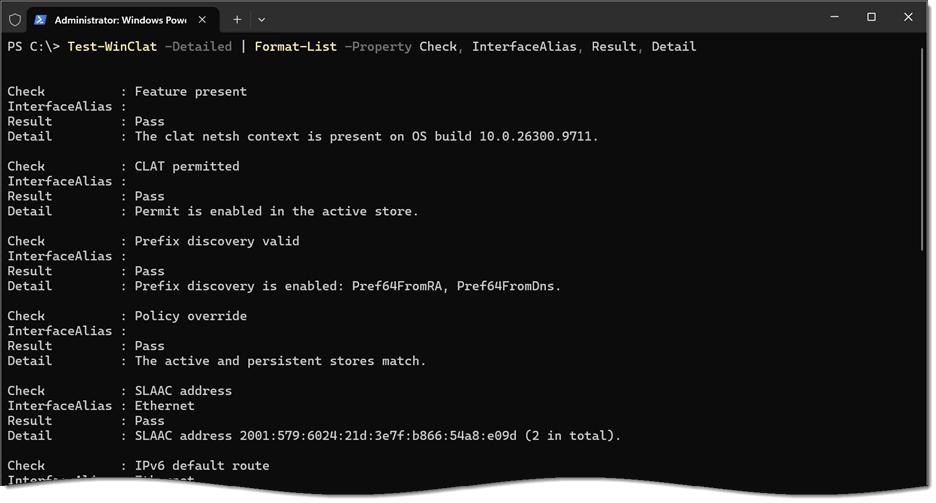
To show only the checks that need attention, including recommended corrective actions, run the following command.

Test-WinClat -Detailed | Where-Object -FilterScript { $_.Result -in 'Fail', 'Warning' } | Format-List -Property Check, InterfaceAlias, Detail, Remediation

Test-WinClat Tests

The following is a list of checks that Test-WinClat performs.

TestWhat it verifies
Feature presentThe clat netsh.exe context exists on the computer
CLAT permittedPermit is enabled in the active (effective) configuration
Prefix discovery validAt least one of Pref64FromRA and Pref64FromDns is enabled
Policy overrideGroup Policy is not overriding the local configuration
SLAAC addressThe interface has an IPv6 address from SLAAC
IPv6 default routeThe interface has an IPv6 default route
Native IPv4The interface has no native IPv4 address
Instance activeWinCLAT is translating when its prerequisites are met
CLAT addressThe WinCLAT IPv6 address is assigned to the interface and on its current prefix
Prefix consistencyThe NAT64 prefix matches the prefix returned by DNS64, when DNS64 is available
Mode sanityWinCLAT can activate: AutoEnable is enabled, or an instance has been enabled manually
Functional testIPv4 traffic passes through WinCLAT (optional)

Global checks do not require elevation. Interface checks are skipped, rather than failed, when the session is not elevated. Results of Info are informational and do not affect the overall result.

Step 2: Inspect the Configuration

Get-WinClatConfiguration returns the global settings. Use -Store Both to compare the active (effective) configuration with the persistent (local) configuration.

Get-WinClatConfiguration -Store Both

Compare the active configuration with the persistent configuration to identify differences between the effective settings and the locally stored settings. Use the PolicyControlled property to identify settings controlled by Group Policy. This property also identifies policy-controlled settings whose effective values match the local values, which a comparison of the two stores alone would not reveal.

Step 3: Inspect the Instances

Get-WinClatInstance returns the WinCLAT state of each IPv6-enabled interface. It requires elevation.

Get-WinClatInstance

Two properties are particularly useful when troubleshooting:

  • Mode shows whether the instance was enabled Automatically by Windows or Manually by an administrator.
  • TriggerSource shows why the instance was enabled: Pref64 RA (the network advertises PREF64), No IPv4 (the interface has no IPv4 connectivity), or Manual. It is read from event 1106 in the Microsoft-Windows-IPxlatCfg/Operational event log.

Common Problems

The following are common problems associated with WinCLAT configuration and operation.

Feature Not Present

Get-WinClatConfiguration returns Status FeatureNotAvailable, and Test-WinClatfails the Feature present check. WinCLAT is generally available on Windows 11 25H2 build 26200.9550 and later. The OSBuild property shows each computer’s build number, making it easy to identify computers that need the latest cumulative update.

WinCLAT is not available on Windows Server. Servers return Status NotSupported, and Test-WinClat reports an overall result of NotApplicable.

WinCLAT Not Permitted

Permit is disabled by default, so WinCLAT does not activate automatically on Wi-Fi or Ethernet interfaces until Permit is enabled, either locally or through Group Policy. Test-WinClat fails the CLAT permitted check only when an interface is IPv6-only and could use WinCLAT. On a dual-stack network, the check is informational because WinCLAT would not be used there anyway.

With AutoEnable enabled, WinCLAT activates on eligible interfaces as soon as Permit is enabled.

DHCPv4 Option 108

Permit also affects DHCPv4 option 108. Windows honors option 108 only while WinCLAT is permitted. With Permit disabled, a client on an IPv6-mostly network accepts a DHCPv4 lease and uses native IPv4, so WinCLAT is not needed, and the CLAT permitted check is informational.

WinCLAT Not Active on Dual-Stack Network

This is expected. WinCLAT does not activate on an interface with native IPv4. Test-WinClatreports Native IPv4 and Instance active as Info on dual-stack interfaces. If a dual-stack interface has no SLAAC address or no IPv6 default route, as on a network that assigns IPv6 addresses with DHCPv6 only, those checks are also Info rather than Fail, because they matter only if the network becomes IPv6-only.

SLAAC Addressing Not Present

WinCLAT requires an IPv6 address configured using SLAAC. An interface whose IPv6 addresses are assigned only through DHCPv6 does not meet this requirement. DHCPv6 can still provide other configuration information, such as DNS server addresses and a domain search list. Test-WinClat checks for a SLAAC address and reports when an interface that needs WinCLAT does not have one.

Group Policy Overrides Local Configuration

Netsh.exe reports success when a local change is made to a setting that Group Policy controls, but the effective value does not change. Set-WinClatConfiguration reads the configuration back after every change and reports the result with Status PolicyOverride when the policy keeps a different value.

In addition, Test-WinClat indicates when local settings conflict with Group Policy enforced settings.

Group Policy can control Permit, Pref64FromRA, and Pref64FromDns. There is no policy for AutoEnable. The policy values are stored in the following registry location.

HKLM\SOFTWARE\Policies\Microsoft\Windows\TCPIP\v6Transition\IPxlatCfgSvc

No NAT64 Prefix Discovered

An instance that is enabled but has no NAT64 prefix cannot translate. Test-WinClat fails the Instance active check and names the prefix discovery methods that are enabled. Common causes include:

  • The network does not include the PREF64 option in router advertisements, and Pref64FromDns is disabled.
  • No usable NAT64 prefix is available through router advertisements, and Pref64FromDns is enabled, but the DNS servers assigned to the client do not provide DNS64.
  • Both Pref64FromRA and Pref64FromDns are disabled. Netsh.exe accepts this combination silently, but WinCLAT can never activate. Set-WinClatConfiguration refuses it.

When WinCLAT discovers a NAT64 prefix through the PREF64 option in router advertisements, DNS64 is not required for prefix discovery or for translating IPv4 application traffic. A reachable NAT64 gateway using that prefix is still required. If DNS64 is unavailable, the Prefix consistency check is informational because there is no DNS64-derived prefix to compare.

Delayed WinCLAT Activation

WinCLAT activates fastest when the network advertises the NAT64 prefix through PREF64. When DNS64 is the only available prefix discovery method, Windows first waits to determine that the interface has no native IPv4 connectivity, so activation takes several seconds longer. Allow time for this process before treating an inactive instance as a configuration problem.

Manually Enabled Instances Continue Translating

Disabling Permit or AutoEnable stops translation on instances that Windows enabled automatically. Manually enabled instances can continue translating after either setting is disabled. When troubleshooting continued translation, check the instance’s Mode property to determine whether it was enabled manually.

Use Get-WinClatInstance to identify manually enabled instances.

Get-WinClatInstance | Where-Object -FilterScript { $_.Enabled -and $_.Mode -eq 'Manual' }

Note that netsh.exe refuses to change an instance while AutoEnable is enabled. To return an interface from manual to automatic control, disable AutoEnable, disable the instance, and enable AutoEnable again:

Set-WinClatConfiguration -AutoEnable Disabled
Set-WinClatInstance -InterfaceAlias 'Ethernet' -State Disabled
Set-WinClatConfiguration -AutoEnable Enabled

WinCLAT Stops Working After Reboot

Manual instance state is runtime only. It survives an adapter restart and link loss, but it is lost on reboot. Enabling an instance manually requires disabling AutoEnable, and AutoEnable remains disabled after the reboot, so WinCLAT does not activate at all. Enable AutoEnable again to restore automatic operation:

Set-WinClatConfiguration -AutoEnable Enabled

The Mode sanity check in Test-WinClat reports this condition.

IPv4 Fails After Moving to a Different Network

When a translating client moves to a different IPv6 network without restarting its network adapter, WinCLAT keeps its IPv6 address on the previous network’s prefix. The instance still reports that it is translating, but IPv4 traffic through WinCLAT fails. Microsoft has acknowledged this known issue and is working to resolve it in a future release.

Test-WinClat detects this condition. The CLAT address check fails, naming the address in use and the current prefix, while the Instance active check passes.

Restarting the network adapter resolves the issue.

Restart-NetAdapter -Name 'Ethernet'

The IPv6 address reported by netsh.exe interface clat show instance cannot be used to detect this condition, because it may report a new address that is not actually assigned to the interface. The CLAT address check compares the addresses actually assigned to the adapter with its current prefix.

Netsh.exe Reports Addresses That Are Not Assigned

An instance that is enabled but no longer translating can retain stale information in netsh.exe output. For example, a manually enabled instance on an interface that now has native IPv4 connectivity might still report a WinCLAT IPv6 address and 192.0.0.1 even though those addresses are no longer assigned to the interface. It might also display a NAT64 prefix with a remaining lifetime of zero. Use Get-NetIPAddress to confirm the addresses assigned to the interface. Clear the manual instance using the three-command sequence shown earlier or restart the computer.

Testing the Translation Path

The checks above assess WinCLAT configuration and local instance state. The functional test verifies connectivity to a specific IPv4 destination through WinCLAT and the NAT64 gateway. Use Test-WinClat with an IPv4 target address that is reachable through the gateway and known to respond to the selected test.

Test-WinClat -IPv4Target 172.16.0.204 -Detailed | Format-Table -Property Check, InterfaceAlias, Result, Detail -Wrap

The test sends up to three ICMP echo requests. Add -IPv4Port to test a TCP connection instead, which is useful where ICMP is filtered.

Test-WinClat -IPv4Target 172.16.0.204 -IPv4Port 443

Keep the following in mind when interpreting the result.

  • Use an IPv4 address as the target. A hostname can resolve to a synthesized AAAA record through DNS64, allowing the connection to use IPv6 through NAT64 without using WinCLAT. Testing with an IPv4 address ensures the test uses IPv4. Check the selected interface and source address to confirm that the traffic passes through WinCLAT.
  • Native IPv4 can bypass WinCLAT. If another interface provides native IPv4 connectivity to the test destination, Windows might send the test traffic through that interface. The module reports Info when the selected path bypasses WinCLAT, even if the destination responds successfully. Review the Detail property to identify the selected interface and source address and confirm whether the test used WinCLAT.
  • Unreachable destinations time out. ICMP destination unreachable messages that NAT64 returns for IPv4 destinations are not delivered to the IPv4 application, so a test to an unreachable or filtered address returns a Warning after timing out rather than an immediate failure. Choose a target that is known to respond, ideally on your own infrastructure.
  • One test covers one path. When several interfaces translate, the test proves that IPv4 works through the interface Windows chose, not on each interface.

Troubleshooting at Scale

The WinCLAT commands accept computer names from the pipeline, including input from Get-Content and Get-ADComputer, and process remote computers in parallel over WinRM. Before connecting, the module checks TCP port 5985. If that connection fails, it reports the computer as Unreachable without waiting for a full WinRM timeout. This status indicates that the module could not reach the required endpoint. The computer might be offline, the port might be blocked, or WinRM might be configured to use a different TCP port.

Filtering and Exporting Results

The module returns a result for every target computer, including those that cannot be reached, do not support the feature, or cannot be fully checked because the session lacks elevation. The Status property identifies the outcome, and the Message property explains it.

# Test every computer in an OU and show only the computers with problems
Get-ADComputer -Filter * -SearchBase 'OU=Windows Clients,DC=corp,DC=example,DC=net' | Test-WinClat | Where-Object -FilterScript { $_.Overall -ne 'Pass' }
# Export the detailed results of every check for later analysis
Get-Content -Path .\clients.txt | Test-WinClat -Detailed | Export-Csv -Path .\winclat-results.csv -NoTypeInformation
# Save the names of unreachable computers to test again later
Get-Content -Path .\clients.txt | Test-WinClat | Where-Object -FilterScript { $_.Status -eq 'Unreachable' } | Select-Object -ExpandProperty ComputerName | Set-Content -Path .\retry.txt

The output is flat, so it exports cleanly with Export-Csv for reporting and comparison over time.

Known Issues

The following Windows behaviors can affect WinCLAT operation and troubleshooting. The module can identify some of these conditions, but it does not correct the underlying Windows behavior. Available workarounds are listed below.

IssueEffectWorkaround
WinCLAT keeps its IPv6 address on the previous prefix after a network changeIPv4 traffic through WinCLAT fails; Test-WinClat reports CLAT address FailRestart the network adapter
WinCLAT IPv4 address is dynamically registered in DNSConnections to the client may fail when DNS resolves its name to a WinCLAT IPv4 addressNone
Translated ICMP errors are not delivered to IPv4 applicationsUnreachable IPv4 destinations time out instead of failing immediatelyNone

Summary

Troubleshooting WinCLAT starts with Test-WinClat, which checks every prerequisite, explains each failure, and suggests remediation. Get-WinClatConfiguration reveals Group Policy overrides, and Get-WinClatInstance shows whether each instance was enabled automatically or manually. Most problems come down to a few causes: Permit disabled by default, Group Policy overriding local settings, no NAT64 prefix discovered, a manual instance that does not follow the global settings, or a stale WinCLAT address after a network change. Because netsh.exe reports success even when a change does not take effect, always verify the result by reading the state back, which the WinCLAT module does automatically.

Additional Information

WinCLAT PowerShell Module on GitHub

WinCLAT on directaccess.richardhicks.com

Entra Internet Access TLS Inspection and Always On VPN: Troubleshooting SSTP Connection Failures

Microsoft Entra Global Secure Access (GSA) is a cloud-based Security Service Edge (SSE) solution that includes Entra Private Access to provide zero-trust network access to private data and applications, and Entra Internet Access to provide security controls for general internet access. Entra Internet Access includes features such as web content filtering, AI prompt controls, TLS inspection, and more. Entra Private Access and Entra Internet Access share a common client: the Global Secure Access Client.

TLS Inspection

TLS inspection is a powerful feature of Entra Internet Access that allows inspection and policy enforcement for encrypted internet traffic. It enables more thorough inspection and is required for features such as AI prompt policies. When TLS inspection is enabled, the TLS connection from the target server (origin server) is terminated by the Entra service. A new session is created between the cloud and the endpoint using a dynamically generated TLS certificate issued by Entra. As Entra holds the private key for this certificate, it can decrypt and inspect traffic as necessary.

Always On VPN

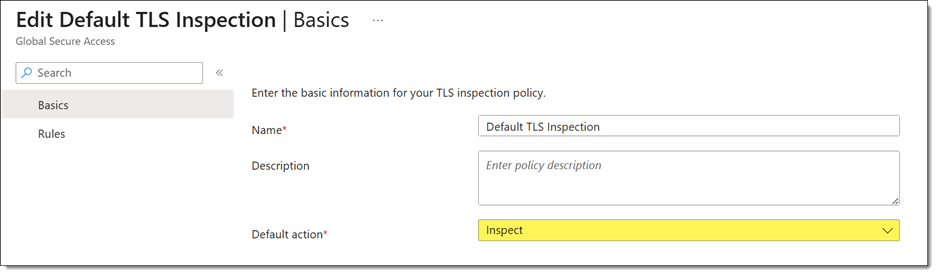
Recently, a customer asked me to help troubleshoot an Always On VPN user tunnel connectivity issue. The problem began shortly after deploying the Global Secure Access client with TLS inspection enabled. Administrators had configured the default TLS inspection policy to inspect traffic for all websites.

User Tunnel Failures

Attempts to manually start the Always On VPN user tunnel resulted in a failed connection attempt with the following error message.

Error 0x800704D4: The network connection was aborted by the local system.

Event Logs

Reviewing the client event logs revealed numerous Event ID 20227 entries from the RasClient source with the following error message.

The user DOMAIN\User dialed a connection named [connection name] which has failed. The error code returned on failure is -2147023660.

Note: Error code -2147023660 is the decimal equivalent of 0x800704D4.

Troubleshooting

Initial testing with Test-NetConnection confirmed that TCP port 443 on the VPN server was reachable. However, using Get-TlsCertificate revealed the real problem.

Although the certificate subject matched the VPN server, the issuer did not. Instead of the VPN server’s issuing CA, the certificate had been issued by Microsoft Entra Global Secure Access, confirming that TLS inspection was intercepting the connection.

SSTP and TLS Inspection

The Secure Socket Tunneling Protocol (SSTP) is a Microsoft proprietary VPN transport that uses HTTP for tunneling and TLS for security. Unlike a web browser, which can establish a new trusted TLS session with an inspection proxy, SSTP validates the VPN server’s certificate as part of establishing the VPN tunnel. Any certificate substitution, even by a trusted TLS inspection service, changes the server certificate thumbprint and causes SSTP validation to fail.

Workaround

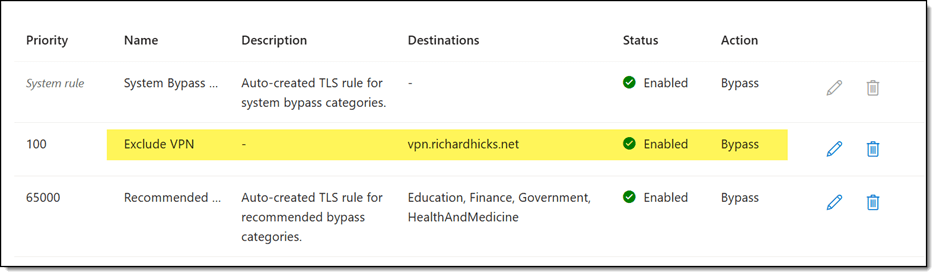
The solution is to create a TLS inspection exclusion policy to exempt inspection for the VPN server FQDN(s), as shown here.

Summary

Microsoft Entra Internet Access TLS inspection can unintentionally interfere with Always On VPN deployments that use SSTP. Because TLS inspection replaces the VPN server’s certificate with one issued by Microsoft Entra, SSTP detects the certificate mismatch and terminates the connection. If you use Always On VPN with Entra Internet Access, configure a TLS inspection exclusion for your VPN server FQDNs to prevent interception while preserving TLS inspection for general internet traffic.

Additional Information

Always On VPN vs. Entra Private Access: Choosing the Right Access Model for your Organization

What is Microsoft Entra Global Secure Access?

Microsoft Entra Internet Access

Microsoft Entra Private Access

Always On VPN SSTP and 47-Day TLS Certificates

Always On VPN SSTP and HSTS

What’s New in Entra Private Network Connector v1.5.4892.0

An important update is available for the Microsoft Entra Private Network Connector. The Entra Private Network Connector is used to publish on-premises web applications to the internet. It is also used for Global Secure Access (GSA) with Entra Private Access, allowing GSA clients to access on-premises resources. Entra Private Network Connector v1.5.4892.0 includes important new functionality to streamline troubleshooting and improve stability and performance.

New Features

The Entra Private Network Connector v1.5.4892.0 now includes a diagnostic tool on the system tray. This gives administrators a visual indicator of connector status and provides quick access to diagnostics and log files.

Diagnostics

Right-clicking the connector and choosing ‘Connector diagnostics’ launches the Connector Diagnostics window. Here you’ll find three tabs: Overview, Health Check, and Advanced Logs.

Overview

The Overview tab provides details about the connector, such as the Tenant ID, Connector ID, version, supported TLS versions, the connector server’s IPv4 address (IPv6 information is not displayed), the server’s hostname, and the operating system version.

Health Check

Clicking on the Health Check tab will perform a comprehensive system health check. Status information for each check is provided, indicating whether it is Passed or Failed. Optionally, administrators can export the report in text, HTML, or JSON format for further analysis. Each health check can be expanded to reveal additional information about the individual check.

Advanced Logs

Clicking the Advanced Logs tab allows administrators to retrieve detailed log information. Session channel logging is enabled by default but can optionally be disabled if needed. You can choose specific start and end dates and times to collect logs, then click Retrieve Logs to collect them.

Once complete, it’s not immediately obvious where to find these logs. Clicking the Logs Retrieved button prompts the administrator to select a location in which to save the log files.

Improvements

This update improves the reliability of name resolution by filtering invalid DNS responses. In addition, the update improves connector logging to the Windows Event Log and fixes various issues and bugs.

Updating to v1.5.4892.0

Existing Entra Private Network Connector installations will not automatically receive this update. Administrators must manually download the connector from the Microsoft Entra admin center and apply the update themselves to take advantage of these new features and capabilities.

Additional Information

Microsoft Entra Private Network Connector v1.5.4892.0

Microsoft Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Troubleshooting NDES Error 0x80094800 Unsupported Cert Type on Windows Server 2025

With Windows Server 2016 fast approaching end of life (EOL – January 2027) I’ve been helping many customers get their existing Network Device Enrollment Service (NDES) server upgraded to Windows Server 2025. In the past I’ve had few problems deploying NDES on Windows Server 2016, 2019, and 2022. However, NDES deployments on Windows Server 2025 have proven more challenging. Unlike previous releases, many installations fail during initial configuration with little indication of the underlying cause. The error described below is quite common, in my experience.

Unsupported Cert Type

When configuring the NDES role on Windows Server 2025, administrators may encounter an installation failure with the following error message.

Failed to enroll RA certificates. The requested certificate template is not supported by this CA. 0x80094800 (-2146875392 CERTSRV_E_UNSUPPORTED_CERT_TYPE)

Investigation

Inspection of the issuing CA confirmed that the required NDES certificate templates had been published successfully and were visible on the target issuing CA server.

After confirming the templates were published, I validated connectivity between the NDEs server and the issuing CA to rule out communication issues.

certutil.exe -config <servername\commonname> -ping

Root Cause

Although the precise root cause remains unclear, the issue appears related to timing or object availability during NDES configuration. In many cases it behaves like a delay in template publication visibility, Active Directory replication latency, or another dependency timing issue encountered during setup.

Note: This error can also occur if the administrator is not a member of the Enterprise Administrators group, or if the security permissions on these default templates has changed.

Recovery

Fortunately, if you encounter this issue you can usually just remove the configuration using PowerShell and run it again.

Uninstall-AdccsNetworkDeviceEnrollmentService -Force

However, in my experience running the installer again results in another error, usually the 0x80070003 ‘Path Not Found’ error. If that happens, see my published guidance for recovering from this error here.

https://directaccess.richardhicks.com/2026/05/26/troubleshooting-ndes-error-0x80070003-path-not-found-on-windows-server-2025

While recovery is usually straightforward, preventing the issue entirely is preferable.

Recommendation

I recommend publishing the required templates on the target issuing CA before proceeding with the NDES configuration. Publishing these templates manually before running NDES configuration ensures they are already visible and available to the CA, potentially avoiding timing-related enrollment failures during setup. The following default templates are required for NDES configuration.

  • IPsec (Offline request)
  • CEP Encryption
  • Exchange Enrollment Agent (Offline request)

Note: Best practice is to remove these templates after configuration because they are intended only for NDES registration authority enrollment and are not typically required for ongoing issuance.

Summary

When deploying NDES on Windows Server 2025, administrators may encounter the 0x80094800 CERTSRV_E_UNSUPPORTED_CERT_TYPE error even when the required templates appear correctly configured. Although the exact cause remains uncertain, the issue appears related to timing or template availability during setup. In most cases, removing and re-running the NDES configuration resolves the problem, while pre-publishing the default NDES templates before configuration can help prevent it entirely.

Additional Information

Troubleshooting NDES Error 0x80070003 Path Not Found on Windows Server 2025

Intune PKCS and SCEP Certificate Validity Period

TRAINING: Mastering Enterprise PKI Certificates with Microsoft Intune

Troubleshooting NDES Error 0x80070003 Path Not Found on Windows Server 2025

When deploying enterprise PKI certificates with Microsoft Intune using SCEP, administrators must deploy one or more on-premises Network Device Enrollment Service (NDES) servers together with the Intune Certificate Connector. Installing and configuring NDES can be challenging because the solution includes multiple dependencies and has many moving parts. Troubleshooting installation failures can be difficult, particularly on Windows Server 2025 where I have observed installation issues more frequently than on earlier Windows Server releases.

Path Not Found

As I work with customers to migrate their existing NDES services to Windows Server 2025, I frequently encounter installation errors. Specifically, the ‘Path Not Found’ error is increasingly common. Using PowerShell or the Server Manager, administrators may encounter a failed NDES installation that returns the following error message.

CMSCEPSetup::Install: The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND)

Investigation

Reviewing the NDES installation log at C:\Windows\certocm.log yields an important clue.

Microsoft Active Directory Certificate Services: Failed to add the web virtual directory. The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND): The system cannot find the path specified. 0x80070003 (WIN32: 3 ERROR_PATH_NOT_FOUND)

Root Cause

This error occurs after a failed installation attempt which corrupts the IIS configuration on the NDES server. This prevents the NDES installer from configuring applications in the default web site. Fortunately, the problem is easy to resolve.

Recovery Steps

To recover from this error, first uninstall the NDES service (not the role) by opening an elevated PowerShell command window and running the following command.

Uninstall-AdcsNetworkDeviceEnrollmentService -Force

Next, remove the corrupt IIS configuration file.

Remove-Item C:\Windows\System32\inetsrv\config\applicationHost.config -Force

Copy a known-good IIS configuration file from the WinSxS folder.

$WinSxSConfig = Get-ChildItem C:\Windows\WinSxS -Recurse -Filter applicationHost.config -ErrorAction SilentlyContinue | Sort-Object LastWriteTime -Descending | Select-Object -First 1
Copy-Item -Path $WinSxSConfig.FullName "C:\Windows\System32\inetsrv\config\applicationHost.config" -Force

And finally, recreate the default website.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" add site /name:"Default Web Site" /bindings:http/*:80: /physicalPath:"%SystemDrive%\inetpub\wwwroot"

Once complete, proceed with the NDES configuration.

Pro Tip

Because this issue occurs frequently enough in my experience, I recommend backing up the IIS configuration immediately after installing the NDES role and before beginning configuration. You can backup the IIS configuration by opening an elevated PowerShell command window and running the following command.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" add backup 'Backup Name'

If the NDES configuration subsequently fails, uninstall the configuration, then restore the backup using the following command.

& "$env:SystemRoot\System32\inetsrv\appcmd.exe" restore backup 'Backup Name'

Once complete, proceed with the NDES configuration once again.

Summary

NDES installation failures on Windows Server 2025 can leave IIS in an inconsistent state and trigger 0x80070003 ERROR_PATH_NOT_FOUND errors during configuration. Restoring a known-good IIS configuration and recreating the default web site resolves the issue quickly. Backing up the IIS configuration before beginning NDES configuration can significantly reduce recovery time if installation problems occur.

Additional Information

Troubleshooting NDES Error 0x80094800 Unsupported Cert Type on Windows Server 2025

Intune PKCS and SCEP Certificate Validity Period

TRAINING: Mastering Enterprise PKI Certificates with Microsoft Intune

What’s New in Entra Global Secure Access Client v2.24.117

In early December 2025, Microsoft announced an update for the Entra Global Secure Access client. This latest release, v2.24.117, includes important changes that administrators will find helpful for efficient connectivity and enhanced troubleshooting.

Intelligent Local Access

The latest release of the Microsoft Entra Global Secure Access client adds support for Intelligent Local Access (ILA). ILA ensures optimal network connectivity when accessing published resources. ILA can detect when it is on a trusted network and send traffic directly to the resource, bypassing the cloud gateway to improve performance. Authentication and authorization are still required for application access regardless of location.

B2B Guest Access

B2B Guest Access, now in public preview, enables external partners to securely access an organization’s private resources using their own devices and home Microsoft Entra ID credentials, without credential duplication. Partners install the Global Secure Access client, sign in, and switch to the resource tenant, routing traffic via Private Access profiles for Conditional Access, MFA, and continuous evaluation. It supports BYOD and multitenant switching, requires guest user setup and specific client configurations in the resource tenant, and needs licensing only in the resource tenant. However, B2B Guest Access does not support Kerberos-based on-premises resources. More details here.

Traceroute

This latest release of the Entra Global Secure Access client also includes a new traceroute tool. GsaTracert.exe, located in the C:\Program Files\Global Secure Access Client\GSATracert\ folder, allows administrators to test connectivity to published resources and evaluate network response time and performance.

FQDN

Administrators can use GsaTracert.exe to validate connectivity to a resource using its fully qualified domain name (FQDN). When running the command, GsaTracert.exe reports the round-trip time (RTT) in milliseconds for each hop along the path, including the target resource. It will also indicate which point of presence (PoP) the client is currently connected to. The syntax to perform this test is:

.\GsaTracert.exe --host <fqdn:port>

For example:

.\GsaTracert.exe --host app1.lab.richardhicks.net:443

IP:Host

In addition to testing an FQDN, administrators can test individual resources using a combination of IP address and port number. The syntax to perform this test is:

.\GsaTracert.exe --host <ip:port>

For example:

.\GsaTracert.exe --host 172.16.0.254:22

Application ID

In addition to FQDN and IP:Port, administrators can also supply the application ID to test. However, since an application can include multiple IP addresses and/or ports, the measurement for backend resources is omitted when using this option. The syntax to perform this test is:

.\GsaTracert.exe --app-id <app ID>

For example:

.\GsaTracert.exe --app-id a8b914b-4143-4901-9fbb-09b61319d5a6

Note: You can find the application ID for a published application by opening the Entra admin center and navigating to Global Secure Access > Applications > Enterprise Applications. The application ID will be displayed on the Overview page of the published Enterprise application.

Speedtest

Administrators can use the –speedtest switch with any of the combinations above to test the endpoint’s Internet performance. The results are for the connection to the public Internet, not to the published resource.

Additional Features

The following new features are designed to improve the user experience for Global Secure Access users.

Disable Private Access

Administrators can now use a registry setting to show the Disable button, allowing users to disable Entra Private Access. Disabling Private Access is helpful when a device is on the internal network, and the user prefers to access resources directly rather than through Global Secure Access.

View Account

The new Global Secure Access client now includes a View Account link to the user’s Microsoft Entra My Account website.

Summary

The Microsoft Entra Global Secure Access Client v2.24.117 introduces several valuable enhancements for administrators and users alike. Key highlights include Intelligent Local Access for optimized performance on trusted networks, public preview support for B2B Guest Access enabling secure external collaboration without credential duplication, and the new GsaTracert.exe traceroute tool for detailed network diagnostics. Additional improvements, such as the ability to disable Private Access via registry settings and quick access to the My Account portal, further streamline management and troubleshooting. These updates reinforce Microsoft Entra Global Secure Access as a robust solution for secure, efficient resource connectivity.

Additional Information

Microsoft Entra Global Secure Access client v.2.24.117

Install the Entra Global Secure Access client for Microsoft Windows

Microsoft Entra Private Access Intelligent Local Access (ILA)

Preventing Port Exhaustion on Entra Private Network Connector Servers

Always On VPN vs. Entra Private Access: Choosing the Right Access Model for Your Organization

Always On VPN Troubleshooting with Windows Packet Monitor PktMon.exe

When troubleshooting Always On VPN, taking a network packet capture or network trace is sometimes required to identify the root cause of a problem. After all, Packets Don’t Lie™. There are numerous ways to capture packets. Many administrators will install Wireshark for this purpose. However, Windows has a native packet capture tool called PktMon.exe that offers many advantages over Wireshark.

Wireshark

Many Always On VPN administrators will be familiar with Wireshark. Wireshark is a popular open-source network protocol analyzer that enables the capture and analysis of network traffic for troubleshooting. A packet capture driver must first be installed to capture network traffic with Wireshark. Typically, administrators will install Npcap, which is part of the default installation of Wireshark. Installing a capture driver poses a potential problem, as the administrator must install software on the target device before capturing traffic. Installing software may not always be feasible or possible. Fortunately, there’s an alternative.

PktMon.exe

The Windows Packet Monitor (PktMon.exe) is a built-in command-line tool first introduced in Windows 10 1809 and Windows Server 2019. It is designed to capture network traffic on Windows servers and client systems. This native lightweight tool is ideal for collecting network traces for offline analysis.

Capture All Interfaces

The most common scenario for PktMon.exe is to capture data for offline analysis. Use the following command to capture all network traffic on all active network interfaces.

PktMon.exe start –capture –file c:\capture.etl –pkt-size 0 –comp nics –flags 0x10

The command breaks down as follows:

–capture – captures network traffic

–file – the path of the file to save the data to

–pkt-size 0 – captures the full packet (not truncated)

–comp nics – captures traffic on all active network interfaces

–flags 0x10 – captures the raw packet

After reproducing the issue, you can stop the trace by running the following command.

PktMon.exe stop

Capture Specific Interface

Administrators may wish to capture traffic on a specific network interface instead of all active network interfaces. In this example, I have a multi-homed VPN server and want to capture traffic on only the DMZ interface. To do this, use PktMon.exe to enumerate all interfaces using the following command.

PktMon.exe list

Note: The output of PktMon.exe filter list does not include information that easily maps to existing network interfaces. I suggest also running the Get-NetAdapter PowerShell command to view detailed information about network interfaces. You can use this information to select the correct Network ID for PktMon.exe filtering.

Next, change the value of –comp nics in the command referenced above to –comp <Network ID>. Here’s an example.

PktMon.exe start –capture –file c:\capture.etl –pkt-size 0 –comp 62 –flags 0x10

Filtering

It’s also possible to use PktMon.exe to capture network traffic selectively. Filtering allows you to narrow the capture to relevant traffic, making analysis easier and faster. Add a filter, then start a trace to restrict data capture to traffic that matches the defined filters. You can add one or more filters to apply to the capture. Here are a few examples.

Protocols and Ports

Let’s say you are troubleshooting a device tunnel connection and want to see only IKEv2 traffic. The following filter will restrict the network capture to only the IKEv2-related protocols and ports.

PktMon.exe filter add IKEv2 -t UDP -p 500
PktMon.exe filter add IKEv2 -t UDP -p 4500

IP Address

The following filter will capture data that includes the specified IP address in the source or destination address field.

PktMon.exe filter add VPN1 -i 172.21.12.50

You can also specify IP address subnets using their CIDR notation.

PktMon.exe filter add Subnet1 -i 172.16.0.0/16

View and Clear Filters

You can view configured filters using the following command.

PktMon.exe filter list

You can remove configured filters using the following command. Use with caution, as this removes ALL filters!

PktMon.exe filter remove

Reference

You’ll find a complete list of PktMon.exe filters here.

Analysis

PktMon.exe outputs captured data in ETL format. Administrators can convert captured data to the standard PCAP format by running the following command.

PktMon.exe etl2pcap <path of trace file>

This command converts the file from ETL to PCAPNG format. Administrators can then open the capture in Wireshark for further detailed analysis.

Display Only

PktMon.exe can be configured to display network traffic in the console for quick troubleshooting. Console traffic display can be helpful for those scenarios where a quick check to validate traffic is reaching a particular destination is required. Here’s an example.

PktMon.exe start –capture –pkt-size 0 –comp nics –flags 0x10 -m real-time

Note: In the example above, I applied a traffic filter to limit the capture to only SSTP traffic (TCP 443).

Limitations

One crucial limitation of PktMon.exe is that it doesn’t support persistent network captures that survive a reboot. Persistent captures can be helpful when troubleshooting a device tunnel connection or slow logons. In this scenario, you must use netsh.exe.

netsh.exe trace start capture=yes tracefile=c:\tracefile.etl persistent=yes

<reboot>

netsh.exe trace stop

Although PktMon.exe supports the ‘etl2pcap’ switch, it does NOT work for converting .etl files generated with netsh.exe. To convert captures created with netsh.exe, use the open-source etl2pcapng tool.

Learn More

PktMon.exe has many different uses. This post barely scratches the surface of what PktMon.exe can do. PktMon.exe comes with robust help, accessible by adding the ‘help’ switch to commands. Here are some examples.

PktMon.exe start help
PktMon.exe filter add help

Be sure to view the online help to explore various options for capturing and logging to meet your specific needs.

Summary

PktMon.exe is a native command-line utility in Windows that provides a lightweight solution for capturing network traffic, making it particularly useful for Always On VPN troubleshooting. Key functionalities include full-packet captures, selective filtering by protocol, port, or IP address, and conversion of ETL files to PCAPNG format for analysis in tools like Wireshark. Real-time traffic displays are also supported for quick diagnostics. While effective for many scenarios, PktMon.exe lacks support for persistent captures across reboots, for which netsh.exe is recommended. The techniques outlined above offer administrators a practical, software-free approach to deep packet inspection for troubleshooting Always On VPN issues.

Have you used PktMon.exe for network troubleshooting? Feel free to share tips and tricks in the comments section below!

Additional Information

Getting Started with Windows Packet Monitor (PktMon.exe)

PktMon.exe Filter Reference

Open-source Etl2pcap for netsh.exe captures

Always On VPN Discord Channel

I’m excited to announce the launch of a brand-new Discord channel dedicated to administrators working with Always On VPN! Whether you’re a seasoned pro or just getting started, this community is designed to be your go-to hub for collaboration, troubleshooting, and staying up to date on all things Always On VPN. The channel was established by my good friend Leo D’Arcy, the creator of the popular Always On VPN Dynamic Profile Generator (DPC) software.

Why Discord?

Always On VPN is a powerful solution for secure, seamless remote connectivity, but managing it comes with its own set of challenges. From configuration quirks to deployment strategies, administrators often need a space to share insights, ask questions, and learn from one another in real time. That’s where our new Discord channel comes in.

Community Forum

Discord offers a dynamic, user-friendly platform for instant communication and community building. Unlike forums or email threads, it’s a place where you can start a conversation, jump into live discussions, share resources, ask questions, share important insights or experiences, and much more.

Channels

Today, the Always On VPN Discord channel is part of the Microsoft Remote Access User Group Discord Server. It consists of multiple channels divided into the following topics.

General – This is a great place to introduce yourself and say hello to everyone!

DPC-Development – Here, you can ask questions about DPC, provide feedback, and suggest new features and functionality.

DPC-Chat – This channel is for administrators to discuss all things DPC, including deployment strategies, operation, support, and more.

Aovpn-Chat – If you’ve deployed Always On VPN but aren’t using DPC, this is your channel! Although DPC is fantastic, not everyone is using it. In this channel, you can submit questions and share general information about Always On VPN.

Gsa-Chat – We’ve also included a Microsoft Entra Global Secure Access channel for the new Microsoft Security Service Edge (SSE) solution, which includes Entra Private Access. This channel is pretty quiet right now. Hopefully, it will grow in the future!

DirectAccess-Chat – Yes, we realize some of you are still running DirectAccess, so there’s also a channel for you! Feel free to drop in and ask questions here, hopefully about migrating soon. 😉

Who Is This For?

This channel is open to anyone managing Microsoft secure remote access products. Whether you’re an IT administrator in a small business, an enterprise network engineer, or a consultant helping clients stay connected. If you’re working with Microsoft remote access technologies, this is the place to be!

Why Not Reddit?

Funny story: I tried to create an Always On VPN subreddit a few years ago. It lasted one day before it was banned! No reason was given, and I couldn’t get anyone from Reddit to respond. I answer questions ad hoc on Reddit all the time, but there’s no dedicated space for Always On VPN or Microsoft remote access in general.

How To Join

Joining our Discord channel is easy.

  1. Click this link.
  2. Set up your Discord account if you don’t already have one. It’s free and only takes a minute!
  3. Optionally, you can download the Discord app here.
  4. Say hello and introduce yourself in the #general channel.
  5. Explore the other channels, ask questions, give feedback, and share your expertise!

See You There!

Leo and I, along with many other experienced Always On VPN administrators, are on the forums daily. We encourage you to share your expertise, ask questions, and help others along the way. The more we contribute, the stronger this resource becomes for everyone. Join us today!

Additional Information

Always On VPN Discord Channel

Always On VPN Dynamic Profile Configurator (DPC)

DPC on GitHub

DirectAccess Fails on Windows 11 24H2

Microsoft recently released Windows 11 24H2. Not long after the release there have been numerous reports of DirectAccess failing after performing an in-place upgrade from previous versions of Windows 11. New installations of Windows 11 24H2 experience the same problem.

Update 10/28/2024: This issue is resolved with KB5044384.

Testing

After downloading and configuring a Windows 11 24H2 test client I was able to quickly reproduce the issue. While previous versions of Windows 11 can connect to my test DirectAccess server without issue, the Windows 11 24H2 client fails.

Troubleshooting

Looking at the DirectAccess status indicator in the UI the DirectAccess connection remains ‘Connecting’ perpetually. Further investigation indicates an IP-HTTPS interface error. Running the command netsh.exe interface httpstunnel show interface reveals an error code 0x57 (invalid parameter) with the following error message.

Failed to connect to the IPHTTPS server. Waiting to reconnect.

Workaround

Currently there is no known root cause for this issue and there is no available workaround. Administrators should delay upgrading to Windows 11 24H2 if DirectAccess is deployed in the organization. I will continue to investigate and post additional information as I learn more. Stay tuned!

Additional Information

Troubleshooting DirectAccess IP-HTTPS Error Code 0x800b0109

Troubleshooting DirectAccess IP-HTTPS Error Code 0x90320

Troubleshooting DirectAccess IP-HTTPS Error 0x80090326

Troubleshooting DirectAccess IP-HTTPS Error 0x2af9

Microsoft DirectAccess Now Formally Deprecated

Always On VPN Device Tunnel Fails to Connect Automatically

After the April 2024 Microsoft security updates were released, many Always On VPN administrators noticed that the device tunnel suddenly stopped connecting automatically for many, if not all, their endpoints.

Note: There were additional problems with the April 2024 security update that affected the Always On VPN device tunnel. Details here.

Troubleshooting

When this problem occurs, administrators can establish the device tunnel connection successfully if it is initiated manually. This indicates that there are no issues with the IKEv2 VPN connection or security configuration.

Subscription Activation

The root cause of this issue is related to a subscription activation issue broken in the April 2024 security updates. In this case, Windows 10/11 Enterprise Edition devices that were initially provisioned using Professional Edition and used a step-up upgrade (subscription activation) to Enterprise Edition are reverting to Professional Edition. The Always On VPN device tunnel requires Enterprise Edition to work correctly. Although you can deploy a device tunnel to Windows Professional, it will not connect automatically. It will, however, connect manually.

KB5040527

On July 25, 2024, Microsoft released a preview of updates (KB5040527), including a fix for this subscription activation issue. Administrators experiencing problems with Always On VPN device tunnels where their devices revert to Professional Edition can install this update to resolve this issue.

Additional Information

Always On VPN Device Tunnel Issue with the Microsoft April 2024 Security Update

Always On VPN Device Tunnel Status Indicator

Always On VPN Devcie Tunnel Only Deployment Considerations