Configuring Proper Time Synchronization in an Active Directory Domain

Wall clock representing time synchronization

Accurate time is critical in an Active Directory environment. Kerberos authentication depends on it, and by default it tolerates no more than five minutes of clock skew between a client and a domain controller. Certificate validity periods, CRL publication, OCSP responses, and log correlation all depend on it too, which becomes even more important as organizations move to short-lived certificates. During a recent engagement to assess and remediate a customer’s Active Directory Certificate Services (AD CS) deployment, I noticed intermittent Kerberos authentication anomalies that didn’t line up with anything in the PKI itself. The root cause turned out to be time synchronization, which nobody had configured correctly across the domain. This post explains what I found and how I fixed it. I’ve reproduced the customer’s configuration in my lab, so the examples and output come from lab.richardhicks.net, but the process is the same one I used in the customer’s environment.

What I Found

When I reviewed time configuration across the customer’s domain, I found several problems, including the following.

  • Inconsistent domain controller configuration. Some domain controllers had never been configured and were still running the defaults. Others had been pointed manually at different external time sources, presumably by different administrators at different times. This resulted in more than one time root in the domain, which is exactly what the Windows time hierarchy is designed to prevent.
  • The PDC emulator was not authoritative. The domain controller holding the PDC emulator role had no external time source configured, so it wasn’t anchoring the domain to UTC.
  • Hyper-V was quietly providing the time. Most of the domain controllers were virtual machines running on Hyper-V. The Hyper-V time synchronization integration service (VMICTimeProvider) was enabled on all of them, and W32Time on the domain controllers was taking time from the host instead of the domain hierarchy.
  • The Hyper-V hosts had no time configuration at all. Most of the domain was running on Hyper-V hosts that were workgroup members. Workgroup machines don’t participate in the domain time hierarchy, and nobody had configured them. They were running on their own clocks, polling time.windows.com infrequently, if they could reach it at all.

The result was a loop with no anchor. The domain controllers took their time from the hosts, the hosts drifted on their own, and nothing in the environment was reliably tied to UTC. Different domain controllers on different hosts could disagree by a meaningful amount, which explained the inconsistent Kerberos behavior. In my lab, the PDC emulator showed the problem clearly.

PS C:\> w32tm.exe /query /status
Leap Indicator: 0(no warning)
Stratum: 1 (primary reference - syncd by radio clock)
...
ReferenceId: 0x564D5450 (source name: "VMTP")
...
Source: VM IC Time Synchronization Provider

Don’t be fooled by Stratum 1. The VM IC provider always reports Stratum 1, but the real source is the Hyper-V host’s clock. A quick comparison against a public time server showed the PDC emulator was about 840 milliseconds off UTC.

PS C:\> w32tm.exe /stripchart /computer:time.cloudflare.com /samples:3 /dataonly
Tracking time.cloudflare.com [162.159.200.1:123].
Collecting 3 samples.
17:36:52, +00.8405031s
17:36:54, +00.8443389s
17:36:56, +00.8415804s

That’s not enough to break Kerberos on its own, but it was drifting, and in the customer’s environment, with multiple hosts and multiple time roots, the differences were much larger.

How Time Sync Should Work

Before making changes, it’s worth reviewing how Windows time synchronization is designed to work in an Active Directory domain. The hierarchy is simple and consists of the following.

  • The forest root PDC emulator is the authoritative time source. It is the only domain controller that should synchronize with an external source, and it advertises itself as a reliable time server (AnnounceFlags 5).
  • All other domain controllers follow the domain hierarchy. They use the NT5DS type and synchronize with the PDC emulator (directly or through their domain’s PDC emulator in a multi-domain forest). They advertise as time servers, but not as reliable ones (AnnounceFlags 10, the default).
  • Domain members synchronize with a domain controller. This is the default behavior for every domain-joined machine, although virtual machines need one adjustment, which I cover next.

Virtual Machines

Virtualization adds a wrinkle. On Hyper-V, the time synchronization integration service registers its own W32Time provider, VMICTimeProvider, which feeds the guest time from the host. It’s enabled by default on every virtual machine, and on a domain-joined VM it competes with the domain hierarchy and usually wins. Microsoft’s guidance is to disable VMICTimeProvider on virtual domain controllers so they get their time from the PDC emulator instead. I recommend disabling it on domain member VMs as well, so every domain-joined machine follows the same hierarchy.

Workgroup Hyper-V Hosts

The Hyper-V hosts matter too. If they’re domain members, they’ll follow the domain hierarchy automatically. If they’re workgroup members, as they were here, they need to be configured explicitly. Even with VMICTimeProvider disabled, the host’s clock still sets each VM’s time at startup and after a restore from a saved state, and the host needs accurate time for its own logs and certificates.

Target Configuration

The end state looks like this. The PDC emulator and the Hyper-V hosts both sync with the same public source, and every domain-joined machine, physical or virtual, follows the domain hierarchy.

SystemTime sourceConfigured by
PDC emulatortime.cloudflare.comDC Time Sync GPO
Other domain controllersPDC emulatorDC Time Settings GPO
Domain members (physical and virtual)Domain controllersDomain Member Time Settings GPO
Hyper-V hosts (workgroup)time.cloudflare.comLocal configuration

Resetting Domain Controllers to the Default Configuration

With domain controllers configured inconsistently, the cleanest approach is to return every one of them to the default configuration and then manage time centrally with Group Policy. Resetting first is important. Local settings remain in the registry underneath any policy, and if a domain controller ever stops receiving the policy (for example, after the PDC emulator role moves), it falls back to whatever was configured locally. Leftover manual peer settings would quietly create a second time root.

Restoring the Defaults

The following commands reset W32Time on every domain controller in the domain. They re-enable the Hyper-V time provider (the default), restore domain hierarchy synchronization, reset the peer list to the stock time.windows.com,0x9 value, and set AnnounceFlags back to 10 with /reliable:no.

$DomainControllers = (Get-ADDomainController -Filter *).HostName
Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
# Re-enable the Hyper-V time provider (default)
$VmicKey = 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
If (Test-Path -Path $VmicKey) {
Set-ItemProperty -Path $VmicKey -Name Enabled -Value 1
}
# Restore domain hierarchy sync, default peer list, and default AnnounceFlags (10)
w32tm.exe /config /manualpeerlist:"time.windows.com,0x9" /syncfromflags:domhier /reliable:no /update
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover
}

I recommend this targeted approach over w32tm.exe /unregister and w32tm.exe /register. Re-registering the service rebuilds the entire W32Time configuration, but it can also remove the VMICTimeProvider subkey. That key is created by the Hyper-V integration components, not by W32Time, and it’s the key we’ll target with Group Policy in the next step.

Verifying the Reset

Next, confirm each domain controller is running the defaults and that no existing Group Policy is configuring W32Time.

Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
Write-Output "=== $env:COMPUTERNAME ==="
w32tm.exe /query /configuration | Select-String 'Type:|NtpServer:|AnnounceFlags:' | ForEach-Object { $_.Line.Trim() }
w32tm.exe /query /source
Write-Output "Time policy present: $(Test-Path -Path 'HKLM:\SOFTWARE\Policies\Microsoft\W32Time')"
}

Each domain controller should report Type: NT5DS (Local) and AnnounceFlags: 10 (Local), and the time policy check should return False. If it returns True, another GPO is already configuring W32Time. Find it and remove those settings before continuing. Don’t be surprised if the source still shows VM IC Time Synchronization Provider on some domain controllers at this point. That’s the default behavior we’re about to fix.

Configuring Time Sync with Group Policy

With every domain controller back to a known state, the next step is to configure time centrally with three GPOs. Two are linked to the Domain Controllers OU, and the third is linked to the domain root for domain members. The design includes the following.

GPOApplies toSettings
DC Time SettingsAll domain controllersType NT5DS, AnnounceFlags 10, NTP client and server enabled, VMICTimeProvider disabled
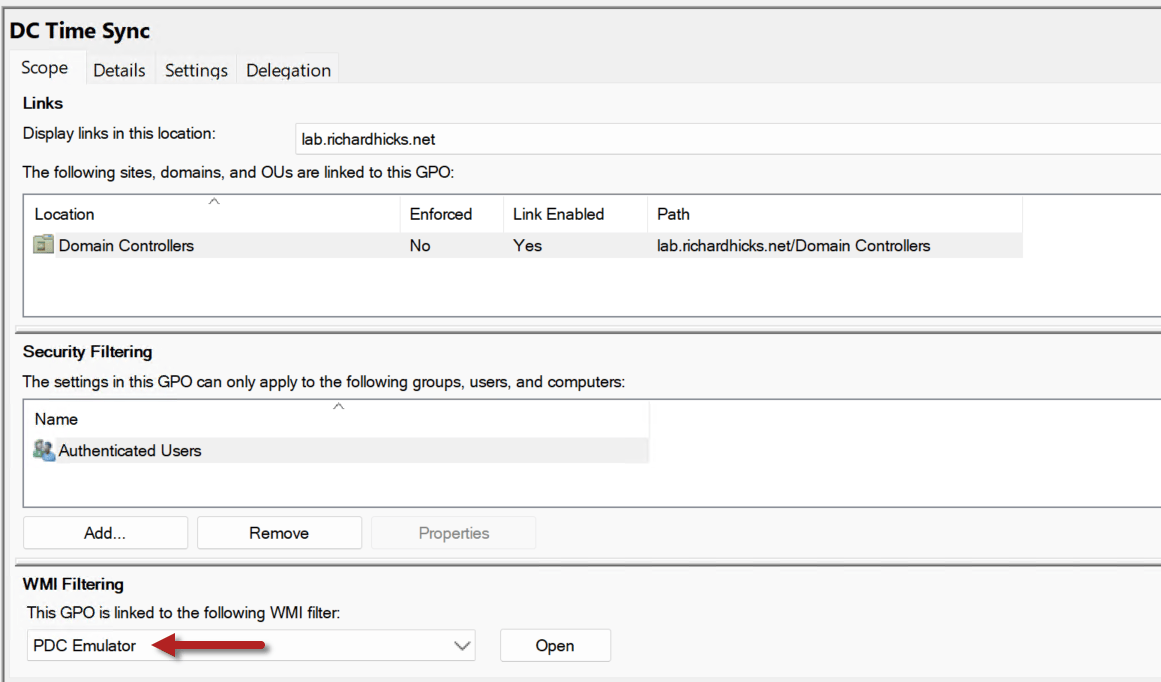
DC Time SyncPDC emulator only (WMI filter)Type NTP, NtpServer time.cloudflare.com,0x8 time.nist.gov,0xa, AnnounceFlags 5
Domain Member Time SettingsAll domain members (linked to the domain root)VMICTimeProvider disabled

DC Time Sync is linked with a higher precedence (link order 1), so on the PDC emulator its values override the baseline from DC Time Settings. Every other domain controller receives only the baseline. A nice benefit of this design is that it follows the PDC emulator role automatically. If the role moves to another domain controller, the WMI filter matches the new role holder, and the old one falls back to the baseline with no administrator intervention. However, if the PDC emulator role moves to another DC, don’t forget to update the outbound access rules on the edge firewall to allow the new server to access the public time resource.

Choosing a Time Source

I used time.cloudflare.com as the primary time source for this customer, with time.nist.gov as a fallback. You can use any reliable public time service, such as time.windows.com or a regional pool.ntp.org address. Separate multiple servers with spaces in the NtpServer value.

Adding a Fallback Time Source

A single upstream time source works, but it makes the entire domain dependent on one provider. Microsoft recommends configuring three or more time servers when using multiple peers, or, with only two, marking one with the UseAsFallbackOnly flag (0x2). I chose the latter, setting NtpServer to time.cloudflare.com,0x8 time.nist.gov,0xa. The 0xa flag combines client mode (0x8) and fallback only (0x2), so W32Time uses NIST only when Cloudflare is unavailable. Keep the following in mind when choosing a fallback.

  • It removes a single point of failure. Cloudflare’s time service is highly reliable, but the service itself isn’t the only thing that can fail. A DNS resolution failure, a BGP route leak or hijack affecting the provider’s prefixes, an upstream ISP routing problem, or a firewall change can all make a single provider unreachable from your network. NIST runs on a completely separate network and doesn’t use anycast, so an event that affects one provider is unlikely to affect the other.
  • An outage isn’t catastrophic. Even if the PDC emulator can’t reach any upstream source, it keeps running on its own clock and continues serving time to the rest of the domain. Every domain controller and domain member still follows the PDC emulator, so the domain stays in sync with itself while slowly drifting from UTC. That’s what matters most for Kerberos, which compares the client’s clock with the domain controller’s clock, not with UTC. A typical system clock drifts by a few seconds per day at most, so an outage lasting hours or even days has no practical impact. When the time source becomes reachable again, W32Time corrects the accumulated offset automatically.
  • Both sources must handle leap seconds the same way. Cloudflare and NIST both insert leap seconds as a one-second step, so they’re a safe pair. Google, AWS, and Meta smear leap seconds instead, so don’t pair one of them with Cloudflare or NIST. The next section explains why.
  • A fallback doesn’t improve accuracy. A second source improves availability, not accuracy. With UseAsFallbackOnly, W32Time only consults NIST when Cloudflare is unreachable, so there’s nothing to cross-check against. Even with two active peers, there’s no majority to decide which one is right if they disagree. That’s fine for a typical Active Directory domain, which doesn’t require high-accuracy time.

Leap Second Considerations

Avoid mixing time services that handle leap seconds differently. A leap second is an occasional one-second adjustment to UTC that keeps it aligned with the Earth’s rotation. Most time services, including Cloudflare and NIST, apply it the standard way, by inserting the extra second all at once. Google (and AWS) instead “smear” it by slightly slowing their clocks over a 24-hour window, so during that period their time differs from other services by up to half a second. If a domain controller has both kinds of servers in its peer list, they disagree during a leap event, and the results are unpredictable. Pick one approach and use it consistently. You can read more about each approach in Google’s leap smear documentation and Cloudflare’s NTP documentation.

Allowing Outbound NTP

The PDC emulator must be able to reach both time services on UDP port 123. In the customer’s environment, as in my lab, outbound NTP was blocked at the edge firewall. I added a rule allowing outbound UDP 123 from the PDC emulator to the IPv4 and IPv6 addresses of both time services. Cloudflare publishes its addresses in its documentation, and NIST publishes the list of servers that time.nist.gov rotates across. Be sure to include both address families if your domain controllers have IPv6 connectivity, because W32Time will often prefer IPv6 when the name resolves to both. Also, remember to update the rule if the PDC emulator role moves to a different server. You can validate reachability to both services from the PDC emulator before configuring anything.

w32tm.exe /stripchart /computer:time.cloudflare.com /samples:3 /dataonly
w32tm.exe /stripchart /computer:time.nist.gov /samples:3 /dataonly

If both return offsets, you’re good to go. An error of 0x800705B4 indicates a timeout, which usually means UDP 123 is blocked or the IPv6 path isn’t working.

Creating the GPOs

The following script creates the WMI filter and all three GPOs. It links the two domain controller GPOs to the Domain Controllers OU and the member GPO to the domain root. It requires the GroupPolicy and ActiveDirectory modules (Install-WindowsFeature -Name GPMC, RSAT-AD-PowerShell on Windows Server) and Domain Admin rights. Run it in Windows PowerShell 5.1. You can also download the script from GitHub.

#Requires -Modules GroupPolicy, ActiveDirectory
$ErrorActionPreference = 'Stop'
# Variables
$Domain = Get-ADDomain
$DomainFqdn = $Domain.DNSRoot
$DomainDn = $Domain.DistinguishedName
$DcOu = $Domain.DomainControllersContainer
$Pdc = $Domain.PDCEmulator
$PolicyKey = 'HKLM\SOFTWARE\Policies\Microsoft\W32Time'
$NtpServer = 'time.cloudflare.com,0x8 time.nist.gov,0xa'
# Create the WMI filter (or reuse it if it already exists)
$WmiFilterName = 'PDC Emulator'
$WmiQuery = 'SELECT * FROM Win32_ComputerSystem WHERE DomainRole = 5'
$SomPath = "CN=SOM,CN=WMIPolicy,CN=System,$DomainDn"
$WmiFilter = Get-ADObject -Server $Pdc -SearchBase $SomPath -LDAPFilter "(&(objectClass=msWMI-Som)(msWMI-Name=$WmiFilterName))" -Properties 'msWMI-ID'
If ($null -eq $WmiFilter) {
$WmiId = "{$([Guid]::NewGuid().ToString().ToUpper())}"
$Now = (Get-Date).ToUniversalTime().ToString('yyyyMMddHHmmss.ffffff-000')
$FilterParams = @{
Server = $Pdc
Name = $WmiId
Type = 'msWMI-Som'
Path = $SomPath
OtherAttributes = @{
'msWMI-Name' = $WmiFilterName
'msWMI-Parm1' = 'Domain controller holding the PDC emulator role'
'msWMI-Parm2' = "1;3;10;$($WmiQuery.Length);WQL;root\CIMv2;$WmiQuery;"
'msWMI-Author' = "$env:USERNAME@$DomainFqdn"
'msWMI-ID' = $WmiId
'msWMI-CreationDate' = $Now
'msWMI-ChangeDate' = $Now
}
}
New-ADObject @FilterParams
}
Else {
$WmiId = $WmiFilter.'msWMI-ID'
}
# DC Time Settings (all domain controllers)
$AllDcGpo = New-GPO -Name 'DC Time Settings' -Comment 'Baseline W32Time settings for all domain controllers' -Server $Pdc
$Gpo = @{ Name = $AllDcGpo.DisplayName; Server = $Pdc }
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'Type' -Type String -Value 'NT5DS' | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Config" -ValueName 'AnnounceFlags' -Type DWord -Value 10 | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\TimeProviders\NtpClient" -ValueName 'Enabled' -Type DWord -Value 1 | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\TimeProviders\NtpServer" -ValueName 'Enabled' -Type DWord -Value 1 | Out-Null
# Disable the Hyper-V time provider (Group Policy Preference, writes to the service key)
$PrefParams = @{
Name = $AllDcGpo.DisplayName
Server = $Pdc
Context = 'Computer'
Action = 'Update'
Key = 'HKLM\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
ValueName = 'Enabled'
Type = 'DWord'
Value = 0
}
Set-GPPrefRegistryValue @PrefParams | Out-Null
# DC Time Sync (PDC emulator only)
$PdcGpo = New-GPO -Name 'DC Time Sync' -Comment 'External NTP source for the PDC emulator' -Server $Pdc
$Gpo = @{ Name = $PdcGpo.DisplayName; Server = $Pdc }
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'Type' -Type String -Value 'NTP' | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Parameters" -ValueName 'NtpServer' -Type String -Value $NtpServer | Out-Null
Set-GPRegistryValue @Gpo -Key "$PolicyKey\Config" -ValueName 'AnnounceFlags' -Type DWord -Value 5 | Out-Null
# Assign the WMI filter to DC Time Sync
$PdcGpoDn = "CN={$($PdcGpo.Id.ToString().ToUpper())},CN=Policies,CN=System,$DomainDn"
Set-ADObject -Server $Pdc -Identity $PdcGpoDn -Replace @{ gPCWQLFilter = "[$DomainFqdn;$WmiId;0]" }
# Domain Member Time Settings (all domain members)
$MemberGpo = New-GPO -Name 'Domain Member Time Settings' -Comment 'Disable the Hyper-V time provider so domain members follow the domain hierarchy' -Server $Pdc
$PrefParams = @{
Name = $MemberGpo.DisplayName
Server = $Pdc
Context = 'Computer'
Action = 'Update'
Key = 'HKLM\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider'
ValueName = 'Enabled'
Type = 'DWord'
Value = 0
}
Set-GPPrefRegistryValue @PrefParams | Out-Null
# Link both DC GPOs (DC Time Sync takes precedence)
New-GPLink -Name 'DC Time Sync' -Target $DcOu -LinkEnabled Yes -Order 1 -Server $Pdc | Out-Null
New-GPLink -Name 'DC Time Settings' -Target $DcOu -LinkEnabled Yes -Order 2 -Server $Pdc | Out-Null
# Link the member GPO to the domain root
New-GPLink -Name 'Domain Member Time Settings' -Target $DomainDn -LinkEnabled Yes -Server $Pdc | Out-Null
Get-GPInheritance -Target $DcOu -Server $Pdc | Select-Object -ExpandProperty GpoLinks | Format-Table DisplayName, Order, Enabled
Get-GPInheritance -Target $DomainDn -Server $Pdc | Select-Object -ExpandProperty GpoLinks | Format-Table DisplayName, Order, Enabled

There are a few things worth noting about this script.

  • Everything targets the PDC emulator. The GroupPolicy cmdlets talk to the PDC emulator by default, but the ActiveDirectory cmdlets can pick any domain controller. Without -Server, Set-ADObject may land on a domain controller where the new GPO hasn’t replicated yet, and the script fails partway through. I hit this in the field, so the script now pins every call to the PDC emulator.
  • Only the required values are written. Enabling the Global Configuration Settings Administrative Template writes every value it contains, including some outdated clock discipline defaults. Setting individual registry values avoids that, and everything not set by policy keeps its default. The trade-off is that GPMC may show these under Extra Registry Settings instead of Windows Time Service. That’s cosmetic.
  • VMICTimeProvider is disabled with a preference, not a policy. There is no Administrative Template setting for it. The Group Policy Preference writes directly to the service key, so it persists even if the GPO stops applying, which is what you want for a domain controller.
  • The member GPO needs only the preference. Domain members already default to NT5DS, so VMICTimeProvider is the only thing keeping virtual machines off the domain hierarchy. Because it’s linked to the domain root, it also applies to domain controllers. That’s harmless, since DC Time Settings sets the same value and takes precedence.
  • The WMI filter is assigned directly. The GroupPolicy module has no cmdlet for creating or assigning WMI filters, so the script writes the gPCWQLFilter attribute itself.
  • Multi-domain forests. DomainRole = 5 matches the PDC emulator of any domain. Link DC Time Sync only in the forest root domain. Child domain PDC emulators should follow the domain hierarchy.
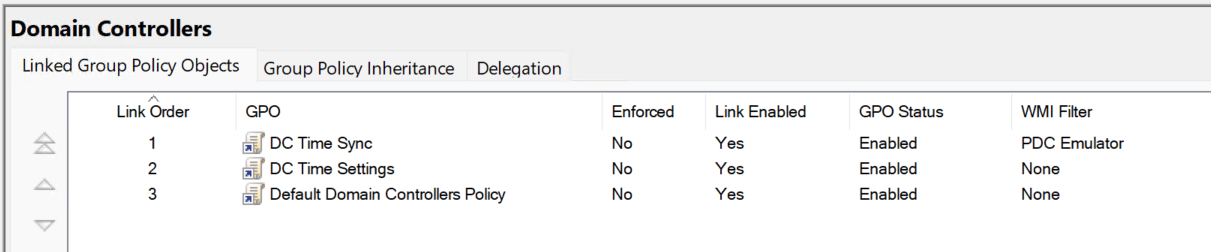
DC Time Sync and DC Time Settings GPOs linked to the Domain Controllers OU

GPOs applied to domain controllers.

DC Time Sync GPO with the PDC Emulator WMI filter applied

DC Time Sync GPO with WMI filtering applied to PDC emulator.

Applying the Policies

Force replication so every domain controller has the new GPOs, then apply them and restart the time service.

Invoke-Command -ComputerName $Pdc -ScriptBlock { repadmin.exe /syncall /AdeP | Out-Null }
Start-Sleep -Seconds 60
Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
gpupdate.exe /target:computer /force | Out-Null
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover | Out-Null
}

Domain members pick up the new GPO at their next policy refresh. However, W32Time reads which providers are enabled only when the service starts, so a member VM keeps using VMICTimeProvider until W32Time restarts or the machine reboots. To switch a member over immediately, run the following commands on it.

gpupdate.exe /target:computer /force
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover

Configuring the Workgroup Hyper-V Hosts

With the domain controllers fixed, the last piece is the Hyper-V hosts. In the customer’s environment, most of the domain ran on hosts that were workgroup members, and none had any time configuration. The VMs no longer take their time from the host continuously, but the host’s clock still sets each VM’s time at startup and after a restore from a saved state. Workgroup machines don’t participate in the domain hierarchy, so Group Policy can’t help here. Each host must be configured locally, and there are two reasonable options.

  • Sync directly from the public time service. This is what I did for the customer. The hosts don’t depend on a VM they’re running, which avoids a chicken-and-egg problem at boot. It does require allowing outbound UDP 123 from each host.
  • Sync from the PDC emulator. This keeps a single internal source of truth and needs no additional edge firewall rules, since domain controllers answer NTP requests by default. The downside is that the host boots before the PDC emulator VM and runs on its own clock until the domain controller is available.

Either way, everything traces back to the same UTC source. Run the following commands locally on each Hyper-V host.

# Sync from Cloudflare, with NIST as a fallback
# (0x1 = use SpecialPollInterval, 0x2 = fallback only, 0x8 = client mode)
w32tm.exe /config /manualpeerlist:"time.cloudflare.com,0x9 time.nist.gov,0xb" /syncfromflags:manual /update
# Poll every 1024 seconds (workgroup machines default to once a week)
Set-ItemProperty -Path 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\NtpClient' -Name SpecialPollInterval -Value 1024
Restart-Service -Name W32Time
w32tm.exe /resync /rediscover

Setting SpecialPollInterval is important. The workgroup default is 604,800 seconds, or one week, which is far too infrequent to keep a virtualization host accurate. The 0xb flag on time.nist.gov adds fallback only (0x2) to the same flags, so the hosts follow the same primary and fallback design as the PDC emulator. To sync from the PDC emulator instead, replace the peer list with the PDC emulator’s name or IP address, and optionally add another domain controller with the 0xb flag as a fallback. Use IP addresses if the hosts don’t use the domain’s DNS servers.

Domain Member Virtual Machines

VMICTimeProvider is enabled by default on every Hyper-V VM, not just domain controllers, so domain-joined member VMs take their time from the host instead of the domain hierarchy. With accurate hosts, that works, but it creates a second time root. Domain controllers follow the PDC emulator, while member VMs follow whichever host they run on. In my lab, a member VM was about 77 milliseconds off the PDC emulator, even though both its host and the PDC emulator synced with Cloudflare. If a host loses access to its time source, its VMs drift away from the domain controllers, which is the original problem in a new place. The Domain Member Time Settings GPO prevents this. It disables only the W32Time provider, not the Hyper-V time synchronization integration service, so VMs still get their clock set at startup and after a restore from a saved state.

Validating the Configuration

Once everything is in place, confirm each tier of the hierarchy is getting time from the right place, including the domain controllers, domain members, the Hyper-V hosts, and the domain as a whole.

Validating Domain Controllers

Run the following commands to check the time configuration and status of every domain controller.

Invoke-Command -ComputerName $DomainControllers -ScriptBlock {
Write-Output "=== $env:COMPUTERNAME ==="
w32tm.exe /query /configuration | Select-String 'Type:|NtpServer:|AnnounceFlags:' | ForEach-Object { $_.Line.Trim() }
w32tm.exe /query /status | Select-String 'Stratum:|Root Dispersion:|Source:' | ForEach-Object { $_.Line.Trim() }
Write-Output "VMICTimeProvider Enabled: $(Get-ItemPropertyValue -Path 'HKLM:\SYSTEM\CurrentControlSet\Services\W32Time\TimeProviders\VMICTimeProvider' -Name Enabled)"
}
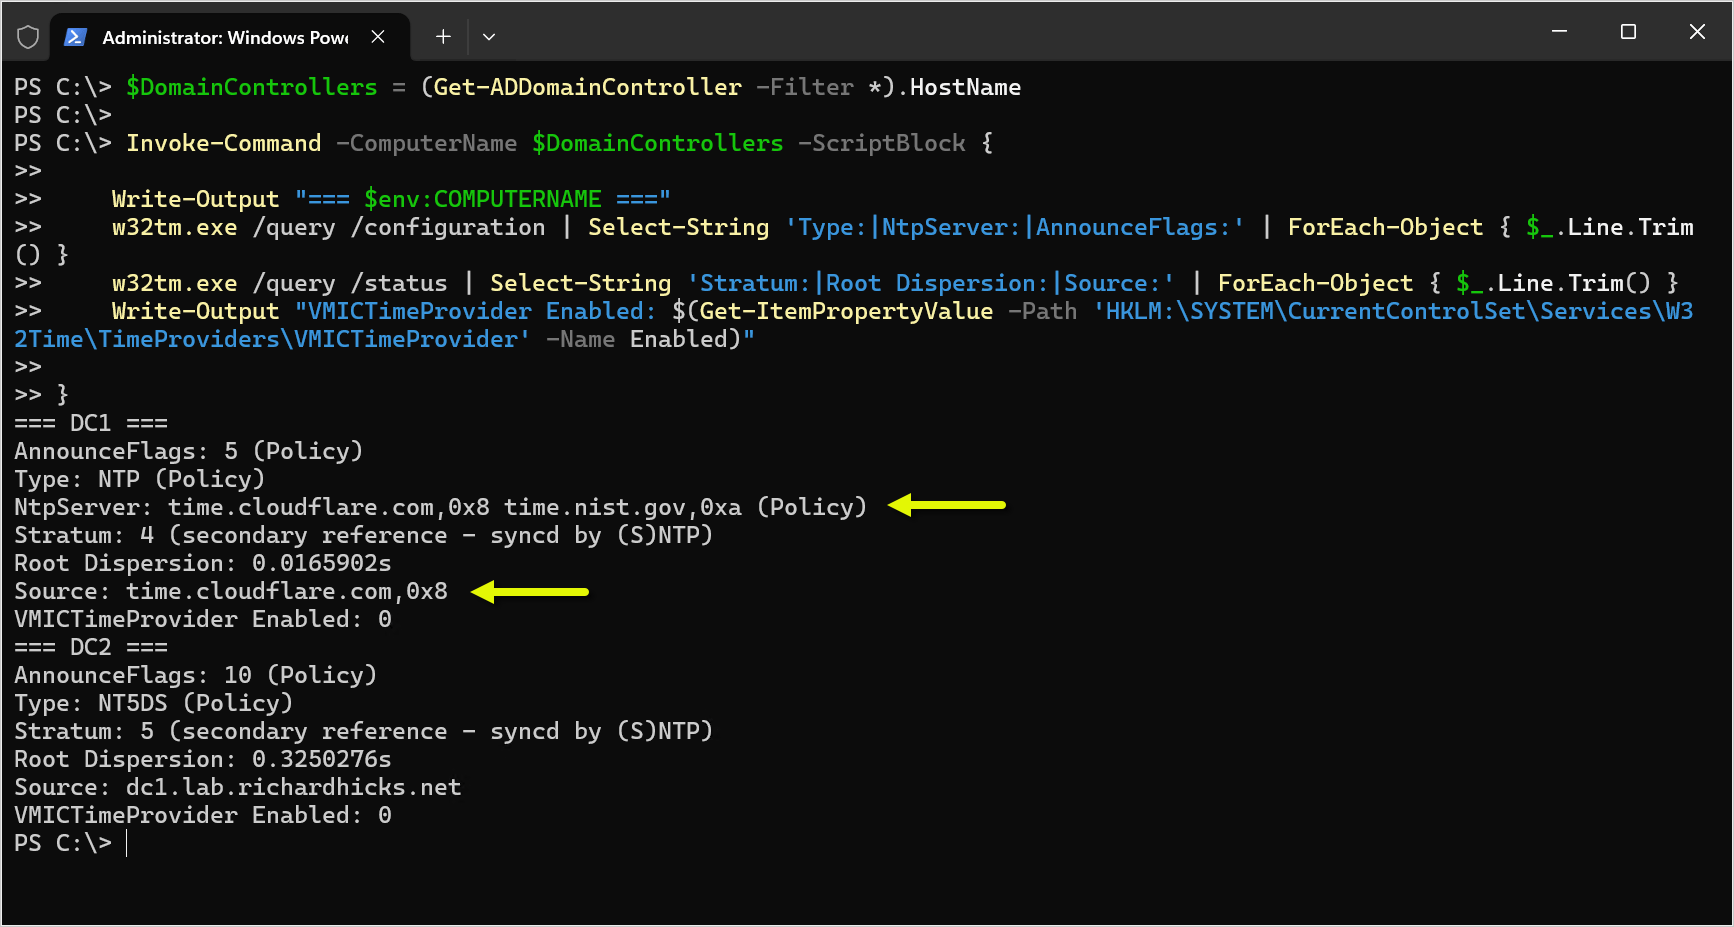
PowerShell output validating W32Time configuration on each domain controller

Validating domain controller time configuration settings.

The .Line.Trim() is there for a reason. Select-String results returned through Invoke-Command are deserialized objects that PowerShell can’t format, so without it you’ll see blank lines instead of the output. The following table shows what to look for on each type of server.

ServerTypeAnnounceFlagsSourceStratumVMICTimeProvider
PDC emulatorNTP (Policy)5 (Policy)time.cloudflare.com,0x840
Other domain controllersNT5DS (Policy)10 (Policy)PDC emulator50
Hyper-V hostsNTP (Local)n/atime.cloudflare.com,0x94n/a

The (Policy) label confirms Group Policy is in control rather than local settings. Root Dispersion will be high immediately after the service restarts and should settle under a second within about 30 minutes. NtpServer lists both time services, but the source should show time.cloudflare.com. If it shows time.nist.gov, the PDC emulator can’t reach Cloudflare and has switched to the fallback.

Validating Domain Members

On a domain member VM, run the following commands to confirm it follows the domain hierarchy and agrees with the PDC emulator.

w32tm.exe /query /source
w32tm.exe /query /status | Select-String 'Stratum:|Source:|ReferenceId:'
w32tm.exe /stripchart /computer:$Pdc /samples:5 /dataonly
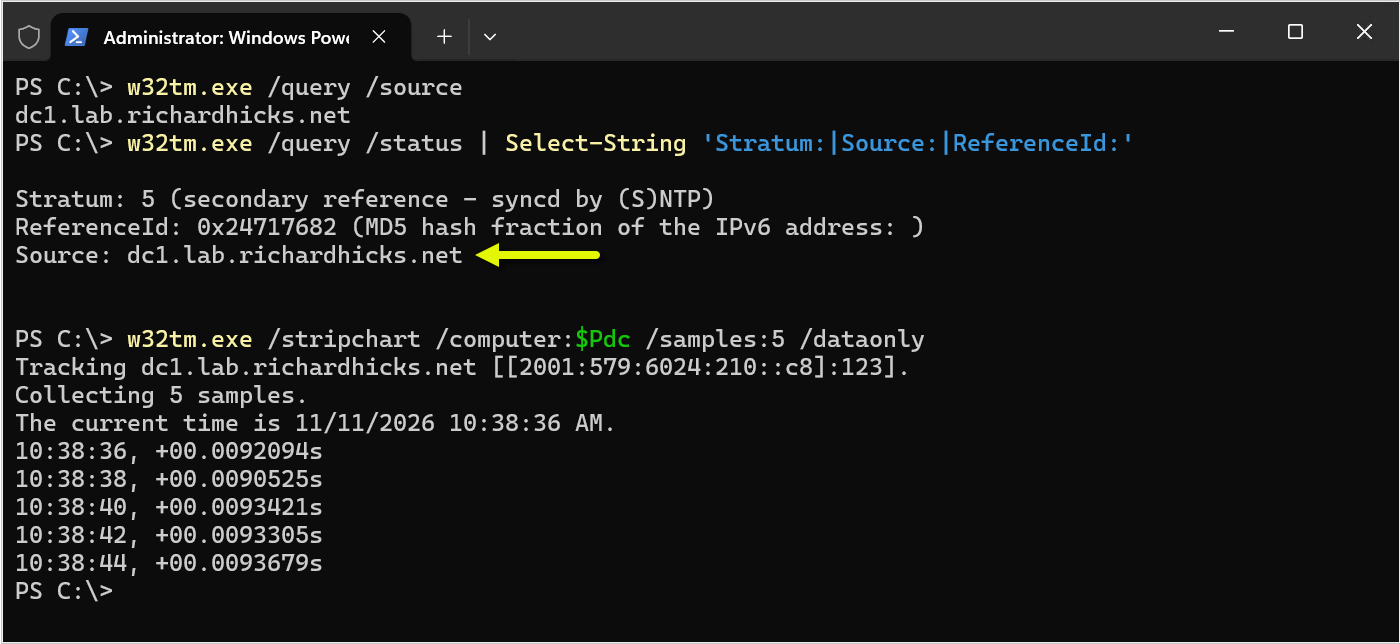
w32tm.exe output on a domain member VM synchronizing with the PDC emulator dc1

Domain member VM synchronizing with the PDC emulator.

The source should be a domain controller, not VM IC Time Synchronization Provider, and the stratum should be one or two levels below the PDC emulator. In my lab, a member VM went from about 77 milliseconds off the PDC emulator to under 10 milliseconds within minutes of switching to the domain hierarchy.

Validating Hyper-V Hosts

On the Hyper-V hosts, run the following commands locally.

w32tm.exe /query /source
w32tm.exe /query /status | Select-String 'Stratum:|Root Dispersion:|Last Successful Sync Time:'
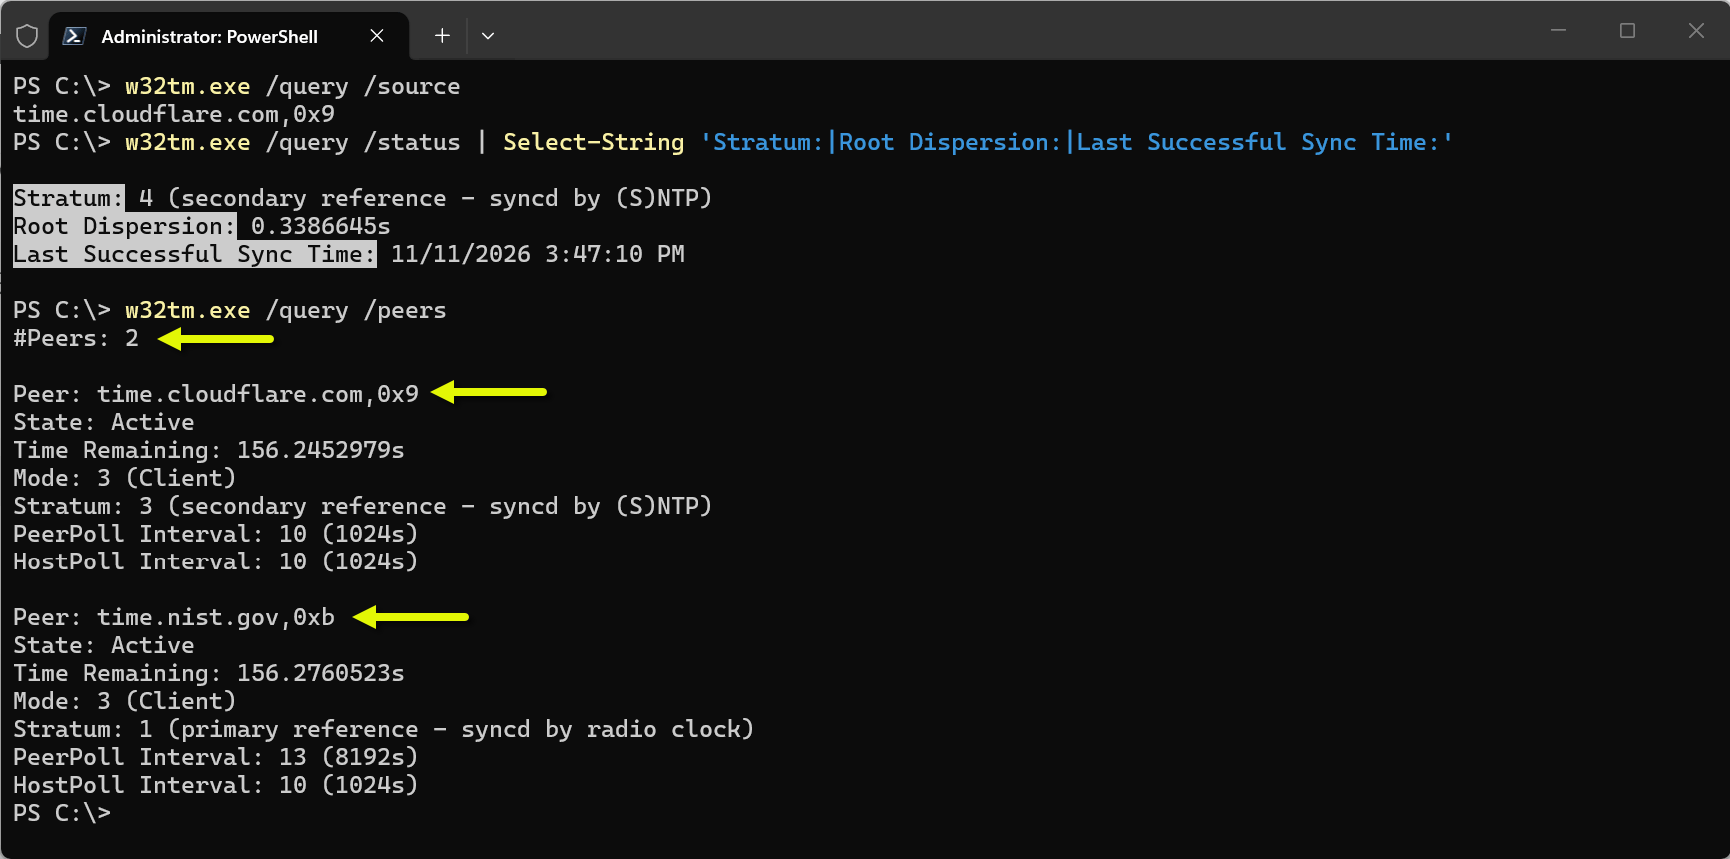
w32tm.exe /query /peers
w32tm.exe output on a Hyper-V host synchronizing with time.cloudflare.com, with time.nist.gov as a fallback peer

Time synchronization settings on the Hyper-V host server.

Both time services are listed as peers. The State for time.cloudflare.com should be Active. A state of Pending that persists usually means the host can’t reach that time server. However, Pending is also normal for up to one polling interval after the service restarts, which is about 17 minutes with a SpecialPollInterval of 1024 seconds, because W32Time rebuilds its peer list and resets the peer statistics. To tell the difference, run w32tm.exe /query /peers /verbose and check LastSyncError. A value of 0x00000000 (Succeeded) means the last sync worked, and the peer will return to Active at its next poll.

Validating the Domain

After things have had time to settle, check the entire domain at once. Every domain controller should show a small offset relative to the PDC emulator, with no errors.

w32tm.exe /monitor /domain:$DomainFqdn
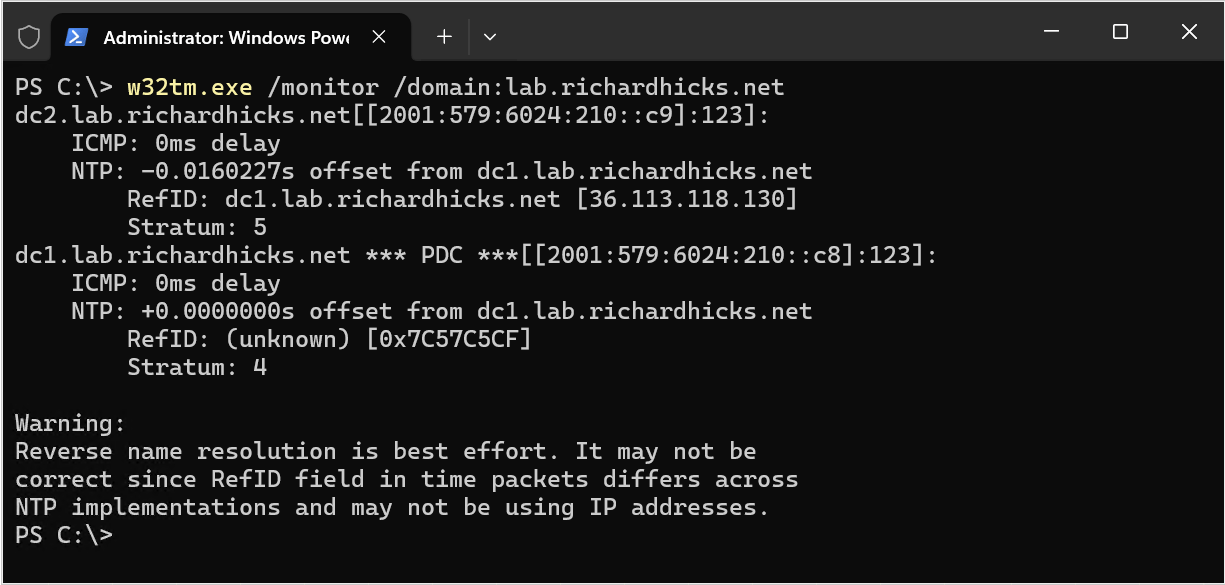
w32tm.exe /monitor output showing all domain controllers in sync with the PDC emulator

All domain controllers synchronizing with the PDC emulator.

You might notice an unusual IPv4 address listed for dc1, such as 36.113.118.130. That’s not dc1’s address, and it’s not a real IPv4 address at all. It’s the RefID, which identifies the server’s upstream time source. The NTP reference ID field is only 32 bits, so when the source is reached over IPv6, as time.cloudflare.com is here, the field contains the first 32 bits of the MD5 hash of the source’s IPv6 address, as defined in RFC 5905. It’s expected behavior and can safely be ignored. In my lab, the PDC emulator went from roughly 840 milliseconds off UTC to closely tracking UTC once it began syncing with Cloudflare. In the customer’s environment, the Kerberos anomalies stopped once all domain controllers and hosts converged on a single source.

Summary

Time synchronization is easy to overlook, especially in virtualized environments where Hyper-V quietly fills in the gaps. In this case, the symptoms showed up as Kerberos anomalies during an AD CS engagement, but the root cause was a domain with no single, authoritative time source. The fix came down to the following steps.

  1. Reset every domain controller to the default W32Time configuration.
  2. Configure the PDC emulator, and only the PDC emulator, to sync with a reliable public time service, plus a second as a fallback, using a WMI-filtered GPO.
  3. Configure all other domain controllers to follow the domain hierarchy and disable VMICTimeProvider on every domain controller with a second GPO.
  4. Disable VMICTimeProvider on domain members with a third GPO linked to the domain root, so virtual machines follow the domain hierarchy too.
  5. Allow outbound UDP 123 for the systems that sync externally.
  6. Explicitly configure any workgroup Hyper-V hosts, since they don’t participate in the domain hierarchy.

With Group Policy managing the domain controllers and domain members, the configuration is consistent, self-documenting, and follows the PDC emulator role automatically if it ever moves.

Additional Information

Windows Time Service Technical Reference

Windows Time Service Tools and Settings

Synchronizing Time on Virtualized AD DS Environments: VMICTimeProvider vs AD

Configure the Root PDC with an Authoritative Time Source and Avoid a Widespread Time Skew

Cloudflare Time Services

NTP Pool Project

NIST Internet Time Service (ITS)

Network Time Protocol Version 4 (RFC 5905)

Managing Windows CLAT (WinCLAT) with Intune Remediations

Microsoft Intune icon

Windows CLAT (WinCLAT) allows IPv4 applications to reach IPv4 destinations on IPv6-only and IPv6-mostly networks. Windows does not permit WinCLAT on Wi-Fi or Ethernet by default, and Microsoft Intune does not currently expose a setting to permit it. This post explains how to deploy the permit setting with Intune Remediations, verify that WinCLAT is translating, and maintain connectivity to Intune when removing the setting.

WinCLAT Configuration Options in Intune

At the time of this writing, Intune does not expose WinCLAT configuration settings in the Settings Catalog or through a CSP. The corresponding Group Policy settings are defined in the built-in Windows template tcpip.admx. However, Intune’s custom ADMX import feature is intended for third-party and custom templates. Microsoft explicitly advises against importing built-in Windows ADMX files when the goal is to configure those settings, recommending the Settings Catalog or a custom profile instead.

Configuring WinCLAT with Remediations

An Intune Remediation can write the same registry value that Group Policy uses to permit WinCLAT on non-cellular interfaces. Windows reads that value as policy and gives it precedence over the local permit setting. If Group Policy already configures the setting on a device, continue managing it through Group Policy, since a policy refresh can overwrite the value written by the remediation script.

Deployment Requirements

Before deploying the Remediation, confirm that clients meet the following connectivity, platform, and licensing requirements.

Intune Connectivity Before WinCLAT Starts

The Intune Management Extension must be able to reach the endpoints it uses to retrieve the script package before WinCLAT starts. Native IPv4 provides that path on dual-stack networks and on IPv6-mostly networks where Windows still has a DHCPv4 lease. On an IPv6-only network, DNS64 and NAT64 can provide access to IPv4-only Intune endpoints by name. If the target network has no working path to the required endpoints before WinCLAT starts, deploy the package from a network that does. After deployment, verify that the device can still check in with Intune from the target network.

NetworkPath to Intune before WinCLAT is enabledExpected delivery path available?
Dual-stackNative IPv4Yes
IPv6-mostly (DHCPv4 option 108)Native IPv4. While WinCLAT is not permitted, Windows does not honor option 108 and takes a DHCPv4 leaseYes
IPv6-only with DNS64/NAT64DNS64 and NAT64Yes
IPv6-only without DNS64/NAT64No path to required IPv4-only endpoints in this scenarioNo

Windows and Intune Prerequisites

Devices must run Windows 11 version 25H2 build 26200.9550 or later, be Microsoft Entra joined or Microsoft Entra hybrid joined, and be enrolled in Intune or co-managed. Verify that device users have a qualifying license, such as Windows Enterprise E3 or E5, and that the Intune Management Extension is installed before running the package on demand.

WinCLAT Policy Settings

The WinCLAT Group Policy settings are in tcpip.admx under Computer Configuration > Policies > Administrative Templates > Network > TCPIP Settings > IPv6 Transition Technologies, and they are stored as DWORD values in the following location.

HKLM\SOFTWARE\Policies\Microsoft\Windows\TCPIP\v6Transition\IPxlatCfgSvc
Registry valuenetsh.exe settingModule propertyPurpose
PermitNonCellularCLATpermitPermitPermits WinCLAT on non-cellular interfaces
GetPrefixInfoFromRApref64fromraPref64FromRADiscovers the NAT64 prefix from the PREF64 option in router advertisements
GetPrefixInfoFromDNSpref64fromdnsPref64FromDnsDiscovers the NAT64 prefix by querying ipv4only.arpa against a DNS64 server

Interpreting WinCLAT Policy Values

Each policy value is a REG_DWORD. A value of 1 enables the setting, and a value of 0 disables it. Deleting the value returns control to the local setting. Windows allows NAT64 prefix discovery through both router advertisements and DNS by default, so the scripts in this post manage only PermitNonCellularCLAT.

Deploying the WinCLAT Remediation

Detect-WinClatPermitPolicy.ps1 compares PermitNonCellularCLAT with the desired registry state. It returns exit code 0 when the state matches and 1 when a change is needed. When detection returns 1, Intune runs Remediate-WinClatPermitPolicy.ps1 to write or remove the policy value.

Setting the Desired Policy State

Both scripts begin with a $DesiredState variable that corresponds to the three states of the Group Policy setting. Remediations do not accept parameters, so set the variable to the same value in both scripts before uploading them and create a separate Remediation for each state that is needed, such as Enable WinCLAT and Remove WinCLAT Policy.

# Enabled, Disabled, or NotConfigured. Must match the remediation script.
$DesiredState = 'Enabled'
Desired stateRegistry valueResult
Enabled1WinCLAT is permitted, and the setting is under policy control
Disabled0WinCLAT is not permitted, and the setting is under policy control
NotConfiguredDeleted, along with the IPxlatCfgSvc key if it is then emptyThe setting returns to the local configuration

Creating and Assigning the Package

Perform the following steps to create the Remediation in the Microsoft Intune admin center.

  1. Go to Devices > Manage devices > Scripts and remediations, then select Create script package.
  2. Enter a name, such as Enable WinCLAT, and upload the detection and remediation scripts with $DesiredState set to Enabled.
  3. Configure the following settings:
    1. Run this script using the logged-on credentials: No. The scripts write to HKLM and must run as SYSTEM.
    2. Enforce script signature check: No, unless the scripts are signed.
    3. Run script in 64-bit PowerShell: Yes.
  4. Assign the Remediation to a group of devices and choose a schedule. An hourly or daily schedule keeps the value in place if it is removed.
Intune Remediation script package settings

Intune Remediation script configuration settings.

Testing the Remediation on a Single Device

To test the package, open the device’s Overview page in the Intune admin center, select Run remediation, and choose the WinCLAT script package. You can run the package on demand without assigning it to the device. The device must be online, have the Intune Management Extension installed, and be able to communicate with Intune and the Windows Push Notification Service (WNS).

Run remediation action on an Intune device page

Run Remediation interactively on a specific endpoint.

Reviewing Remediation Results in Intune

On the device page in the Intune admin center, select Remediations to review the script package results. In the example below, With issues indicates that the registry state differed from the desired state, and Issue fixed indicates that the script corrected it. Verify the effective permit setting and translation state separately on the client.

Intune device Remediations results showing With issues and Issue fixed

Remediation results.

WinCLAT Activation After Remediation

Applying the permit policy allows Windows to start WinCLAT automatically on eligible interfaces. What happens next depends on whether the interface already has a native IPv4 address and whether Windows can discover a NAT64 prefix.

IPv6-Only Networks

On an IPv6-only test network, WinCLAT begins translating about a minute after the script writes the permit value, without a reboot, Group Policy refresh, or service restart. The instance uses an address from the IPv4 Service Continuity Prefix (RFC 7335), typically 192.0.0.1. Automatic activation requires an eligible interface with a Stateless Address Autoconfiguration (SLAAC) address, a discoverable NAT64 prefix, and autoenable enabled. The policy value persists across reboots.

IPv6-Mostly Networks

On an IPv6-mostly network, Windows already has a DHCPv4 lease when the remediation runs. Neither applying the permit policy nor running ipconfig /renew releases the existing lease. After the adapter restarts, Windows honors DHCPv4 option 108 (IPv6-Only Preferred), comes up without a native IPv4 address, and starts translating within seconds. For a production rollout, let devices reconnect normally or restart the target adapter during a maintenance window. Restarting it interrupts connectivity.

WinCLAT Activation Events

Use the Microsoft-Windows-IPxlatCfg/Operational log to verify that WinCLAT started. Event 1106 (Instance enabled) records why Windows enabled the instance, and Get-WinClatInstance reports that reason in TriggerSource when the event is available. When a new instance starts translating, event 1106 is typically followed by event 1108 (Remote prefix discovered) and event 1109 (Translation started). For more on event 1106 and how to identify the associated network adapter, see Understanding Windows CLAT (WinCLAT) Event Logging.

Event 1109 in the IPxlatCfg Operational log showing that WinCLAT translation started

Event 1109 shows that WinCLAT began translating.

Verifying Policy and Translation

Verify the effective permit setting first, then check whether WinCLAT is translating on the target interface. Use netsh.exe or the WinCLAT PowerShell module for both checks.

Verifying the Effective Permit Setting

Run netsh.exe interface clat show global store=both or Get-WinClatConfiguration -Store Both to compare the active and persistent stores. The active store shows the effective configuration, and the persistent store shows the saved local configuration. In this example, policy enables permit in the active store while the local setting remains disabled. Use the module’s PolicyControlled property to confirm that policy controls Permit, even when both stores report the same value.

Output of netsh interface clat show global store=both

Output of netsh.exe interface clat show global store=both.

Get-WinClatConfiguration -Store Both | Format-List
Output of Get-WinClatConfiguration -Store Both

Output of Get-WinClatConfiguration -Store Both.

Verifying Translation on an Interface

From an elevated command window, run netsh.exe interface clat show instance interface=<index> using the interface index from Get-NetAdapter, and look for Is translating : yes. Alternatively, run Get-WinClatInstance and look for IsTranslating : True on the target interface. The module lists active adapters with IPv6 enabled, so you can run it without supplying an interface index. To verify end-to-end connectivity, test an IPv4-only application or connect to a literal IPv4 address from the target network.

Output of netsh interface clat show instance

Output of netsh.exe interface clat show instance.

Output of Get-WinClatInstance

Output of Get-WinClatInstance.

Removing the WinCLAT Policy

Unassigning the enablement package leaves the policy value in the registry. To restore local control, create a removal package using the same scripts with $DesiredState set to NotConfigured. Use Disabled when you want policy to enforce a disabled permit setting.

Maintaining Intune Connectivity During Removal

Before removing the policy, confirm that the device will still be able to reach Intune if automatic WinCLAT translation stops. A device that relies on WinCLAT to reach IPv4-only Intune endpoints can lose its ability to report the result or receive a recovery package. Use a network with a working path to Intune through native IPv4 or DNS64 and NAT64. On an IPv6-mostly network, check whether the device has a native IPv4 address after removal. Reconnect the adapter if it needs to obtain a new DHCPv4 lease.

Replacing the Enablement Assignment

Before assigning the Remove WinCLAT Policy package, remove the target devices from the enablement assignment. Use a pilot device to confirm that it has received the assignment change and that the enablement package no longer runs on it. After the target devices report successful removal, you can assign the removal package more broadly.

Verifying Policy Removal

Run Get-WinClatConfiguration and confirm that PolicyControlled no longer lists Permit. The effective Permit value should now match the local setting, which is disabled by default. If removal stops an automatically enabled instance, Get-WinClatInstance should report IsTranslating : False for that interface. The operational log may also show event 1110 (Translation stopped) and event 1107 (Instance disabled).

Event 1107 showing that Windows disabled the WinCLAT instance

Event 1107 shows that Windows disabled the WinCLAT instance on the interface.

Get-WinClatConfiguration output showing Permit False and an empty PolicyControlled field

Get-WinClatConfiguration shows Permit=False and an empty PolicyControlled field.

Get-WinClatInstance output showing IsTranslating False

Get-WinClatInstance shows IsTranslating=False.

Limits of Registry-Based Management

The script packages manage the WinCLAT permit policy. Automatic activation, manually enabled instances, and local changes to policy-controlled settings require separate checks.

Automatic Activation

The autoenable setting is enabled by default and has no corresponding WinCLAT Group Policy setting. If an administrator has disabled it, setting PermitNonCellularCLAT to 1 permits WinCLAT but leaves automatic activation disabled. To restore automatic activation, use netsh.exe interface clat set global autoenable=enabled or Set-WinClatConfiguration -AutoEnable Enabled.

Manually Enabled Instances

Disabling Permit stops automatically enabled instances. A manually enabled instance can continue translating until you disable it explicitly or the device reboots. Check the instance state on the target interface if your objective is to stop translation.

Local Changes to Policy-Controlled Settings

When policy controls a WinCLAT setting, netsh.exe interface clat set global can report success and update the local value in the persistent store while the active value continues to follow policy. Use netsh.exe interface clat show global store=active to verify the effective value. If you use Set-WinClatConfiguration to request a value that differs from the effective policy value, the cmdlet reports PolicyOverride.

Using netsh.exe in a Remediation

A Remediation can also run netsh.exe to configure WinCLAT, and this is the only way to enforce autoenable. However, netsh.exe changes the local configuration rather than policy, and reliable detection requires parsing localized command output, so this approach is outside the scope of this post.

Summary

Intune Remediations can deploy and remove the WinCLAT permit policy on Windows 11. Make sure devices can reach Intune before deployment, then verify the effective policy and translation state on the target interface. On IPv6-mostly networks, devices with an existing DHCPv4 lease may need to reconnect before Windows uses WinCLAT. Before removing the policy, confirm that devices will still have a working path to Intune.

Additional Information

WinCLAT resources on directaccess.richardhicks.com

Always On VPN DPC 5.2.0 Now Available

I’m pleased to announce that Always On VPN Dynamic Profile Configurator (DPC) version 5.2.0 is now available. My good friend Leo D’Arcy has been hard at work for the last few months squashing some bugs and adding a few new features to DPC. If you are running a previous release of Always On VPN DPC, either open source or commercial, it’s time to upgrade.

Important!! DPC 5.2.0 has a bug that prevents the service from stopping. This has been addressed in DPC 5.2.1. Guidance for upgrading from DPC 5.2.0 to 5.2.1 can be found here.

Reminder: We’re on Discord. Join the conversation today!

What’s New in DPC 5.2.0

Always On VPN DPC 5.2.0 has some compelling new features.

  • Exclude Routes from DNS – DPC has a feature that allows administrators to add routes to the routing table using DNS. When this setting is enabled, DPC will attempt to resolve the specified hostname to an IP address and add it to the VPN’s routing table when creating the profile. With 5.2.0, this capability has been extended to exclusion routes, allowing administrators to exclude resources by host name.
  • Write Event Logs to Disk – This setting allows administrators to optionally write DPC event information to a text file in addition to logging them in the event log. Writing event log information to a text file on disk can make troubleshooting easier in some scenarios.
  • Delay Profile Updates – This new feature ensures reliable VPN profile creation after group policy updates take place.

Bug Fixes

In addition to new capabilities, Always On VPN DPC 5.2.0 includes fixes for many outstanding issues.

  • DPC name resolution issue where duplicate IP addresses are returned, resulting in failed route additions when using ‘Allow Routes from DNS’.
  • Missing events in the DPC operational event log.
  • Enabling ‘Disable Disconnect Button’ or ‘Disable Advanced Edit Button’ settings results in a profile mismatch warning.
  • Added resiliency to DPC name resolution when one or more name resolution requests fail.

Group Policy Template

As a reminder, any time there are new features in DPC, there will be corresponding changes to Group Policy administrative template and template language files. Be sure to update your ADMX and ADML files in the group policy central store to take advantage of these new capabilities in DPC 5.2.0.

Recommendation

If you are running any release of Always On VPN DPC, commercial or open source, consider upgrading now to gain access to new features and operational reliability improvements. You can find DPC v5.2.0 on GitHub here.

Additional Information

Always On VPN DPC v5.2.0 Available Now

Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN DPC Now Open Source

Migrating from Always On VPN DPC Commercial to Open Source

Always On VPN DPC with Microsoft Intune

Microsoft Always On VPN on Discord

Always On VPN DPC

Managed Certificates for Remote Desktop Protocol

The Remote Desktop Protocol (RDP) is arguably the most widely used protocol for Windows remote server administration. RDP uses Transport Layer Security (TLS) for server authentication, data encryption, and integrity. However, the default configuration of TLS for RDP in Windows is less than ideal.

RDP Self-Signed Certificate

By default, RDP uses a self-signed certificate for TLS operations. TLS with self-signed certificates is a bad security practice because they are not validated by a trusted certificate authority (CA), making it impossible for clients to verify the authenticity of the server they are connecting to, which can lead to interception attacks.

Certificate Warning

Most administrators have encountered a warning error when connecting to a remote host via RDP using a self-signed RDP certificate.

“The remote computer could not be authenticated due to problems with its security certificate. It may be unsafe to proceed.”

Nmap

You can view the default self-signed certificate with the Nmap utility by running the following command.

nmap.exe -n -p 3389 <hostname> –script ssl-cert

Managed Certificates

A better solution for RDP TLS is to use managed certificates issued by an enterprise Public Key Infrastructure (PKI) such as Microsoft Active Directory Certificate Services (AD CS). AD CS is widely deployed in AD domain environments and can be configured to issue certificates for RDP TLS.

AD CS

To configure AD CS to issue RDP certificates, perform the following steps.

Certificate Template

On an issuing CA or an administrative workstation with the Remote Server Administration Tools (RSAT) installed, open the Certificate Templates management console (certtmpl.msc) and perform the following steps.

*My apologies for the list numbering format issues below. Microsoft Word and WordPress can’t seem to agree on the list format. Hopefully, you can figure it out, though. 🙂

  1. Right-click the Workstation Authentication template and choose Duplicate Template.
  2. Select the Compatibility tab.
    1. Select the operating system (OS) version corresponding to the oldest OS hosting the issuing CA role in your environment from the Certification Authority drop-down list.
    1. Select the OS version corresponding to your environment’s oldest supported server or client OS from the Certificate recipient drop-down list.
  3. Select the General tab.
    1. Enter a descriptive name in the Template display name field.
    1. Select an appropriate validity period for your environment. The best practice is to limit the validity period to one year or less.
  4. Select the Cryptography tab.
    1. From the Provider Category drop-down list, choose Key Storage Provider.
    1. From the Algorithm name drop-down list, choose RSA.
    1. In the Minimum key size field, enter 2048.
    1. From the Request hash drop-down list, choose SHA256.
  5. Select the Subject Name tab.
    1. From the Subject name format drop-down list, select DNS name.
    1. Ensure that DNS name is also checked in the subject alternate name section.
  6. Select the Extensions tab.
    1. Click on Application Policies.
    1. Click Edit.
    1. Select Client Authentication.
    1. Click Remove.
    1. Click Add.
    1. Click New.
    1. Enter Remote Desktop Authentication in the Name field.
    1. Enter 1.3.6.1.4.1.311.54.1.2 in the Object identifier field.
    1. Click Ok.
    1. Select Remote Desktop Authentication.
    1. Click Ok.
  7. Select the Security tab.
    1. Click Domain Computers.
    1. Grant the Read and Enroll permissions.
  8. Click Ok.

Next, open the Certification Authority management console (certsrv.msc) and follow the steps below to publish the certificate.

  1. Expand the CA.
  2. Right-click Certificate Templates and choose New > Certificate Template to Issue.
  3. Select the Remote Desktop Authentication certificate template.
  4. Click Ok.

Group Policy

Next, on a domain controller or a workstation with the RSAT tools installed, open the Group Policy Management console (gmpc.msc) and perform the following steps to create a new GPO to enroll domain computers for the Remote Desktop Authentication certificate

  1. Right-click Group Policy Objects and choose New.
  2. Enter a descriptive name for the GPO in the Name field.
  3. Click Ok.
  4. Right-click the GPO and choose Edit.
  5. Navigate to Computer Configuration > Policies > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Security.
  6. Double-click Server authentication certificate template.
  7. Select Enabled.
  8. Enter the name of the Remote Desktop Authentication certificate template in the Certificate Template Name field. Note: Be sure to enter the template name, not the template display name!
  9. Click Ok.

Once complete, link the GPO to the domain or OU to target the servers and workstations to which you wish to deploy the RDP certificate.

Validate Certificate

After updating group policy on a target resource, you’ll find that Nmap now shows the enterprise PKI-issued certificate used for RDP connections.

Additional Information

Understanding the Remote Desktop Protocol (RDP)

Migrating from Always On VPN DPC Commercial to Open Source

Always On VPN Dynamic Profile Configurator (DPC) is a software solution that enables administrators to deploy and manage Always On VPN client configuration settings using Active Directory and Group Policy or Microsoft Intune. DPC began life as a commercial product. Recently, DPC has been released to the public via open source. DPC open source allows administrators everywhere to deploy the solution without cost. If you’re not using DPC today, I’d strongly recommend it. If you were previously a DPC commercial customer, you’ll want to migrate to DPC open source soon.

We’re on Discord! Join the conversation: https://discord.aovpndpc.com/.

Migration

Migrating from DPC commercial to open source requires the administrator to deploy a Group Policy Object (GPO) and client software in a specific order to avoid disruption to end users. Perform the following steps to complete the migration.

GPO Files

Download the DPC v5.0 (open source) group policy settings file (ADMX) file here and the language definition (ADML) file here.

After downloading the files, copy dpc.admx to the following location.

\\<DC name>\sysvol\<domain name>\Policies\PolicyDefinitions

Next, copy dpc.adml to the following location.

\\<DC name>\sysvol\<domain name>\Policies\PolicyDefinitions\en-US

Once complete, allow domain controller replication to finish before deploying DPC group policy settings.

New GPO

Create a new GPO that will contain the VPN client configuration settings. Do NOT copy the original DPC commercial GPO. Starting with a blank GPO is best to ensure proper operation and prevent conflicts. Also, please note the location for DPC settings has changed. The new location for DPC v5.0 settings is:

Computer Configuration > Policies > Administrative Templates > DPC Client

You can now link the GPO to the applicable OU(s) or complete this task before deploying the new software.

Migration Tool

The easiest way to migrate from DPC commercial to open source is to migrate the settings from the current GPO to a new one. A PowerShell script is available to simplify this task. You can download the Migrate-DpcConfig.ps1 PowerShell script here.

Note: It is not strictly required to migrate your current settings from DPC commercial. Although this migration script makes importing settings easier, nothing prevents you from creating a new GPO for DPC open source and starting from scratch if you wish.

Prerequisites

The PowerShell migration script requires the installation of the Remote Server Administration Tools (RSAT). Specifically, the Group Policy Management tools are needed. Although it’s possible to run this script on a domain controller, it is not recommended. The best practice is to install the RSAT tools on an administrative workstation or server.

You can install the necessary RSAT feature on Windows 11 by opening an elevated PowerShell or command window and running the following command.

dism.exe /Online /add-capability /CapabilityName:Rsat.GroupPolicy.Management.Tools~~~~0.0.1.0

On Windows Server, you can install the Group Policy Management tools by opening an elevated PowerShell command window and running the following command.

Install-WindowsFeature -Name GPMC

Once complete, restart the server to complete the installation process.

Import Settings

To migrate the DPC settings, open an elevated PowerShell command window and run the following command.

.\Migrate-DpcSetting.ps1 -PreviousGPOName <name of old DPC GPO> -NewGPOName <name of new DPC GPO>

For example,

.\Migrate-DpcSetting.ps1 -PreviousGPOName ‘Always On VPN DPC’ -NewGPOName ‘Always On VPN DPC – Open Source’

Apply GPO

If not done earlier, link the new DPC open-source GPO to the applicable OU(s). Do NOT unlink or delete the old GPO until all endpoints have been upgraded to the DPC v5.0 client.

Install Software

Once the new GPO has been configured and applied in Active Directory, the next step is to upgrade the DPC commercial client to the DPC open source client (v5.0). Software can be deployed via GPO using Active Directory software installation, SCCM, or any other method you use in your environment to deploy software. No switches or additional parameters are required to perform the upgrade. Simply run the .MSI file on the device, and the upgrade will occur automatically.

Important Note: Administrators must ensure that the new GPO settings are applied to the endpoint before installing the DPC v5.0 client.

Clean Up

After all endpoints have been upgraded to DPC v5.0, administrators can remove the DPC commercial GPO from AD. In addition, the commercial DPC ADMX and ADML files can be removed from domain controllers if desired.

Need Help?

If you’d like assistance migrating DPC commercial to open source, please don’t hesitate to reach out! I’m available to answer questions or provide remote assistance if necessary. You can reach me on the DPC-Chat channel on Discord here. Alternatively, you can fill out the form below, and I’ll provide more information.

← Back

Thank you for your response. ✨

Additional Information

PowerON Platforms Are No More

Always On VPN DPC Open Source

Always On VPN DPC Advanced Features

Always On VPN DPC with Microsoft Intune

What’s New in Always On VPN DPC 4.3.1

The latest release of PowerON Platforms’ Always On VPN Dynamic Profile Configurator (DPC), version 4.3.1, is now available for download. This recent update includes fixes for previously known issues. In addition, it contains some critical new features administrators will find helpful in addressing the challenges they face with Always On VPN client configuration.

What Is DPC?

Always On VPN DPC is a solution to manage Always On VPN client configuration settings. It was originally designed to be used with on-premises Active Directory but can also be deployed with Microsoft Intune. DPC streamlines the configuration and management of client settings and includes many advanced features to fine-tune and optimize Always On VPN.

What’s New in 4.3.1

The following essential features are new in the 4.3.1 release of DPC.

Add Device Tunnel Routes to User Tunnel

Always On VPN administrators can now configure DPC to add device tunnel routes to the user tunnel automatically. This configuration option ensures that all traffic flows of the user tunnel when both user and device tunnels are established.

Note: This feature also requires administrators to define route metric options in DPC. Ensure the user tunnel route metrics are set to a lower value than the device tunnel metrics for proper operation.

Restart RasMan

Always On VPN connections occasionally fail with error 602 (ERROR_PORT_ALREADY_OPEN). The workaround for this is to restart the RasMan service on the endpoint. DPC now supports automatically restarting the RasMan service when this error occurs, ensuring reliable operation for Always On VPN connections.

Machine Certificate Filtering

DPC 4.3.1 now includes a feature to allow administrators to enable machine certificate filtering for Always On VPN device tunnels. This addresses a challenge when the endpoint has multiple machine certificates in its local computer certificate store when the VPN server is configured to accept a certificate with a specific custom application policy (EKU).

Additional Features

In addition, the updated DPC agent core service now run as x64 processes. Also, DPC now supports VPN server FQDNs longer than 63 characters (good news for those using DPC with Azure VPN gateway!).

Download DPC

For those customers currently licensed for Always On VPN DPC you can download the latest release here.

https://support.poweronplatforms.com/support/solutions/articles/8000066807

Not using DPC?

If you’re not using DPC, you are missing out! You can learn more about DPC and register for a free evaluation by visiting the link below.

https://aovpndpc.com

Optionally, you can fill out the form below and I’ll provide you with more information.

Additional Information

PowerON Platforms’ Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN DPC Advanced Features

Always On VPN DPC with Microsoft Intune

Always On VPN and Interface Metrics

Always On VPN DNS Registration Update Available

In Windows, each network interface identified by the operating system is assigned a metric value. Interface metrics are settings that determine the priority or preference of network interfaces when there are multiple active network connections. The Windows networking stack uses these metrics to determine which network interface should be used for routing traffic when multiple network interfaces are available. Network interface metrics are critical for Always On VPN administrators to understand because they can impact how name resolution requests are processed when an Always On VPN connection is established.

Metric Values

By default, Windows automatically assigns metric values to network interfaces (including VPN interfaces) based on various factors, including the connection speed, link state, and interface type. It tries to select the most suitable interface for general internet connectivity.

Metrics and DNS

Windows will also use the network interface with the lowest metric value as the preferred interface for sending DNS queries by default. This means that DNS queries will be routed through the network interface with the lowest metric value, assuming it is available and connected. When an Always On VPN connection is established, DNS queries may fail or return unexpected results if the network interface metrics are not configured optimally.

Split DNS and Wired Ethernet

Split DNS (sometimes called ‘split brain DNS’) is when the DNS namespace is the same internally and externally. The most common scenario where interface metric settings interfere with DNS operation is when using split DNS and the endpoint is connected to the Internet with a wired Ethernet connection. In this scenario, the Ethernet interface will be assigned the same or lower interface metric value as the Always On VPN interface, which can yield unexpected results.

Viewing Metrics

Always On VPN administrators can view currently assigned interface metric values by running the following PowerShell command.

Get-NetIpInterface

Get-NetIpInterface output showing interface metrics

Assigning Metrics

Most Always On VPN administrators will never have to change interface metric settings. However, if your implementation uses split DNS and some of your endpoints connect using wired Ethernet connections, you may need to update the interface metric settings to ensure proper DNS operation. Choose a setting for the interface metric value that is lower than the wired Ethernet interface. I’ve used a value of ‘3’ without issue for many years. Use one of the following methods to update the interface metric for Always On VPN connections.

PowerShell

Updating interface metric settings in Windows can be accomplished by running the Set-NetIpInterface PowerShell command.

Set-NetIpInterface -InterfaceAlias <connection name> -InterfaceMetric 3

Set-NetIpInterface assigning interface metric 3 to the VPN connection

Note: Using PowerShell to assign the interface metric is not persistent! While this method is suitable for local validation testing, you should use one of the following methods to implement this change permanently.

Rasphone.pbk

To assign the interface metric permanently, Always On VPN administrators can edit the following settings in the rasphone.pbk configuration file.

IpInterfaceMetric=3

Ipv6InterfaceMetric=3

Administrators can automate updating this setting using the Update-Rasphone.ps1 PowerShell script. In addition, the following scripts can be used with Microsoft Intune remediation.

Detect-DeviceIpv4InterfaceMetric.ps1

Remediate-DeviceIpv4InterfaceMetric.ps1

Detect-DeviceIpv6InterfaceMetric.ps1

Remediate-DeviceIpv6InterfaceMetric.ps1

Detect-Ipv4InterfaceMetric.ps1

Remediate-Ipv4InterfaceMetric.ps1

Detect-Ipv6InterfaceMetric.ps1

Remediate-Ipv6InterfaceMetric.ps1

DPC

Organizations using Always On VPN Dynamic Profile Configurator (DPC) to manage Always On VPN client configuration settings with Active Directory and group policy or Microsoft Intune can enable the VPN Tunnel Metric setting.

Always On VPN DPC VPN tunnel metric setting

Additional Information

Always On VPN: Secure Remote Access for Windows

Get-NetIpInterface PowerShell Command

Set-NetIpInterface PowerShell Command

Managing Always On VPN Client Settings with DPC

Always On VPN DPC with Microsoft Intune

Always On VPN DPC Advanced Features

Always On VPN DPC Video Demonstration

Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN Trusted Network Detection and Native Azure AD Join

Administrators deploying Microsoft Always On VPN are quickly learning that the native Azure Active Directory join (AADJ) model has significant advantages over the more traditional Hybrid Azure AD join (HAADJ) scenario. Native AADJ is much simpler to deploy and manage than HAADJ while still allowing full single sign-on (SSO) to on-premises resources for remote users. Intune even allows for the import of custom ADMX and ADML administrative templates, further reducing the dependency on on-premises Active Directory for device management.

Remote Management

Although devices aren’t joined to the domain, administrators may still wish to access those clients connected to their network for device discovery or to perform administrative tasks. However, when native AADJ clients connect via Always On VPN, the Public Windows firewall profile is assigned to the VPN tunnel adapter. The Public profile is, of course, more restrictive and blocks most management protocols by default.

Firewall Rules

While adding firewall rules to the Public profile to allow management protocols is possible, this isn’t recommended for security reasons. The Public profile is typically loaded when the device is on an untrusted network. Exposing management protocols on an insecure network is asking for trouble.

Domain Profile

Domain-joined or Hybrid AADJ endpoints will use the Domain Windows firewall profile. This profile is more permissive, allowing many standard management protocols by default. Also, administrators can add rules to allow additional access as required without increasing the risk for devices on untrusted networks.

Trusted Network Detection

So, the trick is to get a native AADJ endpoint to load the Domain profile for the VPN tunnel adapter when connected via Always On VPN. Trusted Network Detection is accomplished by using settings configured on the endpoint using the NetworkListManager Configuration Service Provider (CSP).

Intune and XML

There are two settings administrators can enable AADJ devices to detect a trusted network and load the Domain Windows firewall profile. Unfortunately, these settings can only be applied using Intune and the Custom XML template. Administrators will use the following OMA-URI settings.

AllowedTlsAuthenticationEndpoints

The AllowedTlsAuthenticationEndpoints policy setting defines the URL the device uses to validate a trusted network. The target must be an on-premises web server with a valid TLS certificate using HTTPS. The target must be a highly available internal resource inaccessible from the Internet. DirectAccess administrators will be quite familiar with this concept; it’s the Network Location Server (NLS)!

Use the following OMA-URI to configure the TLS authentication endpoint.

URI: ./Device/Vendor/MSFT/Policy/Config/
NetworkListManager/AllowedTlsAuthenticationEndpoints

String: <![CDATA[https://nls.corp.example.net]]>

ConfiguredTlsAuthenticationNetworkName

The ConfiguredTlsAuthenticationNetworkName policy setting is optional. Administrators can use this setting to provide a friendly name for the authenticated trusted network. The FQDN of the target resource (NLS) is used by default. However, using this setting overrides the default with something more meaningful.

Use the following OMA-URI to configure the TLS authentication network name.

URI: ./Device/Vendor/MSFT/Policy/Config/
NetworkListManager/ConfiguredTlsAuthenticationNetworkName

String: <Friendly network name>

Results

Once configured, you’ll find the Always On VPN tunnel adapter uses the Domain Windows firewall profile and an optional friendly network name.

Additional Information

Deploying Always On VPN with Intune using Custom XML and CSP

Always On VPN CSP Updates

Always On VPN and VpnStrategy with CSP

Always On VPN DPC with Intune

In the past, I’ve written about Always On VPN Dynamic Profile Configurator (DPC), a software solution administrators can use to provision and manage Always On VPN client configuration settings using Active Directory and group policy. In addition to streamlining the deployment and management of Always On VPN client settings, DPC has many advanced features and capabilities to ensure optimal security, performance, and connection reliability.

Optimizations

Many settings required to fine-tune and optimize Always On VPN connections are not exposed in the Intune UI or XML. They must be configured by manipulating configuration files, setting registry keys, and running PowerShell commands. Much of this can be automated using Intune Proactive Remediation, but it is far from ideal. Administrators must configure Always On VPN using one method, then deploy optimizations using another. In addition, Proactive Remediation suffers from timing issues where some settings are not applied immediately, resulting in degraded or inoperable VPN connections until changes take effect.

Always On VPN DPC

Always On VPN DPC allows administrators to configure many advanced settings quickly and conveniently using the familiar Group Policy Management console (gpmc.msc). DPC dramatically reduces the administrative burden associated with Always On VPN client management. In addition, DPC enables many of these options by default, ensuring optimal security and reliable operation. Also, DPC immediately implements all configuration settings, eliminating the need to reboot to apply configuration changes.

Intune and ADMX

Historically, Always On VPN DPC could only be used when managing endpoints exclusively with Active Directory group policy. However, DPC can now be used with Microsoft Endpoint Manager/Intune thanks to a new feature that allows administrators to import custom ADMX and ADML administrative templates to Microsoft Endpoint Manager (MEM).

Note: This feature is in public preview at the time of this writing.

DPC and Intune

The combination of DPC and Intune brings with it many advantages. Using DPC with Microsoft Endpoint Manager/Intune offers administrators simplified deployment and many advanced features provided by Always On VPN DPC. In addition, customers who have deployed DPC on-premises can now migrate seamlessly to Microsoft Endpoint Manager/Intune management without giving up DPC’s valuable features.

Learn More

Enter your contact details in the form below for more information regarding Always On VPN DPC. Also, visit https://aovpndpc.com/ to register for a free Always On VPN DPC trial.

Additional Information

Always On VPN with Active Directory Group Policy

Introduction to Always On VPN DPC

Always On VPN DPC Advanced Features

Always On VPN DPC Video Demonstrations

What’s New in Always On VPN DPC v3.0

Always On VPN DPC Free Trial

Always On VPN NPS Auditing and Logging

The Network Policy Server (NPS) event log is incredibly valuable for administrators when troubleshooting Always On VPN user tunnel connectivity issues. Administrators can find these pertinent events by opening the Event Viewer on the NPS server (eventvwr.msc) and navigating to Custom Views > Server Roles > Network Policy and Access Services.

Event Logs

When configured correctly, event logs will record the disposition of all authentication requests, allowed or denied. The two most common recorded events are event IDs 6272 (access granted) and 6273 (access denied).

NPS Event ID 6272 – Access granted.

NPS Event ID 6273 – Access denied.

Auditing

In some cases, administrators may find none of these events recorded even though user authentication is working correctly. Here, the only events recorded are NPS informational events indicating which domain controller the NPS server is using to perform authentication.

The lack of 6272 and 6273 events in the event log indicates that auditing for NPS events is not enabled. Open an elevated PowerShell window and run the following command to view the current auditing setting for NPS events.

auditpol.exe /get /subcategory:”Network Policy Server”

Open an elevated PowerShell window and run the following command to enable auditing for NPS events.

auditpol.exe /set /subcategory:”Network Policy Server” /success:enable /failure:enable

Group Policy

Alternatively, consider using Active Directory group policy to enforce the NPS server auditing settings. Open the Group Policy Management Console (GPMC) and create a new GPO. Next, navigate to Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Audit Policies > Logon/Logoff > Audit Network Policy Server and select the option to audit both success and failure attempts.

Once complete, link this GPO to the OU where the NPS servers reside.

Missing Events

If auditing is enabled and there are no recorded 6272 or 6273 events, the NPS server did not receive any authentication requests from the VPN server. Review the event logs on any other NPS servers if there is more than one configured. In addition, this may indicate that network communication between the VPN and NPS server is blocked. Ensure network connectivity and name resolution are working as expected.

Troubleshooting Guides

Are you interested in learning more about Always On VPN troubleshooting? My Always On VPN book contains an entire chapter dedicated to troubleshooting. Also, my Always On VPN video training course on Pluralsight includes a module on troubleshooting. The video training course is available to Pluralsight subscribers only. If you don’t have a Pluralsight subscription, you can sign up for a free trial here.

Additional Information

Troubleshooting Always On VPN Errors 691 and 812

Troubleshooting Always On VPN Errors 691 and 812 – Part 2

Troubleshooting Always On VPN Errors 691 and 812 – Part 3

Always On VPN NPS Load Balancing