Windows CLAT (WinCLAT) Overview and Configuration

Microsoft has announced the general availability of Windows CLAT (WinCLAT), extending IPv4 application compatibility to IPv6-only and IPv6-mostly networks on Windows 11. WinCLAT works with a network NAT64 gateway to allow IPv4-dependent applications to communicate without native IPv4 connectivity on the client’s network interface. This article provides an overview of WinCLAT, explains its network requirements, and demonstrates how to enable and configure it using netsh.exe and Active Directory Group Policy.

What Is CLAT?

CLAT (customer-side translator) is part of the 464XLAT IPv6 transition and translation technology. CLAT uses the Stateless IP/ICMP Translation Algorithm (SIIT) to translate IPv4 packets generated by the client into IPv6. A corresponding provider-side translator (PLAT), typically a NAT64 gateway, translates the packets back to IPv4 before forwarding them to their destination.

Background

CLAT has been part of Windows for quite some time. It first shipped with Windows Phone and was later ported to Windows 10 with the Creators Update (v1703) in April 2017. Until now, the implementation was limited to wireless wide area network (WWAN) cellular interfaces.

Why Do We Need CLAT?

Although modern applications increasingly support IPv6, many applications and services still depend on IPv4. Some applications use IPv4-only sockets or application programming interfaces (APIs), while others connect directly to literal IPv4 addresses. Because these applications cannot use DNS64-generated AAAA records, they require another mechanism to communicate across an IPv6-only network. WinCLAT provides this compatibility while allowing the network to operate without native IPv4 connectivity.

How WinCLAT Works

When enabled, WinCLAT determines whether the client is operating without native IPv4 connectivity. This can occur on an IPv6-only network or an IPv6-mostly network where Dynamic Host Configuration Protocol for IPv4 (DHCPv4) Option 108 instructs capable clients to forgo an IPv4 address. WinCLAT then learns the network’s NAT64 prefix from a router advertisement (RA) or via DNS and the ipv4only.arpa domain. Next, WinCLAT creates a synthetic IPv4 address on the network interface. When an application generates IPv4 traffic, WinCLAT statelessly translates the IPv4 packets to IPv6 using the discovered NAT64 prefix and forwards them to the network. Return traffic is translated back to IPv4. This process is transparent to most applications, which can continue using IPv4 sockets without native IPv4 connectivity on the network.

SLAAC Requirement

WinCLAT currently requires the client to obtain its IPv6 address using Stateless Address Autoconfiguration (SLAAC). It does not work on networks that assign client IPv6 addresses exclusively through stateful DHCPv6. Organizations using DHCPv6 for IPv6 address assignment must also enable SLAAC before deploying WinCLAT.

The Role of DNS64 and NAT64

DNS64 and NAT64 work alongside WinCLAT to provide access to IPv4-only resources from an IPv6-only network. Their role depends on whether an application communicates using IPv6 or still requires IPv4.

IPv4 Connectivity for IPv6 Applications

DNS64 synthesizes AAAA records from IPv4 A records, allowing IPv6-capable applications to communicate with IPv4-only destinations through the NAT64 gateway. Applications that use IPv4 sockets or connect to literal IPv4 addresses cannot use these synthesized records and instead rely on WinCLAT for compatibility.

NAT64 Prefix Discovery

DNS also provides one method for WinCLAT to discover the network’s NAT64 prefix. WinCLAT can obtain the prefix by querying ipv4only.arpa, although the preferred method is the PREF64 option in an IPv6 router advertisement.

Note: DNS64 and NAT64 are likely familiar to Microsoft DirectAccess administrators, as these technologies were introduced with DirectAccess in Windows Server 2012.

Configure WinCLAT

After the WinCLAT feature becomes available on your device, you can enable and configure it using netsh.exe.

Enable WinCLAT

To permit WinCLAT operation on non-cellular interfaces, open an elevated command window and run the following command.

netsh.exe interface clat set global permit=enabled

View WinCLAT Settings

You can view the current global configuration by running the following command.

netsh.exe interface clat show global
netsh interface clat show global output displaying WinCLAT global settings

You can also view interface-specific settings using the following command.

netsh.exe interface clat show instance interface=<interface name>
netsh interface clat show instance output displaying WinCLAT settings for a network interface

Prefix Discovery

Optionally, you can enable or disable NAT64 prefix discovery options (from DNS and/or from RA) using the following commands.

# enable pref64 discovery methods
netsh.exe interface clat set global pref64fromdns=enabled
netsh.exe interface clat set global pref64fromra=enabled

# disable pref64 discovery methods
netsh.exe interface clat set global pref64fromdns=disabled
netsh.exe interface clat set global pref64fromra=disabled

Note: At least one prefix-discovery method must remain enabled. When both are enabled, WinCLAT prefers the PREF64 option in an IPv6 router advertisement and uses DNS-based discovery as a fallback.

WinCLAT IPv4 Address

WinCLAT assigns 192.0.0.1/32 to the interface for use by the local IPv4 stack. This address comes from the IANA-reserved 192.0.0.0/29 IPv4 Service Continuity Prefix defined in RFC 7335. Addresses from this prefix support local IPv4 compatibility and are not transmitted as IPv4 packets on the physical network.

Network interface with the WinCLAT IPv4 address 192.0.0.1 assigned

Test IPv4 Connectivity

To test connectivity with WinCLAT, browse to a website or connect to another resource that uses IPv4 only from an IPv6-only network. In this example, I’m connecting to Google’s IPv4-only website https://ipv4.google.com/.

Browser loading the IPv4-only site ipv4.google.com from an IPv6-only network using WinCLAT

Connectivity test confirming IPv4 access to ipv4.google.com from an IPv6-only network

Group Policy

Administrators can also manage WinCLAT configuration settings using Active Directory (AD) and Group Policy. To begin, copy the tcpip.admx and tcpip.adml files from C:\Windows\PolicyDefinitions and C:\Windows\PolicyDefinitions\en-us (or another preferred language) from a device on which WinCLAT is available to the Group Policy Central Store in AD. Once complete, you will find WinCLAT settings in the following location in the Group Policy Management console (gpmc.msc).

Computer Configuration > Policies > Administrative Templates > Network > TCPIP Settings > IPv6 Transition Technologies

Group Policy Management Editor showing WinCLAT settings under IPv6 Transition Technologies

Summary

WinCLAT extends Windows support for 464XLAT to noncellular network interfaces, allowing IPv4-dependent applications to operate on IPv6-only and IPv6-mostly networks. It translates locally generated IPv4 traffic to IPv6 and forwards it to a NAT64 gateway, while DNS64 provides direct NAT64 connectivity for IPv6-capable applications. Administrators can configure WinCLAT locally using netsh.exe or centrally through Group Policy and can use either router advertisements or DNS to discover the NAT64 prefix. WinCLAT currently requires SLAAC-based IPv6 addressing and does not support networks that assign client IPv6 addresses exclusively through stateful DHCPv6.

Additional Information

Microsoft Plans to Extend CLAT Support in Windows 11

Microsoft Windows CLAT Public Preview

RFC 6877 – 464XLAT: Combination of Stateful and Stateless Translation

RFC 8925 – IPv6-Only Preferred Option for DHCPv4

Windows Server DHCP and Option 108

Windows CLAT (WinCLAT) Resources

Configure Windows Server DNS64 for IPv6-Mostly and IPv6-Only

Many organizations are modernizing their networks by migrating from legacy IPv4 to IPv6. The goal is to replace IPv4 with IPv6 entirely. However, even though an organization can successfully migrate to IPv6-only networks internally, they do not control networks outside its boundaries. In some cases, a host on an IPv6-only network may need to communicate with an IPv4 resource. Administrators must deploy an IPv6 transition technology to support this scenario. A common solution to address this need is DNS64 and NAT64.

What are DNS64 and NAT64?

DNS64 and NAT64, defined in RFCs 6147 and 6146, respectively, work together to ensure endpoints on an IPv6-only network can still communicate with IPv4-only resources. DNS64 enables IPv6-only clients to communicate with IPv4-only servers by synthesizing AAAA DNS records from A records. When an IPv6-only client queries a domain with only an IPv4 address (A record), the DNS64 server creates a synthetic IPv6 address by embedding the IPv4 address within an administrator-defined NAT64 IPv6 prefix. The default (referred to as ‘well known’) prefix is 64:ff9b::/96. In the example below, the IPv4-only resource ipv4.test-ipv6.com is resolved using the Cloudflare public DNS64 resolver.

Using the synthetic DNS64 address allows the client to send IPv6 packets to a NAT64 gateway, which translates them to IPv4 for the destination server. DNS64 ensures seamless address resolution for IPv6-only networks accessing IPv4 resources without requiring actual IPv6 addresses for the target.

Caveat

While DNS64 is great for ensuring IPv4 access on IPv6-only networks, it has one critical limitation. The client must connect to a resource using a hostname or a fully qualified domain name. If a client attempts to connect to an IPv4 resource directly (e.g., https://172.16.21.12 or \\10.21.12.83\data), the resource will be unreachable. To address this limitation, the 464XLAT IPv6 transition technology must be used. For more information about 464XLAT, see my previous article, Microsoft Begins Rolling Out Windows CLAT for IPv6-Mostly and IPv6-Only Networks.

Enterprise DNS64

While there are public DNS64 resolves from Cloudflare, Google, and others, they aren’t helpful when trying to resolve internal hostnames in the enterprise. Organizations must deploy their own private DNS64 services in this scenario.

Windows Server and DNS64

Today, Windows Server does not natively support DNS64. Organizations are advised to use an enterprise DNS solution such as Infoblox or BlueCat for DNS64 services. Alternatively, administrators can deploy BIND DNS on the Linux platform of their choice. DNS64 is supported in BIND 9.8.0 and later.

DNS64 Proxy

To support testing and evaluation (and perhaps production deployment for smaller organizations), it is possible to configure any supported version of Windows Server to serve as a DNS64 proxy. In this scenario, a Windows Server is configured as a DNS64 server, but the server itself is not an actual DNS server. It does not have a DNS database or zone file; it is not authoritative for any zones and can’t perform conditional forwarding. It simply forwards DNS queries to the servers defined on its own network interface.

Windows Server DNS64 Configuration

The DNS64 service must be installed using PowerShell and the Set-NetDnsTransitionConfiguration command. Administrators will define some variables, configure DNS64, and create firewall rules to allow DNS traffic inbound to the server.

Configure DNS64

On a Windows Server member server (domain-join is optional), open an elevated PowerShell command window and run the following commands.

# Define variables
$AcceptInterface = ‘Ethernet’ # The interface name or alias that will accept DNS64 traffic
$SendInterface = ‘Ethernet’ # The interface name or alias that will send DNS64 traffic
$Nat64Prefix = ’64:ff9b::/96′ # The NAT64 prefix

# Configure DNS64
Set-NetDnsTransitionConfiguration -State Enabled -AcceptInterface $AcceptInterface -SendInterface $SendInterface -PrefixMapping “$Nat64Prefix,0.0.0.0/0” -PassThru

Configure Windows Firewall

Run the following PowerShell commands to configure the Windows Firewall to allow inbound DNS requests.

# Create firewall rules to allow DNS64 traffic inbound
New-NetFirewallRule -Name ‘DNSSrv-DNS-UDP-In’ -DisplayName ‘DNS (UDP, Incoming)’ -Description ‘Inbound rule to allow remote UDP access to the DNS64 service.’ -Group ‘DNS64 Service’ -Protocol UDP -LocalPort 53 -Direction Inbound -Profile Any -Action Allow -Enabled True

New-NetFirewallRule -Name ‘DNSSrv-DNS-TCP-In’ -DisplayName ‘DNS (TCP, Incoming)’ -Description ‘Inbound rule to allow remote TCP access to the DNS64 service.’ -Group ‘DNS64 Service’ -Protocol TCP -LocalPort 53 -Direction Inbound -Profile Any -Action Allow -Enabled True

GitHub

For reference, I’ve posted the relevant commands for configuring DNS64 on Windows Server on GitHub here.

DNS64 Testing

Once DNS64 is configured on the Windows Server, administrators can test operation by sending a DNS query for an IPv4-only resource to the DNS64 server using the following PowerShell command.

Resolve-DnsName -Name ipv4.test-ipv6.com -Server <DNS64 server IPv6 address>

For example.

Resolve-DnsName -Name ipv4.test-ipv6.com -Server 2001:579:6024:510::64

The DNS64 server responds with the native IPv4 address along with the synthesized IPv6 address. However, if the target resource has only an IPv6 address or has both IPv4 and IPv6 addresses, both are returned, as shown below.

Summary

DNS64 and NAT64 are essential tools for enabling communication between IPv6-only networks and IPv4 resources. While public resolvers exist, enterprises often need their own DNS64 service for internal hostname resolution. Windows Server does not natively support DNS64, but administrators can configure it as a DNS64 proxy for testing and smaller deployments. In this scenario, Windows Server can provide DNS64 functionality, helping organizations transition toward IPv6-only networks while maintaining access to legacy IPv4 systems.

Additional Information

Microsoft Begins Rolling Out Windows CLAT for IPv6-Mostly and IPv6-Only Networks

Configure DHCP Option 108 on Windows DHCP Server

IPv6 Transition Technology Options – IPv6 Buzz Podcast

Set-NetDnsTransitionConfiguration

RFC 6146 – NAT64

RFC 6147 – DNS64

RFC 6877 – 464XLAT

What is IPv6?

Windows CLAT (WinCLAT) Resources

Always On VPN DPC 5.2.0 Now Available

I’m pleased to announce that Always On VPN Dynamic Profile Configurator (DPC) version 5.2.0 is now available. My good friend Leo D’Arcy has been hard at work for the last few months squashing some bugs and adding a few new features to DPC. If you are running a previous release of Always On VPN DPC, either open source or commercial, it’s time to upgrade.

Important!! DPC 5.2.0 has a bug that prevents the service from stopping. This has been addressed in DPC 5.2.1. Guidance for upgrading from DPC 5.2.0 to 5.2.1 can be found here.

Reminder: We’re on Discord. Join the conversation today!

What’s New in DPC 5.2.0

Always On VPN DPC 5.2.0 has some compelling new features.

  • Exclude Routes from DNS – DPC has a feature that allows administrators to add routes to the routing table using DNS. When this setting is enabled, DPC will attempt to resolve the specified hostname to an IP address and add it to the VPN’s routing table when creating the profile. With 5.2.0, this capability has been extended to exclusion routes, allowing administrators to exclude resources by host name.
  • Write Event Logs to Disk – This setting allows administrators to optionally write DPC event information to a text file in addition to logging them in the event log. Writing event log information to a text file on disk can make troubleshooting easier in some scenarios.
  • Delay Profile Updates – This new feature ensures reliable VPN profile creation after group policy updates take place.

Bug Fixes

In addition to new capabilities, Always On VPN DPC 5.2.0 includes fixes for many outstanding issues.

  • DPC name resolution issue where duplicate IP addresses are returned, resulting in failed route additions when using ‘Allow Routes from DNS’.
  • Missing events in the DPC operational event log.
  • Enabling ‘Disable Disconnect Button’ or ‘Disable Advanced Edit Button’ settings results in a profile mismatch warning.
  • Added resiliency to DPC name resolution when one or more name resolution requests fail.

Group Policy Template

As a reminder, any time there are new features in DPC, there will be corresponding changes to Group Policy administrative template and template language files. Be sure to update your ADMX and ADML files in the group policy central store to take advantage of these new capabilities in DPC 5.2.0.

Recommendation

If you are running any release of Always On VPN DPC, commercial or open source, consider upgrading now to gain access to new features and operational reliability improvements. You can find DPC v5.2.0 on GitHub here.

Additional Information

Always On VPN DPC v5.2.0 Available Now

Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN DPC Now Open Source

Migrating from Always On VPN DPC Commercial to Open Source

Always On VPN DPC with Microsoft Intune

Microsoft Always On VPN on Discord

Always On VPN DPC

Always On VPN Client IP Address Assignment Methods

When Always On VPN clients connect to the VPN server, they must be assigned an IP address to facilitate network communication. When using Windows Server and Routing and Remote Access Service (RRAS) for VPN services, administrators must choose between Dynamic Host Configuration Protocol (DHCP) and static address pool assignment methods.

DHCP

DHCP is a quick and easy way to handle VPN client IP address assignment. However, there are some drawbacks and limitations associated with this option. Consider the following.

Allocation

DHCP for Always On VPN clients does not work as you might expect. For example, when a VPN client connects, it does not obtain its IP address directly from the DHCP server. Instead, the VPN server leases a block of IP addresses from the DHCP server and manages those on behalf of its clients. On the DHCP server, you will see the Unique ID column of these IP address leases indicating RAS.

Address Block Size

After configuring the VPN server to use DHCP VPN client IP address assignment, the VPN server will automatically lease a block of ten IP addresses from a DHCP server. When this initial block of ten IP addresses is exhausted, the VPN server will lease another block of ten IP addresses. Administrators can increase the size of the requested address block by creating the following registry key on each VPN server.

Key: HKLM\SYSTEM\CurrentControlSet\Services\RemoteAccess\Parameters\IP
Value: InitialAddressPoolSize
Type: DWORD
Data: <size of DHCP pool request>

Alternatively, administrators can download Update-VpnServerDhcpPoolSize.ps1 from my GitHub repository and run it on each VPN server to increase the size of the initial DHCP address pool request.

DHCP Options

The VPN server discards all DHCP option information returned by the DHCP server. The VPN server uses only the IP address from the DHCP lease. The client is unaware of any other information in the DHCP lease.

Subnet

By default, the VPN server will only request DHCP addresses from a scope that matches the same subnet as the IP address assigned to the VPN server’s network adapter. If the VPN server has more than one network interface, it will send DHCP requests from the network interface listed on the Adapter drop-down list, as shown here.

Note: This option is only available on servers configured with multiple network interfaces. Also, if the value is set to Allow RAS to select adapter, it is best to specifically define the network interface where DHCP and DNS requests are made.

Scope Size

When using the DHCP assignment method, ensure the DHCP scope contains enough IP addresses to support the number of concurrent connections expected on all VPN servers.

IPv6

DHCPv6 is not supported on RRAS for VPN client IP address assignment. The only option for IPv6 is prefix assignment.

RRAS in Azure

DHCP is not supported when deploying RRAS in Azure. Administrators deploying RRAS in Azure to support Always On VPN must use the static address pool assignment method. More details here.

Known Issues

When using DHCP with Windows Server 2019 RRAS servers, a known issue prevents this from working correctly. Administrators can download Update-VpnServerDhcpPrivileges.ps1 from my GitHub repository and run it on each VPN server to ensure proper DHCP operation.

Increased Complexity

Since the VPN server leases IP addresses on behalf of clients and discards DHCP option information included in the lease, there’s no real benefit to using DHCP. Using DHCP only adds complexity and introduces another dependency, making the solution more brittle and difficult to manage. Using the static address pool assignment method is a better choice.

Static Pool

Implementation best practices dictate using the static address pool assignment method instead of DHCP. The following is guidance for configuring RRAS to support the static address pool option for VPN client IP address assignment.

Unique Subnet

Using a unique IP subnet is best when using the static address pool assignment method. However, this also requires configuring internal network routing to return traffic for that subnet to the individual VPN server where that subnet is assigned. Each server must have a unique IP address pool assigned. Define static address pools using subnet boundaries when configuring multiple VPN servers. Assigning IP address pools along subnet boundaries simplifies internal network routing configuration. Ensure that assigned IP address pool subnets are large enough to accommodate the total number of concurrent connections expected on each server. Be sure to overprovision to handle failover scenarios.

Same Subnet

Alternatively, administrators can assign VPN client IP addresses from the same subnet as the VPN server’s network interface. Assigning VPN client IP addresses from the same subnet as the VPN server eliminates the need for any internal network routing configuration, simplifying deployment. However, server subnets are often small and may not have enough IP address space to support numerous concurrent VPN connections. Be sure to plan accordingly.

Static IP Addresses

It is possible to assign a static IP address to an individual user. However, assigning a static IP address to a specific device is not. I will discuss static IP address assignments for Always On VPN clients in a future blog post.

Other Limitations

Here are some additional things to consider when creating a VPN client IP addressing strategy.

DNS

Always On VPN clients can be configured to register their IP address in DNS. However, the VPN client configuration controls this setting. The DHCP server does not register IP addresses in DNS when using DHCP. The client registers its IP address in DNS directly after it connects. In addition, a VPN client will receive a different IP address each time it connects to the VPN server. DNS propagation can delay hostname resolution on-premises for remote-connected VPN clients.

Selective Addressing

Regardless of which assignment method is selected, assigning different IP addresses to different types of connections is not possible. For example, a common ask is to assign user connections from one IP address pool and device connections from another. The only option to support this is to use different servers for each type of connection.

Summary

The best practice for IPv4 VPN client addressing is to use the static address pool method with a unique IPv4 subnet per server. Using static address pool assignment provides the most flexible configuration options and eliminates the dependency on internal services, making the solution more resilient and easier to manage. A unique address pool per server ensures that a large enough subnet can be defined to support the expected number of concurrent connections, regardless of the subnet size the VPN server is assigned to. Also, a unique IP subnet for VPN clients makes configuring internal firewall rules to control VPN client access easier.

Additional Information

Always On VPN and IPv6

Always On VPN Client DNS Server Configuration

Always On VPN Routing Configuration

Always On VPN RRAS Internal Interface Non-Operational

Always On VPN and Interface Metrics

Always On VPN DNS Registration Update Available

In Windows, each network interface identified by the operating system is assigned a metric value. Interface metrics are settings that determine the priority or preference of network interfaces when there are multiple active network connections. The Windows networking stack uses these metrics to determine which network interface should be used for routing traffic when multiple network interfaces are available. Network interface metrics are critical for Always On VPN administrators to understand because they can impact how name resolution requests are processed when an Always On VPN connection is established.

Metric Values

By default, Windows automatically assigns metric values to network interfaces (including VPN interfaces) based on various factors, including the connection speed, link state, and interface type. It tries to select the most suitable interface for general internet connectivity.

Metrics and DNS

Windows will also use the network interface with the lowest metric value as the preferred interface for sending DNS queries by default. This means that DNS queries will be routed through the network interface with the lowest metric value, assuming it is available and connected. When an Always On VPN connection is established, DNS queries may fail or return unexpected results if the network interface metrics are not configured optimally.

Split DNS and Wired Ethernet

Split DNS (sometimes called ‘split brain DNS’) is when the DNS namespace is the same internally and externally. The most common scenario where interface metric settings interfere with DNS operation is when using split DNS and the endpoint is connected to the Internet with a wired Ethernet connection. In this scenario, the Ethernet interface will be assigned the same or lower interface metric value as the Always On VPN interface, which can yield unexpected results.

Viewing Metrics

Always On VPN administrators can view currently assigned interface metric values by running the following PowerShell command.

Get-NetIpInterface

Assigning Metrics

Most Always On VPN administrators will never have to change interface metric settings. However, if your implementation uses split DNS and some of your endpoints connect using wired Ethernet connections, you may need to update the interface metric settings to ensure proper DNS operation. Choose a setting for the interface metric value that is lower than the wired Ethernet interface. I’ve used a value of ‘3’ without issue for many years. Use one of the following methods to update the interface metric for Always On VPN connections.

PowerShell

Updating interface metric settings in Windows can be accomplished by running the Set-NetIpInterface PowerShell command.

Set-NetIpInterface -InterfaceAlias <connection name> -InterfaceMetric 3

Note: Using PowerShell to assign the interface metric is not persistent! While this method is suitable for local validation testing, you should use one of the following methods to implement this change permanently.

Rasphone.pbk

To assign the interface metric permanently, Always On VPN administrators can edit the following settings in the rasphone.pbk configuration file.

IpInterfaceMetric=3

Ipv6InterfaceMetric=3

Administrators can automate updating this setting using the Update-Rasphone.ps1 PowerShell script. In addition, the following scripts can be used with Microsoft Intune remediation.

Detect-DeviceIpv4InterfaceMetric.ps1

Remediate-DeviceIpv4InterfaceMetric.ps1

Detect-DeviceIpv6InterfaceMetric.ps1

Remediate-DeviceIpv6InterfaceMetric.ps1

Detect-Ipv4InterfaceMetric.ps1

Remediate-Ipv4InterfaceMetric.ps1

Detect-Ipv6InterfaceMetric.ps1

Remediate-Ipv6InterfaceMetric.ps1

DPC

Organizations using PowerON Platforms’ Dynamic Profile Configurator (DPC) to manage Always On VPN client configuration settings with Active Directory and group policy or Microsoft Intune can enable the VPN Tunnel Metric setting.

Additional Information

Get-NetIpInterface PowerShell Command

Set-NetIpInterface PowerShell Command

Managing Always On VPN Client Settings with DPC

Always On VPN DPC with Microsoft Intune

Always On VPN DPC Advanced Features

Always On VPN DPC Video Demonstration

PowerON Platforms Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN and Split DNS

Cloudflare Public DNS Resolver Now Available

Split DNS, sometimes called ‘split brain’ DNS, is when an organization uses the same DNS namespace internally and externally. For example, the internal Active Directory domain name is example.com, so internal resources are accessed using a fully qualified domain name (FQDN) like dc1.example.com. Additionally, external properties such as mail and web services use the same namespace so that a public web server might have a name like www.example.com. Internal resources will resolve to internal, private IP addresses, whereas public services resolve to external, public IP addresses.

Complications

Things get complicated when the same resource (FQDN) is available internally and externally, especially for Always On VPN clients. For example, accessing app.example.com on the internal network resolves to a private address, but accessing the same resource on the Internet resolves to a public IP address. Often there are different authentication requirements for internal and external resources, which can yield unexpected results.

Name Resolution

Always On VPN administrators might prefer app.example.com to be accessed via the Internet when connected with Always On VPN. However, VPN clients will attempt to connect via the internal network using their default configuration. Solving this challenge requires internal DNS server changes.

NRPT?

It might be tempting for administrators to use the Name Resolution Policy Table (NRPT) to solve name resolution issues for Always On VPN. However, the NRPT has some limitations and may not always produce the desired results. For example, the NRPT only directs DNS queries. It does not define which resource records are returned by DNS. Also, some applications ignore the NRPT, which limits its usefulness. A better solution is to use DNS Policies in Windows Server.

DNS Policies

Microsoft introduced DNS policies with Windows Server 2016. DNS policies are a powerful tool administrators can use to fine-tune name resolution based on many factors. In the case of split DNS, administrators can configure internal DNS to return an IP address for a resource based on the source IP address of the name resolution query. VPN clients receive one IP address for a given DNS query, while all other clients receive a different IP address. DNS policies ensure that remote clients connected to the VPN will receive the proper IP address for the resource requested, as defined by the administrator.

Caveats

DNS policies are powerful and flexible, but there are some potential drawbacks. All enterprise DNS servers used by Always On VPN clients must be running Windows Server 2016 or later. Also, administrators must use PowerShell to configure DNS policies exclusively. There is no GUI interface to configure DNS policies. DNS policies do not appear in the DNS management interface, which could confuse an administrator unaware that DNS policies are in place. In addition, DNS client subnets and query resolution policies do not replicate across DNS servers. Administrators must manually configure these on each DNS server used by Always On VPN clients. However, zone scopes and resource records in those scopes do replicate automatically.

Scenario

For demonstration purposes, let’s assume that an Always On VPN client needs to access foo.example.com. It resolves to a private IP address on the internal network and a public IP address on the Internet. By default, foo.example.com will resolve to the internal private IP address of the server when connected with Always On VPN. However, the desire is to have foo.example.com resolve to the public IP address when connected with Always On VPN. To accomplish this, we’ll create a DNS policy to ensure that connected Always On VPN clients can resolve foo.example.com to the public IP address when resolving this name over the VPN tunnel.

DNS Policy Configuration

Open an elevated PowerShell command on a DNS server and perform the following steps to create a DNS policy for VPN clients.

Client Subnet

Run the Add-DnsServerClientSubnet PowerShell command to create a client subnet in DNS that includes all IP networks assigned to VPN clients. Summarize IP prefixes if there are multiple VPN servers in the organization.

Add-DnsServerClientSubnet -Name VPN -IPv4Subnet ‘172.16.100.0/22’ -IPv6Subnet ‘2001:db8:fcd2:1000::/60’

If summarizing IP prefixes for multiple servers isn’t possible, multiple subnets can be added to a DNS client subnet using the following command.

Add-DnsServerClientSubnet -Name VPN -IPv4Subnet @(‘172.16.100.0/24’, ‘172.16.101.0/24’, ‘172.16.102.0/24’, ‘172.16.103.0/24’) -IPv6Subnet @(‘2001:db8:fcd2:1001::/64’, ‘2001:db8:fcd2:1002::/64’, ‘2001:db8:fcd2:1003::/64’)

To make changes to an existing DNS client subnet, use the Set-DnsServerClientSubnet PowerShell command.

Note: Client Subnets do not replicate across domain controllers. Run the command above on all DNS servers or each DNS server used by Always On VPN clients.

Zone Scope

Create a Zone Scope that includes the DNS records to be returned to VPN clients. The default zone scope is the DNS zone itself. Configure an additional zone scope for the DNS zone by using the Add-DnsServerZoneScope PowerShell command.

Add-DnsServerZoneScope -ZoneName example.com -Name VPN

Resource Records

Next, add DNS records to the new zone scope using the Add-DnsServerResourceRecord PowerShell command.

Add-DnsServerResourceRecord -ZoneName example.com -A -Name foo -IPv4Address 203.0.113.12 -ZoneScope VPN

Add-DnsServerResourceRecord -ZoneName example.com -AAAA -Name foo -IPv6Address 2001:db8:21::12 -ZoneScope VPN

DNS Policy

Finally, create a DNS query resolution policy that ties everything together. Run the Add-DnsServerQueryResolutionPolicy command to create the DNS query resolution policy. Once configured, when the DNS server receives a DNS query, the policy will recognize that the query originates from a VPN client subnet and will return the resource record from the VPN zone scope with the public IP address defined previously.

Add-DnsServerQueryResolutionPolicy -Name VPN -Action ALLOW -ClientSubnet ‘EQ,VPN’ -FQDN ‘EQ,foo.example.com’ -ZoneScope ‘VPN,1’ -ZoneName example.com

Note: DNS query resolution policies do not replicate across domain controllers. Run the command above on all DNS servers or each DNS server used by Always On VPN clients.

Results

Once complete, the hostname ‘foo’ in our example above resolves to different IP addresses based on the client’s IP address.

DNS query for ‘foo’ from internal client.

DNS query for ‘foo’ from VPN client.

Summary

There are many scenarios where Windows Server DNS policies can be used to fine-tune name resolution for Always On VPN clients. Hopefully, this example gives you an idea of how DNS policies work, and you can use them to solve your unique name resolution challenges with Always On VPN.

Additional Information

Windows Server DNS Policies Overview

Always On VPN Short Name Access Failure

Always On VPN Client DNS Server Configuration

What’s New in Always On VPN DPC v3.0

Recently I wrote about a compelling solution from PowerON Platforms for managing Always On VPN client configuration setting using Active Directory group policy. Always On VPN Dynamic Profile Configurator (DPC) addresses a very specific need for managing Always On VPN for organizations that have not yet migrated to Microsoft Endpoint Manager/Intune. Recently, PowerON Platforms released an important update to DPC that includes many new features and capabilities.

New Features

Always On VPN DPC version 3.0 includes the following new functionality Always On VPN administrators are sure to find useful.

  • Traffic filters – Support for enabling traffic filters for both device tunnel and user tunnel are now supported in DPC, greatly simplifying the task of creating access control lists to enforce zero-trust network access (ZTNA) policies.
  • Enhanced security – The option to disconnect the VPN connection if the VPN server does not present a cryptobinding TLV is now enabled by default. This often-overlooked security setting ensures VPN client connections are not intercepted by detecting man-in-the-middle attacks.
  • Device tunnel enhancements – Administrators can now display the device tunnel connection and status in the Windows UI.
  • Backup connection – Always On VPN DPC now supports the configuration and deployment of a backup VPN connection, which is helpful when Always On VPN connectivity is disrupted.
  • Hostname routing – Administrators can now define hostnames in the routing table. Hostnames are resolved on the endpoint and converted to IP addresses for including in the routing table.
  • Smart card authentication – Always On VPN DPC now supports smart card authentication as an authentication option in addition to client authentication certificates.

Learn More

Interested in learning more about Always On VPN DPC? Fill out the form below and I’ll provide you with additional information or visit aovpndpc.com to sign up for a free trial.

Additional Information

Always On VPN with Active Directory Group Policy

Always On VPN Video Demonstration

Always On VPN DPC Advanced Features

Always On VPN DPC on YouTube

Always On VPN SSTP with Let’s Encrypt Certificates

Always On VPN SSTP Security Configuration

When configuring the Windows Server Routing and Remote Access Service (RRAS) to support Secure Socket Tunneling Protocol (SSTP) for Always On VPN user tunnel connections, administrators must install a Transport Layer Security (TLS) certificate on the VPN server. The best practice is to use a certificate issued by a public Certification Authority (CA). In addition, administrators should use a TLS certificate using Elliptic Curve Digital Signature Algorithm (ECDSA) for optimal security and performance.

Let’s Encrypt

Obtaining a public TLS certificate is not inherently difficult, nor is it expensive. However, Let’s Encrypt is a nonprofit public CA issues TLS certificates entirely for free. Always On VPN supports Let’s Encrypt TLS certificates, and installing a Let’s Encrypt certificate on the Always On VPN RRAS server is quite simple.

Pros and Cons

Using Let’s Encrypt certificates for Always On VPN has several significant advantages over traditional public CAs.

  • Cost – Let’s Encrypt certificates are free! No cost whatsoever.
  • Speed – Enrolling for a Let’s Encrypt certificate takes just a few minutes.
  • Trusted – Let’s Encrypt certificates are trusted by default in Windows 10 and Windows 11.

Let’s Encrypt is not without some drawbacks, however.

  • Lifetime – Let’s Encrypt certificates are only valid for 90 days.
  • Administration – Certificates must be redeployed frequently (every 90 days).
  • Security – PFX files (which include private keys) are left on disk by default.

It is possible to mitigate some of these drawbacks, though. For example, deleting PFX files after import can improve security. Alternatively, using a Certificate Signing Request (CSR) eliminates PFX files completely.

Also, it is possible to fully automate the Let’s Encrypt certificate enrollment and RRAS configuration process, which eases the administrative burden. And rotating certificates every 90 days could be considered an advantage from a security perspective! Enrolling new certificates (and specifically certificates with unique keys) is advantageous in that respect.

Certificate Enrollment

There are several different ways to enroll for Let’s Encrypt certificates. The preferred method is using PowerShell, as it works on both Windows Server with Desktop Experience (GUI) and Windows Server Core. Using PowerShell, administrators can also fully automate the enrollment and assignment of the certificate in RRAS.

PowerShell Module

To enroll for Let’s Encrypt TLS certificates on the VPN server, install the Posh-ACME PowerShell module. On the RRAS server, open an elevated PowerShell window and run the following command.

Install-Module Posh-ACME

Certificate Request

After installing the Posh-ACME PowerShell module, select a Let’s Encrypt environment by running the following command. Use LE_PROD for the production Let’s Encrypt server or LE_STAGE for the staging environment (used for testing).

Set-PAServer LE_PROD

Next, request a new certificate using the following command.

New-PACertificate -Domain vpn.example.net -Contact ‘[email protected]’ -CertKeyLength ec-256 -AcceptTOS -Install

The administrator is prompted to create a TXT record in public DNS to prove ownership of the domain. Using the example above, create a DNS record called _acme-challenge.vpn in the example.net DNS zone.

Once complete, the TLS certificate is automatically installed in the local computer certificate store on the VPN server and can be assigned in the RRAS management console, as shown here.

Note: R3 is a Let’s Encrypt issuing certification authority.

DNS Plugin

The Posh-ACME PowerShell module supports DNS plugins that allow administrators to automate the creation of the DNS TXT record used to authorize certificate enrollment. DNS plugins for many public DNS providers are available. Some of the more popular DNS providers are listed here.

  • Microsoft Azure
  • Amazon Route53
  • Cloudflare
  • Akamai
  • GoDaddy
  • Infoblox
  • Windows Server

A list of all supported DNS plugins for Posh-ACME can be found here.

Certificate Binding

Administrators can use the following PowerShell example code to automate the process of binding the new TLS certificate to the SSTP listener in RRAS.

$Thumbprint = <TLS certificate thumbprint>
$Cert = Get-ChildItem -Path Cert:\LocalMachine\My\$thumbprint
Set-RemoteAccess -SslCertificate $Cert
Restart-Service RemoteAccess -Passthru

Additional Information

Posh-ACME Tutorial

Windows 10 Always On VPN TLS Certificate Requirements for SSTP

Windows 10 Always On VPN SSTP Security Configuration

Always On VPN Error 853 on Windows 11

Recently I did some validation testing with Always On VPN on Windows 11, and I’m happy to report that everything seems to work without issue. However, a few readers have reported 853 errors when establishing an Always On VPN connection after upgrading to Windows 11.

Can’t Connect

After upgrading to Windows 11, an Always On VPN connection may fail with the following error message.

“The remote access connection completed, but authentication failed because the certificate that authenticates the client to the server is not valid. Ensure the certificate used for authentication is valid.”

Error 853

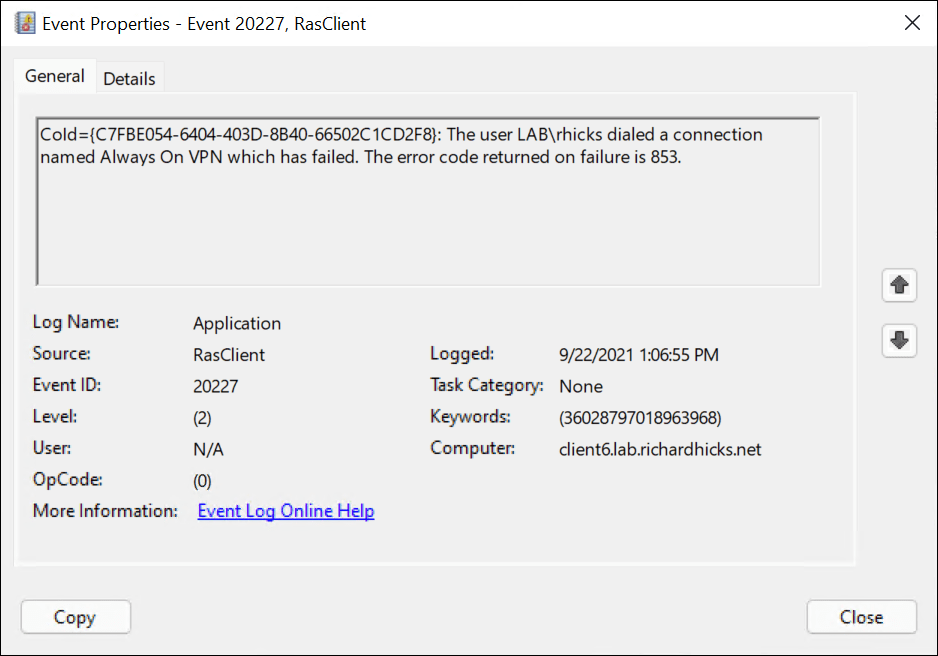
In addition, the Application event log records an event ID 20227 from the RasClient source that includes the following message.

“The user <username> dialed a connection name <connection name> which has failed. The error code returned on failure is 853.”

Server Identity

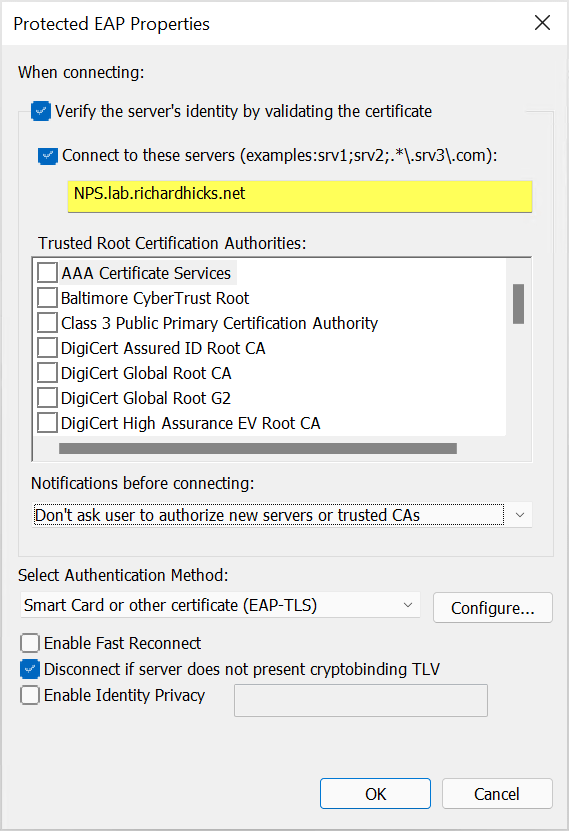
This error will occur when using Protected Extensible Authentication Protocol (PEAP) authentication. Specifically, it can happen when the option to verify NPS server validity by its certificate is selected, and an explicit list of NPS servers is defined, as shown here.

Case Sensitive

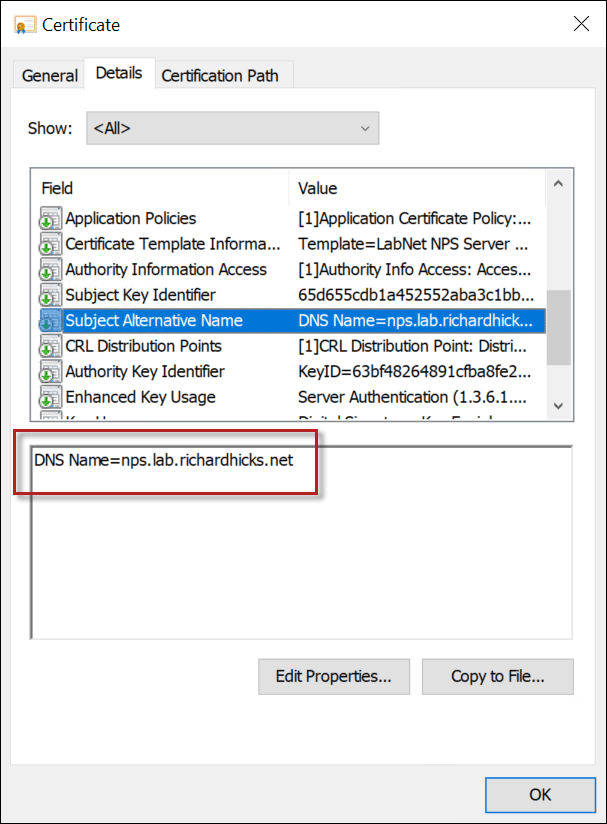
In this specific scenario, Windows 11 now appears to be case-sensitive when it compares the NPS server name entered in the NPS configuration to the Subject Name on the certificate returned by the server. For example, if the Subject Name (or Subject Alternative Name, if present) entry on the NPS server certificate is nps.lab.richardhicks.net, using NPS.lab.richardhicks.net will not match and return an 853 error.

Windows 11

Case matching when validating the NPS server certificate is a change in behavior from Windows 10. Before Windows 11, this comparison was case-insensitive, and any combination of case would match if the entire hostname matched. Going forward, it appears Microsoft has also decided to require case matching to validate the server certificate.

Recommendations

Administrators should look carefully at the server certificate issued to the NPS server and ensure their client configuration accurately reflects the hostname in a case-sensitive manner to ensure a smooth migration from Windows 10 to Windows 11.

Additional Information

Troubleshooting Windows 10 Always On VPN Error 853

Windows 10 Always On VPN Network Policy Server (NPS) Load Balancing

Always On VPN Short Name Access Failure

Using Microsoft Endpoint Manager (Intune), administrators can provision Always On VPN to devices that are Azure AD joined only. Users accessing on-premises resources from these devices can still use seamless single sign-on, making this deployment option popular for organizations moving to the cloud.

Short Names

After deploying Always On VPN to Windows 10 devices that are Azure AD joined only and configured to use client certificate authentication, administrators may find that users cannot access on-premises resources by their short name, such as \\app1. The connection fails and returns the following error message.

“Windows can’t find <servername/sharename>. Check the spelling and try again.”

FQDN

Interestingly, on-premises resources are accessible using their fully qualified domain name (FQDN), such as \\app1.corp.example.net.

Troubleshooting

Testing name resolution using the short name works as expected, and the resource is reachable at the network layer, as shown here.

Workaround

This issue is related to how Windows performs authentication when connected via VPN. To resolve this issue, edit the rasphone.pbk file and change the value of UseRasCredentials to 0. Rasphone.pbk can be found in the $env:AppData\Microsoft\Network\Connections\Pbk folder.

After updating this setting, restart the VPN connection for the change to take effect.

Proactive Remediations

While helpful for testing, editing rasphone.pbk manually obviously does not scale well. To address this, consider using Intune Proactive Remediations. Intune Proactive Remediations allows administrators to deploy detection and remediation PowerShell scripts to monitor specific settings and update them if or when they change. Proactive Remediations will ensure the setting is applied consistently across all managed endpoints.

GitHub Repository

I have created a new GitHub repository dedicated to PowerShell scripts for Endpoint Manager Proactive Remediations for Always On VPN. There you will find detection and remediation scripts for the UseRasCredentials settings change described in this article.

PowerShell

Administrators can also implement this setting by running the following PowerShell command.

Set-ItemProperty -Path ‘HKLM:\SYSTEM\CurrentControlSet\Control\Lsa’ -Name DisableDomainCreds -Value 1

Group Policy

Another option for implementing this setting is by enabling the following Active Directory Group Policy setting.

Computer Configuration > Windows Settings > Security Settings > Local Policies > Security Options > Network access: Do not allow storage of passwords and credentials for network authentication

Additional Information

Always On VPN Endpoint Manager Proactive Remediation Scripts on GitHub

Endpoint Manager Proactive Remediations Tutorial