What’s New in Entra Global Secure Access Client for Windows v2.34.222

On October 19, 2026, Microsoft announced an update for the Entra Global Secure Access (GSA) client. This latest release, v2.34.222, adds support for a new sign-in option, updates Conditional Access sign-in frequency, improves diagnostics, and enhances local network bypass. It also improves Windows Firewall behavior off network, along with telemetry and accessibility improvements.

Changes in v2.34.222

GSA client v2.34.222 includes the following new features and enhancements.

Web Sign-In

The GSA client now supports Web sign-in for Windows. This credential provider enables browser-based Windows sign-in using methods such as Microsoft Authenticator, Temporary Access Pass (TAP), or a SAML-P federated identity. Web sign-in requires a Microsoft Entra-joined device running Windows 11 version 22H2 with KB5030310 or later, plus internet connectivity.

Windows Firewall Profile

This release improves Windows Firewall profile selection when Private Access is enabled. When the device is not directly connected to the corporate network, Windows Firewall does not activate the Domain profile.

Traffic Forwarding Profile Details

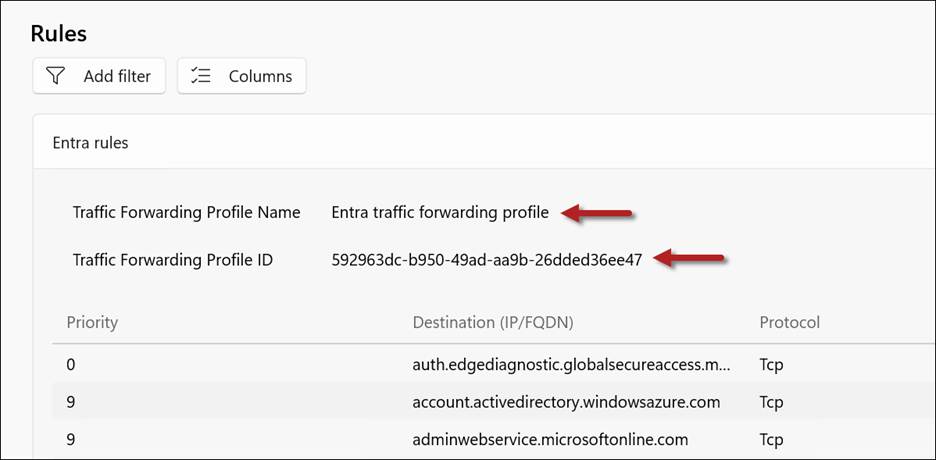
The new GSA client features improved diagnostics. With this update, the Forwarding profile tab in the Advanced diagnostics section now displays the Traffic Forwarding Profile Name as it appears in the Entra admin center, along with the Traffic Forwarding Profile ID.

Traffic Forwarding Profile Name and ID

Conditional Access

GSA client v2.34.222 now includes support for Conditional Access sign-in frequency for Private Access applications. This feature is part of a phased rollout and might not be available in all tenants immediately.

Prefer Local Network Bypass

With this update, the Prefer local network option limits bypass to connections destined for IP addresses in common private network ranges. Microsoft documentation doesn’t elaborate on specifically which ‘common private network ranges’, but I suspect this means private IPv4 address ranges as defined in RFC 1918.

GSA Traceroute Changes

In GSA client v2.34.222, Microsoft has replaced the command-line version of the GSA traceroute tool (GsaTracert.exe) with a new GUI version. However, during my initial testing (and confirmed by others testing this feature), it appears to be broken at this time. When I launch GsaTracert.exe, the UI returns the following error message.

“Could not retrieve the forwarding profile from the registry. Ensure the Global Secure Access Client is installed and running.”

I will post an update as soon as Microsoft resolves this issue.

Additional Changes

In addition to the changes highlighted above, the new GSA client includes the following additional enhancements.

  • UDP tunneling improvements
  • Memory utilization improvements
  • New telemetry capabilities
  • Accessibility improvements
  • Bug fixes and other miscellaneous improvements

Summary

GSA client v2.34.222 introduces several useful enhancements for administrators and users. Organizations should validate the update against their existing configuration before broad deployment. My initial testing also identified an issue with the updated diagnostic tool, as described above.

Additional Information

Microsoft Entra Global Secure Access Client v2.34.222

Microsoft Entra Global Secure Access (GSA)

Microsoft Entra Private Access

Microsoft Entra Internet Access

Entra Private Access and VPN Migration Strategies on Entra.News

Always On VPN Security Updates September 2026

Microsoft released the September 2026 security updates today, which include numerous fixes affecting Always On VPN deployments. This month’s edition addresses vulnerabilities in Windows Server Routing and Remote Access (RRAS), VPN protocols such as Secure Socket Tunneling Protocol (SSTP) and Internet Key Exchange version 2 (IKEv2). The updates also include Active Directory Certificate Services (AD CS), a crucial supporting infrastructure service for Always On VPN.

RRAS

September 2026 Microsoft security updates include 8 CVEs for RRAS. Four are rated Critical, the most severe having a CVSS rating of 9.8.

RCEs

The following five CVEs are Remote Code Execution vulnerabilities. Four are rated Critical.

Privilege Escalation

The following two CVEs are RRAS privilege escalation vulnerabilities. Both are rated Important.

Denial of Service

Finally, the last CVE addresses a denial-of-service vulnerability in RRAS.

VPN Protocols

The following section outlines vulnerabilities addressed in the September 2026 security updates affecting commonly used VPN protocols.

SSTP

The following four CVEs cover vulnerabilities in SSTP. One is rated critical with a CVSS score of 9.8. The rest are rated Important.

IKEv2

The following CVEs address vulnerabilities in the IKEv2 VPN protocol. All are rated important.

AD CS

Microsoft AD CS is commonly deployed to issue and manage certificates used for encryption and user and device authentication in Always On VPN deployments. The following four CVEs address vulnerabilities disclosed in AD CS. The first two are privilege escalation vulnerabilities, the third covers information disclosure, and the last addresses a tampering vulnerability. All are rated Important.

Summary

The September 2026 Microsoft security updates address several critical vulnerabilities affecting organizations that have deployed Microsoft Always On VPN. Administrators are encouraged to update their systems as soon as possible.

Additional Information

Always On VPN: Secure Remote Access for Windows

Microsoft September 2026 Security Updates

Always On VPN Dynamic Profile Configurator (DPC) Webinar

Managing Microsoft Always On VPN deployments doesn’t have to be complicated. Always On VPN Dynamic Profile Configurator (DPC) is a free, open-source solution that simplifies deploying and managing Always On VPN client configuration settings while extending the capabilities of native deployment methods such as Microsoft Intune VPN profiles, custom XML, and PowerShell scripts.

Whether you’re deploying Always On VPN for the first time or looking to streamline an existing implementation, DPC provides powerful features that make advanced VPN configuration easier to deploy, manage, and maintain.

Join Our Live Webinar

Join me on Tuesday, August 18, at 1:00 PM EDT for a live webinar featuring Leo D’Arcy, creator and lead developer of Always On VPN DPC. During this live session, we’ll demonstrate many of DPC’s latest capabilities and show how they can simplify even the most complex Always On VPN deployments. Topics include:

  • Configuring flexible VPN deployment strategies
  • Optimizing interface and route metrics
  • Dynamically excluding Microsoft 365 and custom domains from the VPN tunnel
  • Configuring IKE mobility settings for improved roaming
  • Defining and managing IPv6 routes
  • Deploying DPC using Active Directory and Microsoft Intune
  • Exploring additional advanced features and deployment scenarios

Throughout the webinar, we’ll share practical guidance, configuration tips, and real-world examples to help you get the most from Always On VPN DPC.

Register Today

Registration is free, but you must register in advance to attend. If you can’t attend the live session, register anyway, and you’ll receive access to the on-demand recording after the event.

We’ll also reserve time for a live Q&A at the end of the presentation, giving you the opportunity to ask questions directly to the developers and experts behind DPC.

We look forward to seeing you there!

Additional Information

Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN DPC Advanced Features

Always On VPN DPC with Microsoft Intune

Migrating from Always On VPN DPC Commercial to Open Source

Always On VPN DPC Commercial Support Now Available

Always On VPN DPC Discord Channel

Microsoft Entra Private Network Connector Overview and Deployment Strategies

When deploying Microsoft Entra Private Access, administrators must install at least one Entra Private Network Connector to facilitate communication between Global Secure Access clients and on-premises resources. The Entra Private Network connector is a software agent that communicates outbound only. It requires no inbound connectivity, reducing public network exposure and minimizing the organization’s attack surface.

Entra Private Network Connector

The Entra Private Network connector is essentially Microsoft Entra application proxy (formerly Azure AD Application Proxy), updated to support all TCP and UDP-based communication. You can download the connector by opening the Entra admin center, navigating to Global Secure Access > Connect > Connectors, and clicking the Download connector service link.

Cloud Appliances

To enable access to cloud-hosted resources, the Entra Private Network connector can be installed on a VM in those environments. However, the Entra Private Network connector is also available as an appliance in public preview for the following cloud providers.

Resource Requirements

The following recommendations pertain to VM resources for the Entra Private Network connector server.

  • Windows Server 2016 or later. However, Windows Server 2016 reaches end of life in January 2027, so Windows Server 2022 and later are recommended. The Desktop edition is required, but it can technically be installed on Server Core with the Application Compatibility Feature on Demand for Server Core. However, Microsoft may not formally support this option.
  • Minimum 4 CPU cores and 8GB RAM. Monitor resource utilization during migration. Provision additional CPU and/or memory when utilization consistently exceeds 70% during peak times. Scaling out (adding servers) is preferred over scaling up (adding CPU and RAM).
  • Domain Join. Domain join is optional but recommended. Domain join is required to support single sign-on (SSO).

Connector Groups

A Connector Group is a logical grouping of Entra Private Network connectors. A Connector Group functions as a single unit for high availability and load balancing. Connectors are deployed in the same region as the tenant by default.

Default Group

When you install the Entra Private Network connector, it is placed into the Default connector group. However, this may not always be desirable. For example, the organization may have multiple data centers in different geographies. They may also have resources hosted in different Active Directory forests or perhaps located in isolated network locations. Using a common connector group may be suboptimal or not work at all.

Custom Groups

Administrators can define custom connector groups as needed. Custom connector groups ensure that connectors always have access to the resources nearest to them. They can be deployed in different locations and assigned to other Azure regions to ensure optimal traffic routing and reduced latency. Today, administrators can create connector groups in the North America, Europe, Australia, Asia, and Japan regions.

Create a Connector Group

Open the Microsoft Entra admin center and perform the following steps to create a new Entra Private Network connector group.

  1. Navigate to Global Secure Access > Connect > Connectors and Sensors.
  2. Click on New Connector Group.
  3. In the Name field, enter a descriptive name for the connector group.
  4. From the Connectors drop-down list, select one or more Entra Private Network connectors to assign to the group. Optionally, you can leave this field blank and assign connectors later.
  5. Click Save.
Entra admin center New Connector Group page with name and connector selection

Connector Group Assignment

Once you have created a new connector group, you can assign Quick Access or individual Enterprise applications to it as follows.

Quick Access

To assign a new connector group to the Quick Access application, open the Entra admin console, navigate to Global Secure Access > Applications > Quick Access, and select the Network access properties tab. Select the new connector group from the Connector Group drop-down list.

Quick Access network access properties with the Connector Group drop-down list

Enterprise Applications

To assign a new connector group to an individual Enterprise application, navigate to Global Secure Access > Applications > Enterprise applications. Select an application, then select Network access properties. Select the new connector group from the Connector Group drop-down list.

Enterprise application network access properties with the Connector Group drop-down list

Deployment Strategy

The following are best practices for deploying the Entra Private Network connector.

Redundancy

Always deploy at least two Entra Private Network connectors to ensure high availability and eliminate single points of failure.

Location

Install the Entra Private Network connector on servers closest to the applications they serve. Deploy connectors in all locations where applications are accessed, including on-premises networks and Infrastructure-as-a-Service (IaaS) resources.

Default Connector Group

Avoid using the default connector group for application assignment. Always use custom connector groups for application access. This ensures that new connectors do not process production traffic immediately after installation, which can cause unexpected behavior if the connector is not optimally deployed for the published resource or is not connected to the back-end application.

Deleting Connectors

Entra Private Network connectors cannot be removed from the management console. If you uninstall a connector, its status will show as inactive. After 10 days of inactivity, it will be automatically removed.

Reassigning Connectors

Administrators can reassign connectors to different connector groups at any time. However, existing connections on that connector server from the prior group assignment will remain until they age out. Administrators can restart the connector service or reboot the server to address this issue.

Restart-Service -Name WAPCSvc -PassThru

Connector Updates

The Entra Private Network connector will automatically install major updates when they become available. However, not all updates are applied automatically. Don’t be alarmed if you see discrepancies between release versions across multiple connector servers in the admin console. Administrators can always perform software updates manually to ensure uniform connector versions in their environment, if desired.

Diagnostics

Beginning with Entra Private Network connector v1.5.4287.0, the agent installation also includes the diagnostic utility ConnectorDiagnosticsTool.exe, which is in the C:\Program Files\Microsoft Entra Private Network Connector\ folder on the connector server. Running the tool initiates a series of tests to perform a health check of the connector service, including certificate status, connectivity, enabled TLS versions, service status, and more.

ConnectorDiagnosticsTool.exe health check results for the Entra Private Network connector

Note: Entra Private Network connector v1.5.4522.0 and later includes a graphical output, as shown above. Previous versions featured text-based output only.

Summary

Microsoft Entra Private Network Connectors are lightweight, outbound-only agents that enable secure access to on-premises and cloud resources through Entra Private Access. Best practices emphasize deploying at least two connectors per location for redundancy, placing them close to target applications, using custom connector groups for high availability, load balancing, and optimal routing, and assigning them to Quick Access or enterprise applications while avoiding the default group. Ensure that VMs are appropriately sized for the expected connector traffic, and consider using marketplace appliances for Azure, AWS, and GCP. If you’ve previously deployed the Entra Private Network connector, ensure that it is running the latest release to take advantage of new diagnostics for troubleshooting.

Additional Information

Microsoft Entra Private Network Connectors

Microsoft Entra Private Network Connector groups

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Access Intelligent Local Access

Always On VPN vs. Entra Private Access: Choosing the Right Access Model

Resolving PKCS Certificate Mapping Issues in Windows Autopilot Hybrid Join Deployments

Microsoft Windows Autopilot streamlines device provisioning through Intune, allowing IT administrators to preconfigure new Windows devices with minimal hands-on effort. However, when combined with Hybrid Entra Join and PKCS certificate deployment, specific challenges arise—particularly with certificate mapping and authentication.

Hybrid Entra Join

During autopilot provisioning, administrators may also choose to join the device to their on-premises Active Directory domain, a deployment model called Hybrid Entra join. Hybrid Entra join presents some unique challenges when using Autopilot to remotely provision devices. Specifically, the user must have connectivity to a domain controller to perform the first logon, as they do not have a user profile on the endpoint.

Device Tunnel

To support offline Hybrid Entra join during Autopilot provisioning, administrators can deploy the Always On VPN device tunnel to provide pre-logon connectivity to domain controllers. A device tunnel connection enables users to log on to their newly provisioned device remotely.

Requirements

The following prerequisites must be met to support the Always On VPN device tunnel.

  • The endpoint must be running Windows Enterprise edition.
  • An Always On VPN device tunnel profile must be assigned to the device.
  • A machine certificate must be deployed to the endpoint that includes the Client Authentication EKU (OID 1.3.6.1.5.5.7.3.2).

Note: If you plan to use the subscription step-up upgrade from Windows Professional to Windows Enterprise, the device tunnel will not connect automatically after provisioning is complete, which prevents the user from logging in. More details and a workaround for this issue can be found here.

Strong Certificate Mapping

Microsoft knowledge base article KB5014754, released in May of 2022, introduced changes to domain controllers to require strong certificate mapping when using certificates to authenticate to Active Directory (AD). It was initially deployed in compatibility mode, only warning administrators when certificates are used for authentication that aren’t strongly mapped. However, full enforcement is mandatory beginning with the September 2025 security updates. This requirement introduces some challenges when issuing certificates to the device using PKCS during Autopilot provisioning.

Intune PKCS Certificates

When using PKCS certificates and the Intune Certificate Connector, the endpoint’s on-premises AD security identifier (SID) is not added to the issued certificate during Autopilot. Interestingly, this does not happen when using SCEP certificates. If the device certificate is not strongly mapped, the Always On VPN device tunnel will still authenticate successfully because Always On VPN does not use AD to authenticate device connections. Instead, Always On VPN simply verifies the certificate (e.g., that it is not expired or revoked) and allows authentication if the certificate passes the validation.

However, enterprise Wi-Fi access may fail without strongly mapped certificates if device authentication is required. Also, there may be other scenarios where a device authentication certificate without strong mapping may cause authentication to fail.

Workarounds

There are a few ways to work around this limitation. Consider the following options.

Native Entra ID Join

The simplest way to avoid the challenges of PKCS certificates and Hybrid Entra join is to avoid it altogether in favor of native Entra join. However, this may not be an option for everyone.

Use SCEP

For some reason, certificates issued with SCEP do not suffer from this limitation. In my testing, SCEP certificates are always strongly mapped. However, deploying SCEP certificates is much more complex than using PKCS. (Pro tip: Cloud PKI for Intune uses SCEP and requires no configuration! It’s definitely something to consider.)

Short-Lived Certificates

Another option is to deploy temporary, short-lived certificates (valid for only a few days) using PKCS to ensure the Always On VPN device tunnel works, and then deploy a permanent, long-term certificate post-deployment that includes the strong mapping. To do this, administrators can leverage dynamic group assignments in Intune. For example, the administrator can assign the short-lived certificate to an Autopilot Provisioning devices group and later assign a long-term certificate to the Hybrid Joined devices group.

Here’s an example of the dynamic group membership configuration.

Autopilot Provisioning Devices:

(device.devicePhysicalIDs -any (_ -contains “[ZTDId]”)) -and (device.deviceTrustType -ne “ServerAD”)

Hybrid Entra Join Devices:

(device.deviceTrustType -eq “ServerAD”)

In this configuration, the initial PKCS certificate is deployed without the strong mapping when the endpoint is enrolled to Autopilot but has not yet joined the domain. During this time, the endpoint will only be a member of the Autopilot Provisioning Devices group and will receive the short-lived, temporary certificate. Later, once the endpoint has successfully joined the domain, the device will move from the provisioning group to the Hybrid Entra Join Devices group. When this happens, a permanent, strongly mapped long-term certificate is enrolled on the device.

Manual Certificate Mapping

Certificates can be manually mapped via the altSecurityIdentities property of the computer object in AD. Obviously, this doesn’t scale well, so my good friend Steve Prentice published a PowerShell script to automate this process. You can find more details and the script here.

Summary

Windows Autopilot streamlines device provisioning with Intune, but Hybrid Entra Join introduces challenges when PKCS certificates lack strong mapping during initial deployment, potentially disrupting VPN and Wi-Fi authentication. Administrators can avoid this by switching to native Entra join or by using workarounds such as switching to SCEP, using short-lived certificates, or manually mapping certificates.

Additional Information

KB5014754 – Certificate-based authentication changes on Windows domain controllers

How To: Map a user to a certificate via all methods available in the altSecurityIdentities attribute

Hybrid Autopilot: Automating altSecurityIdentities

Configure Microsoft Entra hybrid join

Overview: Cloud PKI for Microsoft Intune

Certificate Connector for Microsoft Intune Agent Certificate Renewal Failure

The Certificate Connector for Microsoft Intune is a vital component that allows administrators to issue and manage enterprise PKI certificates to endpoints managed by Microsoft Intune. The connector is installed on a Windows server with access to the on-premises Certificate Authority (CA). It is registered with Intune and can be used by any PKCS or SCEP device configuration profiles defined by Intune administrators.

Agent Certificate

When you install the Certificate Connector for Intune, a certificate issued by the Microsoft Intune ImportPFX Connector CA is automatically enrolled into the local computer certificate store of the server where the connector is installed. This certificate authenticates the connector to Intune and is valid for one year from the date of issuance. This certificate is automatically renewed in most cases. However, some configurations prevent this from happening.

Failed To Renew

Administrators may find event log errors with event ID 2 from the CertificateConnectors source in the Microsoft-Intune-CertificateConnectors operational event log with the following information.

Pki Create Service:

Failed to renew agent certificate

System.Security.Cryptography.CryptographicException: Access is denied.

Root Cause

Agent certificate renewal fails when the Certificate Connector for Intune is running under a service account that is not a member of the local administrators security group. You will not encounter this error if the connector services are running in the SYSTEM context, however.

Resolution

There are a few different ways to resolve this issue. Here are some options to consider.

Grant Admin Rights

Adding the service account under which the connector service runs will allow the agent certificate to renew automatically. However, this may not be desirable from a security perspective. To address this, administrators may temporarily grant local administrative access to renew the agent certificate, then revoke this permission once the certificate has been successfully renewed. However, this is a manual process that doesn’t scale well and requires annual administrative intervention.

Reinstall

Uninstalling and reinstalling the Certificate Connector for Intune will force a new certificate enrollment during the registration process. You can delete the old certificate after completing the installation.

Switch to SYSTEM

Changing from a service account to SYSTEM will also resolve this issue. However, it is not recommended to make these changes directly on the services themselves. Instead, administrators should remove and reinstall the Certificate Connector for Intune, selecting the SYSTEM option rather than the service account method.

Note: Using the SYSTEM account for the Certificate Connector for Intune should be avoided when using PKCS. Details here.

Summary

The Certificate Connector for Intune agent certificate renewal fails when the service is configured to run as a service account without local administrative rights. The best way to resolve this is to add the service account to the local administrators group on the server where the connector is installed. However, this isn’t always ideal. Although running the connector in the SYSTEM context is acceptable when using SCEP, it should be avoided when using PKCS. Administrators will have to accept the risk of the service account having local administrative rights or accept that they’ll have to reinstall the connector annually.

Additional Information

Certificate Connector for Intune Service Account and PKCS

Strong Certificate Mapping for Intune PKCS and SCEP Certificates

Intune Strong Certificate Mapping Error

Intune PKCS and SCEP Certificate Validity Period

Certificate Connector for Intune Failure

Certificate Connector for Intune Configuration Failed

Troubleshooting Intune Failed PKCS Request

Always On VPN Servers and Failover

When configuring Microsoft Always On VPN, one of the first and most crucial settings is defining the public hostname of the VPN server to which clients connect. If you’re deploying Always On VPN client configuration settings using Intune—either with the native VPN policy template or a custom XML profile—you’ll see that multiple server entries are supported. Intune even allows administrators to define a “default server.” At first glance, this might suggest that the client will try the default server first and automatically fail over to the others if it’s unavailable. Unfortunately, that’s not how it works.

Intune VPN Template

When using the native Intune VPN device configuration template, administrators will find multiple entry fields for the servers in the Base VPN section.

In the example below, the Global VPN entry is marked as ‘default’.

Custom XML

When defining VPN settings using XML configuration, administrators can also list multiple servers.

Interestingly, the VPNv2 CSP used by custom XML profiles doesn’t support the concept of a “default server” at all.

How It Really Works

Defining multiple servers in the Always On VPN profile does not enable automatic failover. The client connects only to the first server in the list. The so-called “default server” setting in Intune is ignored, and the GUI even allows you to mark all servers as default, which is meaningless.

However, the configuration isn’t entirely useless. If you define multiple servers, they’ll appear on the client side as manual options. If the first server becomes unavailable, the user can open the Settings app, navigate to the advanced settings of the Always On VPN profile, and select an alternate server to connect manually.

Summary

Although Intune and XML configurations allow multiple VPN servers, Always On VPN does not provide automatic failover. Clients only attempt to connect to the first server in the list, and the “default server” setting in Intune has no effect. Multiple entries are still useful, but only for manual server selection by end-users when the primary server is down. For true automated high availability and redundancy, consider an external solution such as Azure Traffic Manager.

Additional Information

Always On VPN Load Balancing

Always On VPN Multisite with Azure Traffic Manager

Always On VPN DPC 5.2.0 Now Available

I’m pleased to announce that Always On VPN Dynamic Profile Configurator (DPC) version 5.2.0 is now available. My good friend Leo D’Arcy has been hard at work for the last few months squashing some bugs and adding a few new features to DPC. If you are running a previous release of Always On VPN DPC, either open source or commercial, it’s time to upgrade.

Important!! DPC 5.2.0 has a bug that prevents the service from stopping. This has been addressed in DPC 5.2.1. Guidance for upgrading from DPC 5.2.0 to 5.2.1 can be found here.

Reminder: We’re on Discord. Join the conversation today!

What’s New in DPC 5.2.0

Always On VPN DPC 5.2.0 has some compelling new features.

  • Exclude Routes from DNS – DPC has a feature that allows administrators to add routes to the routing table using DNS. When this setting is enabled, DPC will attempt to resolve the specified hostname to an IP address and add it to the VPN’s routing table when creating the profile. With 5.2.0, this capability has been extended to exclusion routes, allowing administrators to exclude resources by host name.
  • Write Event Logs to Disk – This setting allows administrators to optionally write DPC event information to a text file in addition to logging them in the event log. Writing event log information to a text file on disk can make troubleshooting easier in some scenarios.
  • Delay Profile Updates – This new feature ensures reliable VPN profile creation after group policy updates take place.

Bug Fixes

In addition to new capabilities, Always On VPN DPC 5.2.0 includes fixes for many outstanding issues.

  • DPC name resolution issue where duplicate IP addresses are returned, resulting in failed route additions when using ‘Allow Routes from DNS’.
  • Missing events in the DPC operational event log.
  • Enabling ‘Disable Disconnect Button’ or ‘Disable Advanced Edit Button’ settings results in a profile mismatch warning.
  • Added resiliency to DPC name resolution when one or more name resolution requests fail.

Group Policy Template

As a reminder, any time there are new features in DPC, there will be corresponding changes to Group Policy administrative template and template language files. Be sure to update your ADMX and ADML files in the group policy central store to take advantage of these new capabilities in DPC 5.2.0.

Recommendation

If you are running any release of Always On VPN DPC, commercial or open source, consider upgrading now to gain access to new features and operational reliability improvements. You can find DPC v5.2.0 on GitHub here.

Additional Information

Always On VPN DPC v5.2.0 Available Now

Always On VPN Dynamic Profile Configurator (DPC)

Always On VPN DPC Now Open Source

Migrating from Always On VPN DPC Commercial to Open Source

Always On VPN DPC with Microsoft Intune

Microsoft Always On VPN on Discord

Always On VPN DPC

Always On VPN and Entra Conditional Access

Microsoft recently introduced Entra Private Access, an identity-centric Zero Trust Network Access (ZTNA) solution to provide secure remote access to on-premises resources. With Entra Private Access, administrators can leverage Entra Conditional Access to enforce policy-based access control for network access. However, Entra Private Access isn’t for everyone. It does not provide full feature parity with Always On VPN, and there are also licensing considerations. However, for those organizations using Always On VPN, the good news is that you can integrate Entra Conditional Access with Always On VPN today to gain some of the security benefits it provides.

Conditional Access

Microsoft Entra Conditional Access is a security feature that enables administrators to create and enforce policies that specify how users can access resources. In the specific case of Always On VPN, conditional access is critical to ensuring legitimate access to authenticated users on authorized devices.

Signals

Conditional access policies use a wide variety of signals for policy enforcement, such as:

  • User Identity: Who is making this access request?
  • User Properties: Is this user a member of a specific group?
  • Location: Where is this access request originating?
  • Device Management: Is this device joined to Entra ID?
  • Device State: Is this device compliant with security policies?
  • Device Platform: Is this a Windows device?
  • Risk Level: Is this login considered risky?

Access Control

Based on these signals, administrators can design a conditional access policy to enforce granular access control, such as:

  • Grant access only from managed devices
  • Deny access from untrusted locations
  • Require additional context-based authentication (e.g., multifactor authentication)
  • Enforce specific authentication types (e.g., phishing-resistant credentials)
  • Allow access only from specific device platforms (e.g., Windows only)
  • Require Entra hybrid-joined device
  • Block access when a device is not compliant with security policies

Always On VPN

Entra Conditional Access works with Always On VPN by issuing a special, short-lived user authentication certificate once the user has been authorized. The Always On VPN infrastructure can be configured to use this certificate to grant access to the VPN. Integrating conditional access with Always On VPN can significantly improve the security posture of organizations using this feature.

Deployment Guide

I’ve published a detailed, step-by-step deployment guide to configure Entra conditional access for Always On VPN. In addition, I have posted a demonstration video for enabling Entra conditional access with Aways On VPN on YouTube.

Additional Information

Microsoft Entra Conditional Access Overview

Configure Entra Conditional Access for Always On VPN

Always On VPN DPC Open Source

Recently, I wrote about the demise of PowerON Platforms, the company behind the popular Always On VPN Dynamic Profile Configurator (DPC) software that allows administrators to deploy and manage Always On VPN client configuration settings using Active Directory Group Policy or Microsoft Intune with custom ADMX/ADML. Initially, the future of DPC was uncertain. However, I’m happy to announce that DPC will continue to be developed.

We’re on Discord! Join the conversation: https://discord.aovpndpc.com/.

DPC Open Source

The lead developer of DPC and my good friend Leo D’Arcy retained the source code for the product and has been working diligently to decommercialize the software. That work has been completed, and Always On VPN DPC is now available via open source. You can find the source code for DPC on GitHub here.

DPC Features

This initial open-source release (version 5.0.0) contains no significant new features or functionality. Most of the development efforts focused on removing references to PowerON Platforms (registry paths, binary names, etc.).

Support

Today, DPC support is community-based. You can report issues on the GitHub issues page for DPC. In addition, you can ask questions about DPC on Discord in the Microsoft Remote Access UG. Leo and I will monitor the group closely and answer any questions you might have there.

Deployment

If you’re not a DPC user today, I encourage you to have a look at its impressive feature set. Not only does DPC make Always On VPN deployment and management easier, but it also includes many advanced capabilities that will make connections more stable and reliable. Here are some links to articles outlining some of those advanced features.

Migration

If you already have a previous commercial release of Always On VPN DPC deployed, migrating to the new open-source DPC is straightforward. You will find guidance for migrating your existing DPC configuration here.

Contribute

Now that DPC is open source, we encourage everyone to contribute. If you have development skills, feel free to help. If you have feedback or feature requests, don’t hesitate to submit them!

Learn More

Are you interested in learning more about Always On VPN DPC? Would you like a personal demonstration of DPC’s features and capabilities? Do you need help migrating from a previous release to the new open-source software? Fill out the form below, and I’ll contact you with more information.

Additional Information

Always On VPN DPC

Always On VPN DPC Open Source on GitHub

PowerON Platforms Are No More