





 The Internet Key Exchange version 2 (IKEv2) VPN protocol is the protocol of choice when the highest level of security is required for Always On VPN connections. It uses IPsec and features configurable security parameters that allow administrators to adjust policies to meet their specific security requirements. IKEv2 is not without some important limitations, but organizations may insist on the use of IKEv2 to provide the greatest protection possible for remote connected clients. Due to complexities of the IKEv2 transport, special configuration on the Citrix ADC (formerly NetScaler) is required when load balancing this workload.
Special Note: In December 2019 a serious security vulnerability was discovered on the Citrix ADC that gives an unauthenticated attacker the ability to arbitrarily execute code on the appliance. As of this writing a fix is not available (due end of January 2020) but a temporary workaround can be found here.
Load Balancing IKEv2
When an Always On VPN client establishes a connection using IKEv2, communication begins on UDP port 500, but switches to UDP port 4500 if Network Address Translation (NAT) is detected in the communication path between the client and the server. Because UDP is connectionless, custom configuration is required to ensure that VPN clients maintain connectivity to the same backend VPN server during this transition.
Initial Configuration
Load balancing IKEv2 using the Citrix ADC is similar to other workloads. Below are specific settings and parameters required to load balance IKEv2 using the Citrix ADC.
Note: This article is not a comprehensive configuration guide for the Citrix ADC. It assumes the administrator is familiar with basic load balancing concepts and has experience configuring the Citrix ADC.
Service Settings
The load balancing services for IKEv2 VPN will use UDP ports 500 and 4500. Create the service group and assign group members for UDP 500 as follows.


Repeat the steps above to create the service group for UDP port 4500.
Virtual Server Settings
Two virtual servers are required, one for UDP port 500 and one for UDP port 4500. Ensure that the service group using UDP port 500 is bound to the virtual server using the same port.


Repeat the steps above to create the virtual service for UDP port 4500.
Service Monitoring
Since IKEv2 uses the UDP protocol, the only option for service monitoring is to use PING, which is configured by default. Ensure that the firewall on the VPN server allows inbound ICMPv4 and ICMPv6 Echo Request. The default PING monitor on the Citrix ADC will ping the resource every 5 seconds. If a different interval is required, the administrator can edit the PING monitor and bind that to the service or service group as necessary.
Persistency Group
A Persistency Group on the Citrix ADC will be configured to ensure that IKEv2 VPN client requests from the same client are always routed to the same backend server. Follow the steps below to create a Persistency Group and assign it to both IKEv2 virtual servers created previously.
- In the Citrix ADC management console expand Traffic Management > Load Balancing > Persistency Groups.
- Click Add.
- Enter a descriptive name for the Persistency Group.
- Select SOURCEIP from the Persistence drop-down list.
- Next to the Virtual Server Name section click the Add button.
- Add both previously configured IKEv2 virtual servers for UDP 500 and 4500.
- Click Create.

Use Client IP
To ensure reliable connectivity for IKEv2 VPN connections it is necessary for the VPN server to see the client’s original source IP address. Follow the steps below to configure the Service Group to forward the client’s IP address to the VPN server.
- In the Citrix ADC management console expand System, click Settings, and then click Configure Modes.
- Select Use Subnet IP.
- Click Ok.

- Expand Traffic Management, click Load Balancing, and then click Service Groups.
- Select the IKEv2 UDP 500 Service Group.
- Click Edit in the Settings section.
- Select Use Client IP.
- Repeat these steps on the IKEv2 UDP 4500 Service Group.

Note: Making the above changes will require configuring the VPN server to use the Citrix ADC as its default gateway.
Additional Information
Windows 10 Always On VPN IKEv2 Load Balancing and NAT
Windows 10 Always On VPN SSTP Load Balancing with Citrix NetScaler ADC
Windows 10 Always On VPN IKEv2 Features and Limitations
Windows 10 AlWAYS On VPN and IKEv2 Fragmentation
 The Internet Key Exchange version 2 (IKEv2) VPN protocol is the protocol of choice for Windows 10 Always On VPN deployments where the highest levels of security and assurance are required. However, as I’ve written about in the past, often the


 When deploying


 DirectAccess has been around for many years, and with Microsoft now moving in the direction of Always On VPN, I’m often asked “What’s the difference between DirectAccess and Always On VPN?” Fundamentally they both provide seamless and transparent, always on remote access. However, Always On VPN has a number of advantages over DirectAccess in terms of security, authentication and management, performance, and supportability.
 Windows 10 Always On VPN is infrastructure independent and can be implemented using third-party VPN devices. It is not necessary to deploy any Windows servers at all to support an Always On VPN solution. However, in a
 Windows 10 Always On VPN hands-on training classes now forming. Details


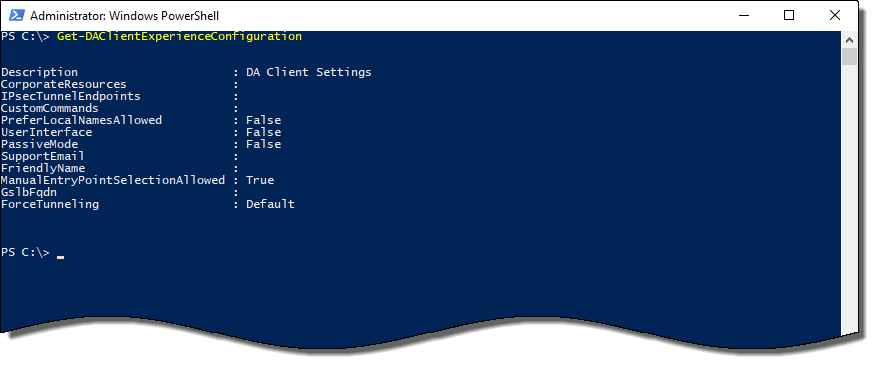
 Native PowerShell commands in Windows 10 make DirectAccess troubleshooting much easier than older operating systems like Windows 7. For example, with one PowerShell command an administrator can quickly determine if a DirectAccess client has received the DirectAccess client settings policy. In addition, PowerShell can be used to view the status of the connection and retrieve additional information or error codes that can be helpful for determining the cause of a failed connection. Further, PowerShell can also be used to review configuration details and perform other troubleshooting and connectivity validation tasks.



 DirectAccess is a thing of beauty when everything is working as it should. When it isn’t, troubleshooting can be quite challenging. DirectAccess relies on many Windows platform technologies such as Active Directory for authentication, PKI for certificate management, group policy for settings deployment, IPsec for encryption, and IPv6 for transport. With so many dependencies, locating the source of the problem can be a difficult and daunting task.


