Always On VPN Security Updates September 2026

Microsoft released the September 2026 security updates today, which include numerous fixes affecting Always On VPN deployments. This month’s edition addresses vulnerabilities in Windows Server Routing and Remote Access (RRAS), VPN protocols such as Secure Socket Tunneling Protocol (SSTP) and Internet Key Exchange version 2 (IKEv2). The updates also include Active Directory Certificate Services (AD CS), a crucial supporting infrastructure service for Always On VPN.

RRAS

September 2026 Microsoft security updates include 8 CVEs for RRAS. Four are rated Critical, the most severe having a CVSS rating of 9.8.

RCEs

The following four CVEs are Remote Code Execution vulnerabilities. All are rated critical.

Privilege Escalation

The following two CVEs are RRAS privilege escalation vulnerabilities. All are rated Important.

Denial of Service

Finally, the last CVE addresses a denial-of-service vulnerability in RRAS.

VPN Protocols

The following section outlines vulnerabilities addressed in the September 2026 security updates affecting commonly used VPN protocols.

SSTP

The following four CVEs cover vulnerabilities in SSTP. One is rated critical with a CVSS score of 9.8. The rest are rated Important.

IKEv2

The following CVEs address vulnerabilities in the IKEv2 VPN protocol. All are rated important.

AD CS

Microsoft AD CS is commonly deployed to issue and manage certificates used for encryption and user and device authentication in Always On VPN deployments. The following four CVEs address vulnerabilities disclosed in AD CS. The first two are privilege escalation vulnerabilities, the third covers information disclosure, and the last addresses a tampering vulnerability. All are rated Important.

Summary

The September 2026 Microsoft security updates address several critical vulnerabilities affecting organizations that have deployed Microsoft Always On VPN. Administrators are encouraged to update their systems as soon as possible.

Additional Information

Microsoft September 2026 Security Updates

Entra Internet Access TLS Inspection and Always On VPN: Troubleshooting SSTP Connection Failures

Microsoft Entra Global Secure Access (GSA) is a cloud-based Security Service Edge (SSE) solution that includes Entra Private Access to provide zero-trust network access to private data and applications, and Entra Internet Access to provide security controls for general internet access. Entra Internet Access includes features such as web content filtering, AI prompt controls, TLS inspection, and more. Entra Private Access and Entra Internet Access share a common client: the Global Secure Access Client.

TLS Inspection

TLS inspection is a powerful feature of Entra Internet Access that allows inspection and policy enforcement for encrypted internet traffic. It enables more thorough inspection and is required for features such as AI prompt policies. When TLS inspection is enabled, the TLS connection from the target server (origin server) is terminated by the Entra service. A new session is created between the cloud and the endpoint using a dynamically generated TLS certificate issued by Entra. As Entra holds the private key for this certificate, it can decrypt and inspect traffic as necessary.

Always On VPN

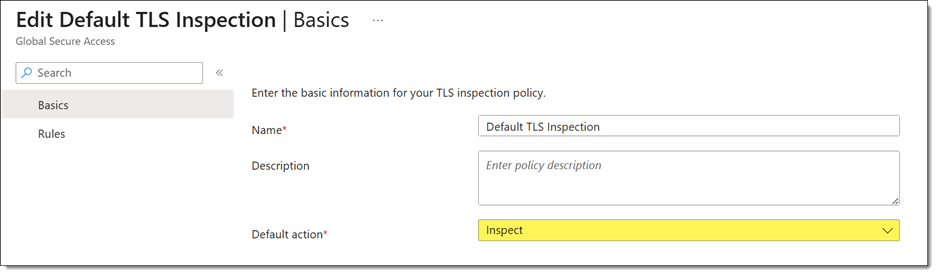
Recently, a customer asked me to help troubleshoot an Always On VPN user tunnel connectivity issue. The problem began shortly after deploying the Global Secure Access client with TLS inspection enabled. Administrators had configured the default TLS inspection policy to inspect traffic for all websites.

User Tunnel Failures

Attempts to manually start the Always On VPN user tunnel resulted in a failed connection attempt with the following error message.

Error 0x800704D4: The network connection was aborted by the local system.

Event Logs

Reviewing the client event logs revealed numerous Event ID 20227 entries from the RasClient source with the following error message.

The user DOMAIN\User dialed a connection named [connection name] which has failed. The error code returned on failure is -2147023660.

Note: Error code -2147023660 is the decimal equivalent of 0x800704D4.

Troubleshooting

Initial testing with Test-NetConnection confirmed that TCP port 443 on the VPN server was reachable. However, using Get-TlsCertificate revealed the real problem.

Although the certificate subject matched the VPN server, the issuer did not. Instead of the VPN server’s issuing CA, the certificate had been issued by Microsoft Entra Global Secure Access, confirming that TLS inspection was intercepting the connection.

SSTP and TLS Inspection

The Secure Socket Tunneling Protocol (SSTP) is a Microsoft proprietary VPN transport that uses HTTP for tunneling and TLS for security. Unlike a web browser, which can establish a new trusted TLS session with an inspection proxy, SSTP validates the VPN server’s certificate as part of establishing the VPN tunnel. Any certificate substitution, even by a trusted TLS inspection service, changes the server certificate thumbprint and causes SSTP validation to fail.

Workaround

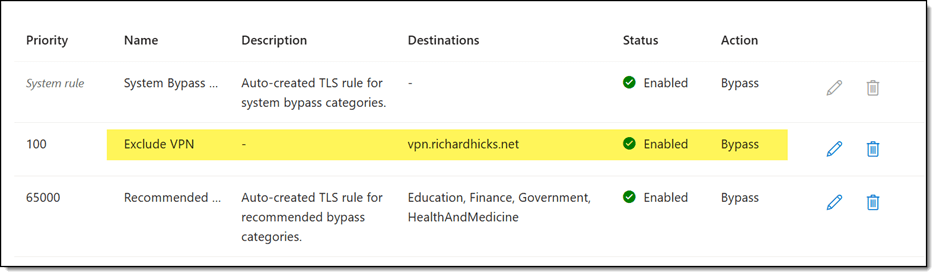
The solution is to create a TLS inspection exclusion policy to exempt inspection for the VPN server FQDN(s), as shown here.

Summary

Microsoft Entra Internet Access TLS inspection can unintentionally interfere with Always On VPN deployments that use SSTP. Because TLS inspection replaces the VPN server’s certificate with one issued by Microsoft Entra, SSTP detects the certificate mismatch and terminates the connection. If you use Always On VPN with Entra Internet Access, configure a TLS inspection exclusion for your VPN server FQDNs to prevent interception while preserving TLS inspection for general internet traffic.

Additional Information

Always On VPN vs. Entra Private Access: Choosing the Right Access Model for your Organization

What is Microsoft Entra Global Secure Access?

Microsoft Entra Internet Access

Microsoft Entra Private Access

Always On VPN SSTP and 47-Day TLS Certificates

Always On VPN SSTP and HSTS

Always On VPN Security Updates July 2026

Microsoft released the July 2026 Windows security updates today, including several fixes that directly affect Always On VPN deployments. This month’s release addresses vulnerabilities in the Secure Socket Tunneling Protocol (SSTP), Internet Key Exchange (IKE), and the Routing and Remote Access Service (RRAS), making it an important update for organizations using Always On VPN.

SSTP Remote Code Execution

The highest-priority issue for Always On VPN administrators is a Remote Code Execution (RCE) vulnerability affecting the Secure Socket Tunneling Protocol (SSTP). SSTP is commonly used for Always On VPN user tunnel connections. Because SSTP is, by design, exposed directly to the Internet, vulnerabilities affecting this protocol deserve immediate attention. Microsoft rates this vulnerability as Critical with a CVSS base score of 8.1.

CVE-2026-50694 – Windows SSTP Remote Code Execution Vulnerability

IKE Vulnerabilities

These vulnerabilities primarily affect IKE-based VPN connections and could allow an attacker to disrupt VPN connectivity using specially crafted packets. While Microsoft rates these vulnerabilities as Important rather than Critical, organizations should still plan to deploy these updates promptly.

CVE-2026-50721 – IKEv1 Denial of Service via RSA-SHA1 authentication payload

CVE-2026-50722 – IKEv2 Denial of Service via RSA-SHA1 authentication payload

CVE-2026-12413 – IKEv2 Denial of Service via malformed fragmentation

CVE-2026-50696 – IKE Protocol Denial of Service Vulnerability

RRAS Vulnerabilities

The July 2026 security updates also address several vulnerabilities in the Windows Server Routing and Remote Access Service (RRAS). All are rated Important by Microsoft.

CVE-2026-57096 – Windows RRAS Elevation of Privilege Vulnerability

CVE-2026-49791 – Windows RRAS Elevation of Privilege Vulnerability

CVE-2026-50451 – Windows RRAS Elevation of Privilege Vulnerability

Summary

The SSTP RCE vulnerability is particularly concerning because the service is typically exposed to the Internet and could allow an unauthenticated attacker to execute code remotely. Organizations should prioritize deployment of this update. The IKE and RRAS vulnerabilities are rated Important and can generally be addressed during the next scheduled maintenance window, although administrators should avoid unnecessary delays in applying these updates.