

Automating Entra App Proxy Certificates with CertKit (Client Secret)

Microsoft Entra ID icon

Microsoft Entra Application Proxy applications published with custom domains require a public TLS certificate, and keeping those certificates current is a manual, error-prone task when done in the Entra admin center. With the industry moving to 47-day public TLS certificates by 2029, automation is quickly becoming a requirement rather than a convenience. I recently configured CertKit to automatically deploy renewed certificates to my Entra App Proxy applications using an Entra app registration with client secret authentication. This configuration follows security best practices and enforces least privilege, granting CertKit only the access it needs to find App Proxy applications and update their certificates. The following sections describe how to configure it using both PowerShell and the Entra admin center. CertKit also supports managed identity authentication, which I’ll cover in a future post.

CertKit Deployment Options

CertKit can deploy a certificate to Entra App Proxy in one of two ways.

  • Individual applications. CertKit updates only the App Proxy applications you specify.
  • All applications. CertKit enumerates every App Proxy application in the tenant, determines which ones have an external URL covered by the certificate, and updates each of them.

If you choose to update all applications, be sure to use a wildcard or multi-SAN (subject alternative name) certificate that covers the external URL of every App Proxy application you want CertKit to manage. CertKit updates only applications whose external URL matches a name on the certificate, so a certificate with a single name updates only the application that uses that name. CertKit also skips Global Secure Access (Private Access) applications, such as Enterprise Quick Access. These applications appear alongside App Proxy applications, but they don’t use a TLS certificate, so there’s nothing to update.

Why 6-Day Certificates

In my lab, I’m using Let’s Encrypt’s short-lived 6-day certificates. Testing and evaluating certificate automation is much easier with short-lived certificates, because renewals happen every few days rather than every few months. Any problem with the renewal or deployment process shows up quickly, and I can confirm the automation works reliably across many renewal cycles in a short time. Short-lived certificates leave little margin for error, though, so I don’t recommend them in production until the automation is proven.

Required Permissions for CertKit

Create a dedicated Entra app registration for CertKit. CertKit uses this identity to sign in to Microsoft Graph, and it requires only the following permissions.

  • Application.Read.All. A read-only Microsoft Graph application permission CertKit uses to find App Proxy applications in the tenant.
  • A custom Entra role. A custom role, named App Proxy Certificate Manager in this example, with only three permissions: read Application Proxy settings, update the Application Proxy SSL certificate, and read connector groups.

This configuration enforces least privilege. Built-in roles such as Application Administrator also work, but they grant far more access than CertKit needs, including the ability to add credentials to any application in the tenant, a well-known privilege escalation path. With the custom role, CertKit can’t add credentials, change API permissions, or grant consent. Custom roles require Microsoft Entra ID P1, which is already required for Application Proxy. CertKit displays a warning that the identity has no Graph permission to update apps, but you can safely ignore it, because the custom role grants that access.

Configuration Using PowerShell

You can perform this configuration in a single run using my New-CertKitAppProxyIdentity.ps1 PowerShell script on GitHub, which creates the app registration, custom Entra role, Application.Read.All permission, role assignment, and client secret for CertKit. If your account has access to more than one tenant, use the -TenantId parameter to specify the tenant to configure. The script displays the connected tenant before making any changes. Alternatively, follow the manual steps below, which show exactly what the script does. Either way, you’ll need the Microsoft.Graph.Authentication module from the Microsoft Graph PowerShell SDK, since every call uses Invoke-MgGraphRequest. Install it using the following command.

Install-Module -Name Microsoft.Graph.Authentication -Scope CurrentUser

Connect to Microsoft Graph

First, connect to Microsoft Graph with an account that can create custom roles, grant application permissions, and assign directory roles, such as Privileged Role Administrator or Global Administrator. If your account has access to more than one tenant, add -TenantId with the tenant ID or domain name to sign in to the correct tenant.

Connect-MgGraph -Scopes 'Application.ReadWrite.All', 'AppRoleAssignment.ReadWrite.All', 'RoleManagement.ReadWrite.Directory' -NoWelcome

Create the App Registration

Next, create a dedicated app registration for CertKit. The command displays the application (client) ID, which CertKit needs later.

$NewApp = Invoke-MgGraphRequest -Method POST -Uri 'https://graph.microsoft.com/v1.0/applications' -Body @{ displayName = 'CertKit App Proxy Deployment'; signInAudience = 'AzureADMyOrg' }
$NewApp.appId

Create the Service Principal

App registrations created with Graph don’t get a service principal automatically, so create one. The role and API permission are assigned to the service principal, not the app registration.

$NewSp = Invoke-MgGraphRequest -Method POST -Uri 'https://graph.microsoft.com/v1.0/servicePrincipals' -Body @{ appId = $NewApp.appId }

Create the Custom Role

Now create a custom role that can only read Application Proxy settings and update the Application Proxy SSL certificate.

$RoleBody = @{
displayName = 'App Proxy Certificate Manager'
description = 'Can read Application Proxy settings and update the Application Proxy SSL certificate. Used by CertKit.'
isEnabled = $true
rolePermissions = @(@{
allowedResourceActions = @(
'microsoft.directory/applications/applicationProxy/read'
'microsoft.directory/applications/applicationProxySslCertificate/update'
'microsoft.directory/connectorGroups/allProperties/read'
)
})
}
$Role = Invoke-MgGraphRequest -Method POST -Uri 'https://graph.microsoft.com/v1.0/roleManagement/directory/roleDefinitions' -Body $RoleBody

Grant the Application.Read.All Permission

Next, grant the service principal the read-only Microsoft Graph application permission Application.Read.All. Assigning the permission this way also grants admin consent.

$GraphSp = (Invoke-MgGraphRequest -Method GET -Uri "https://graph.microsoft.com/v1.0/servicePrincipals?`$filter=appId eq '00000003-0000-0000-c000-000000000000'&`$select=id,appRoles").value[0]
$AppRoleId = ($GraphSp.appRoles | Where-Object { $_.value -eq 'Application.Read.All' -and $_.allowedMemberTypes -contains 'Application' }).id
$Grant = @{
principalId = $NewSp.id
resourceId = $GraphSp.id
appRoleId = $AppRoleId
}
Invoke-MgGraphRequest -Method POST -Uri "https://graph.microsoft.com/v1.0/servicePrincipals/$($NewSp.id)/appRoleAssignments" -Body $Grant

Assign the Custom Role

Now assign the custom role to the service principal, scoped to the entire tenant.

$Body = @{
'@odata.type' = '#microsoft.graph.unifiedRoleAssignment'
roleDefinitionId = $Role.id
principalId = $NewSp.id
directoryScopeId = '/'
}
Invoke-MgGraphRequest -Method POST -Uri 'https://graph.microsoft.com/v1.0/roleManagement/directory/roleAssignments' -Body $Body

If your tenant is licensed for Microsoft Entra ID P2 or Microsoft Entra ID Governance, assign the role through Privileged Identity Management (PIM) instead. Role assignments made outside PIM aren’t tracked by PIM and trigger a high-severity alert. Service principals support only active assignments in PIM, so the following command creates a permanent active assignment.

$Body = @{
action = 'adminAssign'
justification = 'CertKit certificate deployment to Entra Application Proxy'
roleDefinitionId = $Role.id
directoryScopeId = '/'
principalId = $NewSp.id
scheduleInfo = @{
startDateTime = (Get-Date).ToUniversalTime().ToString('o')
expiration = @{ type = 'noExpiration' }
}
}
Invoke-MgGraphRequest -Method POST -Uri 'https://graph.microsoft.com/v1.0/roleManagement/directory/roleAssignmentScheduleRequests' -Body $Body

Create the Client Secret

Finally, create a client secret. I’ve chosen a 1-year expiration, but you can choose a shorter or longer period as you see fit by changing the AddYears(1) value. For example, use AddMonths(6) for a 6-month expiration or AddYears(2) for 2 years. The secret is copied to the clipboard rather than displayed on screen, which keeps it out of console history and screen recordings. The secret value can’t be retrieved later, so paste it into CertKit right away.

$Params = @{
passwordCredential = @{
displayName = 'CertKit'
endDateTime = (Get-Date).AddYears(1).ToString('o')
}
}
$Secret = Invoke-MgGraphRequest -Method POST -Uri "https://graph.microsoft.com/v1.0/applications/$($NewApp.id)/addPassword" -Body $Params
$Secret.secretText | Set-Clipboard

After pasting the secret into CertKit, clear the clipboard.

Set-Clipboard -Value $null

Configuration Using the Entra Admin Center

The same configuration can be performed in the Microsoft Entra admin center using an account that can create custom roles, grant application permissions, and assign directory roles, such as Privileged Role Administrator or Global Administrator.

Create the App Registration

To begin, create the app registration. The admin center creates the service principal (enterprise application) automatically.

  1. Navigate to Entra ID > App registrations and click New registration.
  2. Enter CertKit App Proxy Deployment for the name.
  3. Select Accounts in this organizational directory only.
  4. Leave the redirect URI blank and click Register.
  5. On the Overview page, record the Application (client) ID and Directory (tenant) ID.
The Overview page of the CertKit App Proxy Deployment app registration, showing the Application (client) ID and Directory (tenant) ID.

Grant the Application.Read.All Permission

Next, grant the app registration the read-only Application.Read.All permission.

  1. In the app registration, navigate to API permissions. Select the delegated User.Read permission the admin center adds by default and click Remove permission, since CertKit doesn’t use it.
  2. Click Add a permission, then Microsoft Graph > Application permissions.
  3. Search for and select Application.Read.All, then click Add permissions.
  4. Click Grant admin consent for your tenant and click Yes.

Create the Client Secret

Next, create a client secret for CertKit to authenticate with. I’ve chosen a 1-year expiration, but you can choose a shorter or longer period as you see fit.

  1. In the app registration, navigate to Certificates & secrets > Client secrets and click New client secret.
  2. Enter CertKit for the description and select 365 days (12 months) for the expiration.
  3. Click Add, then copy the Value immediately. Don’t copy the Secret ID. The value is displayed only once.

Create the Custom Role

Now create the custom role.

  1. Navigate to Entra ID > Roles & admins and click New custom role.
  2. Enter App Proxy Certificate Manager for the name, add a description, and click Next.
  3. On the Permissions page, search for and select microsoft.directory/applications/applicationProxy/read, microsoft.directory/applications/applicationProxySslCertificate/update, and microsoft.directory/connectorGroups/allProperties/read, then click Next.
  4. Review the settings and click Create.

Assign the Custom Role

Finally, assign the custom role to the new identity.

  1. Navigate to Entra ID > Roles & admins, then search for and select App Proxy Certificate Manager.
  2. Click Add assignments, then Select member(s).
  3. Search for CertKit App Proxy Deployment, select it, and click Select.
  4. If Privileged Identity Management (PIM) is enabled, click Next, set the assignment type to Active and Permanently assigned, enter a justification, and click Assign. Without PIM, click Add.
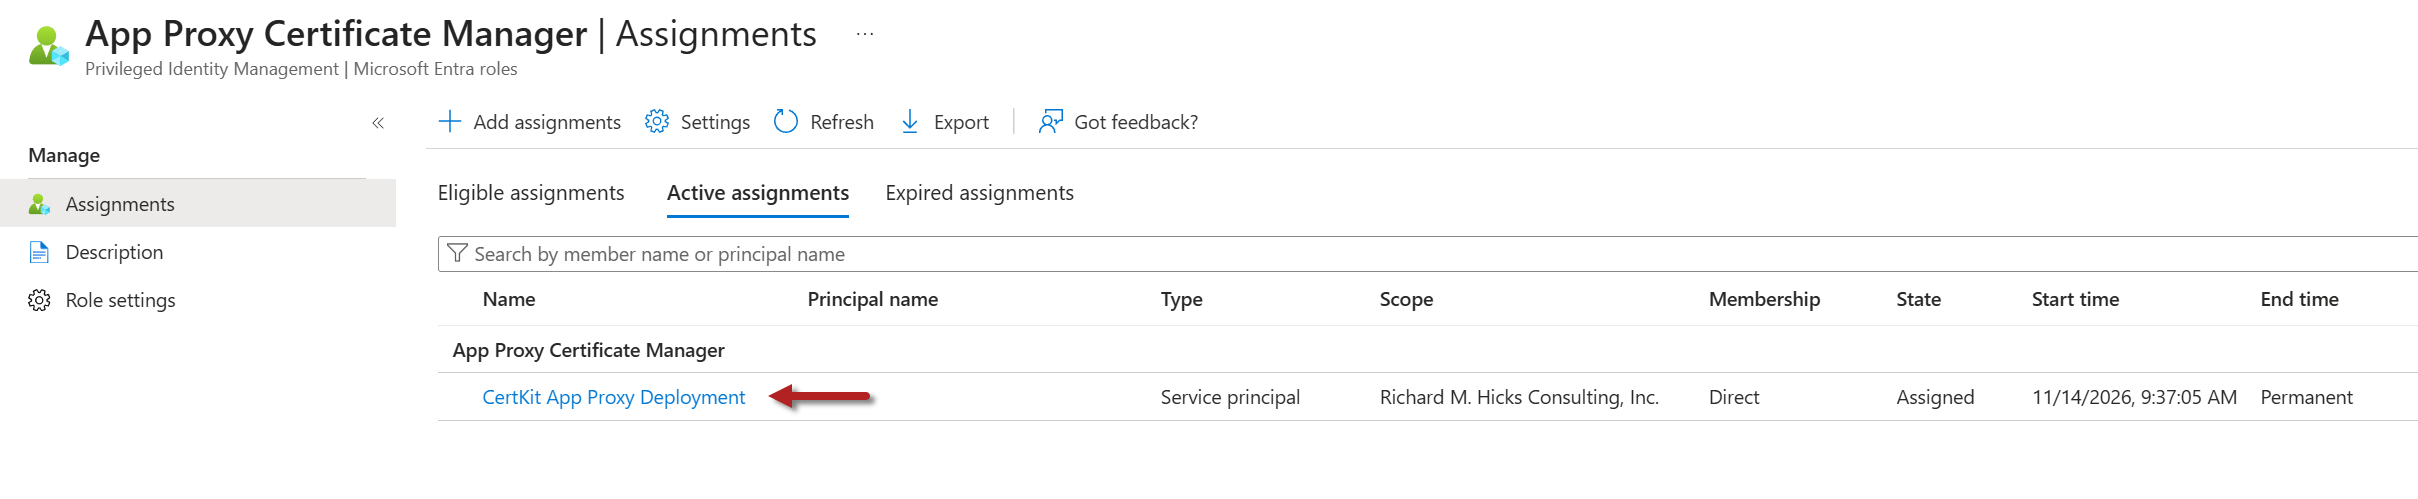
The App Proxy Certificate Manager role's Active assignments tab in Privileged Identity Management, showing CertKit App Proxy Deployment permanently assigned as a service principal.

Configure CertKit

With the app registration in place, create a new deployment in CertKit using the Microsoft Entra Application Proxy (Client Secret Auth) template. Select the certificate to deploy, and enter the directory (tenant) ID, application (client) ID, and client secret from the app registration. Then list the App Proxy applications to update by name, separated by commas, or enter an asterisk (*) as an app list wildcard to update all of them.

A CertKit deployment using the Microsoft Entra Application Proxy (Client Secret Auth) template, with the wildcard set to update all App Proxy applications.

Deploy and Validate

After saving the CertKit deployment and deploying the changes, wait a few minutes for the role assignment and API permission to take effect, then run the deployment. A successful run lists each App Proxy application, whether its external URL is covered by the certificate, and the thumbprint Entra reports after the update.

Update command output:
Microsoft Entra Application Proxy Deployment | Apps: *
[Step 1] Reading certificate...
Certificate: | Thumbprint: <redacted> | Expires: 2026-11-21
Covers: *.example.net, example.net
[Step 2] Signing in to Microsoft Graph...
Signed in as the app registration <redacted> (tenant <redacted>)
Graph permissions: Application.Read.All
Warning: The identity has no Microsoft Graph permission to update apps. Unless an Entra role allows it, uploads will be refused. Grant the application permission Application.ReadWrite.OwnedBy (admin consented) and add the identity as an owner of each App Proxy app.
[Step 3] Finding App Proxy apps...
Found 7 App Proxy app(s)
App1 (https://app1.example.net/): covered by this certificate
Private Access App: skipped, a Global Secure Access (Private Access) app, which has no TLS certificate
App2 (https://app2.example.net/): covered by this certificate
App3 (https://app3.example.net/): covered by this certificate
App4 (https://app4.example.net/): covered by this certificate
App5 (https://app5.example.net/): covered by this certificate
App6 (https://app6.example.net/): covered by this certificate
[Step 4] Uploading certificate...
App1 (https://app1.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
App2 (https://app2.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
App3 (https://app3.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
App4 (https://app4.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
App5 (https://app5.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
App6 (https://app6.example.net/): updated (Entra reports thumbprint <redacted>, expires 2026-11-21)
DONE | Updated 6 app(s), 0 already had the certificate. Entra takes a minute or two to start serving it.

Validate the Entra Configuration

To confirm Entra stored the new certificate, open the application in Entra ID > Enterprise applications and select Application proxy, or query the application’s App Proxy settings with PowerShell. Replace <objectId> with the app registration’s object ID.

The SSL certificate pane of an App Proxy application, showing the certificate's subject, thumbprint, and expiration date.
$Uri = "https://graph.microsoft.com/beta/applications/<objectId>?`$select=onPremisesPublishing"
(Invoke-MgGraphRequest -Method GET -Uri $Uri).onPremisesPublishing.verifiedCustomDomainCertificatesMetadata.thumbprint

Validate the Live Endpoint

App Proxy can take several minutes to begin serving the new certificate after the configuration is updated. To check the certificate the endpoint is actually serving, view it in a browser or use my Get-TlsCertificate PowerShell script.

Get-TlsCertificate is available in the PowerShell Gallery and on GitHub. Install it using the following command.

Install-Script -Name Get-TlsCertificate

Once installed, run it against the application’s external hostname.

Get-TlsCertificate -Hostname app1.example.net
Output of Get-TlsCertificate showing the certificate served by the App Proxy endpoint, including its issuer, thumbprint, expiration date, and subject alternative names.

The expiration date CertKit displays may differ by one day from the date Entra reports. That’s expected, because Entra reports dates in UTC.

Secret Rotation and Security

The client secret must be rotated before it expires, or CertKit deployments will fail. To rotate it, create a new secret on the app registration, update CertKit with the new value, confirm a deployment succeeds, and then delete the old secret. Set a calendar reminder well ahead of the expiration date. Least privilege limits the impact if the secret is ever exposed. Anyone holding it could replace the TLS certificate on App Proxy applications and read app registration details, but couldn’t add credentials to other applications, change permissions, or grant consent. Even so, store the secret securely and limit who can access it.

Summary

CertKit can fully automate certificate deployment to Entra Application Proxy, either for individual applications or for every App Proxy application in the tenant. By combining a custom Entra role limited to App Proxy certificate updates with the read-only Application.Read.All permission, this configuration follows security best practices and enforces least privilege, without the broad access of built-in roles such as Application Administrator. Using short-lived 6-day certificates makes it easy to confirm the automation works, and rotating the client secret before it expires keeps the deployment running.

Getting Started with CertKit

Need help automating TLS certificate deployment for Entra Application Proxy, Always On VPN, DirectAccess, IIS, SQL, and more? I can help you design and implement a secure, least-privilege certificate automation strategy with CertKit across your internal and public-facing workloads. Fill out the form below, and I’ll provide you with more information.

← Back

Thank you for your response. ✨

Additional Information

WEBINAR: Preparing for 100-Day Certificates with CertKit

Join me and the CertKit team on Tuesday, October 6, 2026, at 9:00 AM PDT for a free, live webinar about the upcoming reduction in public TLS certificate lifetimes. Beginning March 15, 2027, the maximum validity period for public TLS certificates will be reduced to 100 days. This change will make manual certificate management increasingly difficult for many organizations.

Automation

Shorter certificate lifetimes require organizations to identify, enroll, deploy, and renew certificates more frequently. Automation can help reduce the administrative effort and the risk of service interruptions caused by expired certificates. This is especially important for public-facing Microsoft workloads such as Internet Information Services (IIS), Remote Desktop Services (RDS), Always On VPN, DirectAccess, and other services that use public TLS certificates.

Visibility

Effective certificate management begins with knowing which certificates exist, where they are installed, and when they expire. Without this visibility, organizations may overlook certificates until they are close to expiration or have already expired.

Internal Certificates

Certificates issued by a private certification authority (CA) aren’t subject to the lifetime restrictions imposed on public TLS certificates. However, they still require inventory, monitoring, and renewal. A consistent approach to managing public and private certificates can help reduce operational overhead.

How CertKit Helps

CertKit is a cloud-based service for managing public and private TLS certificates. During the webinar, we’ll demonstrate how CertKit provides visibility into certificate inventories and expiration dates while automating common lifecycle tasks such as enrollment, deployment, and renewal. We’ll also review recent additions to the service.

Register Now

The webinar takes place on Tuesday, October 6, at 9:00 AM PDT. Registration is required. Everyone who registers will be notified when the session recording is available.

Intranet Certificate Monitoring with CertKit

CertKit is a cloud-based solution that automates the issuance and management of public TLS certificates. It also provides certificate monitoring and alerting for public-facing workloads. However, many organizations have internal (non-public-facing) services that also use TLS. CertKit agent v1.13.0, currently in preview, closes this gap by providing visibility into TLS certificates used by intranet resources. After installing the latest release of the agent, CertKit can now provide visibility into the status of TLS certificates for internal resources.

Intranet Monitoring

After installing or updating the CertKit agent to v1.13.0, administrators can select an internal TLS service to monitor. Follow the steps below to enable this feature.

Certificate Collection

I recommend creating a separate Certificate Collection to support intranet monitoring. In the CertKit management console, click Add Collection, enter a unique, descriptive name, and click Add Collection.

Install the Agent

Once the new collection is created, navigate to the Agents tab, select your platform, then download, install, and register the agent.

Monitor New Host

After the agent is installed and registered, navigate to the Monitoring tab and click Monitor New Host. Enter the fully qualified domain name (FQDN) of the resource and specify its TLS port. Under Host Visibility, select Internal, and then choose the agent to monitor the host from. When finished, click Monitor Host.

Note: The server running the CertKit agent does not require a TLS certificate of its own to monitor internal resources.

Monitored Hosts

CertKit can track certificates for any internal workload that uses TLS. In this example, the monitored resources include web applications, security appliances, load balancers, and HTTP CRL distribution points. The list also includes LDAPS on the domain controllers and the RDP and WinRM HTTPS services on the management workstation.

The circle next to each resource indicates its certificate status. Green indicates a healthy certificate, yellow indicates one approaching expiration, and red indicates an expired certificate or another detected issue.

Note: The RDP certificate on the management workstation appears red because it contains only the Remote Desktop Authentication EKU (1.3.6.1.4.1.311.54.1.2). It intentionally does not include Server Authentication, which CertKit currently expects when validating the service. CertKit is aware of this limitation and plans to address it in a future release.

Host Discovery

CertKit provides robust discovery for public websites but does not currently offer equivalent functionality for intranet resources. Administrators can identify internal systems listening on a specific port by using Nmap.

nmap.exe -Pn -p [port] --open [internal subnet]

For example:

nmap.exe -Pn -p 443 --open 172.16.0.0/24

Alternatively, add the -oX switch to save the output in XML format.

nmap.exe -Pn -p 443 --open 172.16.0.0/24 -oX scan.xml

The resulting Nmap XML file output can be converted to CSV format using this PowerShell code.

Summary

CertKit agent v1.13.0 extends certificate monitoring to internal TLS services, giving administrators greater visibility into certificates that were previously difficult to track. Although intranet host discovery remains a manual process, tools such as Nmap and PowerShell can help identify resources to add to the monitoring platform

Getting Started with CertKit

Need help improving certificate visibility and management across your organization? Want to automate public TLS certificate enrollment for workloads such as DirectAccess, Always On VPN, IIS, SQL, and more? I can help you assess your certificate environment, identify monitoring gaps, and develop a strategy for managing certificates across internal and public-facing workloads. Fill out the form below, and I’ll provide you with more information.

← Back

Thank you for your response. ✨

Additional Information

CertKit Website

What Is CertKit?

CerKit Agent Support for Always On VPN SSTP and DirectAccess IPHTTPS TLS Certificates

IIS TLS Certificate Deployment with CertKit

The Case for 6-Day Public TLS Certificates

DirectAccess IPHTTPS and Let’s Encrypt 6-Day TLS Certificates

Webinar: Certificate Automation in Practice – A Technical Deep Dive

If you manage Windows Server workloads that require public TLS certificates like Always On VPN, DirectAccess, Remote Desktop Gateway, Internet Information Services (IIS), and others, you know that certificate expirations don’t send friendly reminders. Certificates expire quietly. Too often, end users are the ones who sound the alarm—when resources are already unavailable. Of course, this never happens at a convenient time. It’s usually the middle of the night, on the weekend.

Missed the event? Watch the on-demand replay here.

Current State

Most Windows IT teams are still managing certificates the same way they did years ago, using spreadsheets, calendar reminders, and an assortment of renewal scripts. It usually works… until it suddenly doesn’t.

Free Webinar

I’m pleased to announce that I’ll be joining Todd Gardner from CertKit for a free live webinar on Tuesday, June 16, at 11:00 AM CDT, in which we will break down the following:

  • Why certificate mismanagement causes so much pain at scale
  • How to build real automation that works across your full environment, including internal services and vendor appliances
  • A live demonstration of CertKit showing end-to-end discovery, monitoring, and automated renewal

There will also be time for live Q&A, so bring your questions!

Join Us!

If you’re tired of patching the problem with fragile scripts and assorted reminders, join us to learn about a fully automated solution that can dramatically improve the situation. Register now and don’t miss this opportunity to reduce your TLS certificate management burden and end the need for 2 AM certificate renewal fire drills.

Webinar Details

Webinar: TLS Certificate Automation for Windows Infrastructure
Hosts: Todd Gardner (CertKit) and Richard Hicks (Richard M. Hicks Consulting, Inc.)
Date: Tuesday, June 16
Time: 11:00 AM CDT
Registration: Click here to register!

Recording

If you are unable to attend the live session, be sure to register to receive a link to the recorded session for on-demand viewing.

Webinar: Certificate Automation for Windows Infrastructure

If you manage Windows Server workloads that require public TLS certificates like Always On VPN, DirectAccess, Remote Desktop Gateway, Internet Information Services (IIS), and others, you know that certificate expirations don’t send friendly reminders. Certificates expire quietly. Too often, end users are the ones who sound the alarm—when resources are already unavailable. Of course, this never happens at a convenient time. It’s usually the middle of the night, on the weekend.

Did you miss the webinar? You can view it on demand here!

Current State

Most Windows IT teams are still managing certificates the same way they did years ago, using spreadsheets, calendar reminders, and an assortment of renewal scripts. It usually works… until it suddenly doesn’t.

Free Webinar

I’m pleased to announce that I’ll be joining Todd Gardner from CertKit for a free live webinar on Tuesday, May 26, at 11:00 AM CDT, in which we will break down the following:

  • Why certificate mismanagement causes so much pain at scale
  • How to build real automation that works across your full environment, including internal services and vendor appliances
  • A live demonstration of CertKit showing end-to-end discovery, monitoring, and automated renewal

There will also be time for live Q&A, so bring your questions!

Join Us!

If you’re tired of patching the problem with fragile scripts and assorted reminders, join us to learn about a fully automated solution that can dramatically improve the situation. Register now and don’t miss this opportunity to reduce your TLS certificate management burden and end the need for 2 AM certificate renewal fire drills.

Webinar Details

Webinar: TLS Certificate Automation for Windows Infrastructure
Hosts: Todd Gardner (CertKit) and Richard Hicks (Richard M. Hicks Consulting, Inc.)
Date: Tuesday, May 26
Time: 11:00 AM CDT
Registration: Click here to register!

Recording

If you missed the live event, you can view the on demand recording here!

IIS TLS Certificate Deployment with CertKit

With public TLS certificate lifetimes shrinking to just 47 days by 2029, administrators must find ways to automate certificate enrollment and renewal for workloads that require them. One of the most common is Microsoft Internet Information Services (IIS). I’ve been using CertKit.io to handle this process for workloads like Always On VPN and DirectAccess, so it made sense to migrate my public-facing IIS servers to this solution as well. The migration went smoothly, but I encountered an unexpected issue when deploying a new IIS server using CertKit.

CertKit Agent

CertKit Agents make loading certificates on the server a breeze. The CertKit agent automatically detects installed software (e.g., Terminal Services, RRAS, DirectAccess, IIS, etc.) and handles the server-side process of assigning the TLS certificate to the application. For RRAS and DirectAccess, it works perfectly. For an IIS server with an HTTPS binding and TLS certificate already configured, it works without issue as well. However, I ran into a snag when I tried to deploy a certificate to a brand-new IIS server.

New Server

After installing the CertKit agent on an IIS server, it searches for existing HTTPS web bindings to identify the workload. However, on a freshly installed IIS server, no HTTPS bindings have been configured yet, so the agent doesn’t recognize the IIS workload.

Of course, you could create an HTTPS web binding before installing the agent, but you’ll need a TLS certificate first. This introduces the classic “chicken and egg” scenario. 🤪 Fortunately, there are a few ways to resolve the issue.

Windows Certificate Store

With this method, you configure the CertKit agent to download and install the certificate into the local computer certificate store on the IIS server. Once complete, you can create the HTTPS binding in the IIS Manager console or by using PowerShell. After that, restart the CertKit agent service by running the following PowerShell command.

Restart-Service -Name certkit-agent -PassThru

The IIS workload will now appear in the agent’s Software list. At that point, you can delete the Windows certificate store configuration and replace it with the IIS configuration.

Self-Signed Certificate

Using this method before installing the CertKit agent allows the agent to automatically discover IIS after installation, which can be helpful when deploying IIS servers programmatically. First, create a short-lived certificate (one day in this example) and configure the IIS site binding by running the following PowerShell commands.

$Hostname = 'www.example.net'
$Certificate = New-SelfSignedCertificate -DnsName $Hostname -CertStoreLocation 'Cert:\LocalMachine\My' -KeyAlgorithm RSA -KeyLength 2048 -HashAlgorithm SHA256 -NotAfter (Get-Date).AddDays(1) -TextExtension @('2.5.29.37={text}1.3.6.1.5.5.7.3.1')
$Params = @{
    Name                 = 'Default Web Site'
    BindingInformation   = '*:443:'
    Protocol             = 'https'
    CertificateThumbPrint = $Certificate.Thumbprint
    CertStoreLocation    = 'Cert:\LocalMachine\My'
}
New-IISSiteBinding @Params

Once complete, run iisreset.exe to apply the changes. Now, when you install the CertKit agent, it will automatically detect IIS, and you can assign your public TLS certificate accordingly. You can delete the old self-signed certificate later if desired.

Summary

If you’re automating server builds, the self-signed certificate approach is typically the easiest because it enables IIS discovery immediately. For ad-hoc deployments, installing to the Windows certificate store first is usually the quickest option.

Additional Information

CertKit.io

CerKit Agent Support for Always On VPN SSTP and DirectAccess IP-HTTPS TLS Certificates

DirectAccess IPHTTPS and Let’s Encrypt 6-Day Certificates

I’ve written extensively about how public TLS certificate lifetimes will drop to just 47 days by March 2029. Before then, we’ll see certificate lifetimes gradually drop from the current 398 days to 200 days on March 15, 2026, and then to 100 days on March 15, 2027. In preparation for this, I’ve been working with many customers to deploy automated certificate enrollment and renewal solutions to eliminate the need for manual intervention. Interestingly, Let’s Encrypt now offers extremely short-lived certificates that are good for just 6 days! While they work just fine for Always On VPN, I discovered they will not work for DirectAccess.

6-Day Certificate

After successfully enrolling for a 6-day TLS certificate from Let’s Encrypt (I used CertKit, BTW!), I encountered an error when trying to assign the short-lived certificate to the IP-HTTPS listener in the DirectAccess configuration. Specifically, when running the Set-RemoteAccess PowerShell command, I received the following error.

Set-RemoteAccess: The parameter is incorrect.

Further investigation showed that I could install other public TLS certificates just fine. For some reason, though, DirectAccess did not like this new 6-day certificate.

Missing Subject Name

After digging a bit deeper, I realized the Subject field of the new 6-day Let’s Encrypt certificate was empty.

Subject vs. SAN in Modern TLS

Modern TLS clients rely entirely on the Subject Alternative Name (SAN) field for identity validation, and the older practice of matching against the certificate’s Subject field has been phased out for many years. Many certificate authorities, including Let’s Encrypt, now leave the Subject field empty because it no longer serves a functional purpose in current TLS implementations. DirectAccess still expects this field to contain data and does not properly fall back to SAN‑only validation. As a result, any certificate with an empty Subject field, such as the new 6‑day certificates from Let’s Encrypt, will fail when applied to the DirectAccess IP‑HTTPS listener.

Workaround

Admittedly, using 6-Day public TLS certificates for DirectAccess is extreme and likely overkill for this workload. The good news is that DirectAccess still works perfectly with 90-day Let’s Encrypt certificates, so the lack of 6-day certificate support should not be impactful.

CertKit

Have you heard about CertKit? CertKit, an online service for automating Let’s Encrypt certificate enrollment and renewal, has added support for Always On VPN and DirectAccess. Find details on leveraging it for public TLS certificates for these solutions here.

Additional Information

Always On VPN SSTP with Let’s Encrypt Certificates

Always On VPN and 47-Day Public TLS Certificates

The Case for Short-Lived Certificates in Enterprise Environments

CertKit Agent Support for Always On VPN SSTP and DirectAccess IP-HTTPS TLS Certificates

CertKit Agent Support for Always On VPN SSTP and DirectAccess IP-HTTPS TLS Certificates

With public TLS certificate lifetimes set to drop to 200 days soon (next week!), Always On VPN and DirectAccess administrators face an increased risk of service disruption if certificates aren’t renewed on time. These shorter certificate lifetimes require more frequent renewals, substantially increasing management overhead. Although 200 days equate to roughly a twice-a-year renewal, lifetimes will decrease further to 100 days next year and eventually to just 47 days in 2029. SSTP and IP-HTTPS are TLS-based tunneling protocols used by Always On VPN and DirectAccess, respectively, tying their certificate health directly to remote access availability. Now is the time to automate the enrollment and renewal of Always On VPN SSTP and DirectAccess IP-HTTPS/TLS certificates to ensure reliable operation in the future.

Always On VPN

Previously, I wrote about using CertKit.io to automate the enrollment and renewal of public TLS certificates for Always On VPN. CertKit is an online service that administrators can use to delegate the task of enrolling for short-lived certificates from Let’s Encrypt. In that post, I shared some sample code to retrieve the certificate from CertKit and assign it to the SSTP listener for the Routing and Remote Access Service (RRAS). However, CertKit added new features to its solution, eliminating the need for additional code.

CertKit Agents

Recently, CertKit introduced CertKit Agents. These lightweight software agents are installed on Windows Servers (other operating systems are supported as well) to automate the process of downloading CertKit certificates and installing them in the local computer certificate store. Importantly, they now specifically support both the Always On VPN (SSTP) and DirectAccess (IP-HTTPS) workloads natively.

Always On VPN

The CertKit agent automatically detects the Routing and Remote Access (RRAS) workload and updates the certificate binding for the SSTP listener accordingly. Since this process requires a service restart, which terminates all current VPN connections, CertKit allows you to select an outage window for certificate updates.

Here, administrators can define the day(s) and time window during which the agent is authorized to restart the RemoteAccess service when updating the TLS certificate for SSTP. The day and time are based on the server’s configured time zone settings.

DirectAccess

Beginning with CertKit agent v1.6.2, the agent automatically detects whether DirectAccess is configured, enabling IP-HTTPS TLS certificates to be automatically enrolled and renewed. However, additional configuration is required. The following changes must be made to support CertKit for DirectAccess.

  • Service Account – Administrators must configure a service account in Active Directory for the CertKit agent. A Group Managed Service Account (gMSA) is preferred, but a standard domain service account is also supported.
  • GPO Delegation – CertKit service account must be delegated the ‘Edit settings, delete, and modify security’ permission on the DirectAccess server and client settings GPOs.
  • Log On as a Service – When using a domain service account, administrators must grant the CertKit service the ‘Log on as a service’ right on the DirectAccess server. However, when using gMSA, the ‘Log on as a service’ right is not required.
  • Local Administrator – Administrators must also add the CertKit agent service account to the Local Administrators group on the server.

Configuration Script

I have published a PowerShell script to simplify configuring the CertKit agent on DirectAccess servers. The script automatically performs all required tasks for the CertKit agent to work with DirectAccess. You will find the Enable-DACertKit.ps1 PowerShell script on GitHub. Alternatively, you can install the script directly from the PowerShell Gallery.

Install-Script -Name Enable-DACertKit -Scope CurrentUser

After installing the CertKit agent, run the PowerShell script to complete the configuration. Next, authorize the agent in the CertKit management portal and assign a certificate. Once complete, CertKit can fully manage the IP-HTTPS TLS certificate for DirectAccess.

Note: Like Always On VPN, changes to the DirectAccess IP-HTTPS certificate require a service restart, which is disruptive. Be sure to define a maintenance window (as shown previously) to ensure the change is made during non-peak times.

Summary

As TLS certificate lifecycles continue to shrink, automating certificate enrollment and renewal has become essential for both Always On VPN and DirectAccess environments. CertKit agents streamline this process by automatically retrieving, installing, and binding certificates for SSTP and IP-HTTPS, all while supporting scheduled outage windows to minimize disruption. With these new capabilities, administrators can significantly reduce operational overhead and ensure consistent, reliable remote access services without manual intervention. Visit CertKit.io to get started today.

More Information

If you would like to learn more about CertKit or see a demonstration with Always On VPN or DirectAccess, fill out the form below, and I’ll provide you with more details.

Additional Information

Always On VPN SSTP Certificate Automation with CertKit

CertKit Agents

Enable-DACertKit.ps1 on GitHub

Enable Group Managed Service Accounts

Always On VPN SSTP Certificate Automation with CertKit

With public TLS certificates moving to significantly shorter certificate lifetimes, eventually just 47 days, Always On VPN administrators supporting Secure Socket Tunneling Protocol (SSTP) connections must prepare to address this eventuality. The first milestone for shortened public TLS certificate lifetimes is a few months, on March 15, 2026, when public TLS certificate lifetimes will be reduced from a maximum of 398 days to 200 days. One year later, on March 15, 2027, they will be reduced to just 100 days. Now is the time to begin planning an automated certificate enrollment solution to reduce administrative overhead and ensure uninterrupted connectivity for remote users.

Previous Approaches: PowerShell and Posh-ACME

In the past, I’ve written about using Let’s Encrypt Certificates for Always On VPN using the Posh-ACME PowerShell module. I’ve also posted some sample code to demonstrate how to integrate with a DNS provider to automate publishing the ACME challenge to public DNS for certificate enrollment verification. However, this assumes your DNS provider supports this option. Some do not. In addition, granting write permissions to public DNS via an API key introduces significant security risks. So, if direct ACME DNS automation isn’t viable in your environment, CertKit is an excellent alternative.

CertKit: Automated Certificate Issuance, Monitoring, and Alerting

To address these limitations, administrators can use the CertKit service. With CertKit, you delegate the Let’s Encrypt certificate enrollment process to them by simply creating a CNAME record in your public DNS. Once complete, CertKit handles the entire process transparently.

Issuance

Today, CertKit supports issuing certificates using Let’s Encrypt. In the future, support for additional certificate providers such as Google Trust and ZeroSSL will be added. CertKit supports Let’s Encrypt certificates using RSA (2048-bit) and Elliptic Curve (recommended). Certificates can be issued for an individual resource, a group of resources (multi-SAN), and a domain wildcard (e.g., *.example.net).

Monitoring

In addition to certificate issuance and management, CertKit offers domain TLS certificate monitoring to track your public assets. You can monitor your CertKit-managed certificates easily, but you can also add other services using TLS and track them on the same console. In this example, I’m using CertKit to manage certificates for two VPN servers (indicated by solid green dots) and to monitor my public websites, for which certificate management is handled by their respective hosting providers.

Alerts and Notifications

CertKit will automatically send emails to let you know when a certificate is expiring and if a CertKit-managed certificate has been renewed.

Pending certificate expiration.

Successful certificate renewal.

Certificate Retrieval

Once CertKit completes the enrollment process on your behalf, it stores all certificate files (.PFX, .PEM, and .KEY) in a secure S3-compatible storage bucket. While an administrator could easily retrieve and install them manually, automation will help reduce administrative overhead, especially as public TLS certificate lifetimes are further reduced. You can download certificate files programmatically in several ways.

PowerShell

The first way to download the certificate files from CertKit is to use the AWSPowerShell module. However, the AWSPowerShell is relatively heavy and is overkill for this specific use case. A better alternative is to use the MinIO client.

MinIO

The MinIO client (mc.exe) is an open-source command-line tool developed by MinIO. It provides access to any S3-compatible storage, which CertKit uses in its environment. MinIO is a single, portable executable installer that’s easy to use and well-documented.

Sample Code

I’ve published some sample code to demonstrate how to use the MinIO client to retrieve certificates from CertKit and install them on a Windows Server Routing and Remote Access (RRAS) server. You can find the sample code on GitHub here.

https://github.com/richardhicks/aovpn/blob/master/Install-SstpLetsEncryptCertificate-Certkit.ps1

Note: This sample code demonstrates how to download a .PFX file from CertKit and install it on the RRAS server. It is designed to run as a scheduled task in Windows during non-peak times. The code includes robust checks for service viability and will reboot the server if they fail. As such, this sample code could cause service disruptions, so use it with caution.

Cost

Today, CertKit is in beta and is free for everyone to use. In the future, there will be both free and paid tiers. You can learn more about their pricing models and sign up for the service at CertKit.io.

Learn More

If you’d like to learn more about CertKit and how you can leverage it for Always On VPN and other workloads in your environment, or you’d like to see a demonstration of CertKit, fill out the form below, and I’ll provide you with more information.

Additional Information

CertKit

Install-SstpLetsEncryptCertificate-Certkit.ps1 on GitHub

Always On VPN SSTP and 47-Day TLS Certificates

Always On VPN SSTP with Let’s Encrypt Certificates
