

Entra Private Network Connector Session Persistence

The Microsoft Entra Private Network Connector is a lightweight on-premises software agent that enables Microsoft Entra Private Access to forward Global Secure Access (GSA) client traffic to internal resources. In environments with multiple connectors, traffic is normally distributed across available connectors in a connector group. While this improves resiliency and load distribution, it can create challenges for applications that rely on a consistent connector source IP address.

Stateless Connectors

By default, requests are distributed randomly among the available connectors in a connector group. Traffic forwarded to the internal resource uses the connector server’s IP address as its source. Consequently, separate connections from the same user and device can reach the application through different connectors. Importantly, session state is not shared among connectors in a connector group. As such, applications that associate session state with the source IP address may reject or interrupt these connections.

Why Session Persistence Matters

In some scenarios, an internal application might allow access only from specific connector IP addresses or associate an authenticated session with the source IP address. Random connector selection can cause subsequent connections to arrive from a different address, potentially interrupting the session. Session persistence reduces this risk by consistently using the same connector for the user and device.

Session Persistence

Microsoft recently introduced session persistence for Entra Private Access applications. When enabled, requests from the same user and device are consistently routed to the same connector for the duration of the session. This helps maintain a consistent connector egress IP address for applications that depend on source IP addresses for authentication, authorization, or session management.

Traffic Routing

The connector traffic routing method is configured on a per-application basis. Traffic routing methods can be defined on Quick Access or Enterprise applications, and the setting can be configured on the Network access properties tab. Administrators have two options: Random or Session Persistence.
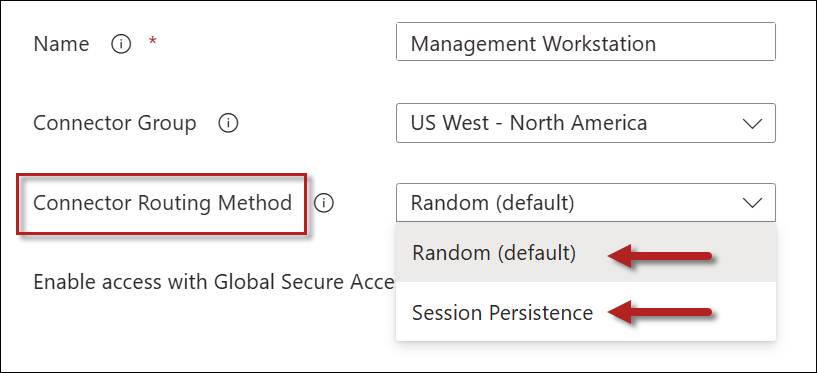
Random

This is the default behavior for the Private Network connector. All new connections are distributed randomly among connectors in the connector group.

Session Persistence

Selecting the Session Persistence option consistently routes requests from the same user and device to the connector on which the session was established.

Connector Routing Method Comparison

The following table summarizes these configuration options.

Routing MethodBenefitsConsiderations
RandomBetter distribution across connectors in a connector groupSource IP address may change between connections
Session PersistenceConsistent connector egress IP addressMay not distribute sessions as evenly as the Random method

Failover

If the preferred connector becomes unavailable, subsequent traffic may be routed through another available connector. Applications that depend on the connector’s source IP address might require the user to establish a new session.

GSA Applications Only

Session persistence applies only to Global Secure Access applications. It is not supported for applications published using Microsoft Entra Application Proxy.

Summary

By default, Microsoft Entra Private Access distributes requests randomly among available connectors. Although this provides load distribution, it can create problems for applications that depend on a consistent connector source IP address. Session persistence addresses this issue by consistently routing traffic from the same user and device through the same connector for the duration of the session. This feature applies only to Global Secure Access applications and is not supported for Microsoft Entra Application Proxy applications.

Additional Information

Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Network Connector Groups

Always On VPN Multisite with Azure Traffic Manager

Always On VPN Multisite with Azure Traffic ManagerEliminating single points of failure is crucial to ensuring the highest levels of availability for any remote access solution. For Windows 10 Always On VPN deployments, the Windows Server 2016 Routing and Remote Access Service (RRAS) and Network Policy Server (NPS) servers can be load balanced to provide redundancy and high availability within a single datacenter. Additional RRAS and NPS servers can be deployed in another datacenter or in Azure to provide geographic redundancy if one datacenter is unavailable, or to provide access to VPN servers based on the location of the client.

Multisite Always On VPN

Unlike DirectAccess, Windows 10 Always On VPN does not natively include support for multisite. However, enabling multisite geographic redundancy can be implemented using Azure Traffic Manager.

Azure Traffic Manager

Traffic Manager is part of Microsoft’s Azure public cloud solution. It provides Global Server Load Balancing (GSLB) functionality by resolving DNS queries for the VPN public hostname to an IP address of the most optimal VPN server.

Advantages and Disadvantages

Using Azure Traffic manager has some benefits, but it is not with some drawbacks.

Advantages – Azure Traffic Manager is easy to configure and use. It requires no proprietary hardware to procure, manage, and support.

Disadvantages – Azure Traffic Manager offers only limited health check options. Today, only HTTP, HTTP, and TCP protocols can be used to perform endpoint health checks. There is no option to use UDP or PING, making monitoring for IKEv2 a challenge.

Note: This scenario assumes that RRAS with Secure Socket Tunneling Protocol (SSTP) or another third-party TLS-based VPN server is in use. If IKEv2 is to be supported exclusively, it will still be necessary to publish an HTTP or HTTPS-based service for Azure Traffic Manager to monitor site availability.

Traffic Routing Methods

Azure Traffic Manager provide four different methods for routing traffic.

Priority – Select this option to provide active/passive failover. A primary VPN server is defined to which all traffic is routed. If the primary server is unavailable, traffic will be routed to another backup server.

Weighted – Select this option to provide active/active failover. Traffic is routed to all VPN servers equally, or unequally if desired. The administrator defines the percentage of traffic routed to each server.

Performance – Select this option to route traffic to the VPN server with the lowest latency. This ensures VPN clients connect to the server that responds the quickest.

Geographic – Select this option to route traffic to a VPN server based on the VPN client’s physical location.

Multivalue – Select this option when endpoints must use IPv4 or IPv6 addresses.

Subnet – Select this option to map DNS responses to the client’s source IP address.

Configure Azure Traffic Manager

Open the Azure management portal and follow the steps below to configure Azure Traffic Manager for multisite Windows 10 Always On VPN.

Create a Traffic Manager Resource

  1. Click Create a resource.
  2. Click Networking.
  3. Click Traffic Manager profile.

Create a Traffic Manager Profile

  1. Enter a unique name for the Traffic Manager profile.
  2. Select an appropriate routing method (described above).
  3. Select a subscription.
  4. Create or select a resource group.
  5. Select a resource group location.
  6. Click Create.

Always On VPN Multisite with Azure Traffic Manager

Important Note: The name of the Traffic Manager profile cannot be used by VPN clients to connect to the VPN server, since a TLS certificate cannot be obtained for the trafficmanager.net domain. Instead, create a CNAME DNS record that points to the Traffic Manager FQDN and ensure that name matches the subject or a Subject Alternative Name (SAN) entry on the VPN server’s TLS and/or IKEv2 certificates.

Endpoint Monitoring

Open the newly created Traffic Manager profile and perform the following tasks to enable endpoint monitoring.

  1. Click Configuration.
  2. Select HTTPS from the Protocol drop-down list.
  3. Enter 443 in the Port field.
  4. Enter /sra_%7BBA195980-CD49-458b-9E23-C84EE0ADCD75%7D/ in the Path field.
  5. Enter 401-401 in the Expected Status Code Ranges field.
  6. Update any additional settings, such as DNS TTL, probing interval, tolerated number of failures, and probe timeout, as required.
  7. Click Save.

aovpn_traffic_manager_multisite_001

Endpoint Configuration

Follow the steps below to add VPN endpoints to the Traffic Manager profile.

  1. Click Endpoints.
  2. Click Add.
  3. Select External Endpoint from the Type drop-down list.
  4. Enter a descriptive name for the endpoint.
  5. Enter the Fully Qualified Domain Name (FQDN) or the IP address of the first VPN server.
  6. Select a geography from the Location drop-down list.
  7. Click OK.
  8. Repeat the steps above for any additional datacenters where VPN servers are deployed.

Always On VPN Multisite with Azure Traffic Manager

Summary

Implementing multisite by placing VPN servers is multiple physical locations will ensure that VPN connections can be established successfully even when an entire datacenter is offline. In addition, active/active scenarios can be implemented, where VPN client connections can be routed to the most optimal datacenter based on a variety of parameters, including current server load or the client’s current location.

Additional Information

Windows 10 Always On VPN Hands-On Training Classes