Always On VPN Error 13868

Troubleshooting Always On VPN Error 691 and 812 – Part 2

The Internet Key Exchange version 2 (IKEv2) VPN protocol is the protocol of choice for Microsoft Always On VPN deployments where the highest levels of security and assurance are required. However, as I’ve written about in the past, often the default IKEv2 security settings are less than desirable. Before using IKEv2 VPN in a production environment the administrator will need to update these security settings accordingly.

Connection Failure

When configuring Windows Server Routing and Remote Access Service (RRAS) or a third-party VPN appliance to support IKEv2 using custom security policies, the administrator may encounter a scenario in which a connection cannot be established due to a policy mismatch error. When the connection attempt fails, an error will be recorded in the Windows Application event log from the RasClient source with Event ID 20227. The error message states the following:

“The user [username] dialed a connection named [connection name] which has failed. The error code returned on failure is 13868.”

Always On VPN IKEv2 Policy Mismatch Error

Error Code 13868

Error code 13868 translates to ERROR_IPSEC_IKE_POLICY_MATCH. Essentially this error indicates that the IKEv2 security policy on the client did not match the configuration on the server.

Server Configuration

To view the current IKEv2 IPsec policy configuration, open an elevated PowerShell command window and run the following command.

Get-VpnServerIPsecConfiguration

Always On VPN IKEv2 Policy Mismatch Error

Client Configuration

To ensure interoperability, the VPN client must be configured to use the same IKEv2 security policy as defined on the sever. To view a VPN client’s currently configured IKEv2 security policy, open an elevated PowerShell command window and run the following command.

Get-VpnConnection -Name [connection name] | Select-Object -ExpandProperty IPsecCustomPolicy

Always On VPN IKEv2 Policy Mismatch Error

Note: If this PowerShell command returns no output, the VPN connection is not using a custom IKEv2 IPsec security policy.

Updating Settings

Guidance for configuring IKEv2 security policies on Windows Server RRAS and Windows 10 can be found here.

NPS Policy

Another common cause of IKEv2 policy mismatch errors is a misconfigured Network Policy Server (NPS) network policy. Specifically, administrators may disable Basic and Strong encryption for MPPE in an attempt to improve security.

Always On VPN IKEv2 Policy Mismatch Error

The NPS policy for Always On VPN must include Strong encryption at a minimum. Basic and No encryption can be safely disabled.

Always On VPN IKEv2 Policy Mismatch Error

Summary

IKEv2 policy mismatch errors can be resolved easily by ensuring both the VPN server and client are configured to use the same IPsec security policies. Use the PowerShell commands in the above referenced above to validate settings and make changes when necessary.

Additional Information

Microsoft Always On VPN Error 13801

Microsoft Windows Always On VPN Error 13806

Microsoft Windows Always On VPN Certificate Requirements for IKEv2

Microsoft Windows Always On VPN IPsec Root Certificate Configuration Issue

Microsoft Windows Always On VPN IKEv2 Policy Mismatch Error

Microsoft Windows Always On VPN IKEv2 Security Configuration

Microsoft Windows Always On VPN IKEv2 Fragmentation

Microsoft Windows Always On VPN IKEv2 Load Balancing and NAT

Microsoft Windows Always On VPN IKEv2 Features and Limitations

Always On VPN RADIUS Configuration Missing

Windows Server Routing and Remote Access Service (RRAS) is a popular choice for administrators deploying Always On VPN. It is easy to configure and scales out easily. Most commonly, RRAS servers are configured to use RADIUS authentication to provide user authentication for Always On VPN client connections. The RADIUS server can be Microsoft Network Policy and Access Server (NPAS, or simply NPS) or a third-party RADIUS solution. It is best to have the RADIUS service running on a server separate from the RRAS server.

RADIUS Authentication

Administrators can configure RADIUS authentication by opening the Routing and Remote Access management console (rrasmgmt.msc), right-clicking the VPN server, then choosing Properties > Security. Click the Configure button to configure authentication and accounting providers accordingly.

RADIUS Options Missing

In some cases, the administrator will notice that the option to configure RADIUS authentication and accounting servers is missing. In its place is the following error message.

“Because Network Policy Server (NPS) is installed, you must use it to configure authentication and accounting providers. To configure authentication and accounting providers, create or modify connection request policies.”

Configuration Options

It might be tempting for administrators to follow this guidance when presented with this message by opening the Network Policy management console (nps.msc) to configure it. However, that is not recommended or necessary. This message results from a common configuration error that should be corrected.

NPS Role Installed

The error message above occurs when an administrator mistakenly installs the NPAS role on the RRAS server itself. Again, this is not recommended or required. To resolve this issue, uninstall the NPS role by opening an elevated PowerShell command window and running the following command.

Uninstall-WindowsFeature NPAS

Configuration Corrupted

After removing the NPAS role from the RRAS server, administrators may encounter the following error message when configuring RADIUS authentication and accounting servers in RRAS.

“The connection request policy used for authentication and accounting configuration is corrupted. Either install Network Policy Server (NPS) and restore the connection request policy manually, or click Repair Settings to restore the connection request policy by using Windows Accounting and Windows Authentication.”

Repair Settings

To resolve this issue, click the Repair Settings button. Once complete, RADIUS authentication and accounting configuration should work as expected.

Additional Information

Always On VPN Network Policy Server (NPS) Auditing and Logging

Always On VPN Network Policy Server (NPS) Load Balancing

Always On VPN and Windows Server 2019 Network Policy Server (NPS) Bug

Always On VPN NPS Auditing and Logging

The Network Policy Server (NPS) event log is incredibly valuable for administrators when troubleshooting Always On VPN user tunnel connectivity issues. Administrators can find these pertinent events by opening the Event Viewer on the NPS server (eventvwr.msc) and navigating to Custom Views > Server Roles > Network Policy and Access Services.

Event Logs

When configured correctly, event logs will record the disposition of all authentication requests, allowed or denied. The two most common recorded events are event IDs 6272 (access granted) and 6273 (access denied).

NPS Event ID 6272 – Access granted.

NPS Event ID 6273 – Access denied.

Auditing

In some cases, administrators may find none of these events recorded even though user authentication is working correctly. Here, the only events recorded are NPS informational events indicating which domain controller the NPS server is using to perform authentication.

The lack of 6272 and 6273 events in the event log indicates that auditing for NPS events is not enabled. Open an elevated PowerShell window and run the following command to view the current auditing setting for NPS events.

auditpol.exe /get /subcategory:”Network Policy Server”

Open an elevated PowerShell window and run the following command to enable auditing for NPS events.

auditpol.exe /set /subcategory:”Network Policy Server” /success:enable /failure:enable

Group Policy

Alternatively, consider using Active Directory group policy to enforce the NPS server auditing settings. Open the Group Policy Management Console (GPMC) and create a new GPO. Next, navigate to Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Audit Policies > Logon/Logoff > Audit Network Policy Server and select the option to audit both success and failure attempts.

Once complete, link this GPO to the OU where the NPS servers reside.

Missing Events

If auditing is enabled and there are no recorded 6272 or 6273 events, the NPS server did not receive any authentication requests from the VPN server. Review the event logs on any other NPS servers if there is more than one configured. In addition, this may indicate that network communication between the VPN and NPS server is blocked. Ensure network connectivity and name resolution are working as expected.

Troubleshooting Guides

Are you interested in learning more about Always On VPN troubleshooting? My Always On VPN book contains an entire chapter dedicated to troubleshooting. Also, my Always On VPN video training course on Pluralsight includes a module on troubleshooting. The video training course is available to Pluralsight subscribers only. If you don’t have a Pluralsight subscription, you can sign up for a free trial here.

Additional Information

Troubleshooting Always On VPN Errors 691 and 812

Troubleshooting Always On VPN Errors 691 and 812 – Part 2

Troubleshooting Always On VPN Errors 691 and 812 – Part 3

Always On VPN NPS Load Balancing

What’s New in Always On VPN DPC v3.0

Recently I wrote about a compelling solution from PowerON Platforms for managing Always On VPN client configuration setting using Active Directory group policy. Always On VPN Dynamic Profile Configurator (DPC) addresses a very specific need for managing Always On VPN for organizations that have not yet migrated to Microsoft Endpoint Manager/Intune. Recently, PowerON Platforms released an important update to DPC that includes many new features and capabilities.

New Features

Always On VPN DPC version 3.0 includes the following new functionality Always On VPN administrators are sure to find useful.

  • Traffic filters – Support for enabling traffic filters for both device tunnel and user tunnel are now supported in DPC, greatly simplifying the task of creating access control lists to enforce zero-trust network access (ZTNA) policies.
  • Enhanced security – The option to disconnect the VPN connection if the VPN server does not present a cryptobinding TLV is now enabled by default. This often-overlooked security setting ensures VPN client connections are not intercepted by detecting man-in-the-middle attacks.
  • Device tunnel enhancements – Administrators can now display the device tunnel connection and status in the Windows UI.
  • Backup connection – Always On VPN DPC now supports the configuration and deployment of a backup VPN connection, which is helpful when Always On VPN connectivity is disrupted.
  • Hostname routing – Administrators can now define hostnames in the routing table. Hostnames are resolved on the endpoint and converted to IP addresses for including in the routing table.
  • Smart card authentication – Always On VPN DPC now supports smart card authentication as an authentication option in addition to client authentication certificates.

Learn More

Interested in learning more about Always On VPN DPC? Fill out the form below and I’ll provide you with additional information or visit aovpndpc.com to sign up for a free trial.

Additional Information

Always On VPN with Active Directory Group Policy

Always On VPN Video Demonstration

Always On VPN DPC Advanced Features

Always On VPN DPC on YouTube

Certificate-Based Authentication Changes and Always On VPN

Microsoft introduced important changes affecting certificate-based authentication on Windows domain controllers as part of the May 10, 2022 update KB5014754 that may affect Always On VPN deployments. The update addresses privilege escalation vulnerabilities when a domain controller is processing a certificate-based authentication request. The recommendation from Microsoft is that the update be applied to all Windows domain controllers and Active Directory Certificate Services (AD CS) servers as soon as possible.

Updated 5/20/2022: An out-of-band update to address authentication issues reported with this update is now available. Updates are available for Windows Server 2022, Windows Server 20H2, Windows Server 2019, Windows Server 2016, Windows Server 2012 R2, Windows Server 2012, Windows Server 2008 R2 SP1, and Windows Server 2008 SP2.

Certificate Services

After applying the update to certification authority (CA) servers, a non-critical extension with Object Identifier (OID) 1.3.6.1.4.1.311.25.2 is added to all issued certificates with the user or device security identifier (SID) included. Domain controllers with the update installed will use this information to validate the certificate used for authentication and ensure that it matches the information in Active Directory.

Domain Controllers

The update operates in Compatibility Mode, by default, when applied to domain controllers. Windows monitors authentication requests and records audit events for certificates presented for authentication under the following conditions.

No strong mapping (event ID 39) – The certificate has not been mapped explicitly to a domain account, and the certificate did not include the new SID extension.

Certificate predates account (event ID 40) – A certificate was issued before the user existed in Active Directory, and no explicit mapping could be found.

User’s SID does not match certificate (event ID 41) – A certificate contains the new SID extension, but it does not match the SID of the corresponding user account.

Certificate Mapping

Administrators can map certificates explicitly to accounts in Active Directory, but this results in a significant administrative burden in most environments. A better option is to reissue user and device authentication certificates after applying the KB5014754 update to all issuing CA servers.

Reenroll Certificates

Administrators should reissue user and device authentication certificates after applying the KB5014754 update. Open the Certificate Templates management console (certtmpl.msc), identify the user or device authentication certificate template, then right-click on the template and choose Reenroll All Certificate Holders.

Enforcement Mode

After applying update KB5014754, administrators should monitor domain controller event logs for event IDs 39, 40, and 41. Once all certificates have been updated, and none of these events have been recorded for 30 days, administrators can switch to Full Enforcement Mode by enabling it in the registry on all domain controllers.

Key: HKLM\SYSTEM\CurrentControlSet\Services\KDC
Value: StrongCertificateBindingEnforcement
Type: DWORD
Data: 2

Updated 12/8/2022: Microsoft has pushed back the original enforcement date of May 9, 2023, to November 14, 2023 “or later”. Stay tuned!

Updated 11/29/2022: Microsoft now states that the full enforcmenet mode date is now February 11, 2025 “or later”. Once again, stay tuned!

Known Issues

There have been some reports of authentication issues after installing the KB5014754 update. Early indications are that device authentication certificates missing a Subject Alternative Name (SAN) entry are to blame. Administrators are encouraged to update their device certificates to include the SAN entry. Optionally, but not recommended, administrators can place the update in disabled mode by editing the registry.

Note: An out-of-band update for these authentication issues is now available. See the reference links at the top of this article for more information.

Caveat

It’s important to understand that this new OID is added only to online templates. Online templates are those that build the subject information from Active Directory. Unfortunately, this new OID is NOT applied to offline templates (templates where the subject name is supplied in the request), such as those used for delivering certificates with Microsoft Endpoint Manager/Intune using PKCS or SCEP. It is impossible to move to enforcement mode when issuing user or device authentication certificates with Microsoft Endpoint Manager or Intune today. Microsoft is aware of this limitation and is working to address this issue as we speak. I expect a fix to be available sometime before the May 2023 deadline when Microsoft permanently switches on enforcement mode.

Additional Information

KB5014754 – Certificate-based authentication changes on Windows domain controllers

Microsoft Windows Always On VPN Users Prompted for Certificate

Microsoft Windows Always On VPN Clients Prompted for Authentication when Accessing Internal Resources

Always On VPN Book Available for Pre-Order

Great news! My new book, Implementing Always On VPN, is now available for pre-order on Amazon.com. This new book, scheduled for release in late 2021, is a comprehensive implementation guide for Windows 10 Always On VPN. Drawing on many years of experience deploying Always On VPN for organizations worldwide, it covers all aspects of an Always On VPN deployment, including planning and design, prerequisite gathering, infrastructure preparation, and client deployment.

In addition, it contains detailed, prescriptive guidance for advanced configuration options such as application and traffic filtering and proxy server configuration. Cloud deployments using Azure VPN gateway and Virtual WAN are covered, and it includes guidance for configuring Azure MFA and Conditional Access.

Also, the book includes thorough guidance for provisioning certificates using Microsoft Endpoint Manager/Intune using both PKCS and SCEP. It outlines options for high availability for VPN and authentication infrastructure and provides details for ongoing system maintenance and operational support.

Finally, the book has an entire chapter dedicated to troubleshooting and resolving common (and not so common!) issues encountered with Windows 10 Always On VPN.

Reserve your copy today. Pre-order Implementing Always On VPN now!

Chapter List

  1. Always On VPN Overview
  2. Plan an Always On VPN Deployment
  3. Prepare the Infrastructure
  4. Configure Windows Server for Always On VPN
  5. Provision Always On VPN clients
  6. Advanced Configuration
  7. Cloud Deployments
  8. Deploy Certificates with Intune
  9. Integrating Azure MFA
  10. High Availability
  11. Monitor and Report
  12. Troubleshooting

Always On VPN Error 853 on Windows 11

Recently I did some validation testing with Always On VPN on Windows 11, and I’m happy to report that everything seems to work without issue. However, a few readers have reported 853 errors when establishing an Always On VPN connection after upgrading to Windows 11.

Can’t Connect

After upgrading to Windows 11, an Always On VPN connection may fail with the following error message.

“The remote access connection completed, but authentication failed because the certificate that authenticates the client to the server is not valid. Ensure the certificate used for authentication is valid.”

Error 853

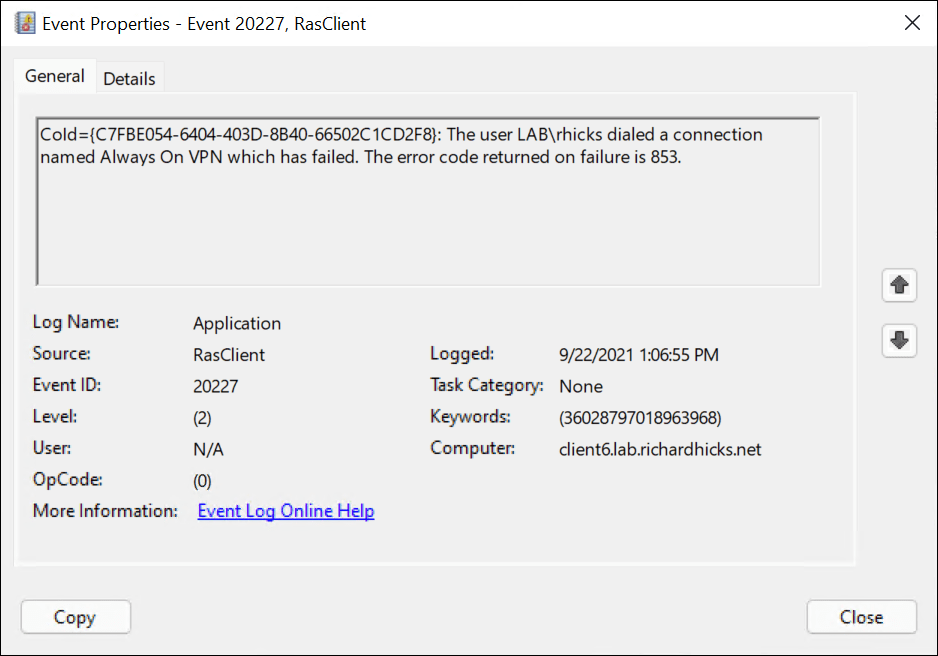
In addition, the Application event log records an event ID 20227 from the RasClient source that includes the following message.

“The user <username> dialed a connection name <connection name> which has failed. The error code returned on failure is 853.”

Server Identity

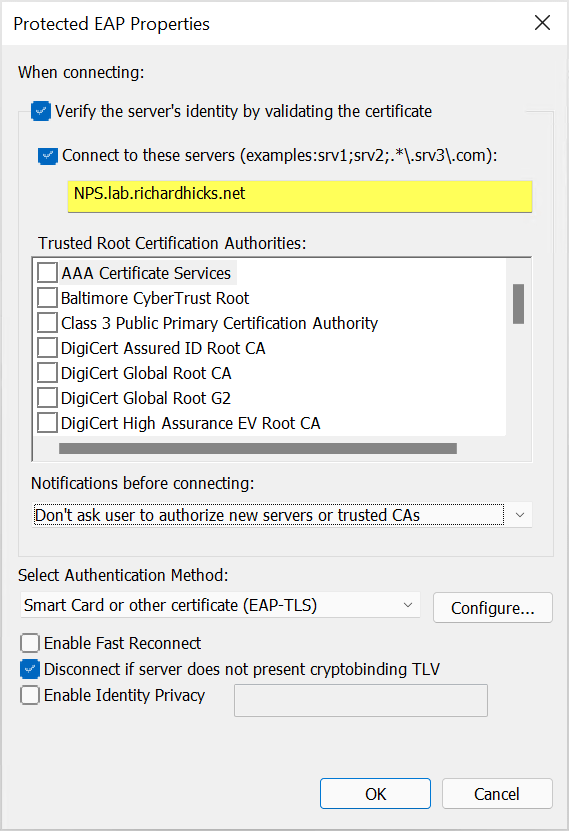
This error will occur when using Protected Extensible Authentication Protocol (PEAP) authentication. Specifically, it can happen when the option to verify NPS server validity by its certificate is selected, and an explicit list of NPS servers is defined, as shown here.

Case Sensitive

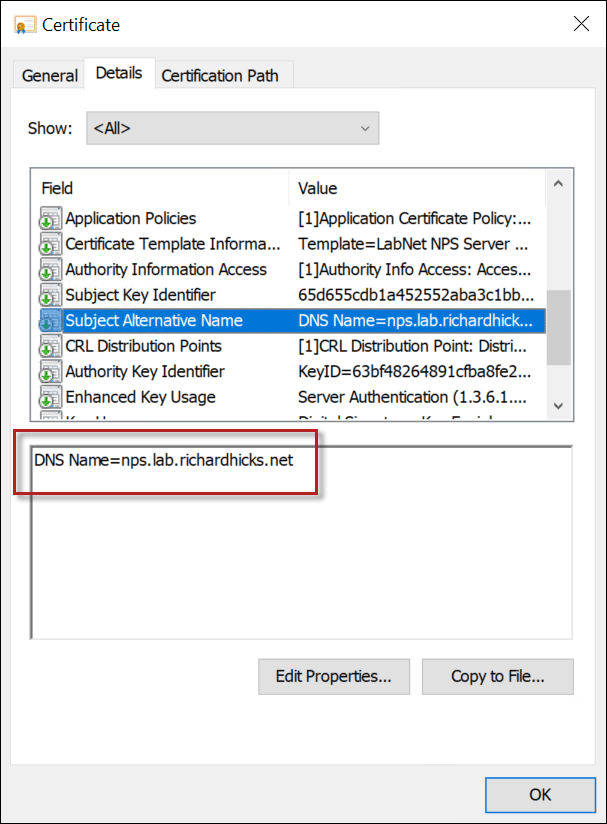
In this specific scenario, Windows 11 now appears to be case-sensitive when it compares the NPS server name entered in the NPS configuration to the Subject Name on the certificate returned by the server. For example, if the Subject Name (or Subject Alternative Name, if present) entry on the NPS server certificate is nps.lab.richardhicks.net, using NPS.lab.richardhicks.net will not match and return an 853 error.

Windows 11

Case matching when validating the NPS server certificate is a change in behavior from Windows 10. Before Windows 11, this comparison was case-insensitive, and any combination of case would match if the entire hostname matched. Going forward, it appears Microsoft has also decided to require case matching to validate the server certificate.

Recommendations

Administrators should look carefully at the server certificate issued to the NPS server and ensure their client configuration accurately reflects the hostname in a case-sensitive manner to ensure a smooth migration from Windows 10 to Windows 11.

Additional Information

Troubleshooting Windows 10 Always On VPN Error 853

Windows 10 Always On VPN Network Policy Server (NPS) Load Balancing

Always On VPN Short Name Access Failure

Using Microsoft Endpoint Manager (Intune), administrators can provision Always On VPN to devices that are Azure AD joined only. Users accessing on-premises resources from these devices can still use seamless single sign-on, making this deployment option popular for organizations moving to the cloud.

Short Names

After deploying Always On VPN to Windows 10 devices that are Azure AD joined only and configured to use client certificate authentication, administrators may find that users cannot access on-premises resources by their short name, such as \\app1. The connection fails and returns the following error message.

“Windows can’t find <servername/sharename>. Check the spelling and try again.”

FQDN

Interestingly, on-premises resources are accessible using their fully qualified domain name (FQDN), such as \\app1.corp.example.net.

Troubleshooting

Testing name resolution using the short name works as expected, and the resource is reachable at the network layer, as shown here.

Workaround

This issue is related to how Windows performs authentication when connected via VPN. To resolve this issue, edit the rasphone.pbk file and change the value of UseRasCredentials to 0. Rasphone.pbk can be found in the $env:AppData\Microsoft\Network\Connections\Pbk folder.

After updating this setting, restart the VPN connection for the change to take effect.

Proactive Remediations

While helpful for testing, editing rasphone.pbk manually obviously does not scale well. To address this, consider using Intune Proactive Remediations. Intune Proactive Remediations allows administrators to deploy detection and remediation PowerShell scripts to monitor specific settings and update them if or when they change. Proactive Remediations will ensure the setting is applied consistently across all managed endpoints.

GitHub Repository

I have created a new GitHub repository dedicated to PowerShell scripts for Endpoint Manager Proactive Remediations for Always On VPN. There you will find detection and remediation scripts for the UseRasCredentials settings change described in this article.

PowerShell

Administrators can also implement this setting by running the following PowerShell command.

Set-ItemProperty -Path ‘HKLM:\SYSTEM\CurrentControlSet\Control\Lsa’ -Name DisableDomainCreds -Value 1

Group Policy

Another option for implementing this setting is by enabling the following Active Directory Group Policy setting.

Computer Configuration > Windows Settings > Security Settings > Local Policies > Security Options > Network access: Do not allow storage of passwords and credentials for network authentication

Additional Information

Always On VPN Endpoint Manager Proactive Remediation Scripts on GitHub

Endpoint Manager Proactive Remediations Tutorial

Always On VPN Authentication Failure with Azure Conditional Access

Always On VPN Clients Prompted for Authentication when Accessing Internal Resources

Integrating Microsoft Azure Conditional Access with Windows 10 Always On VPN has several important benefits. The most important is that it allows administrators to improve their security posture by enforcing access polices that can be dynamically applied. For example, requiring multifactor authentication (MFA) for privileged users (e.g., administrators) or sign-ins that appear to be risky, the type of device they are connecting with, the health of the endpoint, and much more.

Authentication Failure

When configuring Always On VPN to support Azure Conditional Access, administrators may expeirence a failed authentication during preliminary testing. Specifically, an event ID 20227 from the RasClient source may be encountered with the following error message.

“The user <username> dialed a connection named <connection name> which has failed. The error code returned on failure is 812.”

Looking at the event logs on the Network Policy Server (NPS) server reveals an event ID 6273 from the Microsoft Windows security auditing source with Reason Code 258 and the following Reason.

“The revocation function was unable to check revocation for the certificate.”

Root Cause

When Azure Conditional Access is configured for Always On VPN, a short-lived certificate (1 hour lifetime) is provisioned by Azure. This certificate does not include revocation information because, by design, a short-lived certificate does not need to be revoked. However, by default NPS always checks revocation when client authentication certificates are used for authentication. Since the certificate does not include this information, certificate revocation fails.

Resolution

The way to resolve this issue is to disable certificate revocation checking for Protected Extensible Authentication Protocol (PEAP) authentication requests. To do this, open an elevated PowerShell window on the NPS server and run the following command.

New-ItemProperty -Path ‘HKLM:\SYSTEM\CurrentControlSet\Services\RasMan\PPP\EAP\13\’ -Name IgnoreNoRevocationCheck -PropertyType DWORD -Value 1 -Force

Once complete, restart the NPS server for the changes to take effect.

Additional Information

Windows 10 Always On VPN Network Policy Server (NPS) Load Balancing

Windows 10 Always On VPN Network Policy Server (NPS) Server 2019 Bug

Troubleshooting Always On VPN Error 853

Troubleshooting Always On VPN Error 691 and 812 – Part 2

Using Windows Server Network Policy Server (NPS) servers is a common choice for authenticating Microsoft Windows 10 Always On VPN user tunnel connections. The NPS server is joined to the domain and configured with a Network Policy that defines the authentication scheme used by clients for authentication when establishing an Always On VPN connection. Protected Extensible Authentication Protocol (PEAP) using client authentication certificates recommended for most Always On VPN deployment scenarios.

Experiencing error 853 on Windows 11? Click here for more information.

Can’t Connect

Users establishing an Always On VPN user tunnel connection using PEAP and client authentication certificates may encounter a scenario in which a VPN connection attempt fails with the following error message.

“The remote access connection completed, but authentication failed because the certificate that authenticates the client to the server is not valid. Ensure that the certificate used for authentication is valid.”

Error 853

In addition, the Application event log records an event ID 20227 from the RasClient source that includes the following error message.

“The user <username> dialed a connection named <connection name> which has failed. The error code is 853.”

Missing NTAuth Certificate

Error code 853 is commonly caused by a missing issuing Certification Authority (CA) certificate in the NTAuth store on the NPS server. The NPS server must have the issuing CA certificate included in this store to perform authentication using client certificates. You can see the contents of the NTAuth certificate store by opening an elevated command window on the NPS server and running the following command.

certutil.exe -enterprise -viewstore NTAuth

Install Certificate

To install the issuing CA server’s certificate into the NTAuth store, copy the CA certificate to the NPS server, open an elevated command window, then run the following command.

certutil.exe -enterprise -addstore NTAuth <issuing CA certificate>

Once complete, view the store again, and you’ll see the issuing CA certificate listed in the NTAuth certificate store.

Additional Information

Always On VPN Error 853 on Windows 11

Troubleshooting Always On VPN Error Code 858

Troubleshooting Always On VPN Error Code 864

Always On VPN and Windows Server 2019 NPS Bug

Always On VPN Network Policy Server (NPS) Load Balancing

Microsoft Network Policy Server (NPS) Reason Codes