What’s New in Entra Private Network Connector v1.5.5130.0

Microsoft Entra Private Access

On November 9, 2026, Microsoft released an important update for the Microsoft Entra Private Network Connector. The Entra Private Network Connector is used to publish on-premises web applications to the internet. It is also used for Global Secure Access (GSA) with Entra Private Access, allowing GSA clients to access on-premises resources. Entra Private Network Connector v1.5.5130.0 includes new functionality to improve performance monitoring, name resolution, logging, and overall reliability and security.

New Features

This release introduces new capabilities for monitoring connector performance and resolving names in complex network environments, including the following.

Performance and Diagnostics

The Connector Diagnostics tool, available from the system tray, now includes a new Performance tab. Here, administrators can view up to 24 hours of resource history for the connector server, collected in one-minute aggregates. The Performance tab displays average and peak values for the following metrics.

  • Machine CPU: Total CPU usage across the machine.
  • Connector CPU: Share of total machine CPU used by the connector.
  • Connector resident memory: Physical memory used by the connector process.
  • Machine available memory: Physical memory still available to applications.

Administrators can use the Window drop-down list to display performance history for the last 1 hour, 6 hours, or 24 hours. This gives better visibility into resource consumption over time, which is helpful when sizing connector servers or investigating performance issues. In addition, this update improves the accuracy of connector health reporting.

Entra Private Network Connector Diagnostics Performance tab showing machine CPU, connector CPU, connector resident memory, and machine available memory charts

DNS Resolution

The connector now honors DNS suffixes and DNS servers configured on individual network interfaces in Windows. This update also improves the fallback behavior for DNS SRV record queries.

Improvements

In addition to new features, v1.5.5130.0 includes several improvements to logging, reliability, and security.

Logging and Observability

This update includes the following changes to connector logging.

  • Trace file rotation is now supported.
  • The default capacity for the Session event log has been increased to 3 GB.
  • Error messages for connectivity and backend failures have been improved to streamline troubleshooting.

Note: With the larger default Session event log size, administrators should ensure the connector server has sufficient free disk space on the system drive.

Reliability and Security

This update also includes the following reliability and security enhancements.

  • TCP keepalive has been added to reduce idle connection resets.
  • Memory management during request processing has been improved.
  • Security for local log files and other connector files has been enhanced.

Updating to v1.5.5130.0

Existing Entra Private Network Connector installations will not automatically receive this update. Administrators must manually download the connector from the Microsoft Entra admin center and apply the update themselves to take advantage of these new features and capabilities.

Additional Information

Microsoft Entra Private Network Connector v1.5.5130.0

Microsoft Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Entra Private Network Connector Session Persistence

Entra Private Network Connector Session Persistence

The Microsoft Entra Private Network Connector is a lightweight on-premises software agent that enables Microsoft Entra Private Access to forward Global Secure Access (GSA) client traffic to internal resources. In environments with multiple connectors, traffic is normally distributed across available connectors in a connector group. While this improves resiliency and load distribution, it can create challenges for applications that rely on a consistent connector source IP address.

Stateless Connectors

By default, requests are distributed randomly among the available connectors in a connector group. Traffic forwarded to the internal resource uses the connector server’s IP address as its source. Consequently, separate connections from the same user and device can reach the application through different connectors. Importantly, session state is not shared among connectors in a connector group. As such, applications that associate session state with the source IP address may reject or interrupt these connections.

Why Session Persistence Matters

In some scenarios, an internal application might allow access only from specific connector IP addresses or associate an authenticated session with the source IP address. Random connector selection can cause subsequent connections to arrive from a different address, potentially interrupting the session. Session persistence reduces this risk by consistently using the same connector for the user and device.

Session Persistence

Microsoft recently introduced session persistence for Entra Private Access applications. When enabled, requests from the same user and device are consistently routed to the same connector for the duration of the session. This helps maintain a consistent connector egress IP address for applications that depend on source IP addresses for authentication, authorization, or session management.

Traffic Routing

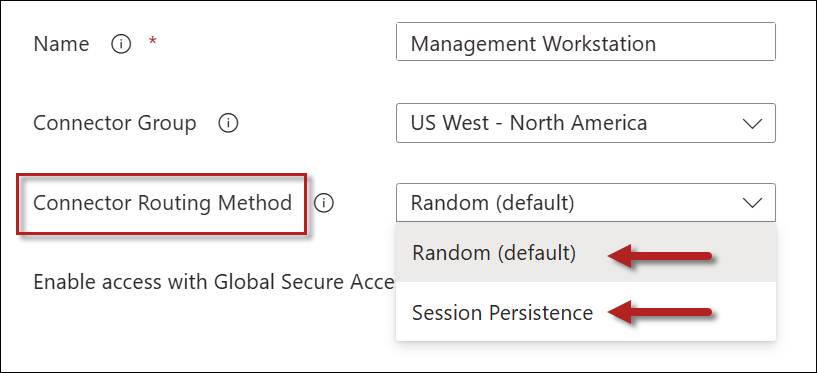
The connector traffic routing method is configured on a per-application basis. Traffic routing methods can be defined on Quick Access or Enterprise applications, and the setting can be configured on the Network access properties tab. Administrators have two options: Random or Session Persistence.

Random

This is the default behavior for the Private Network connector. All new connections are distributed randomly among connectors in the connector group.

Session Persistence

Selecting the Session Persistence option consistently routes requests from the same user and device to the connector on which the session was established.

Connector Routing Method Comparison

The following table summarizes these configuration options.

Routing MethodBenefitsConsiderations
RandomBetter distribution across connectors in a connector groupSource IP address may change between connections
Session PersistenceConsistent connector egress IP addressMay not distribute sessions as evenly as the Random method

Failover

If the preferred connector becomes unavailable, subsequent traffic may be routed through another available connector. Applications that depend on the connector’s source IP address might require the user to establish a new session.

GSA Applications Only

Session persistence applies only to Global Secure Access applications. It is not supported for applications published using Microsoft Entra Application Proxy.

Summary

By default, Microsoft Entra Private Access distributes requests randomly among available connectors. Although this provides load distribution, it can create problems for applications that depend on a consistent connector source IP address. Session persistence addresses this issue by consistently routing traffic from the same user and device through the same connector for the duration of the session. This feature applies only to Global Secure Access applications and is not supported for Microsoft Entra Application Proxy applications.

Additional Information

Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Network Connector Groups

What’s New in Entra Private Network Connector v1.5.4892.0

An important update is available for the Microsoft Entra Private Network Connector. The Entra Private Network Connector is used to publish on-premises web applications to the internet. It is also used for Global Secure Access (GSA) with Entra Private Access, allowing GSA clients to access on-premises resources. Entra Private Network Connector v1.5.4892.0 includes important new functionality to streamline troubleshooting and improve stability and performance.

New Features

The Entra Private Network Connector v1.5.4892.0 now includes a diagnostic tool on the system tray. This gives administrators a visual indicator of connector status and provides quick access to diagnostics and log files.

Diagnostics

Right-clicking the connector and choosing ‘Connector diagnostics’ launches the Connector Diagnostics window. Here you’ll find three tabs: Overview, Health Check, and Advanced Logs.

Overview

The Overview tab provides details about the connector, such as the Tenant ID, Connector ID, version, supported TLS versions, the connector server’s IPv4 address (IPv6 information is not displayed), the server’s hostname, and the operating system version.

Health Check

Clicking on the Health Check tab will perform a comprehensive system health check. Status information for each check is provided, indicating whether it is Passed or Failed. Optionally, administrators can export the report in text, HTML, or JSON format for further analysis. Each health check can be expanded to reveal additional information about the individual check.

Advanced Logs

Clicking the Advanced Logs tab allows administrators to retrieve detailed log information. Session channel logging is enabled by default but can optionally be disabled if needed. You can choose specific start and end dates and times to collect logs, then click Retrieve Logs to collect them.

Once complete, it’s not immediately obvious where to find these logs. Clicking the Logs Retrieved button prompts the administrator to select a location in which to save the log files.

Improvements

This update improves the reliability of name resolution by filtering invalid DNS responses. In addition, the update improves connector logging to the Windows Event Log and fixes various issues and bugs.

Updating to v1.5.4892.0

Existing Entra Private Network Connector installations will not automatically receive this update. Administrators must manually download the connector from the Microsoft Entra admin center and apply the update themselves to take advantage of these new features and capabilities.

Additional Information

Microsoft Entra Private Network Connector v1.5.4892.0

Microsoft Entra Private Network Connector Overview and Deployment Strategies

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Network Connector Overview and Deployment Strategies

When deploying Microsoft Entra Private Access, administrators must install at least one Entra Private Network Connector to facilitate communication between Global Secure Access clients and on-premises resources. The Entra Private Network connector is a software agent that communicates outbound only. It requires no inbound connectivity, reducing public network exposure and minimizing the organization’s attack surface.

Entra Private Network Connector

The Entra Private Network connector is essentially Microsoft Entra application proxy (formerly Azure AD Application Proxy), updated to support all TCP and UDP-based communication. You can download the connector by opening the Entra admin center, navigating to Global Secure Access > Connect > Connectors, and clicking the Download connector service link.

Cloud Appliances

To enable access to cloud-hosted resources, the Entra Private Network connector can be installed on a VM in those environments. However, the Entra Private Network connector is also available as an appliance in public preview for the following cloud providers.

Resource Requirements

The following recommendations pertain to VM resources for the Entra Private Network connector server.

  • Windows Server 2016 or later. However, Windows Server 2016 reaches end of life in January 2027, so Windows Server 2022 and later are recommended. The Desktop edition is required, but it can technically be installed on Server Core with the Application Compatibility Feature on Demand for Server Core. However, Microsoft may not formally support this option.
  • Minimum 4 CPU cores and 8GB RAM. Monitor resource utilization during migration. Provision additional CPU and/or memory when utilization consistently exceeds 70% during peak times. Scaling out (adding servers) is preferred over scaling up (adding CPU and RAM).
  • Domain Join. Domain join is optional but recommended. Domain join is required to support single sign-on (SSO).

Connector Groups

A Connector Group is a logical grouping of Entra Private Network connectors. A Connector Group functions as a single unit for high availability and load balancing. Connectors are deployed in the same region as the tenant by default.

Default Group

When you install the Entra Private Network connector, it is placed into the Default connector group. However, this may not always be desirable. For example, the organization may have multiple data centers in different geographies. They may also have resources hosted in different Active Directory forests or perhaps located in isolated network locations. Using a common connector group may be suboptimal or not work at all.

Custom Groups

Administrators can define custom connector groups as needed. Custom connector groups ensure that connectors always have access to the resources nearest to them. They can be deployed in different locations and assigned to other Azure regions to ensure optimal traffic routing and reduced latency. Today, administrators can create connector groups in the North America, Europe, Australia, Asia, and Japan regions.

Create a Connector Group

Open the Microsoft Entra admin center and perform the following steps to create a new Entra Private Network connector group.

  1. Navigate to Global Secure Access > Connect > Connectors and Sensors.
  2. Click on New Connector Group.
  3. In the Name field, enter a descriptive name for the connector group.
  4. From the Connectors drop-down list, select one or more Entra Private Network connectors to assign to the group. Optionally, you can leave this field blank and assign connectors later.
  5. Click Save.
Entra admin center New Connector Group page with name and connector selection

Connector Group Assignment

Once you have created a new connector group, you can assign Quick Access or individual Enterprise applications to it as follows.

Quick Access

To assign a new connector group to the Quick Access application, open the Entra admin console, navigate to Global Secure Access > Applications > Quick Access, and select the Network access properties tab. Select the new connector group from the Connector Group drop-down list.

Quick Access network access properties with the Connector Group drop-down list

Enterprise Applications

To assign a new connector group to an individual Enterprise application, navigate to Global Secure Access > Applications > Enterprise applications. Select an application, then select Network access properties. Select the new connector group from the Connector Group drop-down list.

Enterprise application network access properties with the Connector Group drop-down list

Deployment Strategy

The following are best practices for deploying the Entra Private Network connector.

Redundancy

Always deploy at least two Entra Private Network connectors to ensure high availability and eliminate single points of failure.

Location

Install the Entra Private Network connector on servers closest to the applications they serve. Deploy connectors in all locations where applications are accessed, including on-premises networks and Infrastructure-as-a-Service (IaaS) resources.

Default Connector Group

Avoid using the default connector group for application assignment. Always use custom connector groups for application access. This ensures that new connectors do not process production traffic immediately after installation, which can cause unexpected behavior if the connector is not optimally deployed for the published resource or is not connected to the back-end application.

Deleting Connectors

Entra Private Network connectors cannot be removed from the management console. If you uninstall a connector, its status will show as inactive. After 10 days of inactivity, it will be automatically removed.

Reassigning Connectors

Administrators can reassign connectors to different connector groups at any time. However, existing connections on that connector server from the prior group assignment will remain until they age out. Administrators can restart the connector service or reboot the server to address this issue.

Restart-Service -Name WAPCSvc -PassThru

Connector Updates

The Entra Private Network connector will automatically install major updates when they become available. However, not all updates are applied automatically. Don’t be alarmed if you see discrepancies between release versions across multiple connector servers in the admin console. Administrators can always perform software updates manually to ensure uniform connector versions in their environment, if desired.

Diagnostics

Beginning with Entra Private Network connector v1.5.4287.0, the agent installation also includes the diagnostic utility ConnectorDiagnosticsTool.exe, which is in the C:\Program Files\Microsoft Entra Private Network Connector\ folder on the connector server. Running the tool initiates a series of tests to perform a health check of the connector service, including certificate status, connectivity, enabled TLS versions, service status, and more.

ConnectorDiagnosticsTool.exe health check results for the Entra Private Network connector

Note: Entra Private Network connector v1.5.4522.0 and later includes a graphical output, as shown above. Previous versions featured text-based output only.

Summary

Microsoft Entra Private Network Connectors are lightweight, outbound-only agents that enable secure access to on-premises and cloud resources through Entra Private Access. Best practices emphasize deploying at least two connectors per location for redundancy, placing them close to target applications, using custom connector groups for high availability, load balancing, and optimal routing, and assigning them to Quick Access or enterprise applications while avoiding the default group. Ensure that VMs are appropriately sized for the expected connector traffic, and consider using marketplace appliances for Azure, AWS, and GCP. If you’ve previously deployed the Entra Private Network connector, ensure that it is running the latest release to take advantage of new diagnostics for troubleshooting.

Additional Information

Microsoft Entra Private Network Connectors

Microsoft Entra Private Network Connector groups

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Access Intelligent Local Access

Always On VPN vs. Entra Private Access: Choosing the Right Access Model

Preventing Port Exhaustion on Entra Private Network Connector Servers

Microsoft Entra Private Access is a powerful zero-trust network access solution that is remarkably simple to install and configure. Administrators can quickly install the Global Secure Access (GSA) agent on their endpoints, then install the Entra Private Network Connector to enable secure remote access to private, internal resources. However, the ease with which Entra Private Access can be configured can potentially lead to connectivity issues in some scenarios. This post demonstrates how to diagnose port exhaustion issues and expand the available port range to address them.

Entra Private Network Connector

The Entra Private Network Connector is a key component of the Entra Private Access solution. The Private Network Connector is essentially the old Azure Application Proxy, enhanced to support TCP and UDP applications in addition to HTTP-based web applications. It is installed on an on-premises Windows server to provide GSA clients with access to internal data and applications.

Network Connectivity

The GSA client is not a virtual network adapter like most traditional VPN clients. Instead, the GSA client installed on the client operates as a filter driver in the network stack, selectively intercepting traffic and tunneling it over the GSA tunnel based on configured policy. As such, it does not appear as a network adapter in the operating system and does not have its own IP address.

Translation

When traffic from the GSA client is routed over the Entra Private Network Connector, the traffic egressing from the connector server to the internal network is effectively translated. That is, the source IP address of traffic destined for an internal resource is the connector server’s IP address, not the client’s original source IP address.

Port Exhaustion

The ephemeral port range on Windows servers spans from 49152 to 65535, leaving only 16,384 ports available. This can easily be exhausted when many clients are connected to a single Entra Private Network Connector server. This pool can also be depleted by poorly written or badly behaving applications that needlessly open many socket connections to internal resources.

Troubleshooting

Administrators can view the ephemeral port configuration for both TCP and UDP by running the following commands.

netsh.exe interface ipv4 show dynamicportrange protocol=tcp

netsh.exe interface ipv4 show dynamicportrange protocol=udp

To determine if port exhaustion is an issue, open an elevated PowerShell command window and run the following command.

Get-NetTcpConnection | Where-Object State -match ‘established’ | Measure-Object

Next, run the following PowerShell command to identify the number of ports consumed exclusively by the Entra Private Network Connector.

$ProcessId = Get-CimInstance -ClassName win32_service | Where-Object Name -eq ‘WAPCSvc’ | Select-Object -ExpandProperty ProcessID

Get-NetTCPConnection | Where-Object { $_.State -match ‘established’ -and $_.OwningProcess -eq $ProcessId } | Measure-Object

If the number of ports consumed by the Entra Private Network Connector approaches the upper limit of available ports, administrators should increase the ephemeral port range to ensure the connector server operates reliably.

Note: Use the Get-NetUdpEndpoint PowerShell command to monitor UDP port consumption on Entra Private Network Connector servers.

Resolution

To increase the ephemeral port range on the Entra Private Network Connector server, open an elevated command window and run the following commands.

netsh.exe interface ipv4 set dynamicportrange protocol=tcp startport=10000 numberofports=55535
netsh.exe interface ipv4 set dynamicportrange protocol=udp startport=10000 numberofports=55535
netsh.exe interface ipv6 set dynamicportrange protocol=tcp startport=10000 numberofports=55535
netsh.exe interface ipv6 set dynamicportrange protocol=udp startport=10000 numberofports=55535

Running these commands will increase the number of available ephemeral ports on the server to more than 50,000, well above the default. In most cases, this should be sufficient to handle many GSA client connections. However, administrators are cautioned to monitor port usage on the Entra Private Network Connector servers to ensure continued reliable operation. It may be necessary to deploy additional connector servers to process the existing workload.

Summary

Entra Private Network Connectors can exhaust the default 16,384-port ephemeral range when many GSA clients access internal TCP/UDP resources. Administrators can diagnose the issue by filtering Get-NetTCPConnection results by the WAPCSvc process, then expanding the range to over 50,000 ports using netsh.exe, as shown above. Monitor usage continuously in high-load environments to ensure consistent and stable access. And if you find you need more than 50,000 ports per server, it’s probably time to deploy additional connector servers. 😊

Additional Information

Microsoft Entra Private Access

Entra Private Access Channels are Unreachable

Microsoft Entra private network connectors

Certificate Connector for Microsoft Intune Agent Certificate Renewal Failure

The Certificate Connector for Microsoft Intune is a vital component that allows administrators to issue and manage enterprise PKI certificates to endpoints managed by Microsoft Intune. The connector is installed on a Windows server with access to the on-premises Certificate Authority (CA). It is registered with Intune and can be used by any PKCS or SCEP device configuration profiles defined by Intune administrators.

Agent Certificate

When you install the Certificate Connector for Intune, a certificate issued by the Microsoft Intune ImportPFX Connector CA is automatically enrolled into the local computer certificate store of the server where the connector is installed. This certificate authenticates the connector to Intune and is valid for one year from the date of issuance. This certificate is automatically renewed in most cases. However, some configurations prevent this from happening.

Failed To Renew

Administrators may find event log errors with event ID 2 from the CertificateConnectors source in the Microsoft-Intune-CertificateConnectors operational event log with the following information.

Pki Create Service:

Failed to renew agent certificate

System.Security.Cryptography.CryptographicException: Access is denied.

Root Cause

Agent certificate renewal fails when the Certificate Connector for Intune is running under a service account that is not a member of the local administrators security group. You will not encounter this error if the connector services are running in the SYSTEM context, however.

Resolution

There are a few different ways to resolve this issue. Here are some options to consider.

Grant Admin Rights

Adding the service account under which the connector service runs will allow the agent certificate to renew automatically. However, this may not be desirable from a security perspective. To address this, administrators may temporarily grant local administrative access to renew the agent certificate, then revoke this permission once the certificate has been successfully renewed. However, this is a manual process that doesn’t scale well and requires annual administrative intervention.

Reinstall

Uninstalling and reinstalling the Certificate Connector for Intune will force a new certificate enrollment during the registration process. You can delete the old certificate after completing the installation.

Switch to SYSTEM

Changing from a service account to SYSTEM will also resolve this issue. However, it is not recommended to make these changes directly on the services themselves. Instead, administrators should remove and reinstall the Certificate Connector for Intune, selecting the SYSTEM option rather than the service account method.

Note: Using the SYSTEM account for the Certificate Connector for Intune should be avoided when using PKCS. Details here.

Summary

The Certificate Connector for Intune agent certificate renewal fails when the service is configured to run as a service account without local administrative rights. The best way to resolve this is to add the service account to the local administrators group on the server where the connector is installed. However, this isn’t always ideal. Although running the connector in the SYSTEM context is acceptable when using SCEP, it should be avoided when using PKCS. Administrators will have to accept the risk of the service account having local administrative rights or accept that they’ll have to reinstall the connector annually.

Additional Information

Certificate Connector for Intune Service Account and PKCS

Strong Certificate Mapping for Intune PKCS and SCEP Certificates

Intune Strong Certificate Mapping Error

Intune PKCS and SCEP Certificate Validity Period

Certificate Connector for Intune Failure

Certificate Connector for Intune Configuration Failed

Troubleshooting Intune Failed PKCS Request

Microsoft Security Service Edge Now Generally Available

A few weeks ago, Microsoft announced the general availability of its Security Service Edge (SSE) offering, Global Secure Access (GSA). GSA encompasses Entra Internet Access, a cloud-based Secure Web Gateway, and Entra Private Access, a Zero Trust Network Access (ZTNA) solution for accessing private data and applications on-premises.

ZTNA vs. VPN

Entra Private Access will be a compelling alternative to traditional VPN solutions such as Windows Always On VPN. Where traditional VPNs grant the endpoint an IP address on the internal network, Entra Private Access provides more granular access and does not require the device to be directly connected to the network.

GSA Client

Administrators must install the GSA client on all endpoints using Entra Internet Access or Entra Private Access. Today, the client is available for Windows and Android devices. iOS and macOS clients are forthcoming.

Private Network Connector

The Entra Private Access solution relies on the Entra Private Network Connector. The Entra Private Network Connector is a software component installed on-premises that provides remote access connectivity. Previously, it was called the Azure AD Application Proxy. Essentially, it is the same technology extended to support TCP and UDP network access in addition to HTTP.

Limitations

Entra Private Access is the way of the future for secure remote access. However, today, there are still some important limitations associated with this technology.

Private DNS

Although Microsoft announced general availability for Entra Private Access, it still lacks the private DNS feature many organizations require to provide feature parity with their existing VPN. This feature is still in private preview at the time of this writing. Hopefully, Microsoft will release this feature soon.

Device Connection

Entra Private Access does not support device-based connections. This limits its capabilities for domain-joined devices. If your organization uses hybrid Entra join today, consider sticking with Always On VPN until you move to native Entra joined endpoints.

Licensing

Global Secure Access (Entra Private Access and Entra Internet Access) are included in the Microsoft Entra Suite license. More information about Entra licensing can be found here.

Additional Information

Microsoft Global Secure Access Now Generally Available

Microsoft Entra Global Secure Access (GSA) Overview

Microsoft Entra Security Service Edge (SSE) on the RunAs Radio Podcast

Microsoft Entra Plans & Pricing

Microsoft Intune Certificate Connector Failure

The Microsoft Intune Certificate Connector enables the provisioning and de-provisioning of on-premises PKI certificates for Intune-managed devices. Always On VPN administrators using Intune to deploy certificates with the Intune Certificate Connector using either PKCS or SCEP may encounter a scenario where certificates are no longer being provisioned to users or devices after working reliably previously.

Certificate Not Found

When this issue occurs, users will no longer be able to access the VPN and receive a “certificate could not be found that can be used with this Extensible Authentication Protocol” error message.

Always On VPN error stating a certificate could not be found that can be used with this Extensible Authentication Protocol

Connector Status

To determine the status of the Intune Certificate Connector, open the Microsoft Intune Admin Center (https://intune.microsoft.com) and navigate to Tenant Administration > Connectors and Tokens > Certificate Connectors. The status of the certificate connector server will be in Error.

Intune admin center Certificate Connectors page showing the connector in an Error state

Event Log

Open the event log on the server where the Intune Certificate Connector is installed. Navigate to Applications and Services Logs > Microsoft > Intune > CertificateConnectors > Operational. Here, you will find a variety of warning and error messages.

Event ID 5001

This is a warning from the CertificateConnectors source with event ID 5001 in the Task Category HealthMessageUploadFailedAttempt with the following details.

PKI Create Service:

Failed to upload health messages. Requeuing messages.

Event ID 1003

This is an error from the CertificateConnectors source with event ID 1003 in the Task Category PkcsDownloadFailure with the following details.

PKI Create Service:

Failed to download PKCS requests.

Event ID 2

This is an error from the CertificateConnectors source with event ID 2 in the Task Category Exception with the following details.

PKI Create Service:

Microsoft.Intune.Connectors.PkiCreateProcessor.Process threw an exception.

Expired Certificate

The warning and error messages recorded in the event log indicate an expired certificate on the Intune Certificate Connector server. Open the local computer certificate store (certlm.msc) on the server where the Intune Certificate Connector is installed. Review the expiration date of the certificate issued by Microsoft Intune ImportPFX Connector CA. It is most likely expired.

Local computer certificate store on the Intune Certificate Connector server showing the expired connector certificate

Click on the Certification Path tab to view the certificate status.

Certificate Certification Path tab showing the certificate has expired

Renew Certificate

To renew this certificate, you must reinstall the Intune Certificate Connector. However, you do not have to uninstall it first. To renew the certificate, navigate to C:\Program Files\Microsoft Intune\PFXCertificateConnector\ConnectorUI and double-click on PFXCertificateConnectorUI.exe. Follow the prompts without making changes to the existing configuration. You’ll be prompted for the service account password (if using a domain account) and proxy credentials (if using a proxy server). In addition, you’ll be asked to sign in to Entra ID (formerly Azure AD). Be sure to provide credentials that are a global administrator and have an Intune license assigned. Once the process is complete, a new certificate will be installed in the local computer certificate store.

Intune Configuration

After updating the Intune Certificate Connector, a new certificate connector appears in the Intune Admin Center. You can now safely delete the old connector and rename the new one accordingly.

Intune admin center listing the old and new Intune Certificate Connector entries

Redundancy

Deploying multiple instances of the Intune Certificate Connector is an excellent way to avoid future outages! It’s also a good idea to stagger their installation by a few months to ensure that a future certificate expiration doesn’t result in lost functionality. If you’ve deployed Intune Certificate Connectors recently, consider updating them at rotating intervals so certificates expire at different times.

Additional Information

Enterprise PKI with Microsoft Active Directory Certificate Services

Intune Certificate Connector Configuration Failed

Intune Certificate Connector Service Account and PKCS

Intune Certificate Connector Configuration Failure

Microsoft Intune Learning Resources for Always On VPN Administrators